Awesome-LLMs-for-Vulnerability-Detection

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

The community's most comprehensive, continuously-updated index of research on Large Language Models for software vulnerability detection — papers…

A comprehensive browser extension (.xpi) malware scanner which checks for many common malware tricks like:, credential-stealers obfuscation tactics,…

Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…

Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…

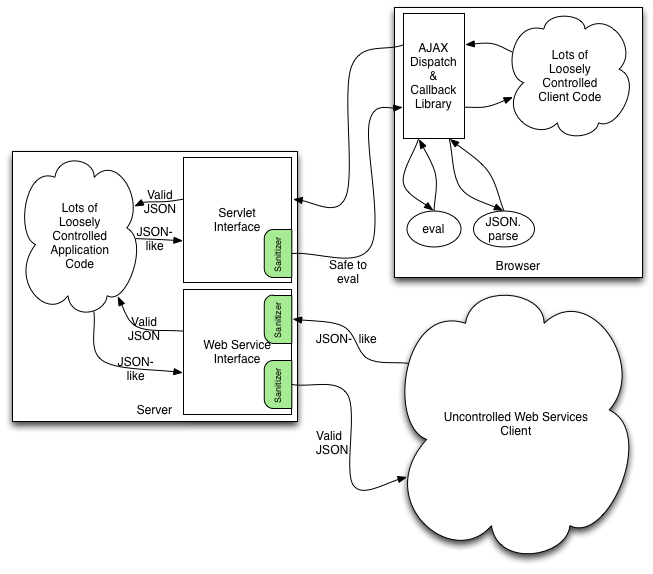
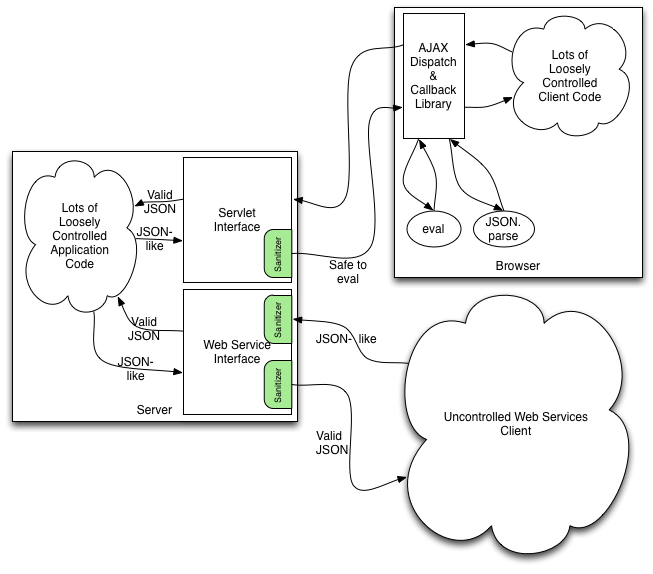
Given JSON-like content, The JSON Sanitizer converts it to valid JSON.

Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.

Java library that converts malformed JSON-like content into standards-compliant, safe JSON, preventing code injection and ensuring embeddability in…

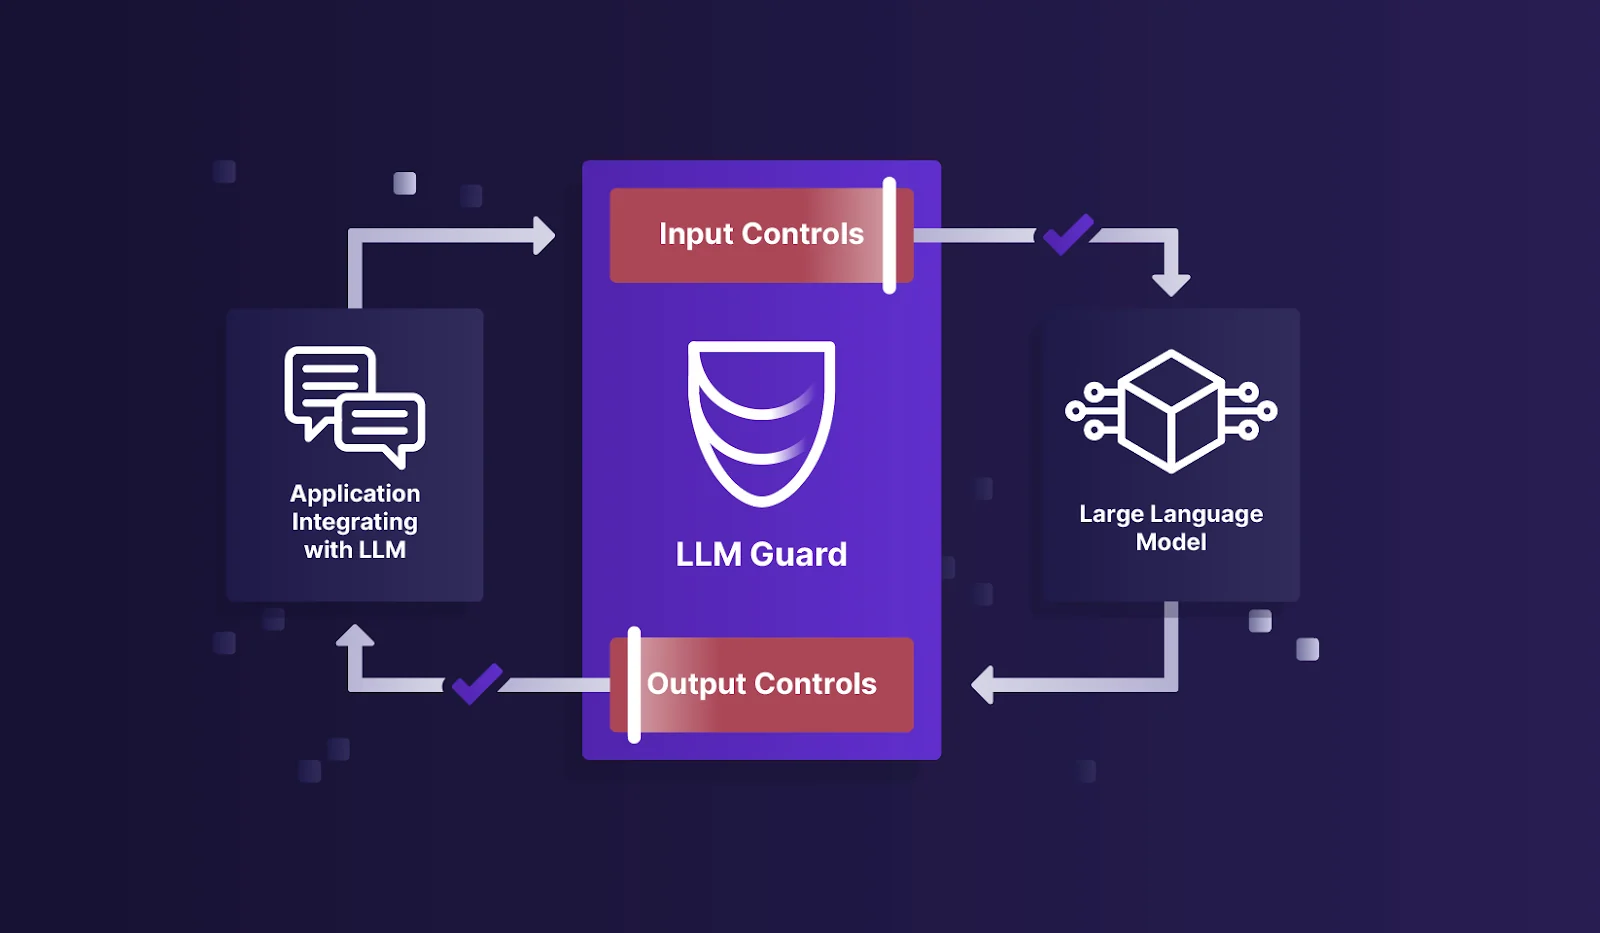
The Security Toolkit for LLM Interactions

Detailed technical analysis of CVE-2026-47777, a high-severity authorization bypass in Mastodon's Featured Collections federation pipeline, including…

Static analysis tool that scans source code for hardcoded secrets, API keys, and credentials using semantic understanding of code context.

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…

OWASP Secure Agent Playbook Project

Enterprise AI agent security toolkit providing pre-flight auditing, configuration hardening, runtime threat detection, and active defense against…

Automatically identify deserialisation issues in Java and .NET applications by using active and passive scans

JSON sanitizer that converts malformed JSON-like content into valid, safe JSON, preventing code injection and ensuring standards compliance for web…

Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…

Jenkins plugin providing script approval workflows and Groovy sandboxing to enforce secure script execution, with ACL-aware permission checks and…

Semgrep rules that flag header-trust auth bypass patterns (CVE-2025-29927 class). Companion to bk-security.github.io.