
CVE-2025-6220
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
code-analysisexploitationpayload-generation+3
d0n601/cve-2025-6220Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
 trailofbits/trailmark
Build and query a graph database representation of source code
 neimar47574/cve-2022-24087
Proof-of-concept exploit for CVE-2022-24086 and CVE-2022-24087, demonstrating pre-authentication remote code execution in Magento/Adobe Commerce via…
 xxconi/cve-2026-3296
CVE-2026-3296 is a CVSS 9.8 Critical unauthenticated PHP Object Injection vulnerability in the Everest Forms WordPress plugin
 crytic/caracal
Static Analyzer for Starknet smart contracts
 raptor-audit/raptor
Framework for auditing blockchain ecosystems, identifying smart contract vulnerabilities, and generating structured findings with multi-platform…
 zhangzhuosjtu/web3bugs
Demystifying Exploitable Bugs in Smart Contracts
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
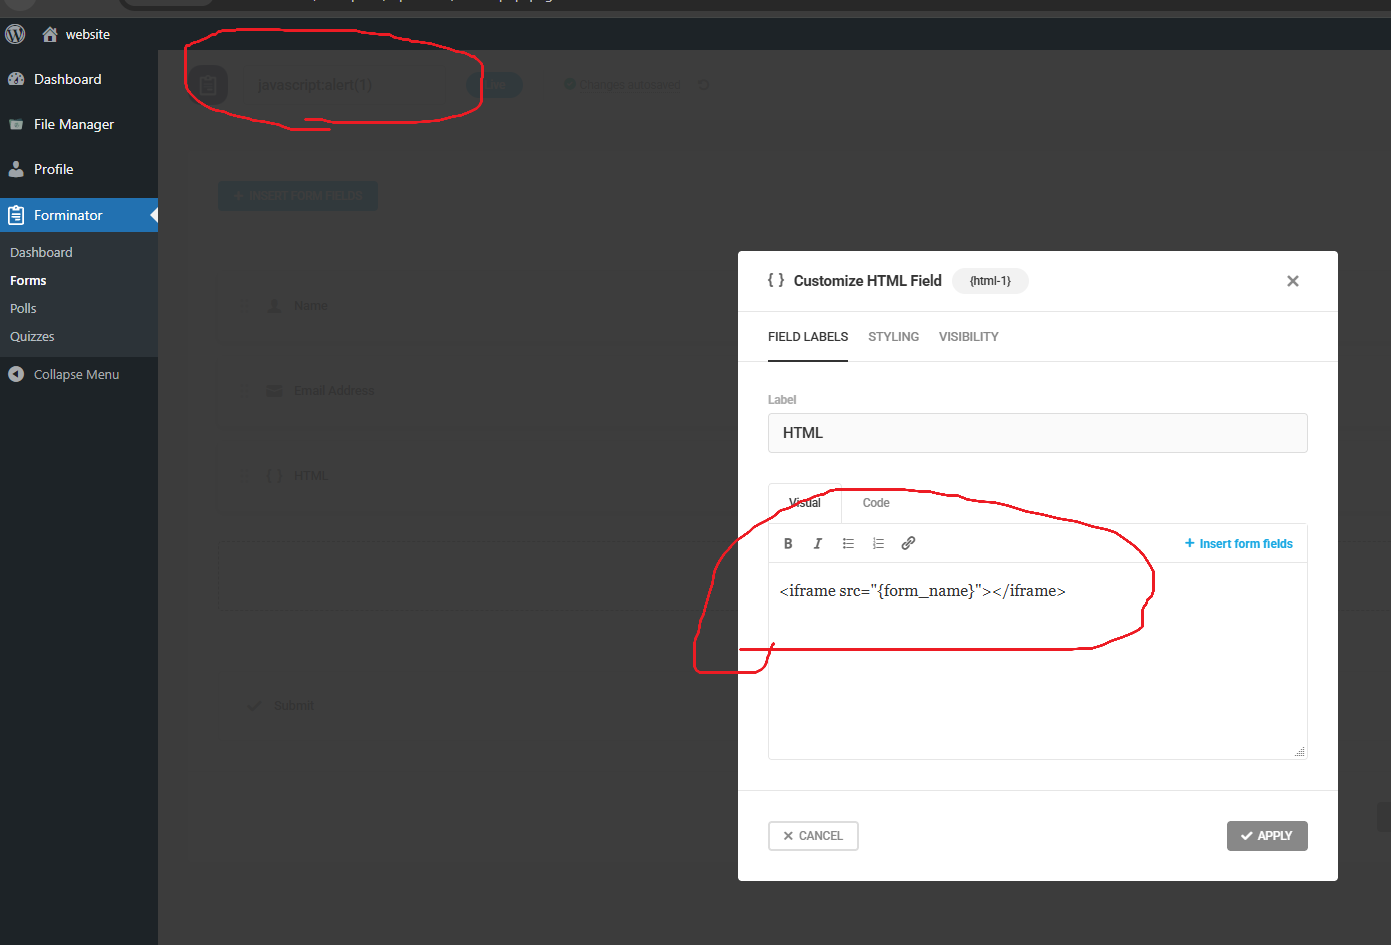 typedefabcd1234ntd/cve-2026-2002-poc
CVE-2026-2002 writeup and Proof-of-concept
 xsultan/log4jshield
Log4j Shield - fast ⚡, scalable and easy to use Log4j vulnerability CVE-2021-44228 finder and patcher
 izxci/cve-2026-9691
CVE-2026-9691: Integration for ActiveCampaign and Contact Form 7, WPForms, Elementor, Ninja Forms <= 1.1.1 Unauthenticated PHP Object Injection PoC,…
 xxconi/cve-2026-5718
CVE-2026-5718: Unauthenticated File Upload To RCE in DnD Upload CF7 Plugin
 mtgsjr/cve-2025-66802
Sourcecodester Covid-19 Contact Tracing System 1.0 is vulnerable to RCE
 kai-one001/-cve-2015-10137-wordpress-n-media-website-contact-form-with-file-upload-1.3.4
Python exploit for CVE-2015-10137 targeting an arbitrary file upload vulnerability in the WordPress N-Media Website Contact Form plugin, enabling…