

-LogicSentry-AI
 vighnesh91/-logicsentry-ai
Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
1
vighnesh91/-logicsentry-aiOffline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 tuo4n8/cve-2022-24760
Detailed technical analysis of CVE-2022-24760, a prototype pollution vulnerability in parse-server leading to remote code execution via BSON…
 nccgroup/android_demystification_toolbox
ADT is a toolset designed to help model application behavior, research and test security vulnerabilities, and facilitate reversing hostile code.
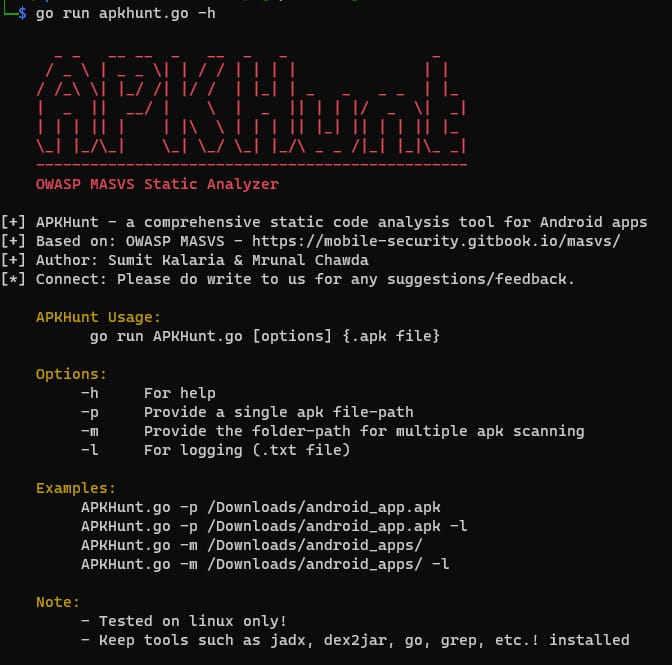 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 ludovicpatho/cve-2022-22965_spring4shell
A Spring MVC or Spring WebFlux application running on JDK 9+ may be vulnerable to remote code execution (RCE) via data binding. The specific exploit…
 edgarloyola/cve-2021-40904
Proof-of-concept for remote code execution in CheckMK Raw Edition 1.5.0–1.5.0p25 via misconfigured Dokuwiki embedded application allowing PHP code…
 sahiloj/cve-2025-5352
Demonstrates a stored XSS vulnerability in lunary-ai/lunary's Analytics component, where unsanitized NEXT_PUBLIC_CUSTOM_SCRIPT injection leads to…
 isacaya/cve-2019-11358
Proof-of-concept exploit for CVE-2019-11358, a prototype pollution vulnerability in jQuery's extend method (versions <3.4.0). Demonstrates the attack…
 warxim/cve-2022-41852
CVE-2022-41852 Proof of Concept (unofficial)
 edgarloyola/cve-2021-40905
Proof-of-concept exploit for CVE-2021-40905, a remote code execution vulnerability in CheckMK Management Web Console via crafted .mkp extension…
 dollarboysushil/dolibarr-17.0.0-exploit-cve-2023-30253
In Dolibarr 17.0.0 with the CMS Website plugin (core) enabled, an authenticated attacker can obtain remote command execution via php code injection…
 toanln-cov/cve-2026-78071
Stored XSS via Location Title in DPCalendar Free
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 0z09e/cve-2022-22909
Hotel Druid 3.0.3 Code Injection to Remote Code Execution
 trickstersec/cve-2019-5420
Exploit for the Rails CVE-2019-5420
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…