
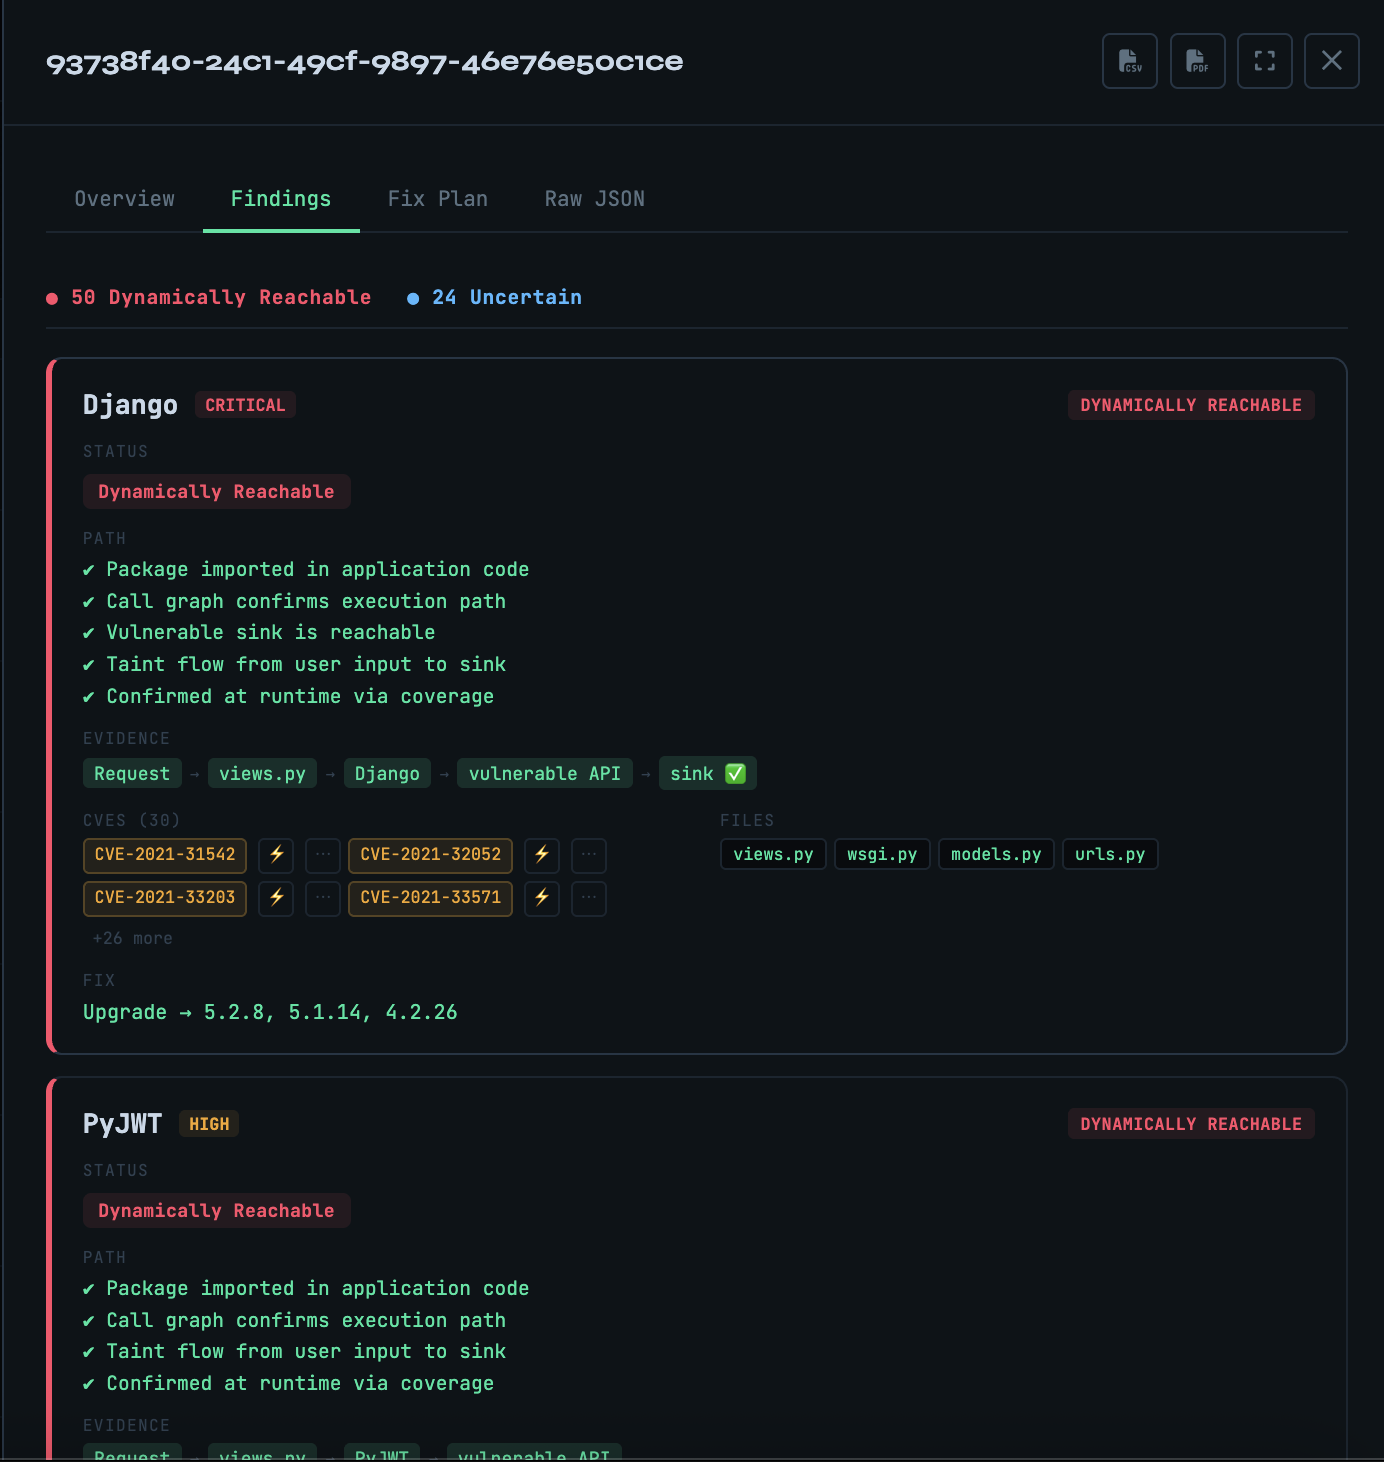
VulnReach
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
code-analysisdevsecopsdynamic-analysis-sandboxing+5
164 days ago
owasp/vulnreachRuntime-aware SCA — proves which CVEs are actually reachable, not just installed.
 osmankandemir/static-code-analysis-helper
Scans project source code across 16 languages to flag dangerous functions linked to SQLi, XSS, SSRF, command injection, weak crypto, and other web…
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 cookiengineer/exocomp
Self-hosted multi-agent environment for Go with LLM-powered pentesting agents (exploiter, reverser, threathunter, webscanner) that automate…
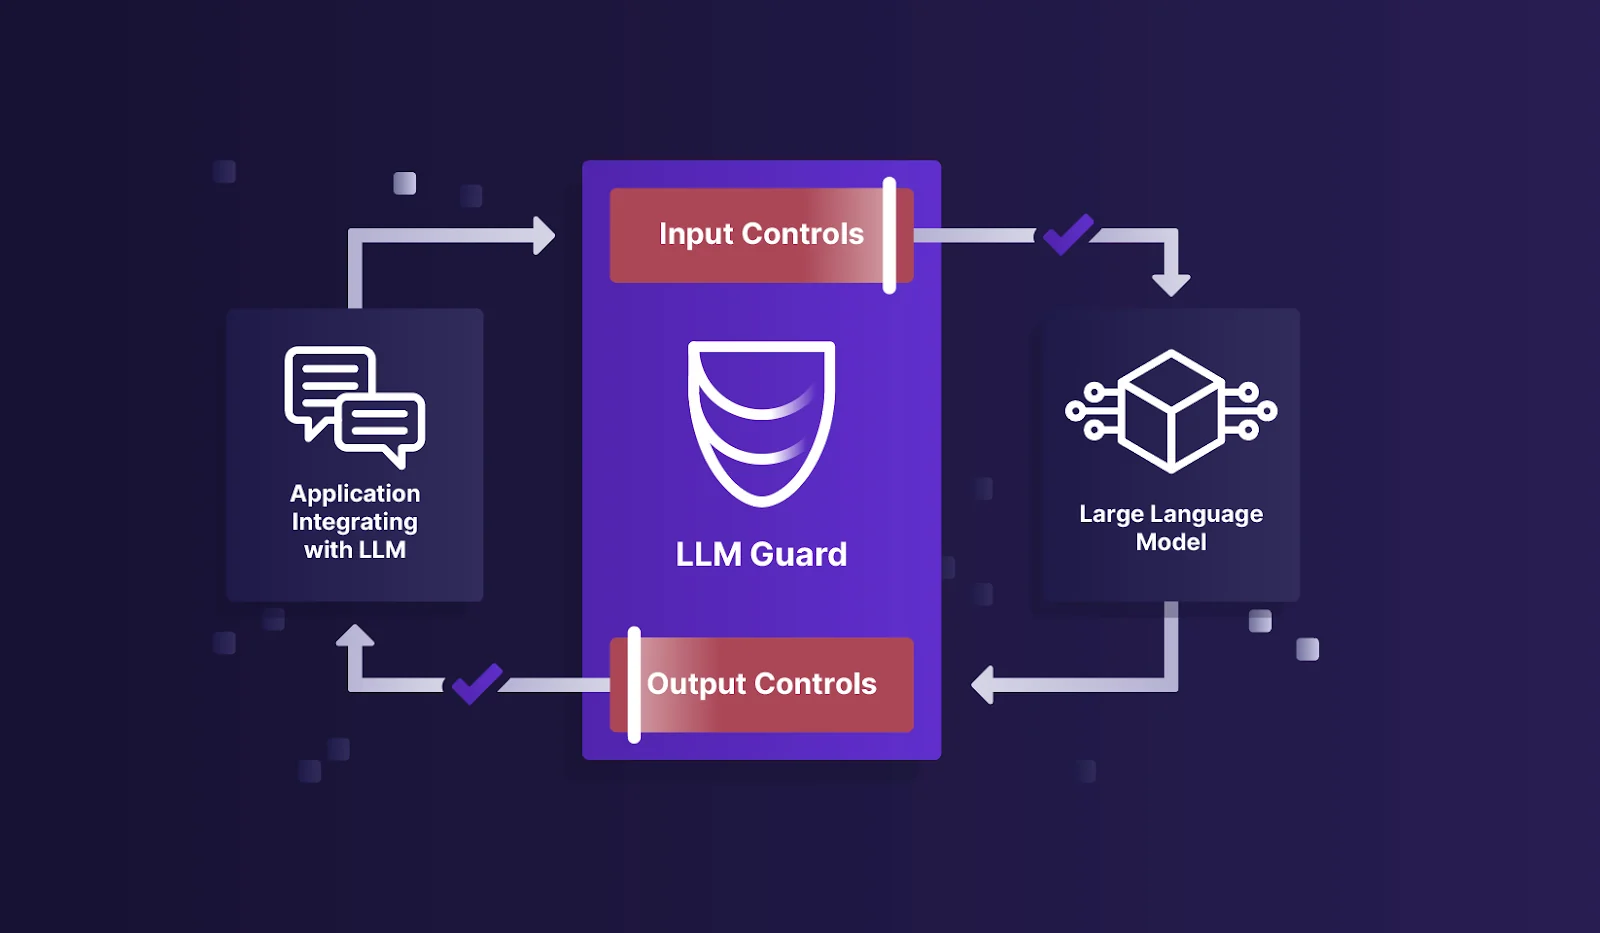 protectai/llm-guard
The Security Toolkit for LLM Interactions
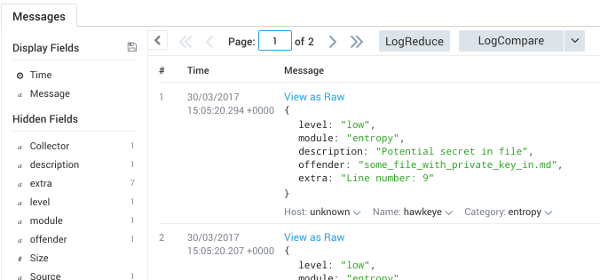 hawkeyesec/scanner-cli
A project security/vulnerability/risk scanning tool
 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
 hozyx/log4shell
Applications that are vulnerable to the log4j CVE-2021-44228/45046 issue may be detectable by scanning jar, war, ear, zip files to search for the…
 checkmarx/checkmarx-cve-2025-30066-detection-tool
Scans GitHub workflows and logs for indicators of CVE-2025-30066, detecting malicious actions and exposed secrets using Checkmarx 2ms integration.
 honeyb33z/cve-2020-11023-scanner
Static analysis scanner for CVE-2020-11023 XSS vulnerabilities in JavaScript. Detects vulnerable jQuery versions and dangerous DOM manipulation…
 shakilkhatri/scanner-for-cve-2025-55182-vulnerability
CVE-2025-55182 Detector. Find which of your GitHub repositories are exposed to the critical React/Next.js RCE vulnerability and generate a clean…
 ill-deed/langflow-cve-2025-3248-multi-target
Langflow versions prior to 1.3.0 are susceptible to code injection in the /api/v1/validate/code endpoint. A remote and unauthenticated attacker can…
 fazilbaig1/cve-2020-28458
Affected versions of this package are vulnerable to Prototype Pollution.
 dream434/cve-2024-34102
Exploit script for CVE-2024-34102, an XXE vulnerability in Adobe Commerce allowing arbitrary code execution via crafted XML documents.