

recon-skills
 uphiago/recon-skills
Field-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
cloud-securitycrawlerexploitation+9
1.3k
uphiago/recon-skillsField-validated offensive security skill pack with 169 techniques for reconnaissance and penetration testing. Covers CORS, SSRF, subdomain takeover,…
 specterops/azurehound
Collects Azure tenant data (users, groups, roles, resources) and exports it for BloodHound attack path analysis in cloud penetration testing and red…
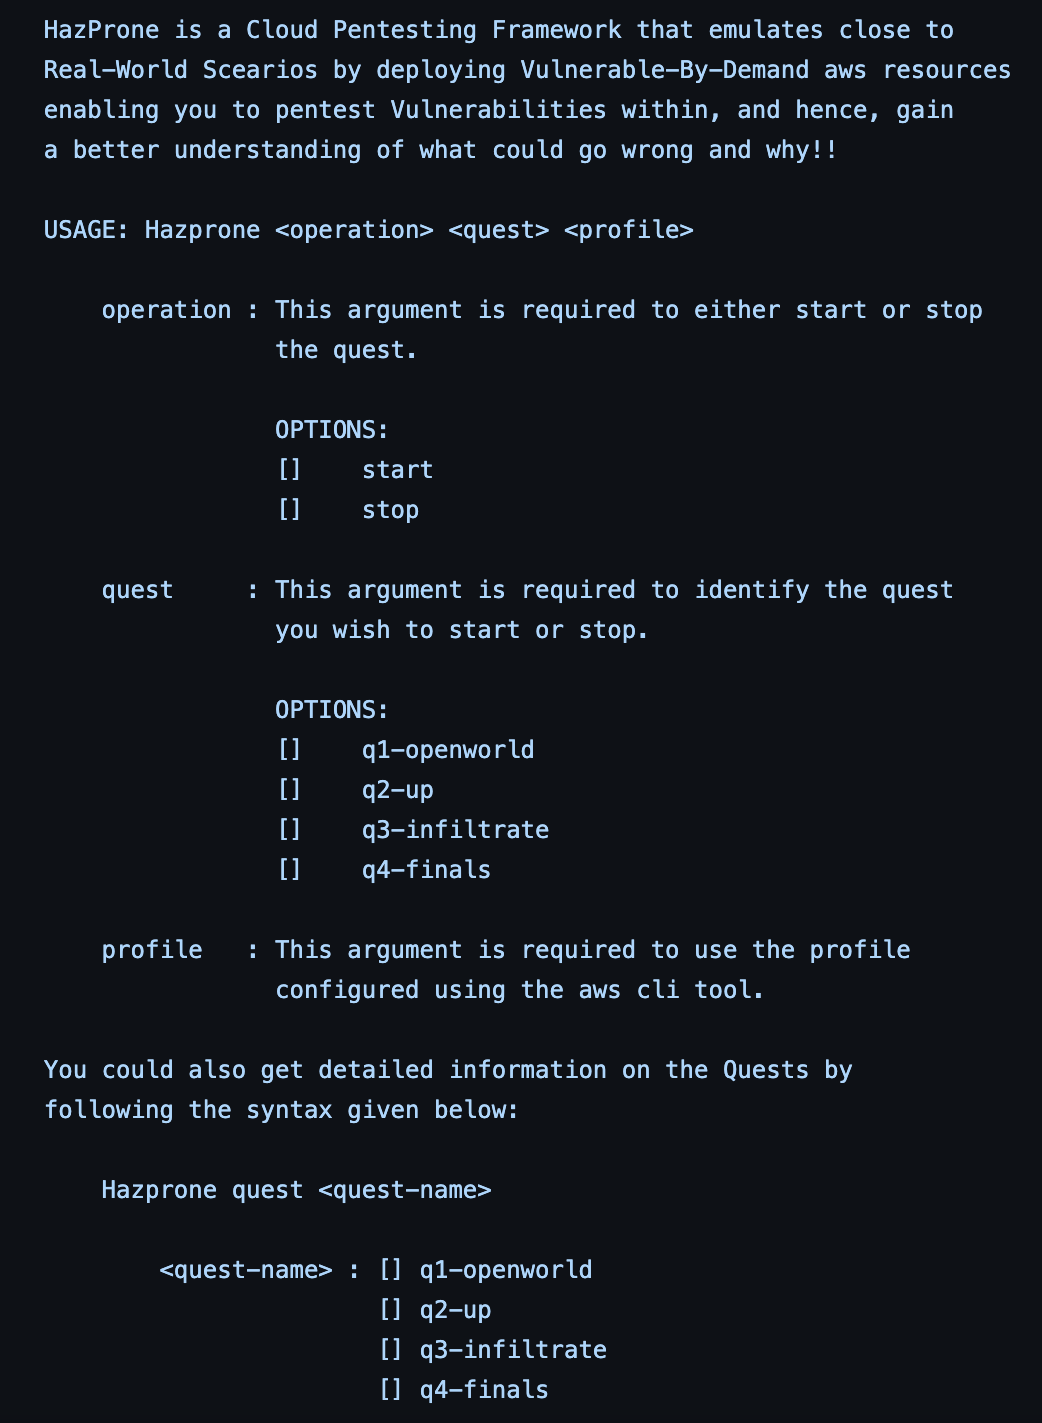 stafordtituss/hazprone
Cloud pentesting framework deploying vulnerable-by-demand AWS resources with quest-based scenarios to teach practical penetration testing and…
 pannagkumaar/pentest-lab
Modern cyber range with 50 hands-on challenges across web, API, cloud, AI, and blue-team security tracks. Features guided attack chains, transparent…
 mgeeky/penetration-testing-tools
A collection of more than 170+ tools, scripts, cheatsheets and other loots that I've developed over years for Red Teaming/Pentesting/IT Security…
 enaqx/awesome-pentest
A collection of awesome penetration testing resources and tools
 oj/gobuster
Directory/File, DNS and VHost busting tool written in Go
 0xsteph/pentest-ai
Open-source AI pentester that proves every finding. Machine oracles re-run each exploit; verified bugs ship a proof capsule you can replay yourself.
 macmod/goblob
A fast enumeration tool for publicly exposed Azure Storage blobs.
 kc57/awesome-pentest
A list of awesome penetration testing tools and resources.
 ajutamangdev/hatiyar
Modular penetration testing framework with a Metasploit-like interactive shell, pre-built CVE exploit modules, and cloud/network reconnaissance…
 shabarkin/aws-enumerator
Read-only AWS service enumerator with 600+ API calls for cloud reconnaissance, info dumping, and result analysis during penetration testing.
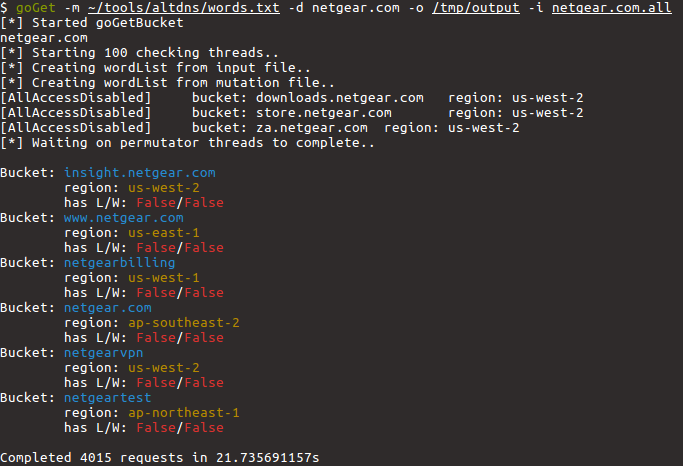 glem0/gogetbucket
A penetration testing tool to enumerate and analyse Amazon S3 Buckets owned by a domain.
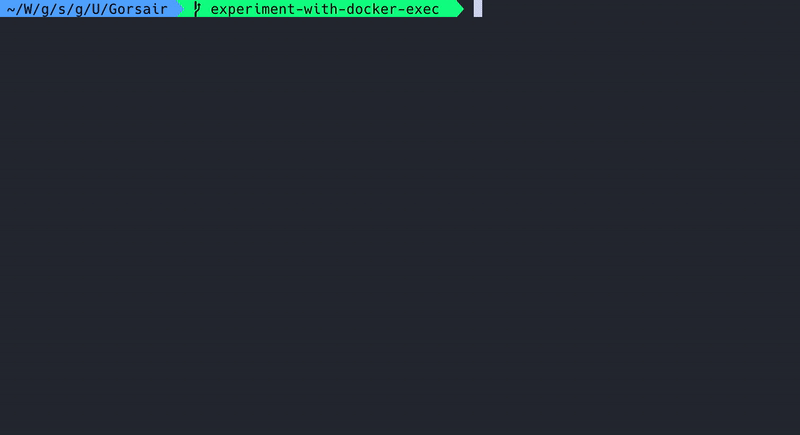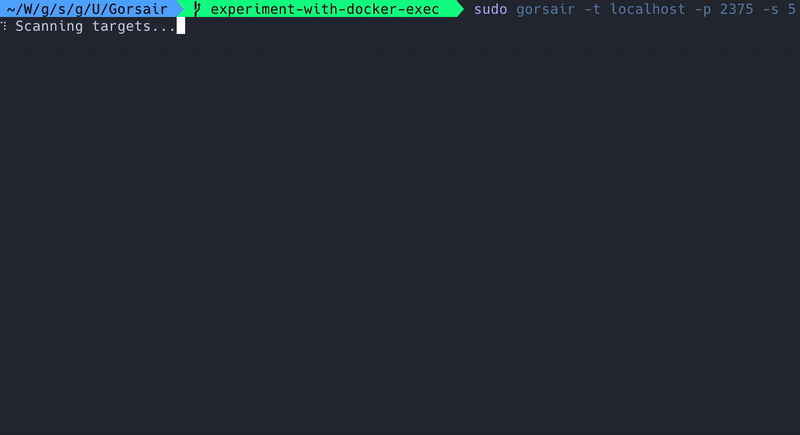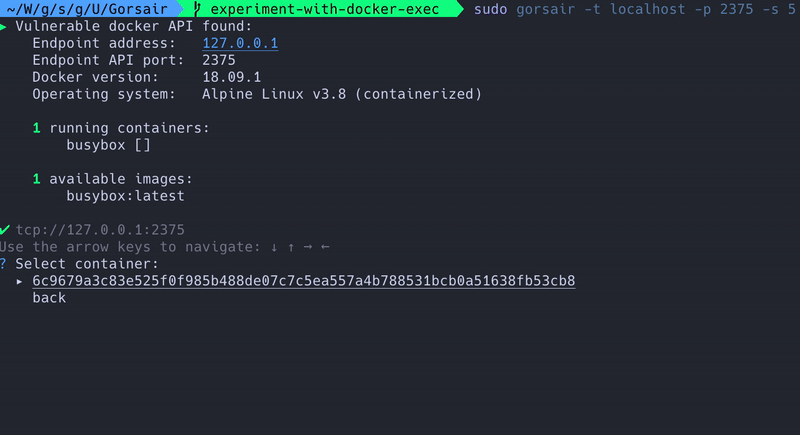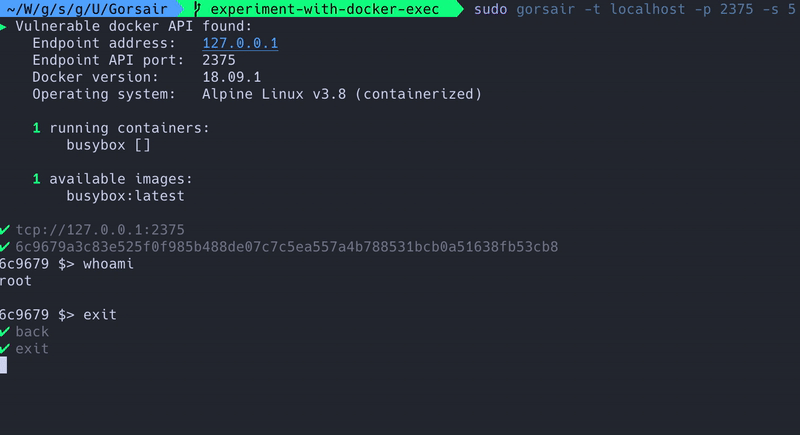 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
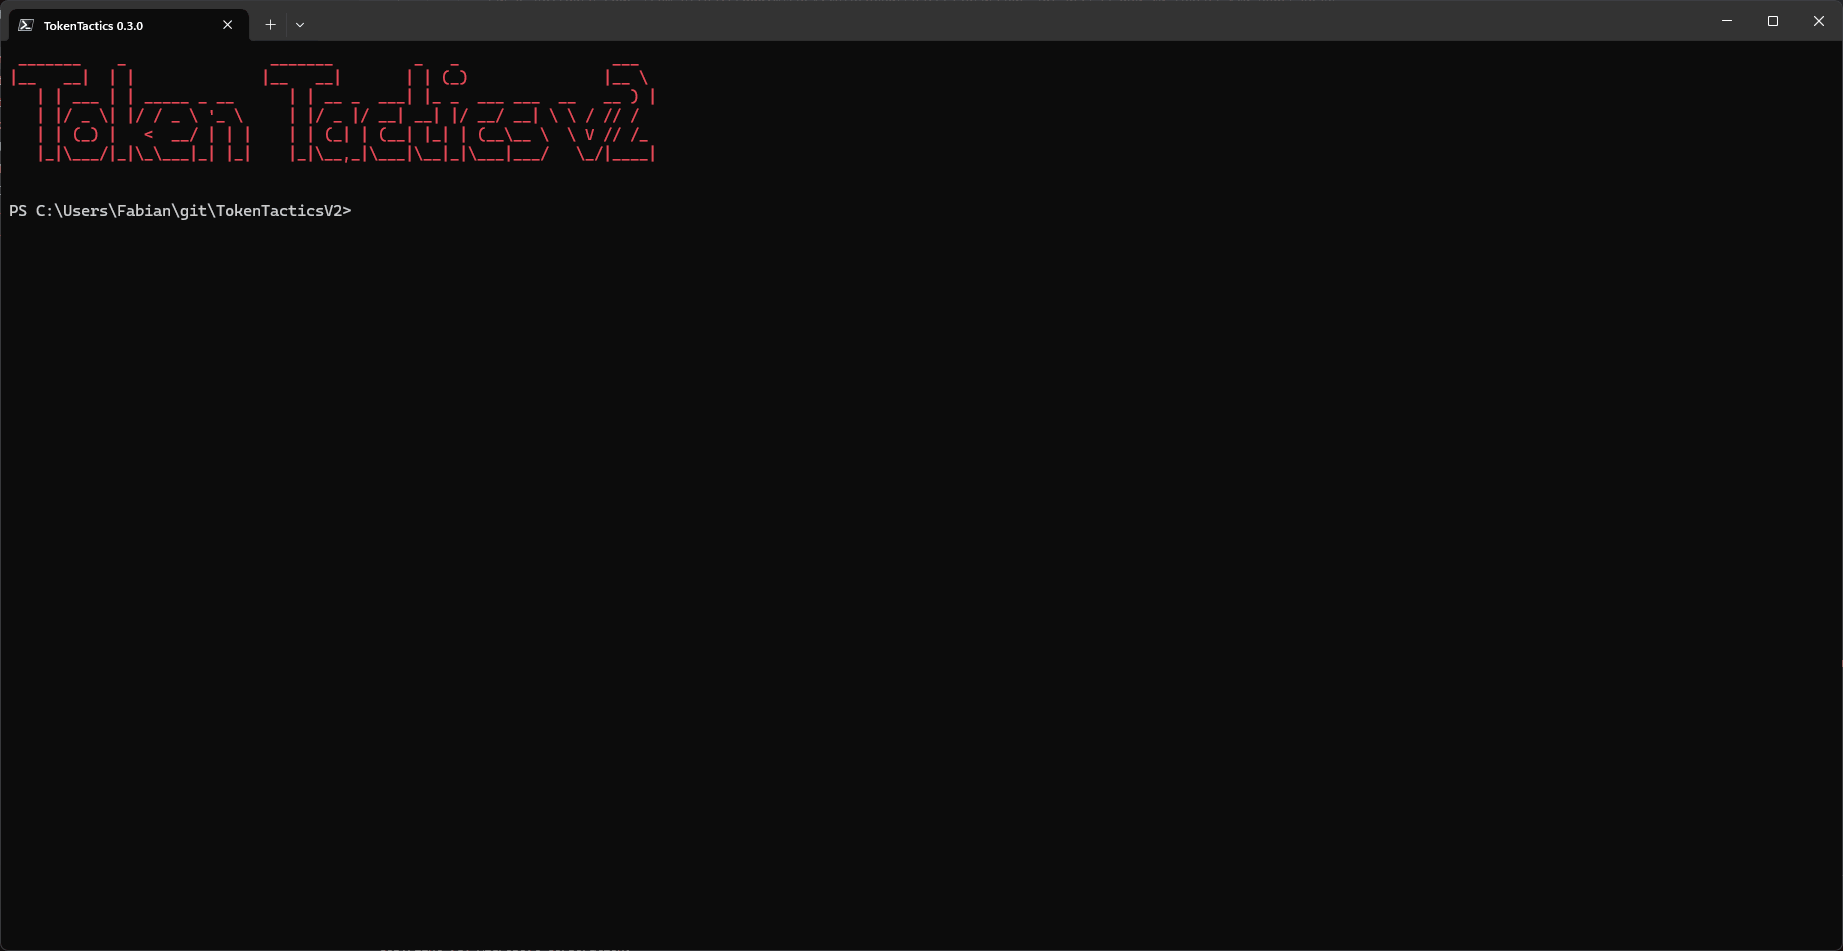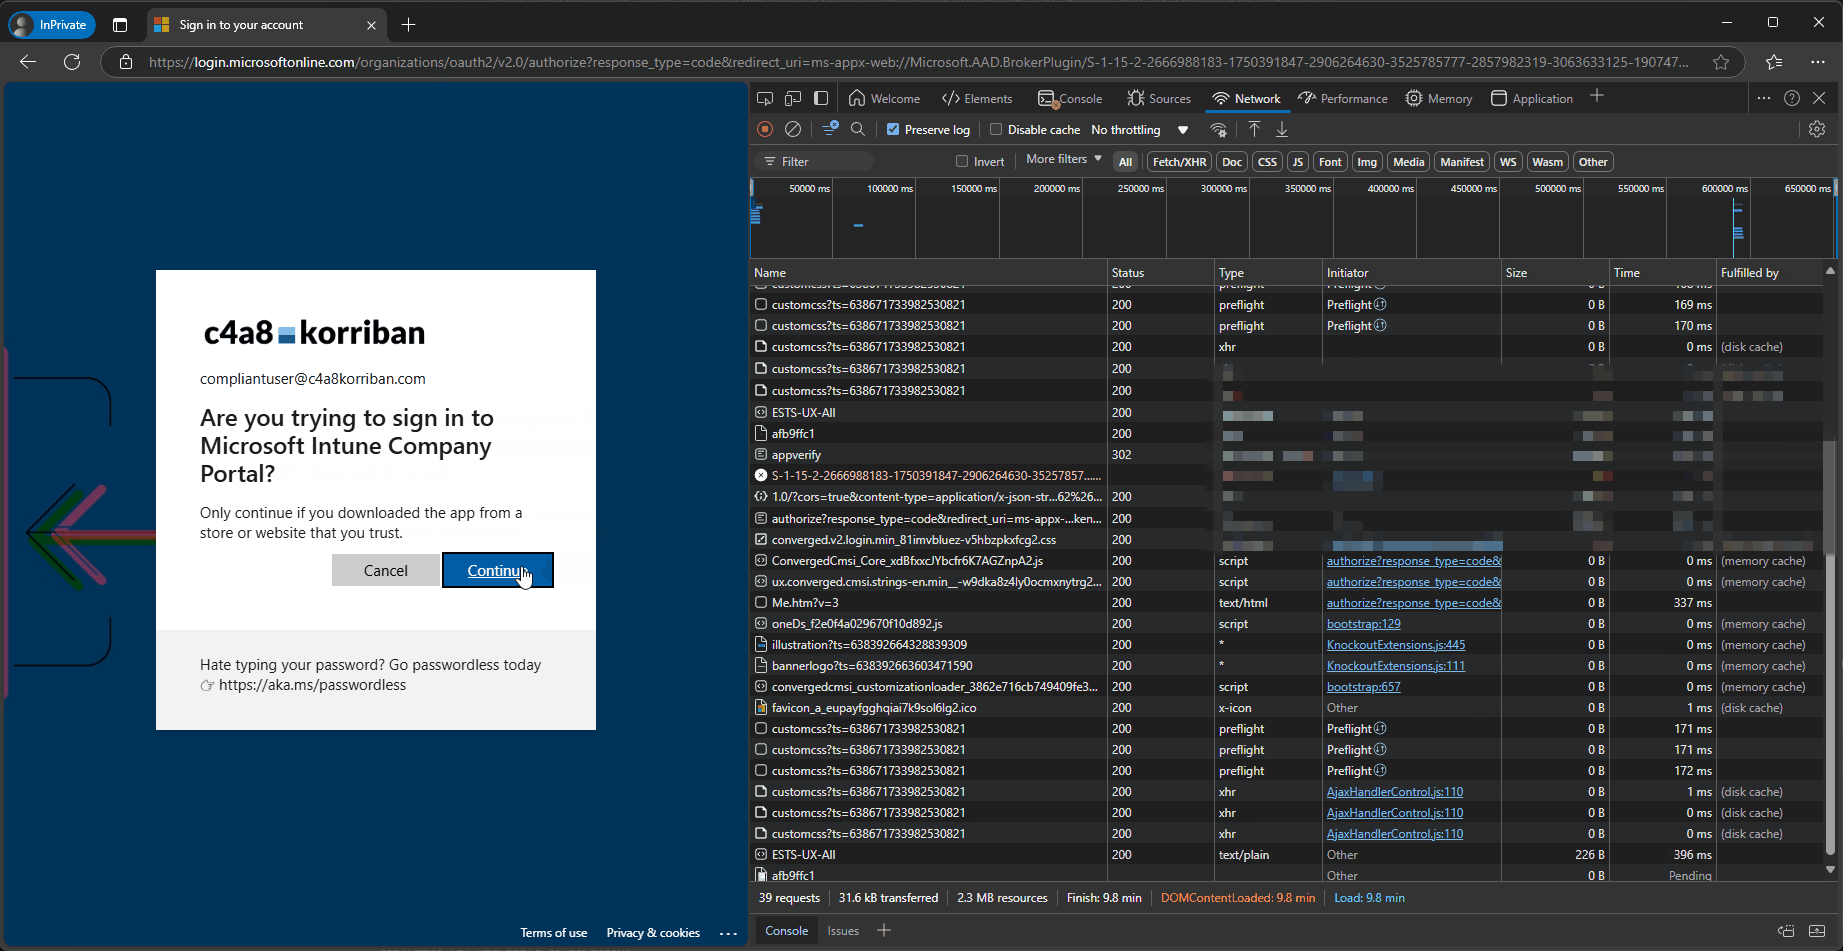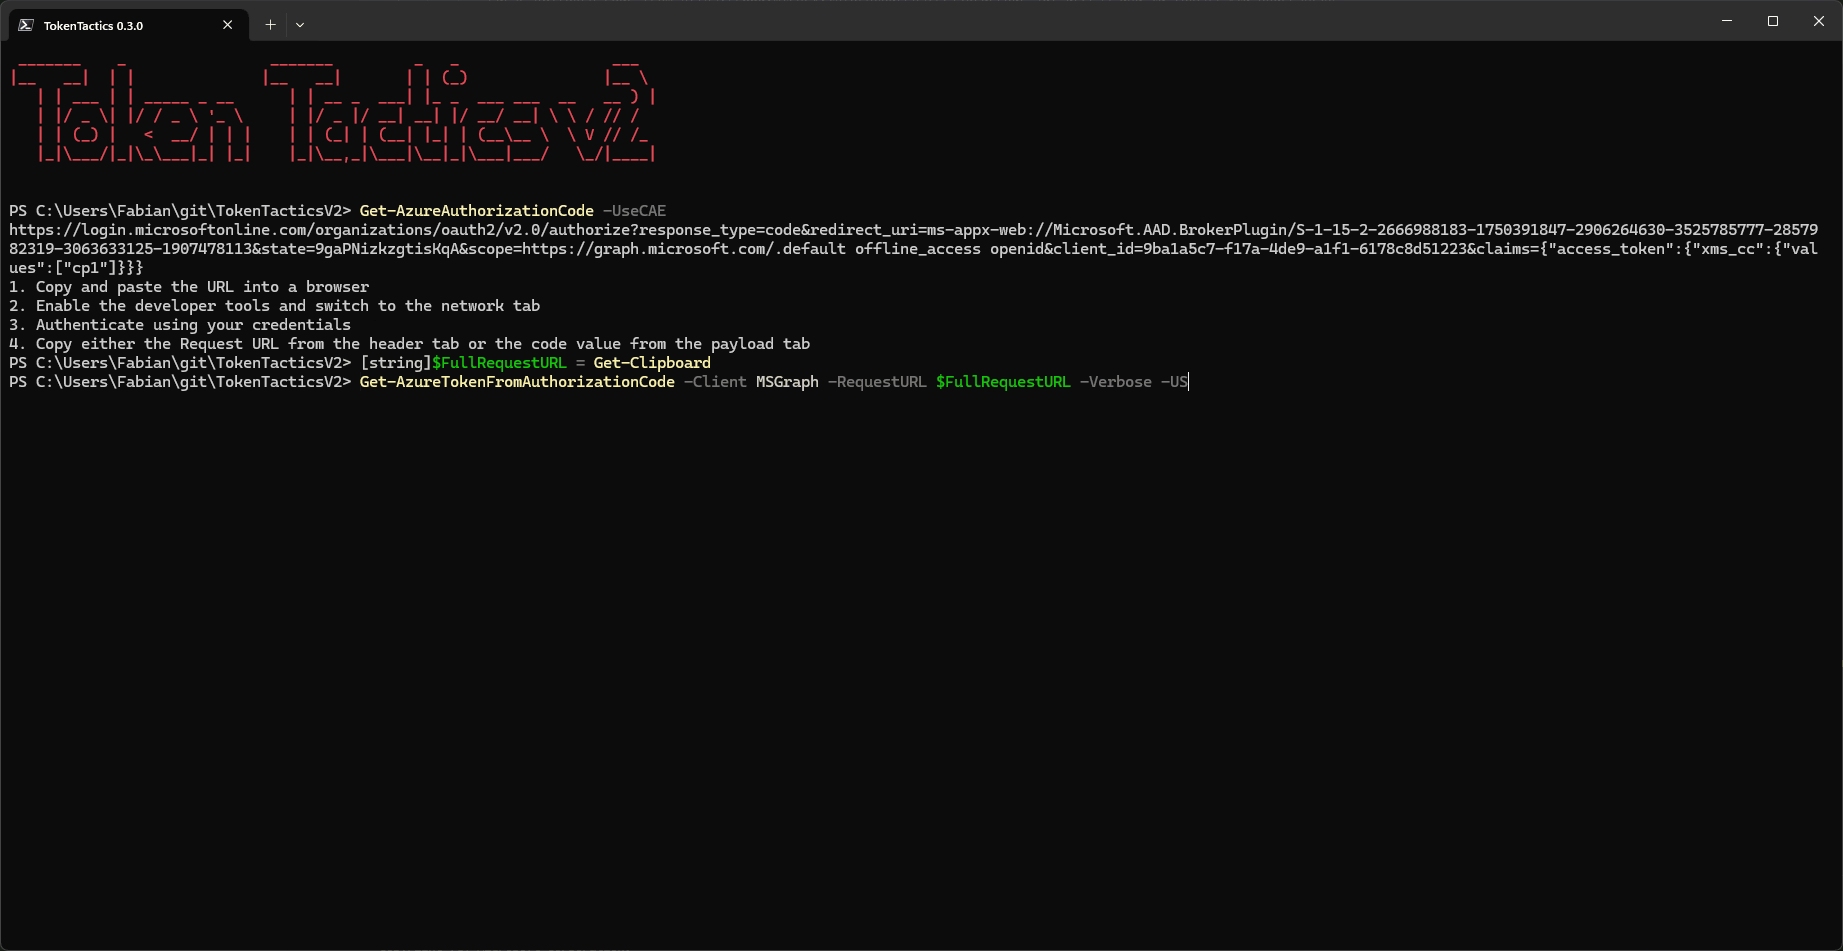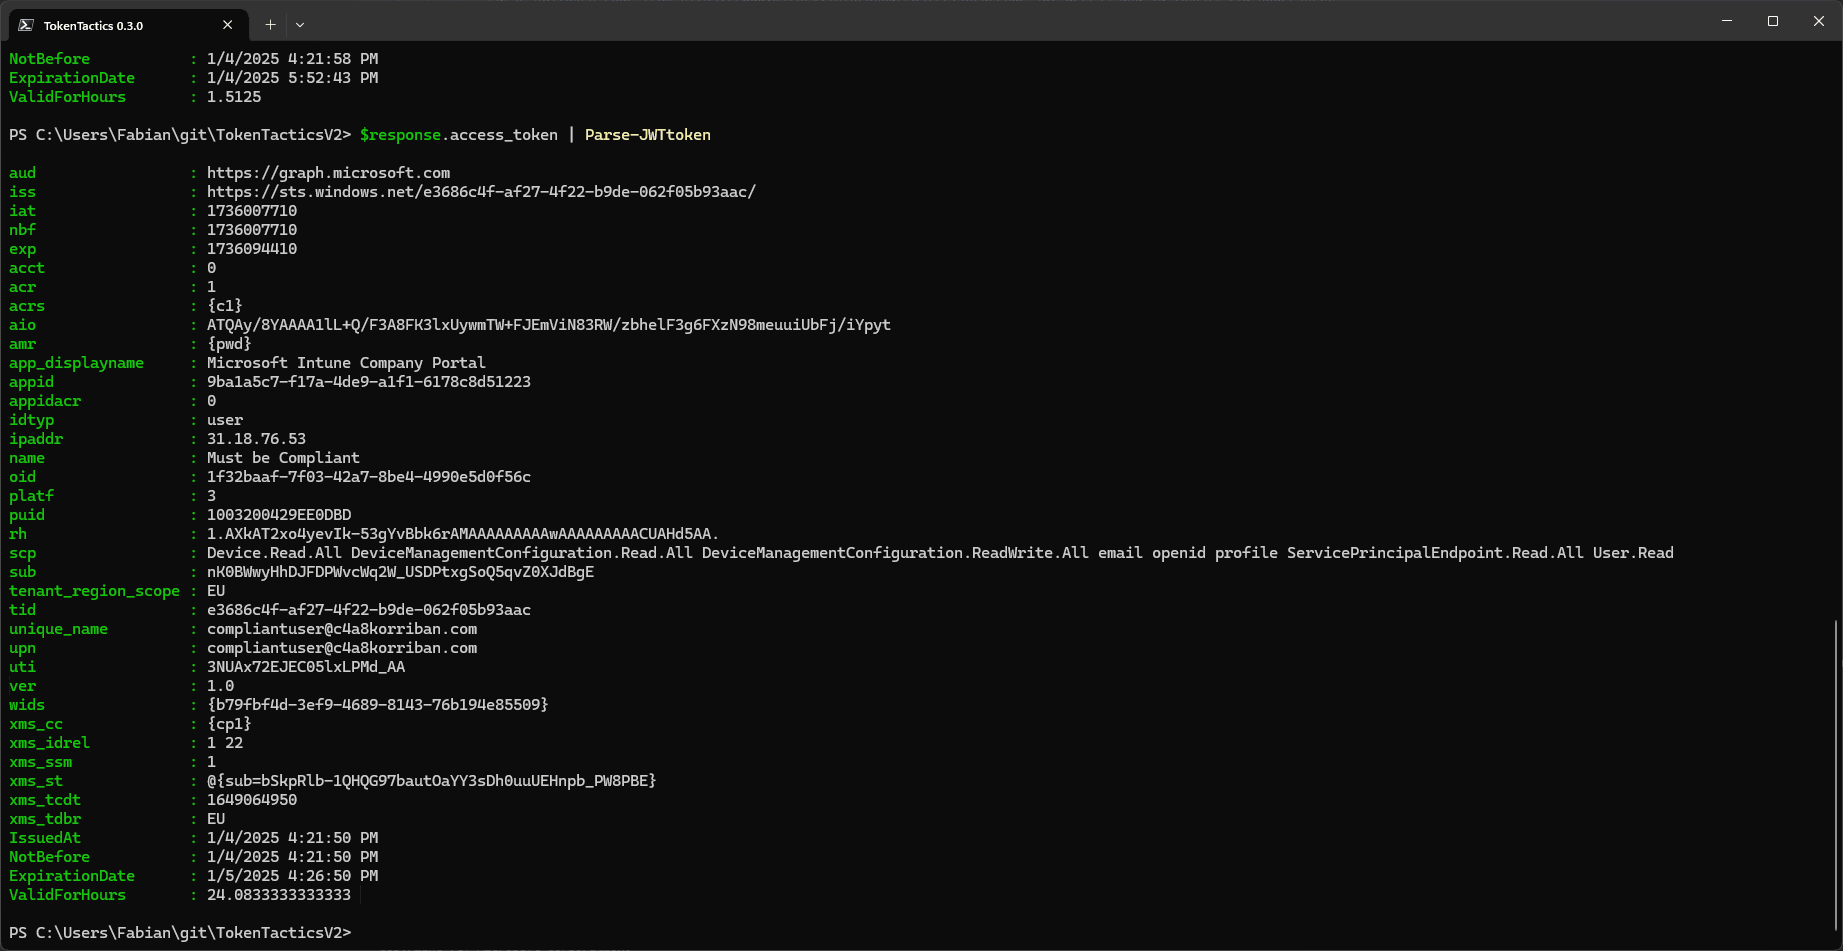 f-bader/tokentacticsv2
A fork of the great TokenTactics with support for CAE and token endpoint v2
 anshumanbh/tko-subs
A tool that can help detect and takeover subdomains with dead DNS records
 alteredsecurity/365-stealer
Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.