
AI-SPM
 dshapi/ai-spm
This opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
ai-securitycloud-securitymisconfiguration+3
14
dshapi/ai-spmThis opensource project dedicated to implementing Enterprise level AI-SPM. By doing so organizations can proactively protect their AI systems from…
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 salesforce/metabadger
Prevent SSRF attacks on AWS EC2 via automated upgrades to the more secure Instance Metadata Service v2 (IMDSv2).
 bishopfox/dufflebag
Search exposed EBS volumes for secrets
 alexzorin/cve-2017-2636-el
Ansible role for workaround for CVE-2017-2636 (Red Hat) - https://access.redhat.com/security/cve/CVE-2017-2636
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 chef-boneyard/bash-shellshock
DEPRECATED: Chef cookbook to audit & remediate "Shellshock" (BASH-CVE-2014-7169)
 lucab85/ansible-role-log4shell
Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).
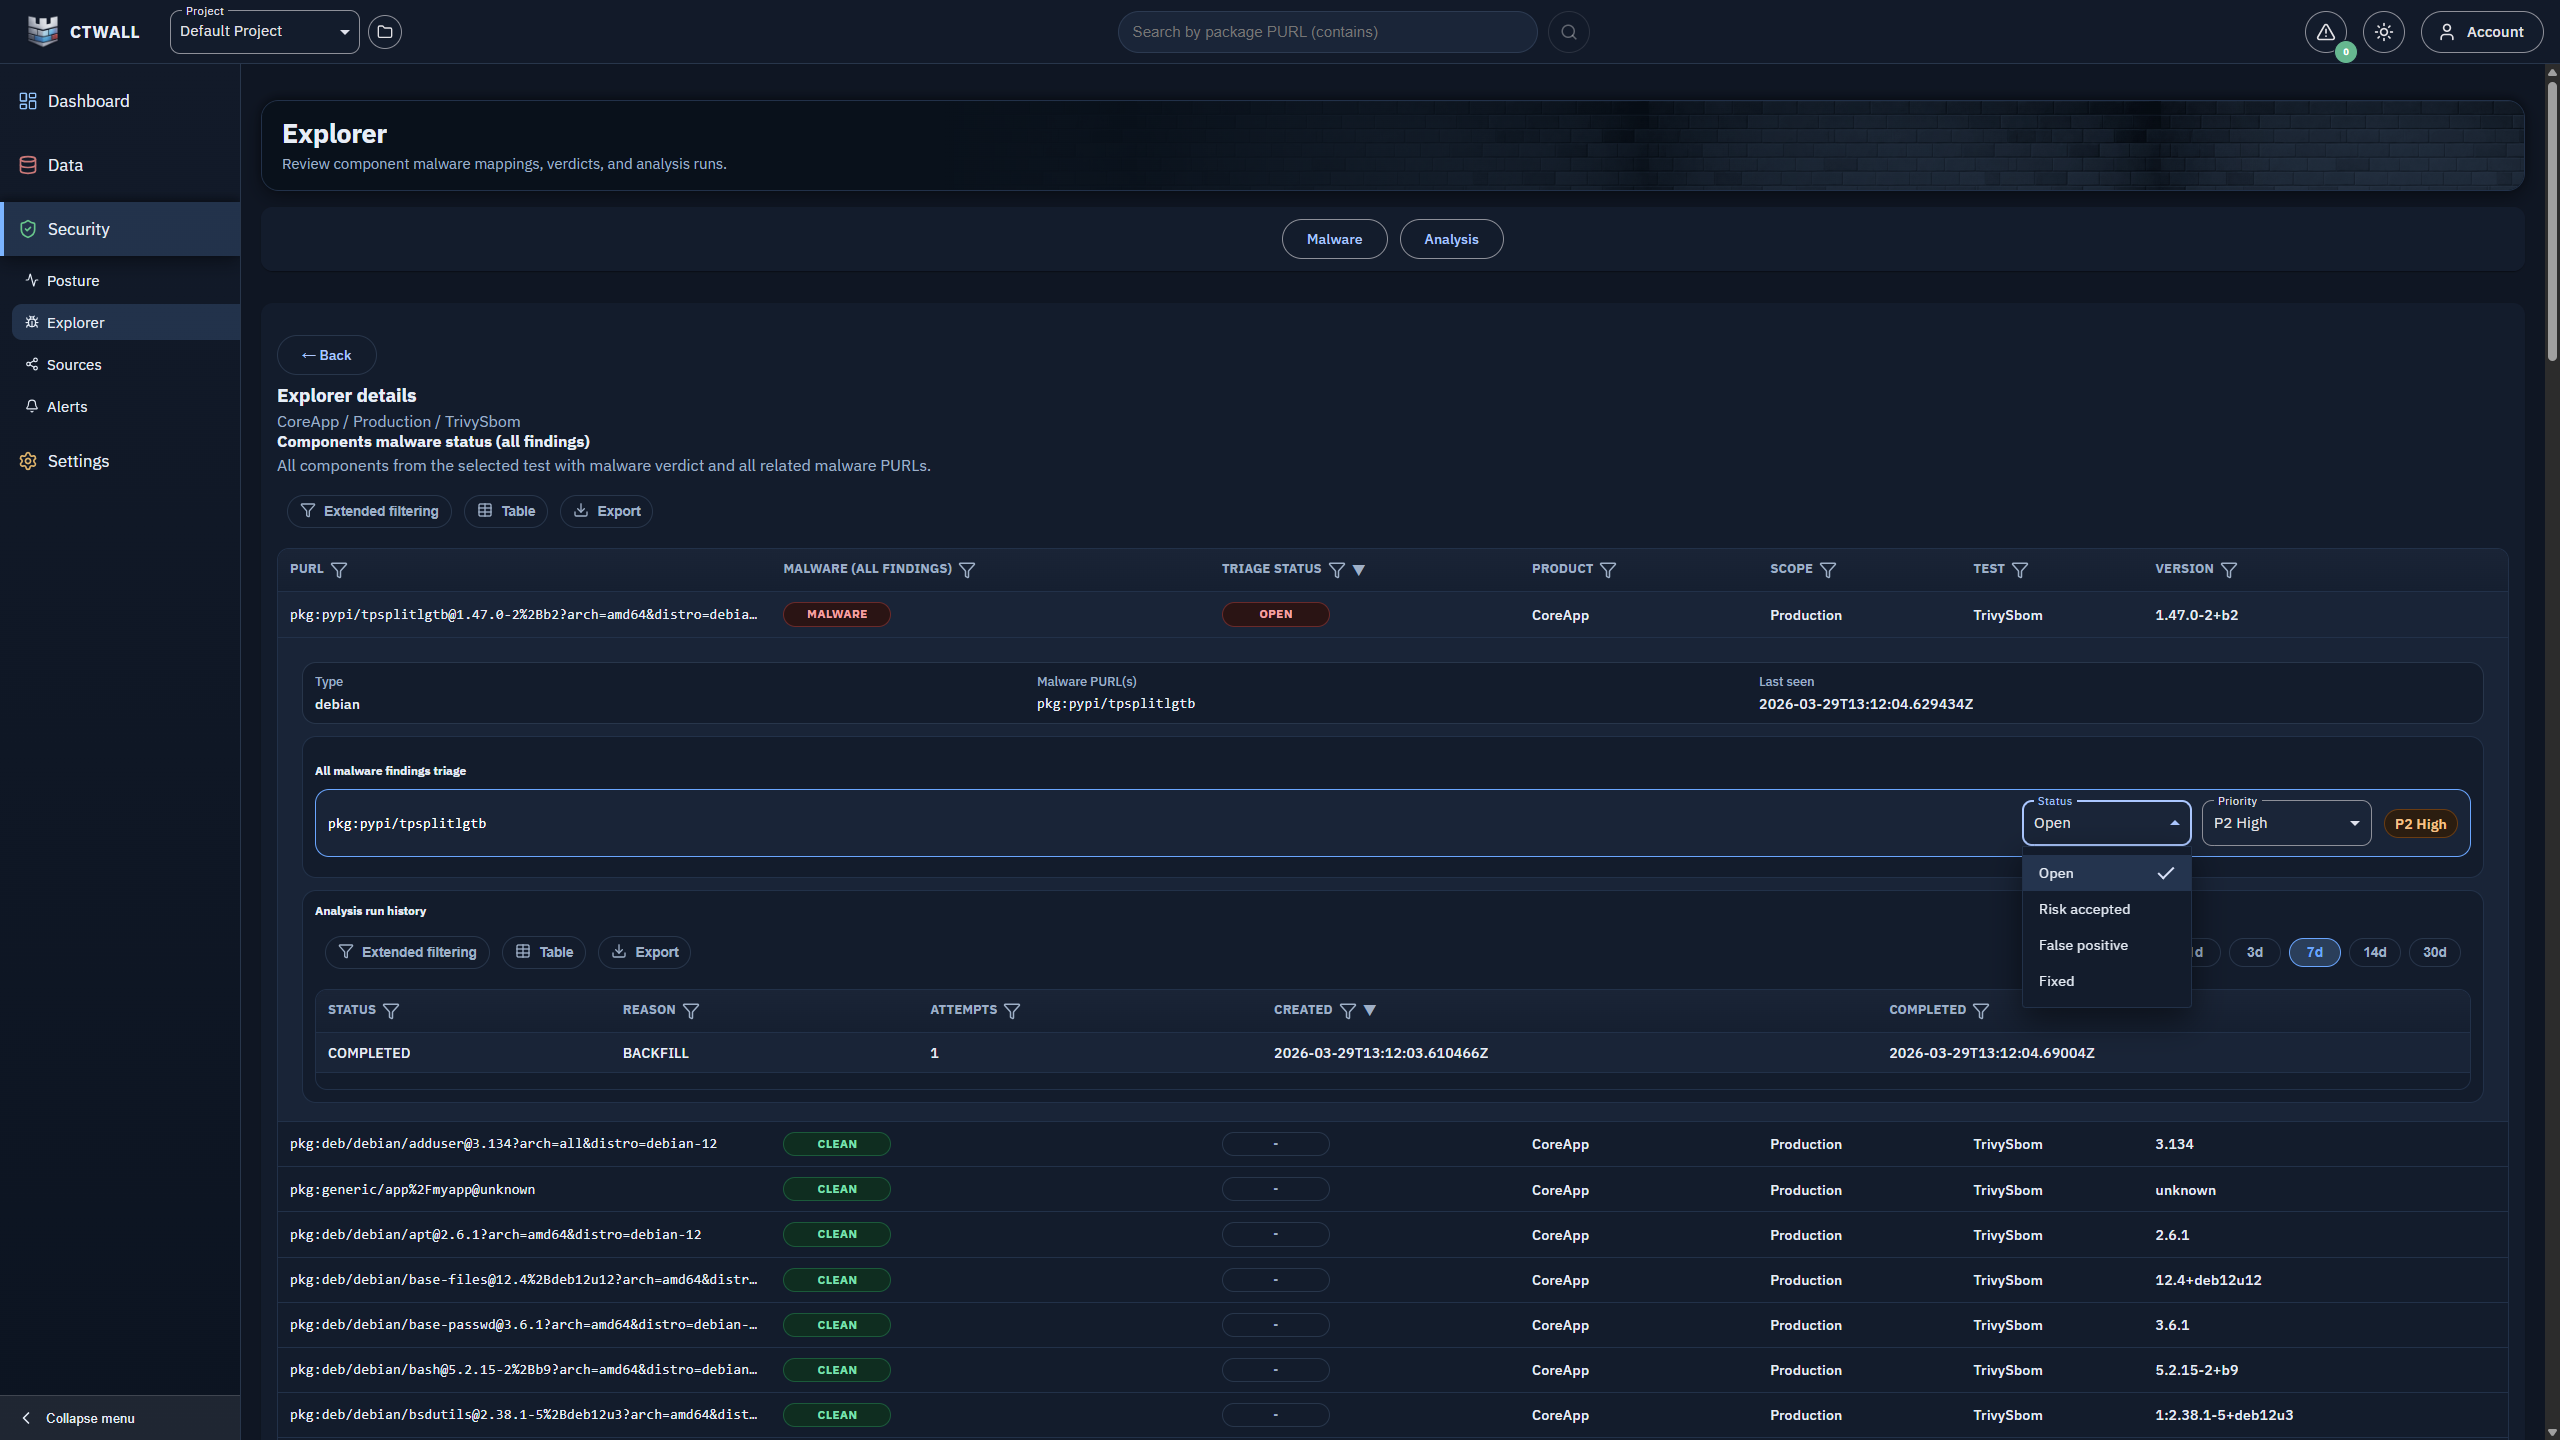 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 redteamoperations/redcloud-os
RedCloudOS is a Cloud Adversary Simulation Operating System for Red Teams to assess the Cloud Security of Leading Cloud Service Providers (CSPs)
 vincentdthe/cve-2025-53786
Proof-of-concept exploit for CVE-2025-53786, demonstrating privilege escalation in hybrid Microsoft Exchange environments via misconfigured trust…
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 bgeesaman/subpath-exploit
Writeup of CVE-2017-1002101 with sample "exploit"/escape
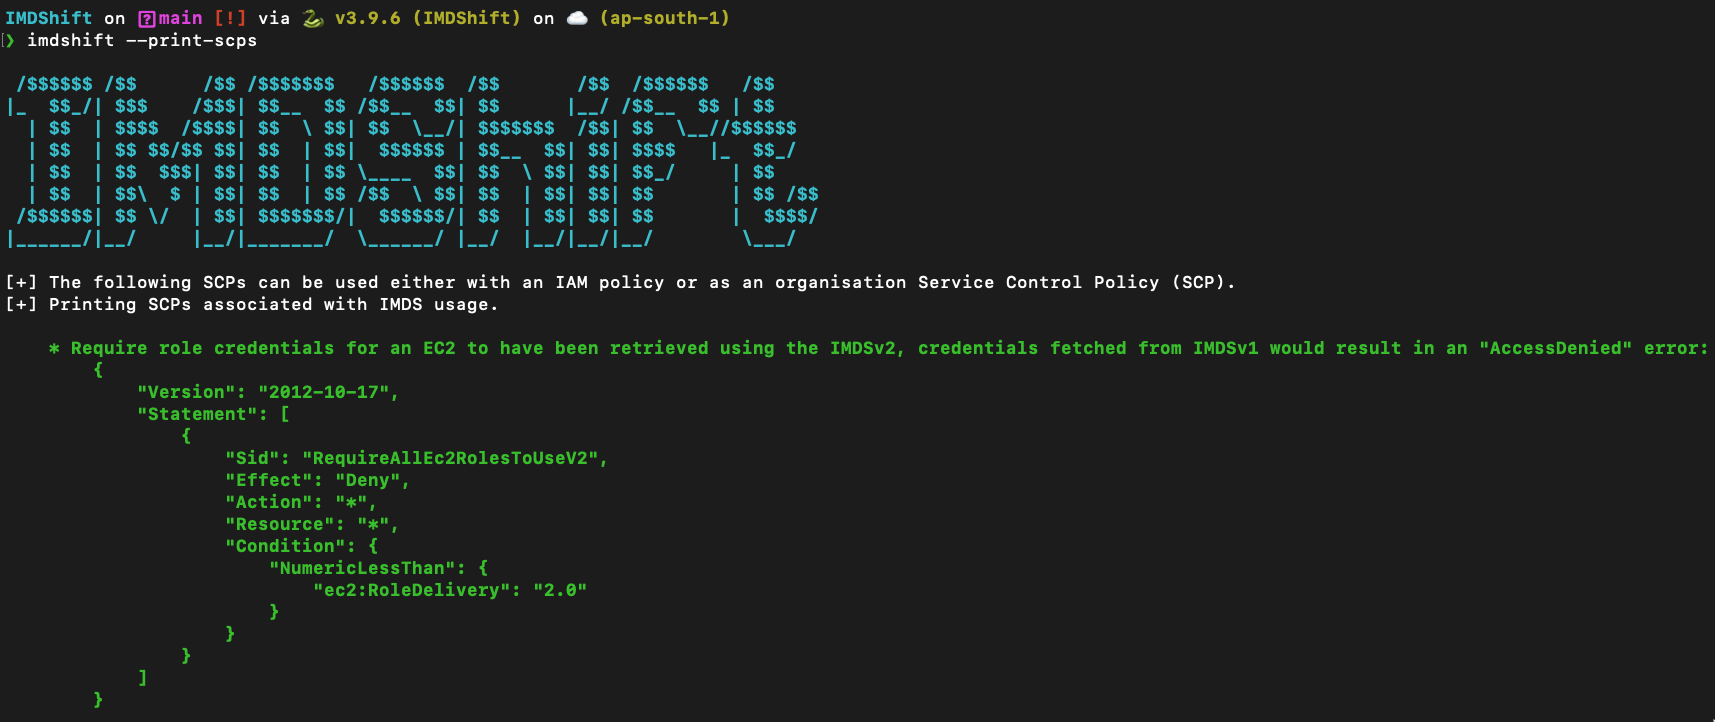 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 certologists/modified-cve-2024-37081-poc
Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.