

DevSecOpsGuideline
 owasp/devsecopsguideline
The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
api-securitycloud-securitycontainer-security+6
1.1k
owasp/devsecopsguidelineThe OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.
 microsoft/windowsprotocoltestsuites
⭐⭐ Join us at SNIA SDC for the SMB3 IO Lab (September 28 - October 1, 2026), see upcoming Interoperability Events
 bishopfox/iam-vulnerable
Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
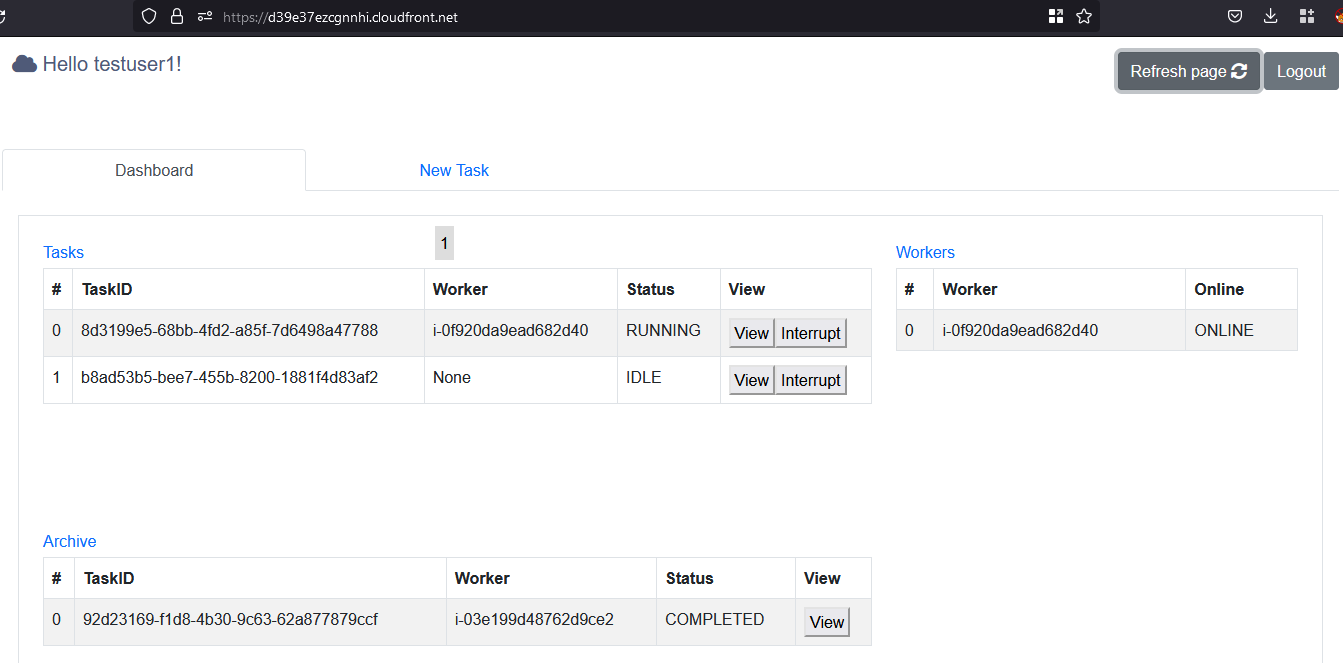 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 claranet/ansible-role-log4shell
Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…