
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
8 results
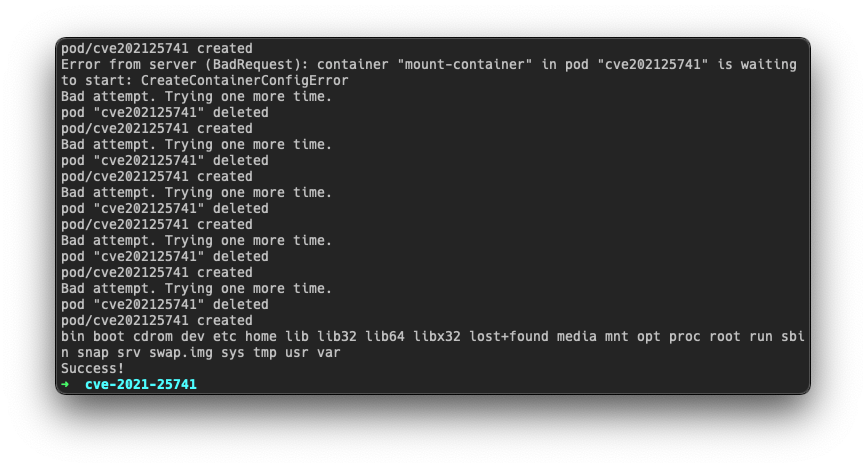
CVE-2021-25741 preview

CVE-2021-25741

GitHubbetep0k/cve-2021-25741

Exploit for CVE-2021-25741 Kubernetes vulnerability allowing host filesystem mount into pods via race condition, with deployment scripts and…
cloud-securitycontainer-escapeexploitation+2
30
4 years ago
grafana-CVE-2024-9264 preview

grafana-CVE-2024-9264

GitHubpatrickpichler/grafana-cve-2024-9264

Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
cloud-securitycontainer-securityeducation+2
1 year ago
HTB-Facts-Writeup preview

HTB-Facts-Writeup

GitHubkarimelsheikh1/htb-facts-writeup

HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.

cloud-securityctfeducation+7
5 months ago
CVE-2026-64849.yaml preview

CVE-2026-64849.yaml

GitHubzavisco/cve-2026-64849.yaml

Detects unauthenticated MLflow webhook SSRF (CVE-2026-64849) that accesses internal or cloud metadata services and leaks response details via…
api-security-testingcloud-securityexploitation+3
1 month ago
2025-Oracle-SSO-LDAP-Attack-Post-Incident-Written-Report preview

2025-Oracle-SSO-LDAP-Attack-Post-Incident-Written-Report

GitHubjwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report

Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…

authenticationcloud-securityeducation+3
25 days ago
AADInternals preview

AADInternals

GitHubgerenios/aadinternals

PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
authenticationcloud-securityidentity-access-management+2
1.7k11 months ago
cloudfoxable preview

cloudfoxable

GitHubbishopfox/cloudfoxable

Create your own vulnerable by design AWS penetration testing playground
cloud-infrastructure-securitycloud-securityctf+3
4754 months ago
CVE-Requests-1896609 preview

CVE-Requests-1896609

GitHubwilliam31212/cve-requests-1896609

CVE-2025-59376, CVE-2025-59377

cloud-securitycommand-and-controlcontainer-security+4
11 year ago