
365-Stealer
 alteredsecurity/365-stealer
Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
cloud-securitypenetration-testingphishing+1
592
alteredsecurity/365-stealerAutomates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
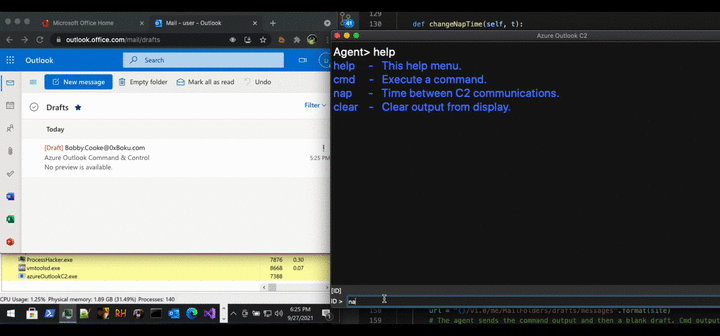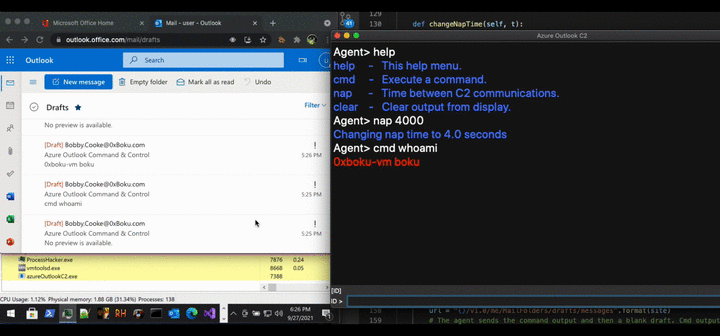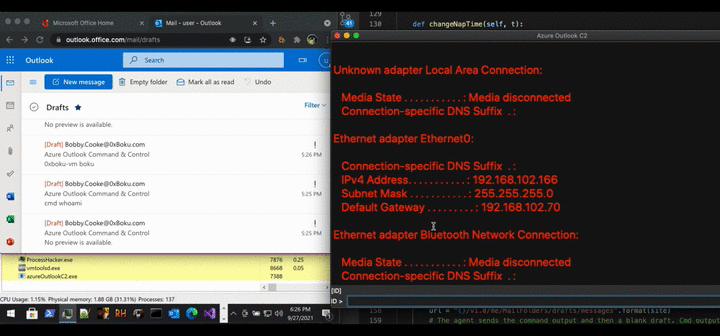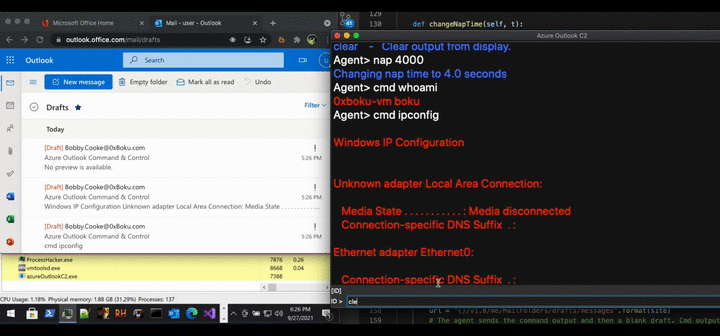 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
 im007/cve-2023-23397
PowerShell script to detect and remediate CVE-2023-23397 privilege escalation vulnerability in Microsoft Outlook and Exchange environments.