kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

A tool to find subdomains and interesting things hidden inside, external Javascript files of page, folder, and Github.

Security Tool to Look For Interesting Files in S3 Buckets

Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…

Uncover a target's cloud infrastructure, files, and apps across major providers (AWS, Azure, GCP) using unauthenticated enumeration with concurrent…

The source files and tools needed to build the OWASP Cornucopia decks in various languages

Rust library and format specification for creating and loading Independent Guest Virtual Machine (IGVM) files, supporting hardware-isolated VMs with…

BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…

Tool to detect and monitor GitHub org users' public repositories for secrets and sensitive files

A simple file-based scanner to look for potential AWS access and secret keys in files

Verdict-as-a-Service SDKs: Analyze files for malicious content

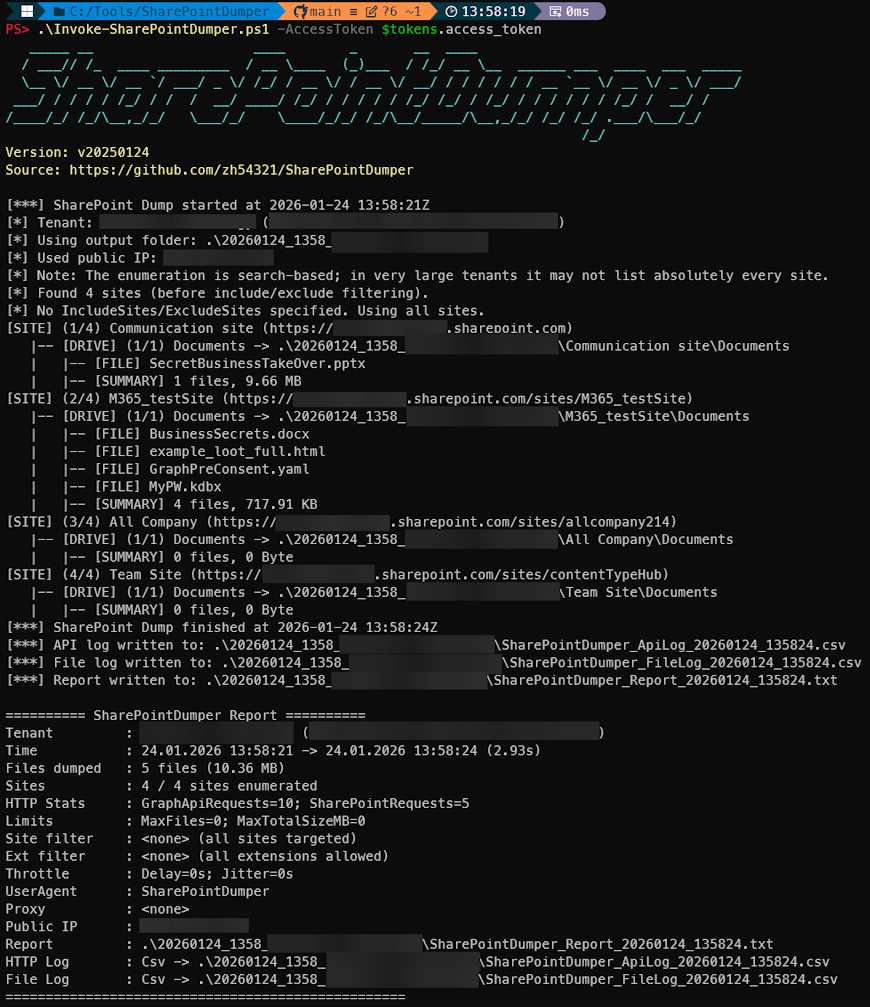
PowerShell SharePoint extraction + auditing tool for red/blue/purple teams. Enumerates all SharePoint sites/drives a user can access via Microsoft…

Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.

Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…

Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…

Whitebox evaluation of effective S3 object permissions, to identify publicly accessible files.

Ansible role to detect Log4Shell (CVE-2021-44228) by scanning filesystem and open files for vulnerable JAR/WAR files, reporting version and…

Proof-of-concept exploit for CVE-2024-52510 demonstrating signature bypass in Nextcloud's E2EEv2 protocol, enabling server-side decryption of…