
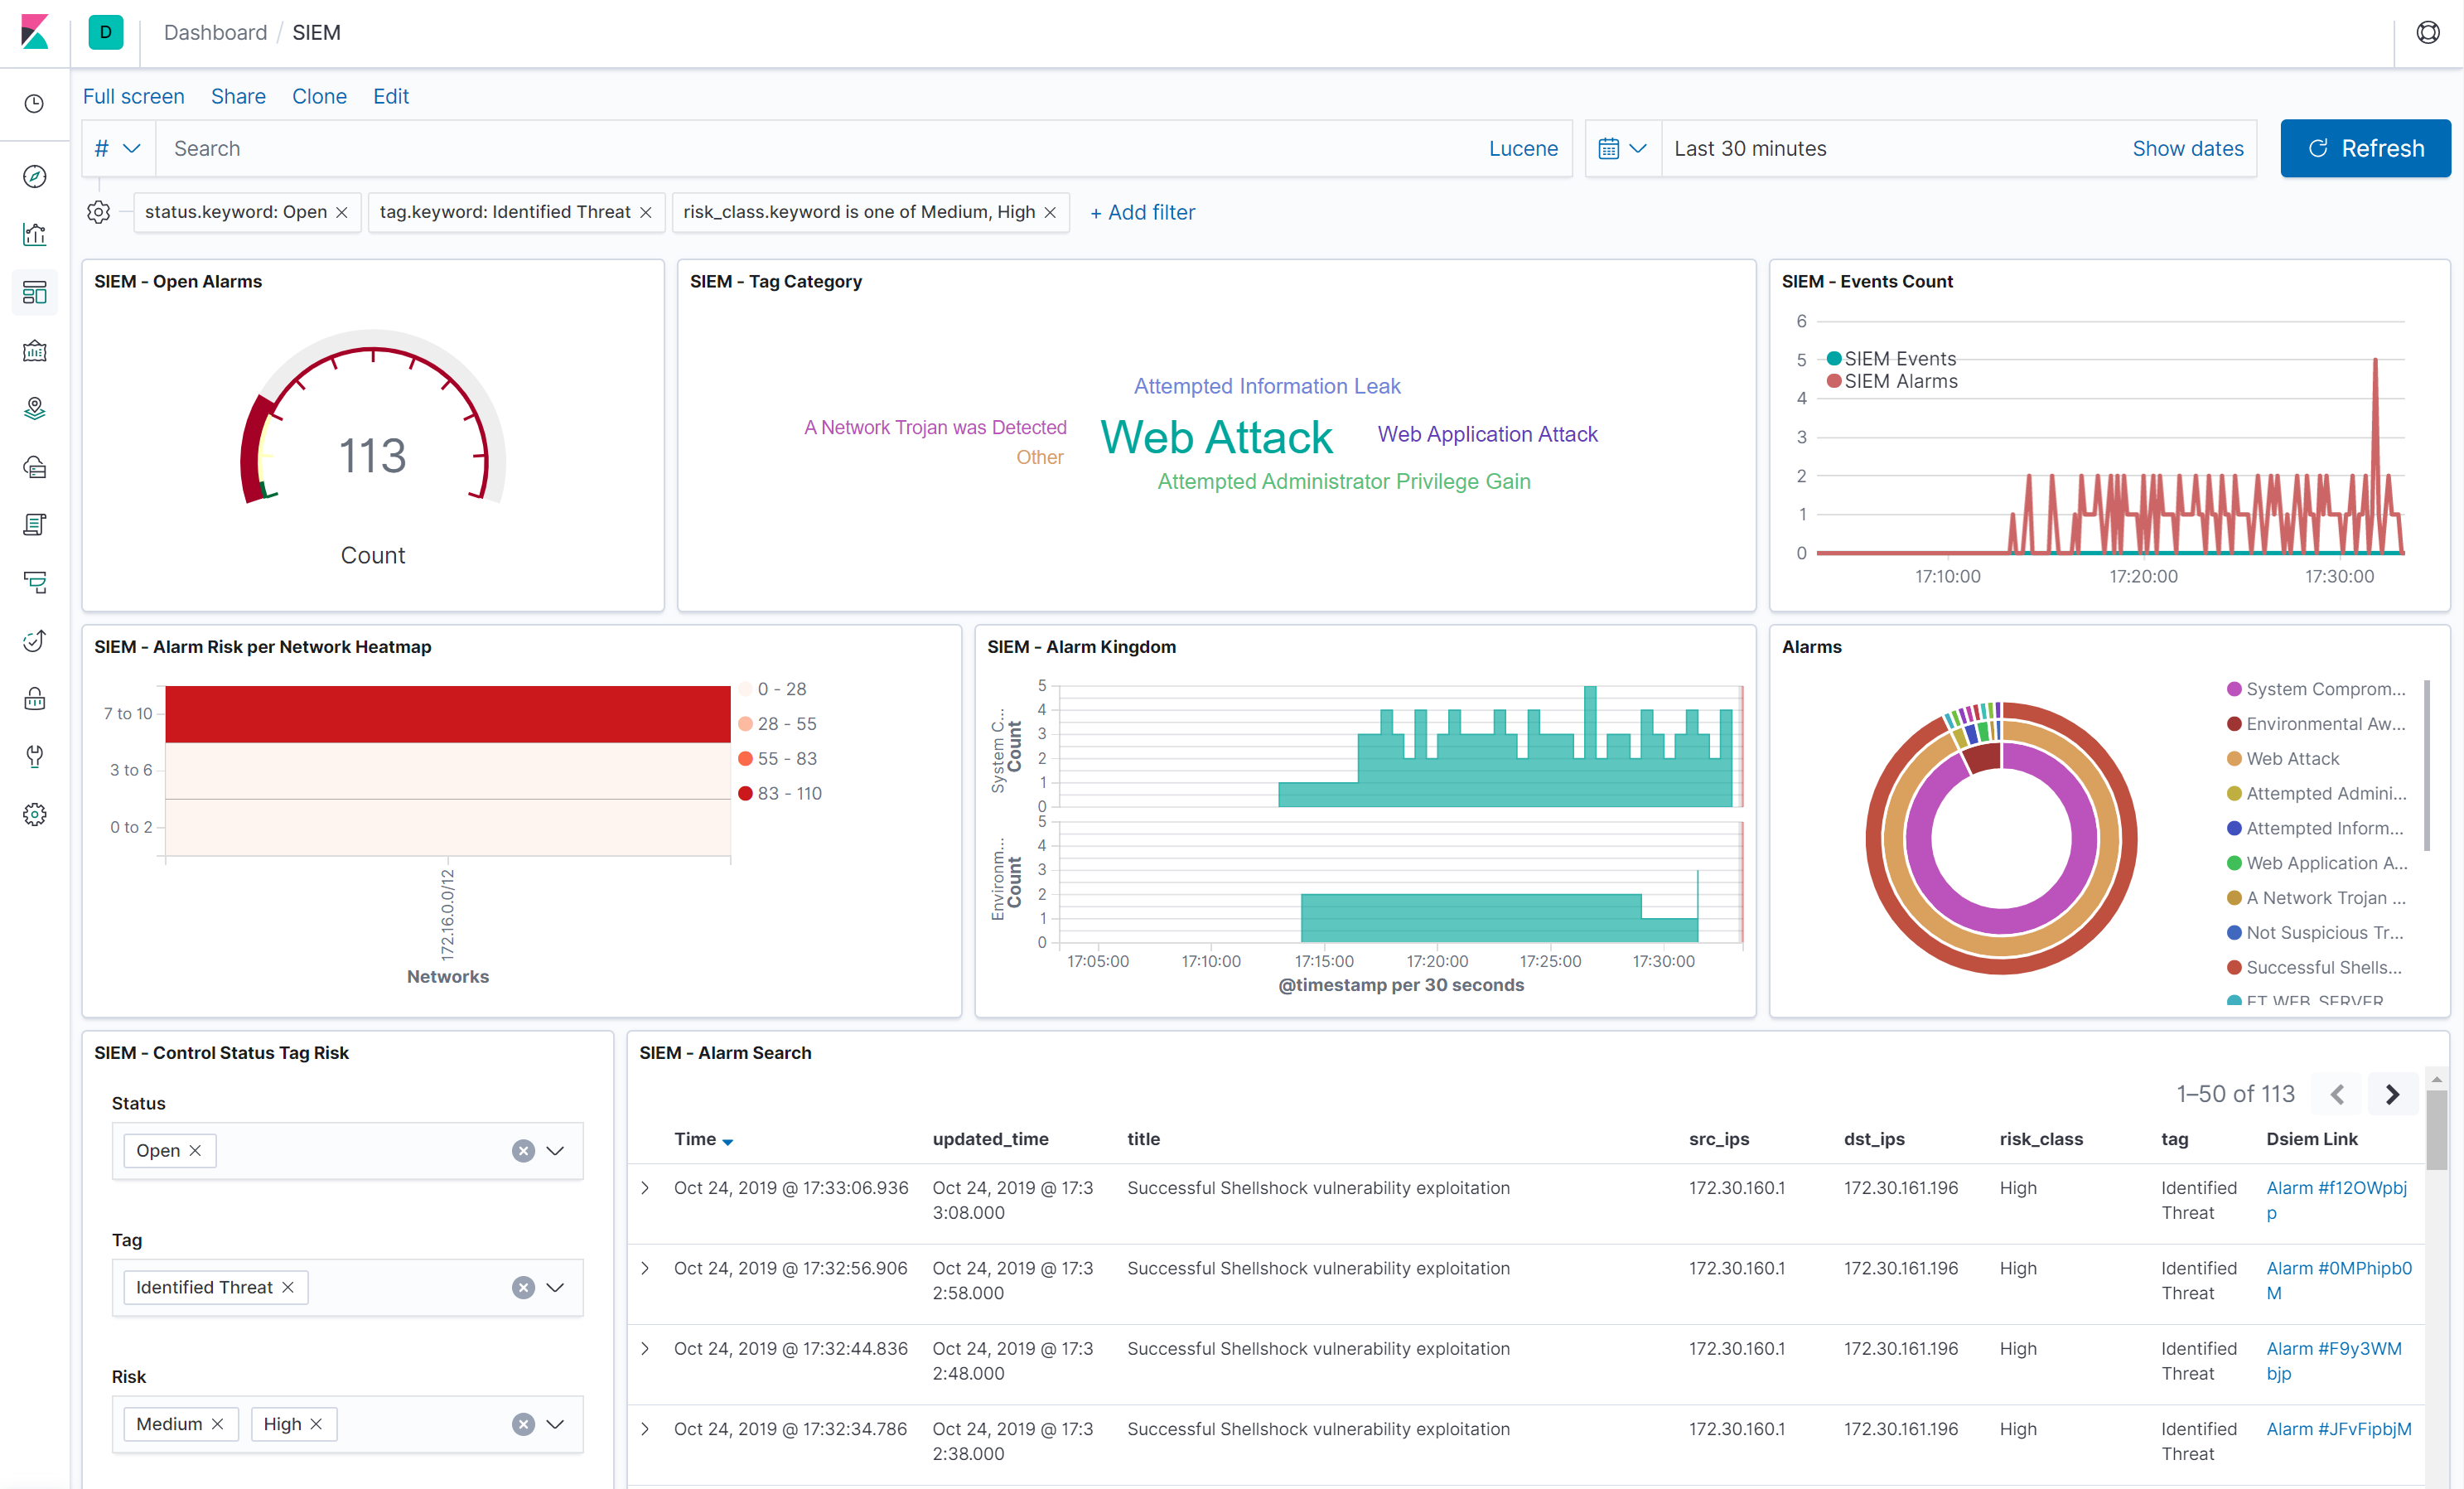
dsiem
 defenxor/dsiem
Security event correlation engine for ELK stack
cloud-securityincident-responseintrusion-detection+3
defenxor/dsiemSecurity event correlation engine for ELK stack
 corelight/corelightforsecops
Chronicle parser for CORELIGHT and related information.
 unfold-security/cve-2026-41940-detection
Detection signatures for CVE-2026-41940 and shemas for cPanel logs
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…