
GuardScan
 ntanwir10/guardscan
100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
ai-securityapi-securitycloud-security+8
ntanwir10/guardscan100% Free & Open Source • Privacy-First Security Scanning and AI Code Review CLI
 cryptomator/cryptomator
Cross-platform client-side encryption for cloud storage with AES-256, encrypted filenames, obfuscated folder structure, and transparent virtual drive…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 mongodb/kingfisher
Detect secrets + live validation. Map blast radius. Revoke fast. Use the CLI or embed in Rust and Python.
 dockur/windows
Run Windows inside a Docker container with KVM acceleration, automatic installation, and customizable resources. Supports multiple Windows versions,…
 joelgmsec/cloudtopolis
Zero Infrastructure Password Cracking
 dbeaver/dbeaver
Free universal database tool and SQL client
 nagwww/s3-leaks
Curated timeline of AWS S3 bucket misconfigurations, exposed data, and leaked IAM credentials, with incident links for cloud security defenders and…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
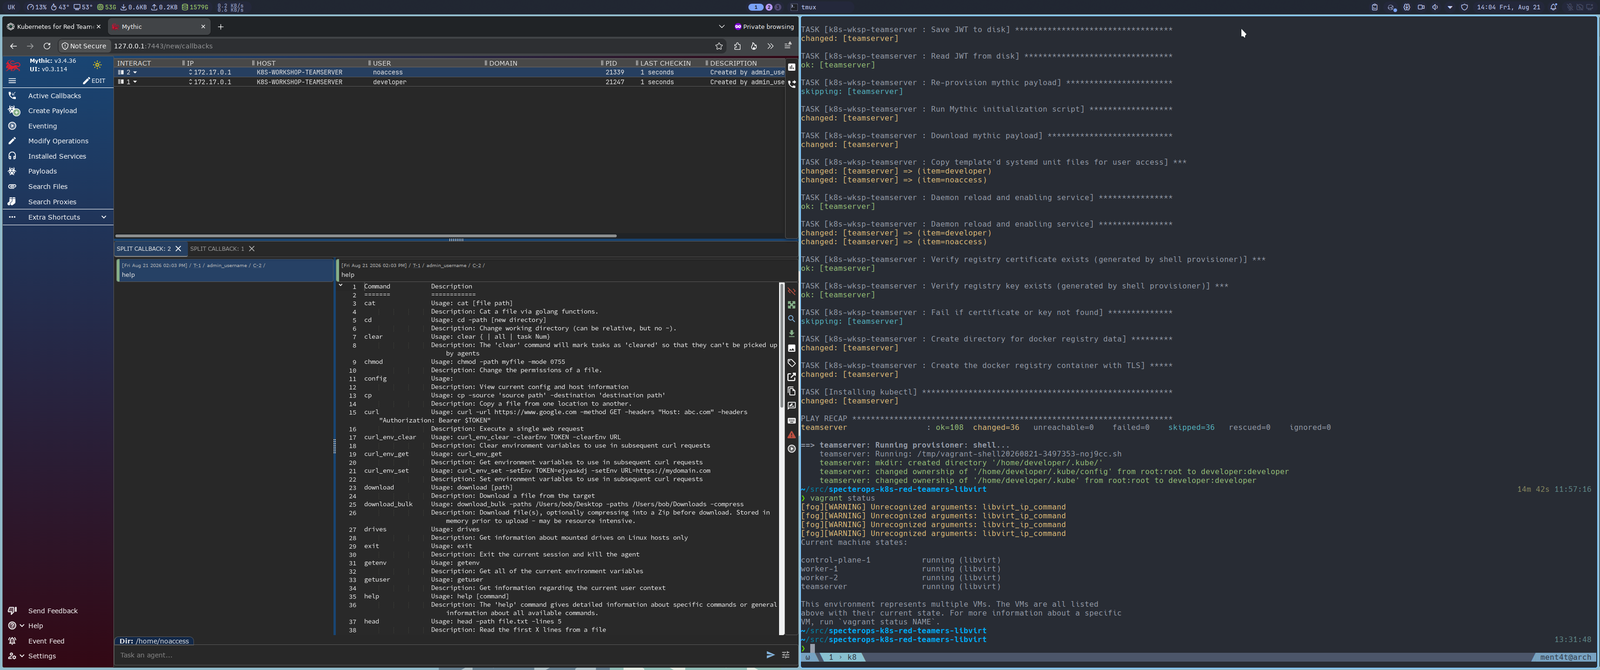 gregdurys/specterops-k8s-red-teamers-libvirt-patch
Unofficial libvirt patch for the free SpecterOps Kubernetes for Red Teamers lab
 samhaxr/assamee
AES-256 file and directory encryption tool with automatic upload to Anonfiles cloud storage, requiring a download ID for decryption and retrieval.
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM
 iknowjason/awesome-cloudsec-labs
Awesome free cloud native security learning labs. Includes CTF, self-hosted workshops, guided vulnerability labs, and research labs.
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 rocketchat/rocket.chat
The Secure CommsOS™ for mission-critical operations