
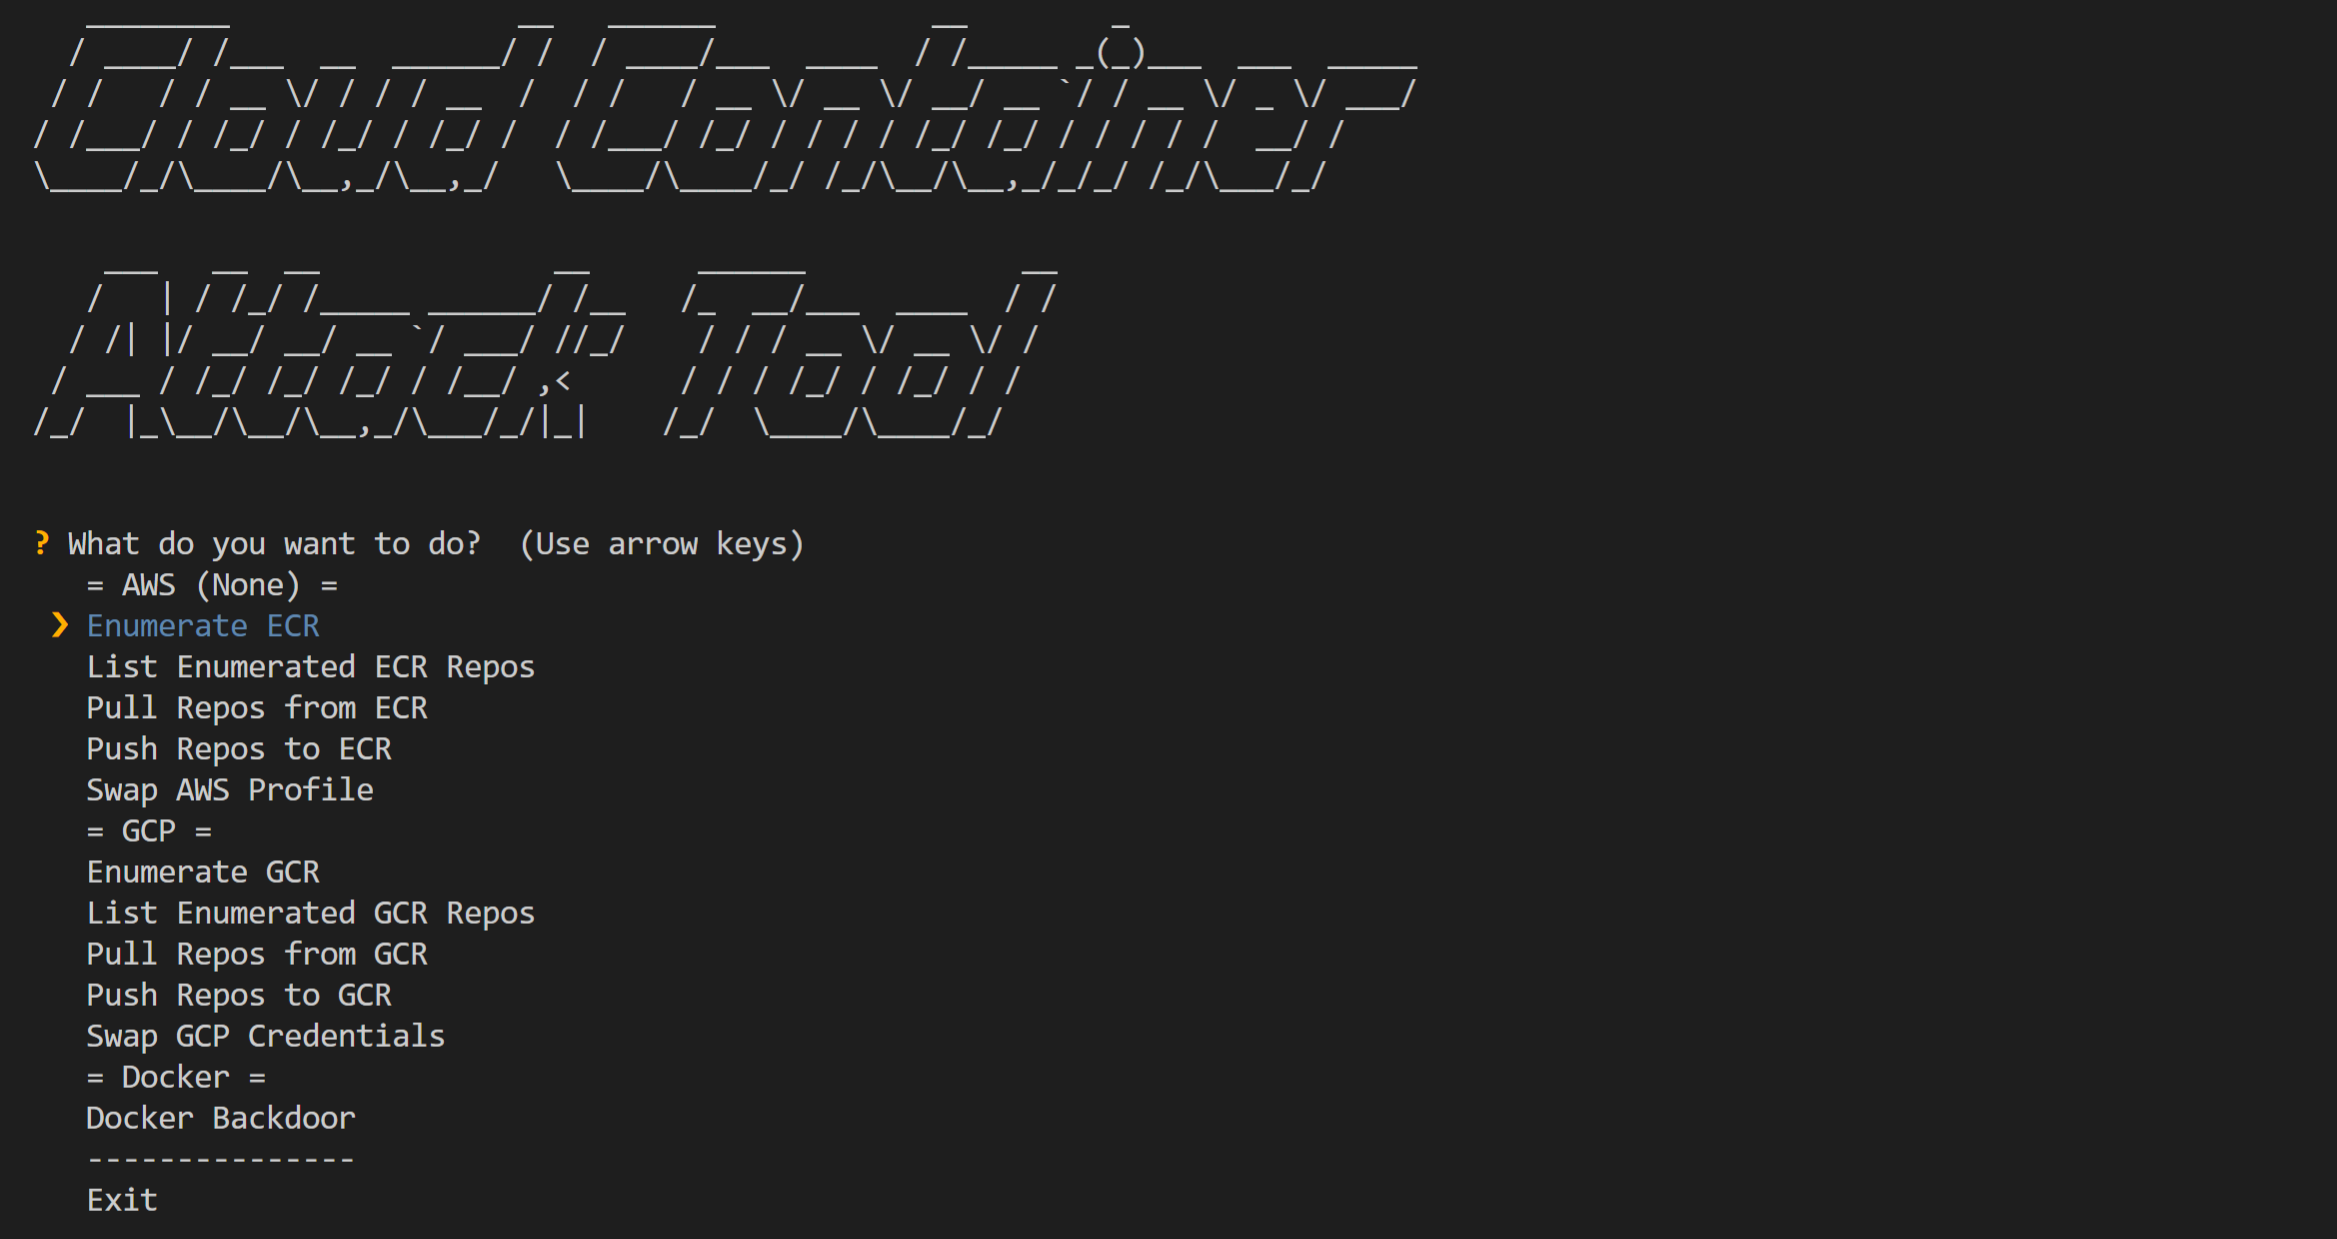
ccat
 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
cloud-securitycontainer-securityexploitation+1
6536 years ago
rhinosecuritylabs/ccatCloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
 shoucheng3/alibaba__nacos_cve-2021-44667_2-0-3
Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…
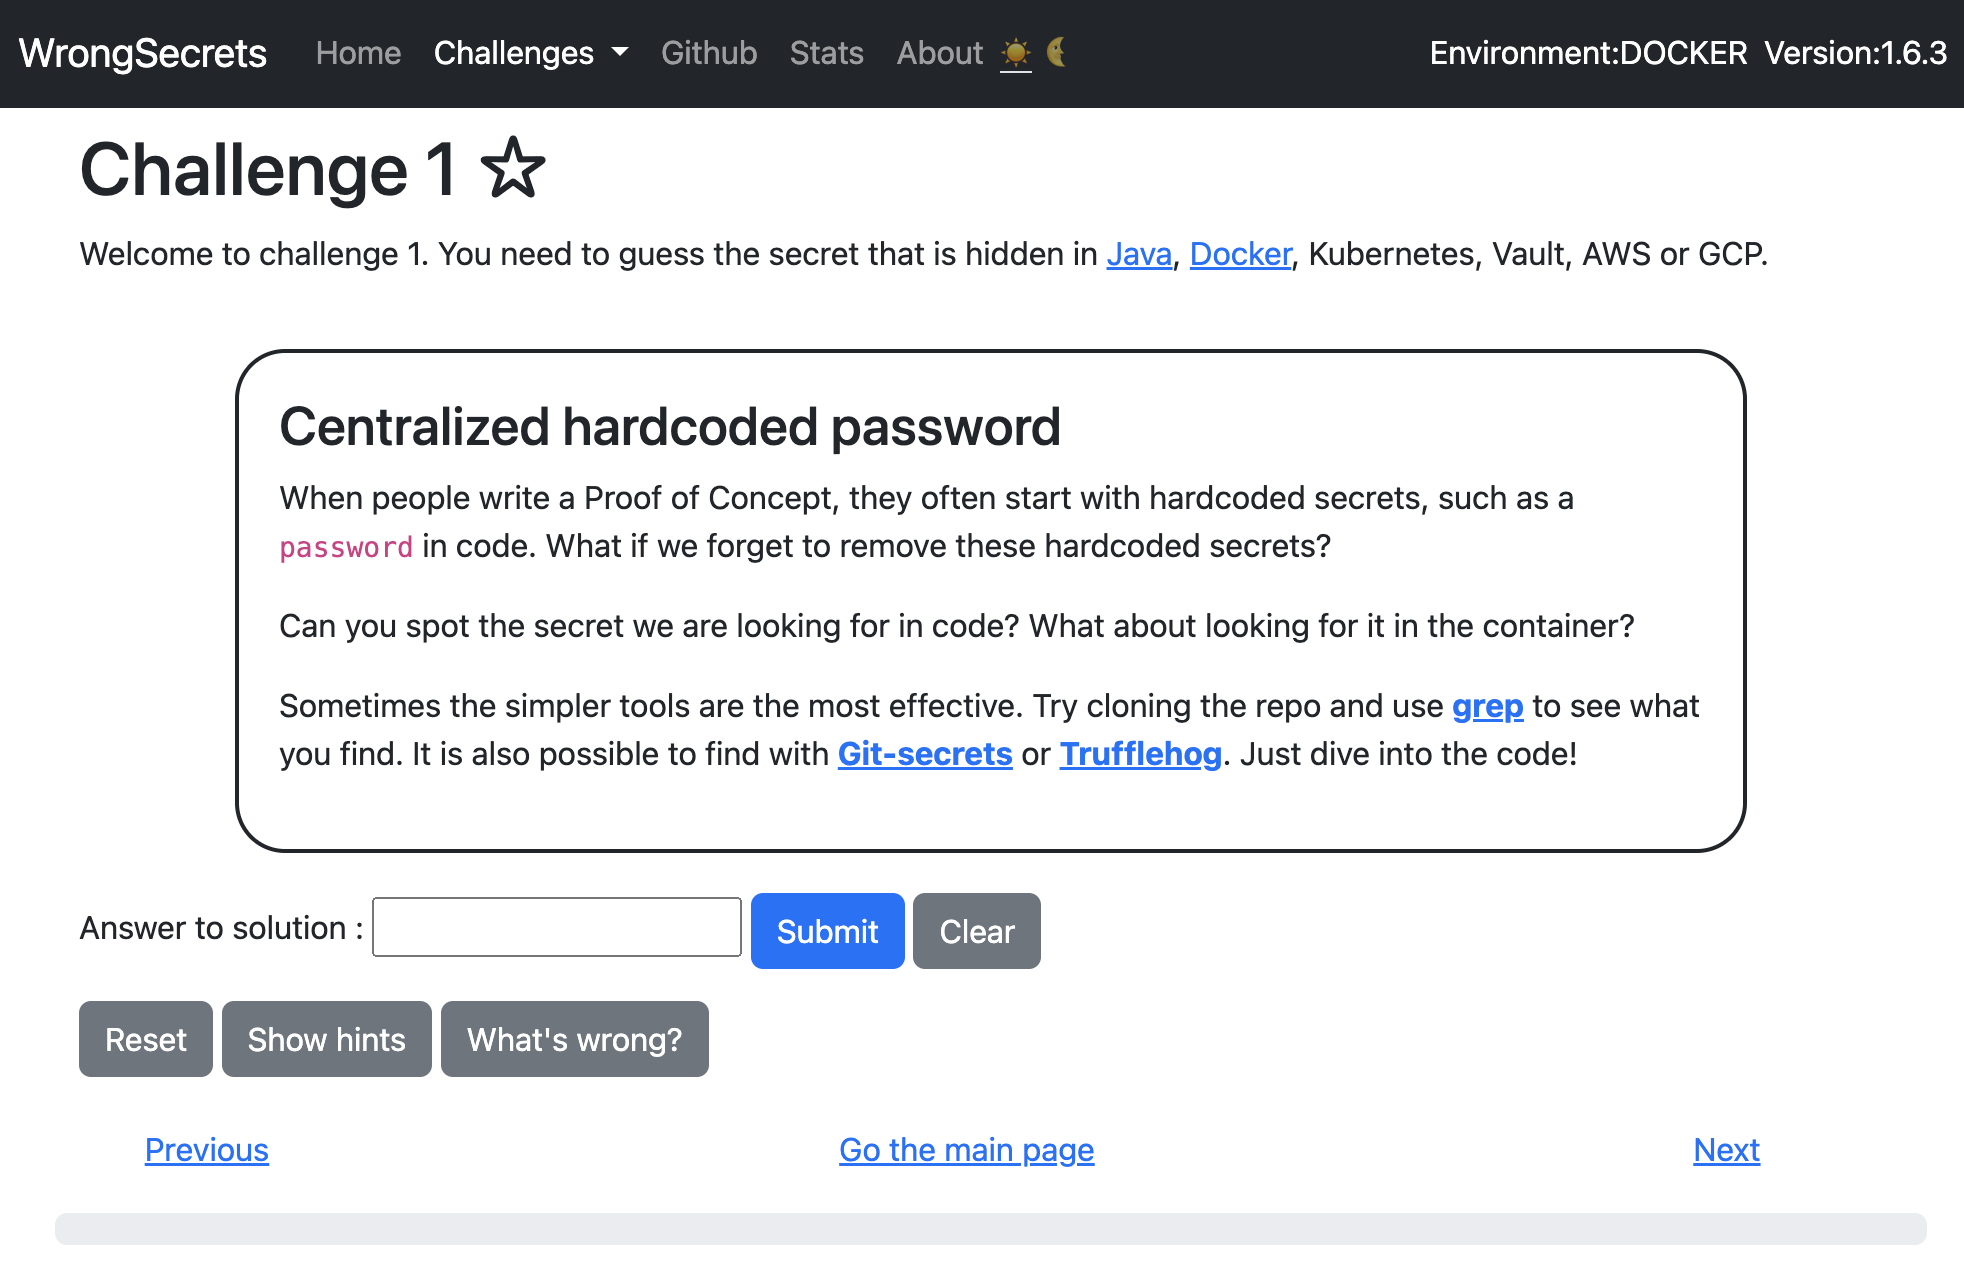 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.
 farenhytee/database-sentinel
Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…
 graphenex/graphenex
Automated System Hardening Framework
 synacktiv/mindmaps
Azure mindmap for penetration tests
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
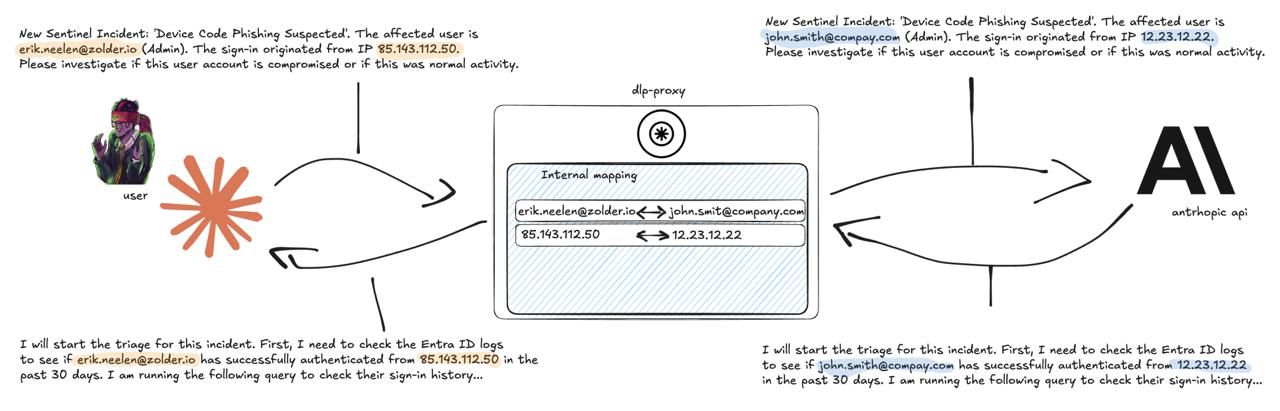 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials