

Mindmaps
 synacktiv/mindmaps
Azure mindmap for penetration tests
cloud-securitycurated-resourceseducation+3
synacktiv/mindmapsAzure mindmap for penetration tests
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 anchore/anchore-engine
A service that analyzes docker images and scans for vulnerabilities
 arzaan789/keyguard
Scan codebases and GCP projects for exposed API credentials
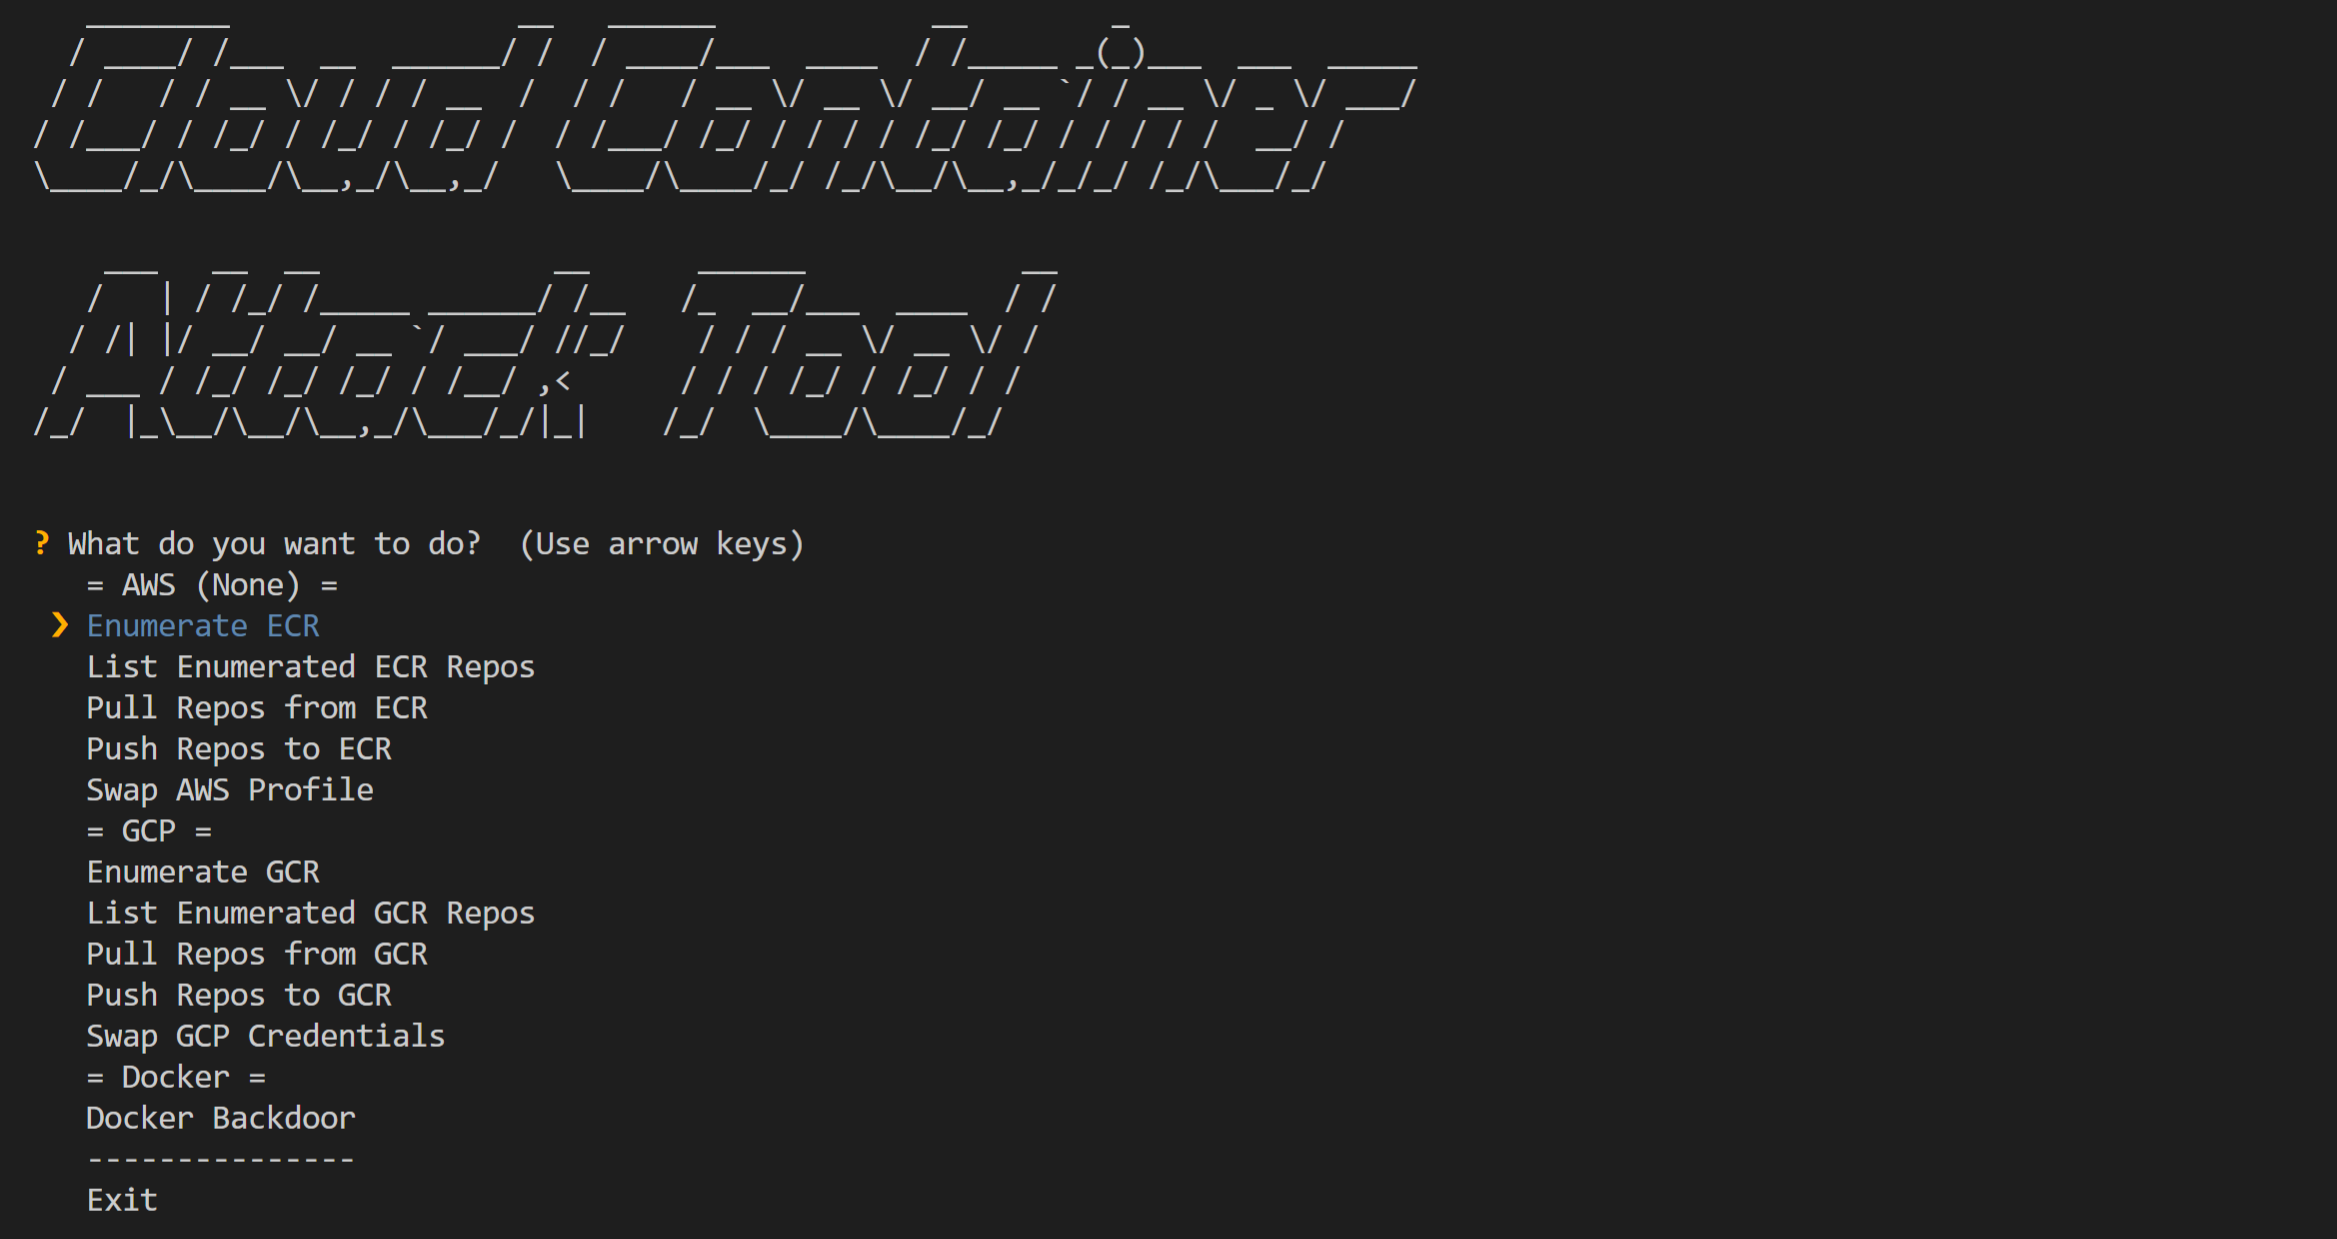 rhinosecuritylabs/ccat
Cloud Container Attack Tool (CCAT) is a tool for testing security of container environments.
 graphenex/graphenex
Automated System Hardening Framework
 ustayready/python-pentesting
Just a repo of random Python scripts to get pentesters started with the Python language on engagements.
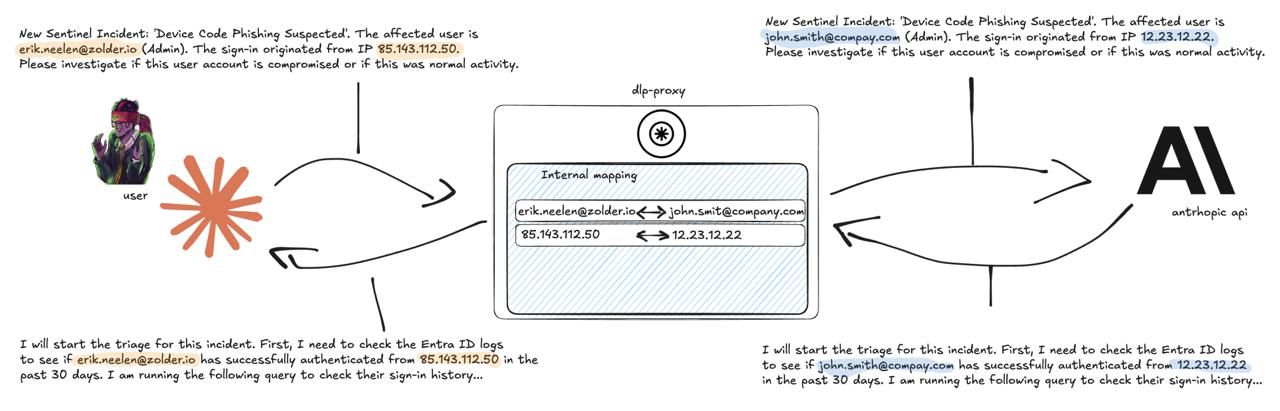 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
 shoucheng3/alibaba__nacos_cve-2021-44667_2-0-3
Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 permanet/permanet
Cryptographically verifiable web archiving. Playwright capture → SHA-256 Merkle hash → Bitcoin-anchored OpenTimestamps → permanent Arweave storage.
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431