

fleet
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
cloud-securityconfiguration-auditingdefensive-tools+4
7.0k
fleetdm/fleetOpen-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 mindersec/minder
Software Supply Chain Security Platform
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
 justinsteven/advisories
Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 rjt-gupta/cve-2021-33104
CVE-2021-33104 - Improper access control in the Intel(R) OFU software
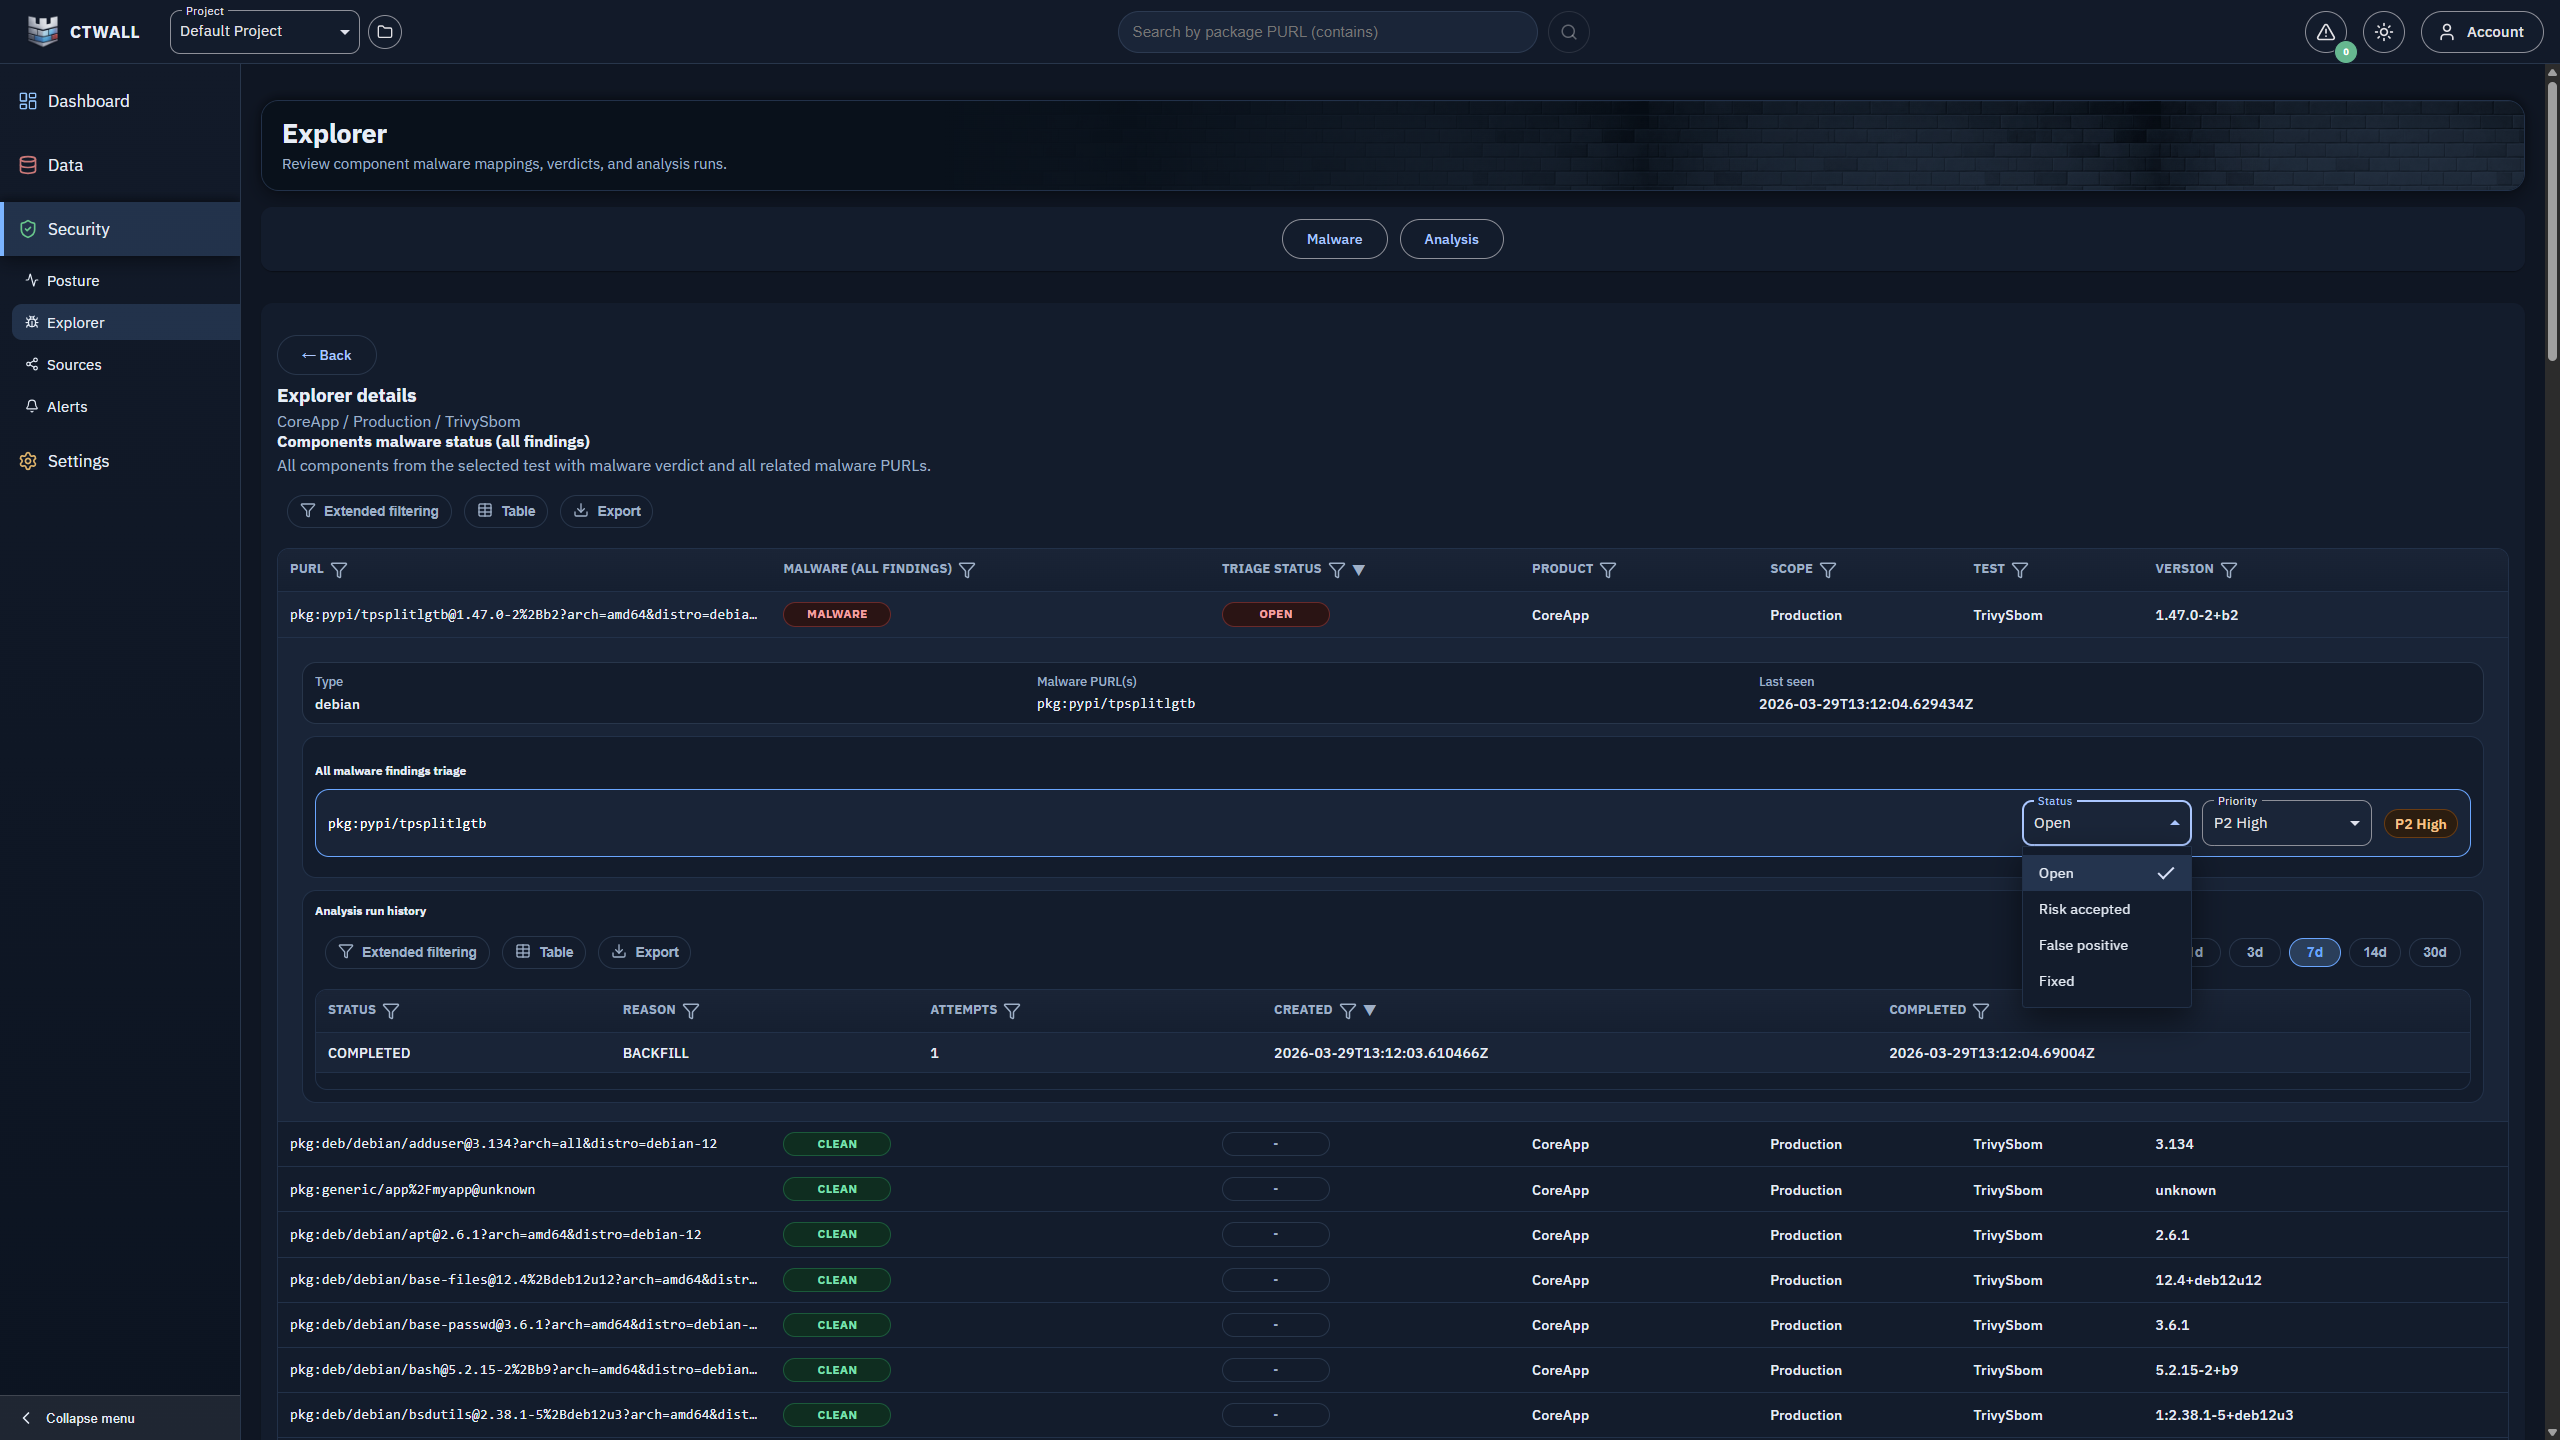 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 horrister/solarwinds-sunburst-cve-2020-10148
Curated vulnerability writeups with full technical analysis, proof-of-concept scripts, IOC listings, and remediation guidance for real-world software…
 cyberdudebivash/cyberdudebivash-5g-core-key-rotation-ghost-admin-auditor
Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…
 openclarity/kubeclarity
KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 nolabs-ai/nono
agent runtime security - zero trust, zero setup, zero latency agent sandboxing
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 securecodebox/securecodebox
Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…
 owasp/cornucopia
The source files and tools needed to build the OWASP Cornucopia decks in various languages
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.