bug-bounty-reports-desai-vinayak

Bug bounty and vulnerability research reports by Desai Vinayak — includes CVE-2023-50290 (Apache Solr) and Zscaler subdomain takeover findings.

Bug bounty and vulnerability research reports by Desai Vinayak — includes CVE-2023-50290 (Apache Solr) and Zscaler subdomain takeover findings.

Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…

PowerShell script to detect and remediate CVE-2023-23397 privilege escalation vulnerability in Microsoft Outlook and Exchange environments.

Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.

Python script to detect CVE-2023-3128 authentication bypass in Grafana via Azure AD email claim validation. Checks Azure AD SSO configuration and…

This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…

Ansible playbook that applies a global JVM environment variable to mitigate the Log4j CVE-2021-44228 remote code execution vulnerability across all…

A Bash script to mitigate the CVE-2024-6387 vulnerability in OpenSSH by providing an option to upgrade to a secure version or apply a temporary…

Shell script to detect and mitigate CVE-2024-6387 vulnerability by auditing system configurations and applying recommended fixes.

A full-stack AI Red Teaming platform securing AI ecosystems via Agent Scan, Skills Scan, MCP scan, AI Infra scan and LLM jailbreak evaluation.

Personal repository of security advisory disclosures covering vulnerabilities in web, cloud, infrastructure, and open-source software.

POC of SecureWorks' recent Azure Active Directory password brute-forcing vuln

IngressNightmare POC. world first non-blind remote execution exploitation with multi-advanced exploitation methods. allow on disk exploitation.…

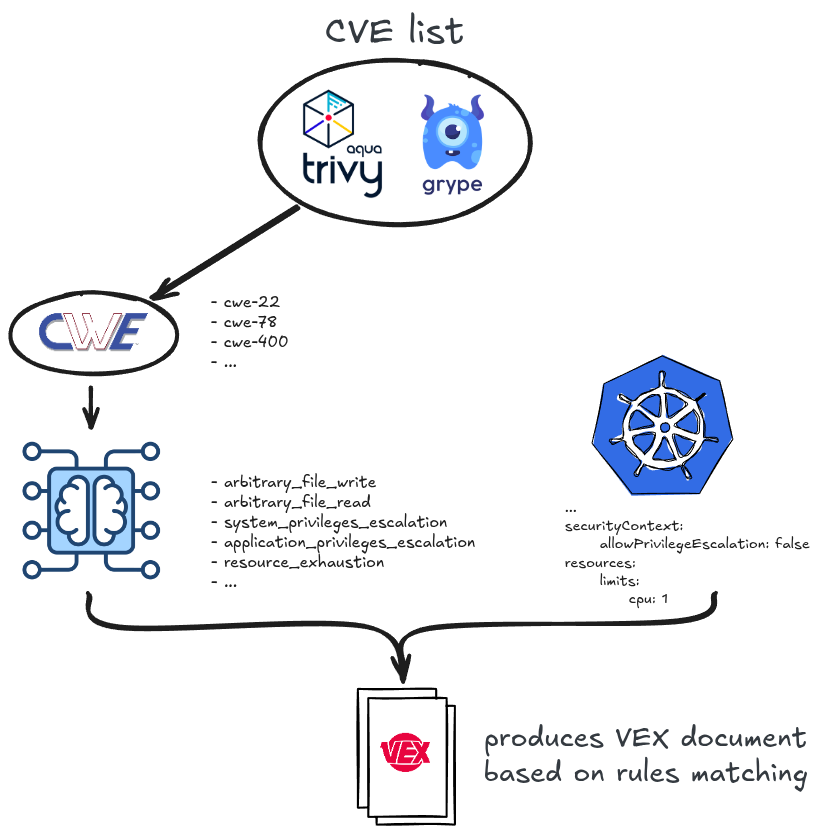
Suppress vulnerabilities applying Kubernetes context to scans

A collection of my public security advisories.

A tool that checks if a TorchServe instance is vulnerable to CVE-2023-43654

A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492

Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)