CVE-2026-32646
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
api-securityauthenticationcloud-security+6
michaeladamgroberman/cve-2026-32646CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 zaidmkh32/cve-2025-27136-xxe-locals3
Proof of Concept for CVE-2025-27136 (XXE in Local-S3)
 michaeladamgroberman/cve-2026-28766
CVE-2026-28766: Missing Authentication on User Account Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 michaeladamgroberman/cve-2026-55726
CVE-2026-55726: Publicly Listable Azure Blob Storage Container (device logs) - Gardyn (ICSA-26-183-03)
 contrast-security-oss/cve-2021-44228
Professional Service scripts to aid in the identification of affected Java applications in TeamServer
 surendrapuppala7/cve-2025-45955
Proof-of-concept exploit for CVE-2025-45955 demonstrating Server-Side Request Forgery (SSRF) in DonWeb Ferozo hosting platform, enabling internal…
 c1ph3rx13/cve-2023-28432
CVE-2023-28432 Minio Information isclosure Exploit
 lhxhl/minio-cve-2023-28432
Detects and exploits MinIO information disclosure vulnerability (CVE-2023-28432) with single and batch URL scanning, written in Go.
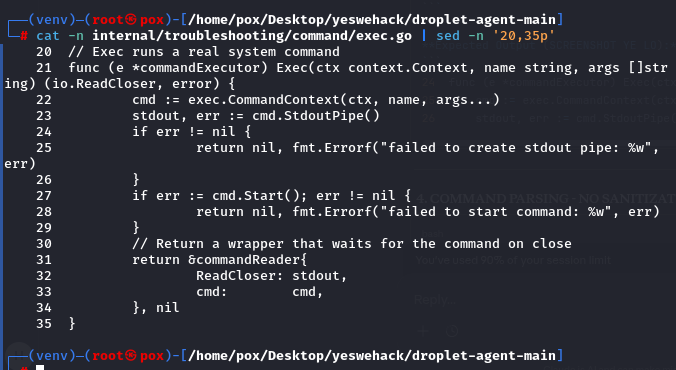 poxsky/cve-2026-24516-digitalocean-rce.
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).
 rrespxwnss/cve-2025-63571
Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 china-china/minio_cve-2023-28432_exp
Exploit for MinIO information disclosure vulnerability CVE-2023-28432, allowing unauthorized access to sensitive environment variables.
 optiv/knockknock
Enumerate valid users within Microsoft Teams and OneDrive with clean output.
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io