
cve-2024-7646
 dovics/cve-2024-7646
PoC CVE-2024-7646
cloud-securitycontainer-securityexploitation+3
11 year ago
dovics/cve-2024-7646PoC CVE-2024-7646

 i3r1h0n/ingressnightterror
My view on IngressNightmare vulnerability (CVE-2025-1974)
 rjhaikal/poc-ingressnightmare-cve-2025-1974
POC IngressNightmare (CVE-2025-1974), modified from https://github.com/yoshino-s/CVE-2025-1974
 c1ph3rx13/cve-2023-28432
CVE-2023-28432 Minio Information isclosure Exploit
 josephgodwinkimani/cloudpanel-2.4.2-cve-2024-44765-recovery
How to "recover" a CloudPanel server affected by the CVE-2024-44765 vulnerability
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 lhxhl/minio-cve-2023-28432
Detects and exploits MinIO information disclosure vulnerability (CVE-2023-28432) with single and batch URL scanning, written in Go.
 dolutech/patch-manual-cve-2025-26465-e-cve-2025-26466
Patch Manual para a correção das CVE-2025-26465-e-CVE-2025-26466, para sistemas sem update do OpenSSH
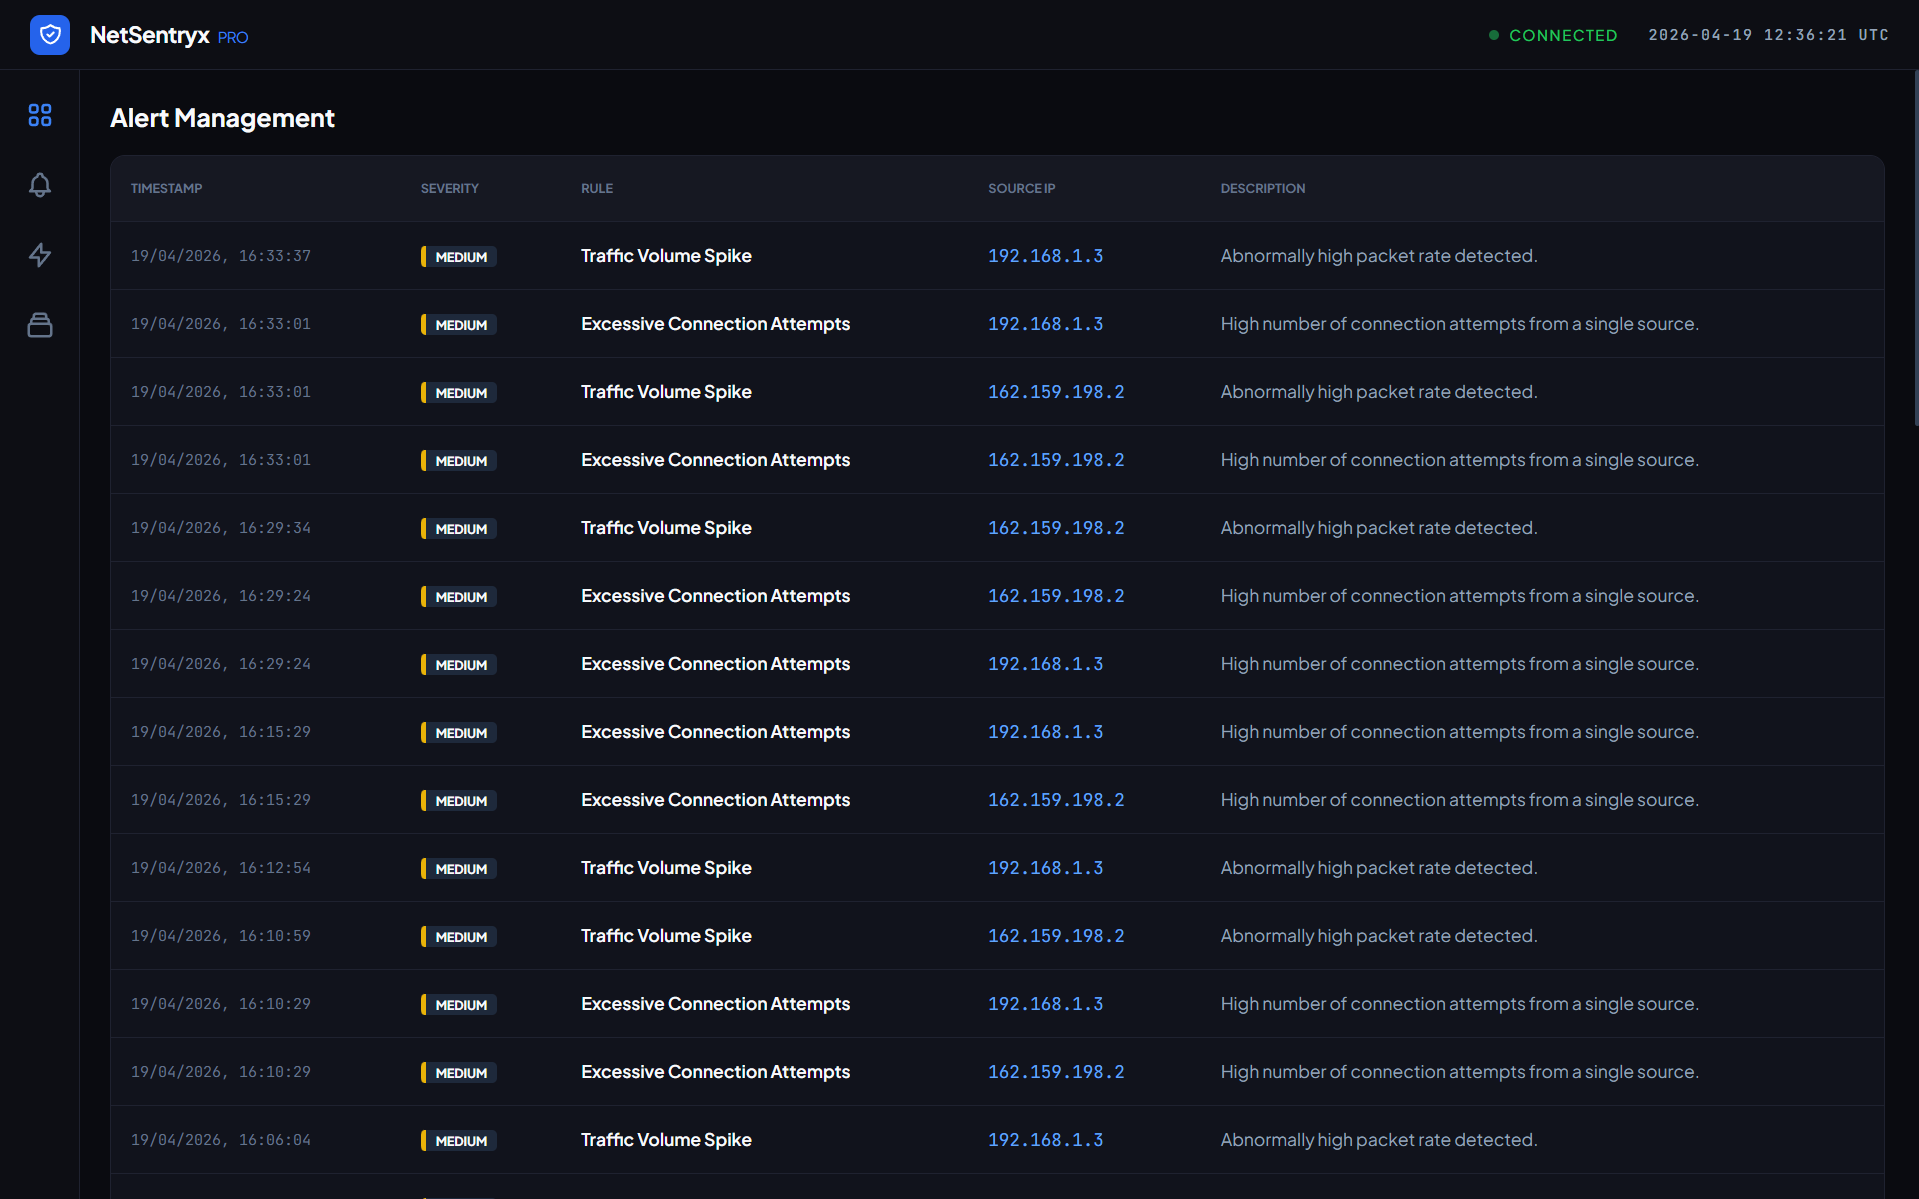 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 there-was-a-bird/triton-cve-2025-23320
Docker-based proof-of-concept demonstrating CVE-2025-23320 in NVIDIA Triton inference server, exploiting shared memory key leakage to trigger an…
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)
 niccox/patch-openssl-cve-2014-0291_cve-2015-0204
Ansible playbook to patch OpenSSL against CVE-2014-0291 and CVE-2015-0204 on Red Hat family servers, with automated service restart and verification.
 glutenfree69/zigraceexploit
CVE-2021-25741 POC in Zig
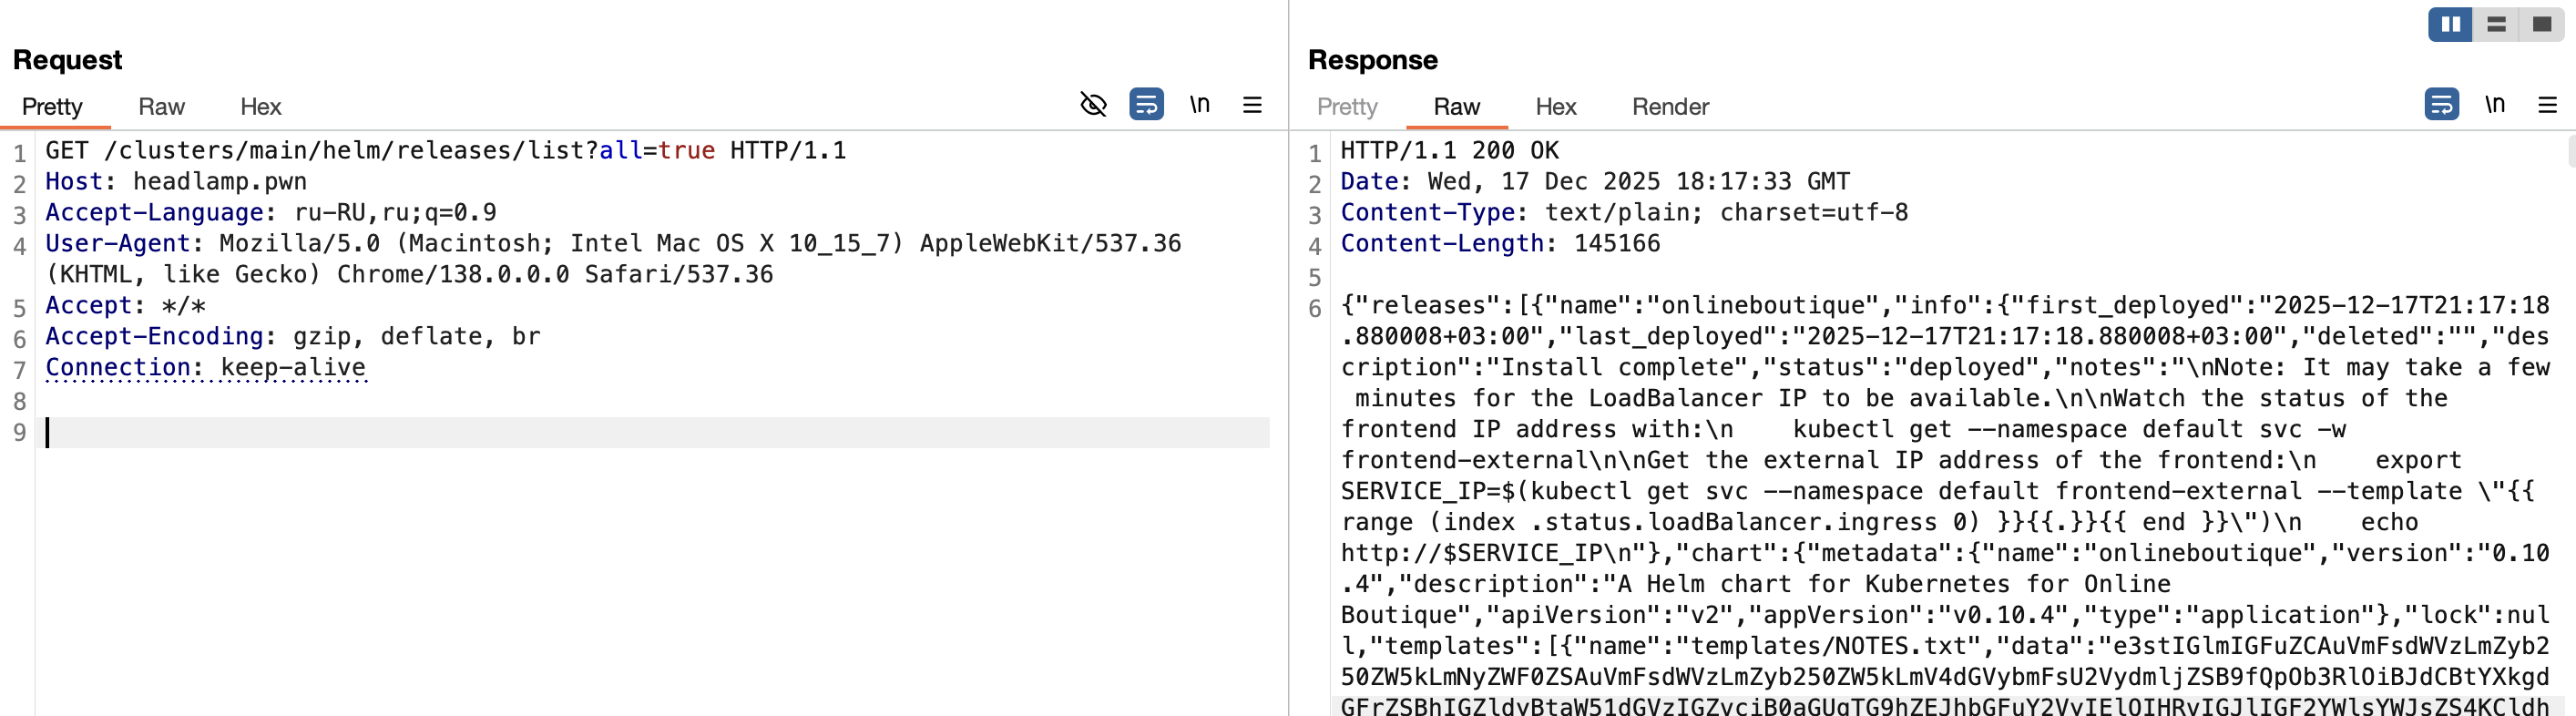 r0binak/cve-2025-14269
CVE-2025-14269 PoC exploit
 gunyakit/cve-2025-1974-poc-exploit
Kubernetes Ingress-nginx RCE (IngressNightmare)
