keycloak__keycloak_CVE-2022-4137_20-0-3

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Open source identity and access management solution providing single sign-on, user federation, and centralized authentication for modern applications…

Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…

Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…

CVE-2016-4468

Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…

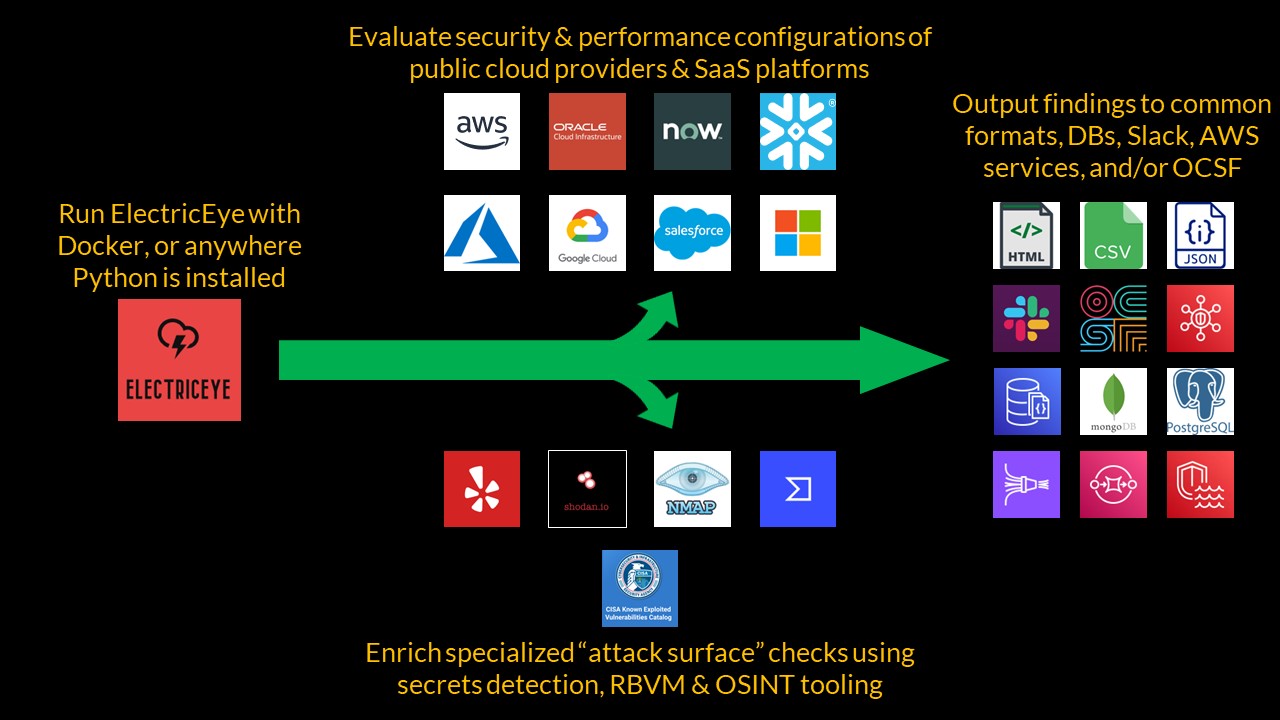
ElectricEye is a multi-cloud, multi-SaaS Python CLI tool for Asset Management, Security Posture Management & Attack Surface Monitoring supporting…

Gixy-Next: NGINX Configuration Security Scanner & Performance Checker

Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.

Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…

Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.

Production-grade tool for detecting & remediating CVE-2026-0622 (Ghost Admin privilege escalation & master key exposure in 5G core software).

Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.

Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…

Expose and detail an unauthenticated stored XSS vulnerability in the Google Cloud Vertex AI Python SDK affecting versions 1.98.0 to 1.130.9.

Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…

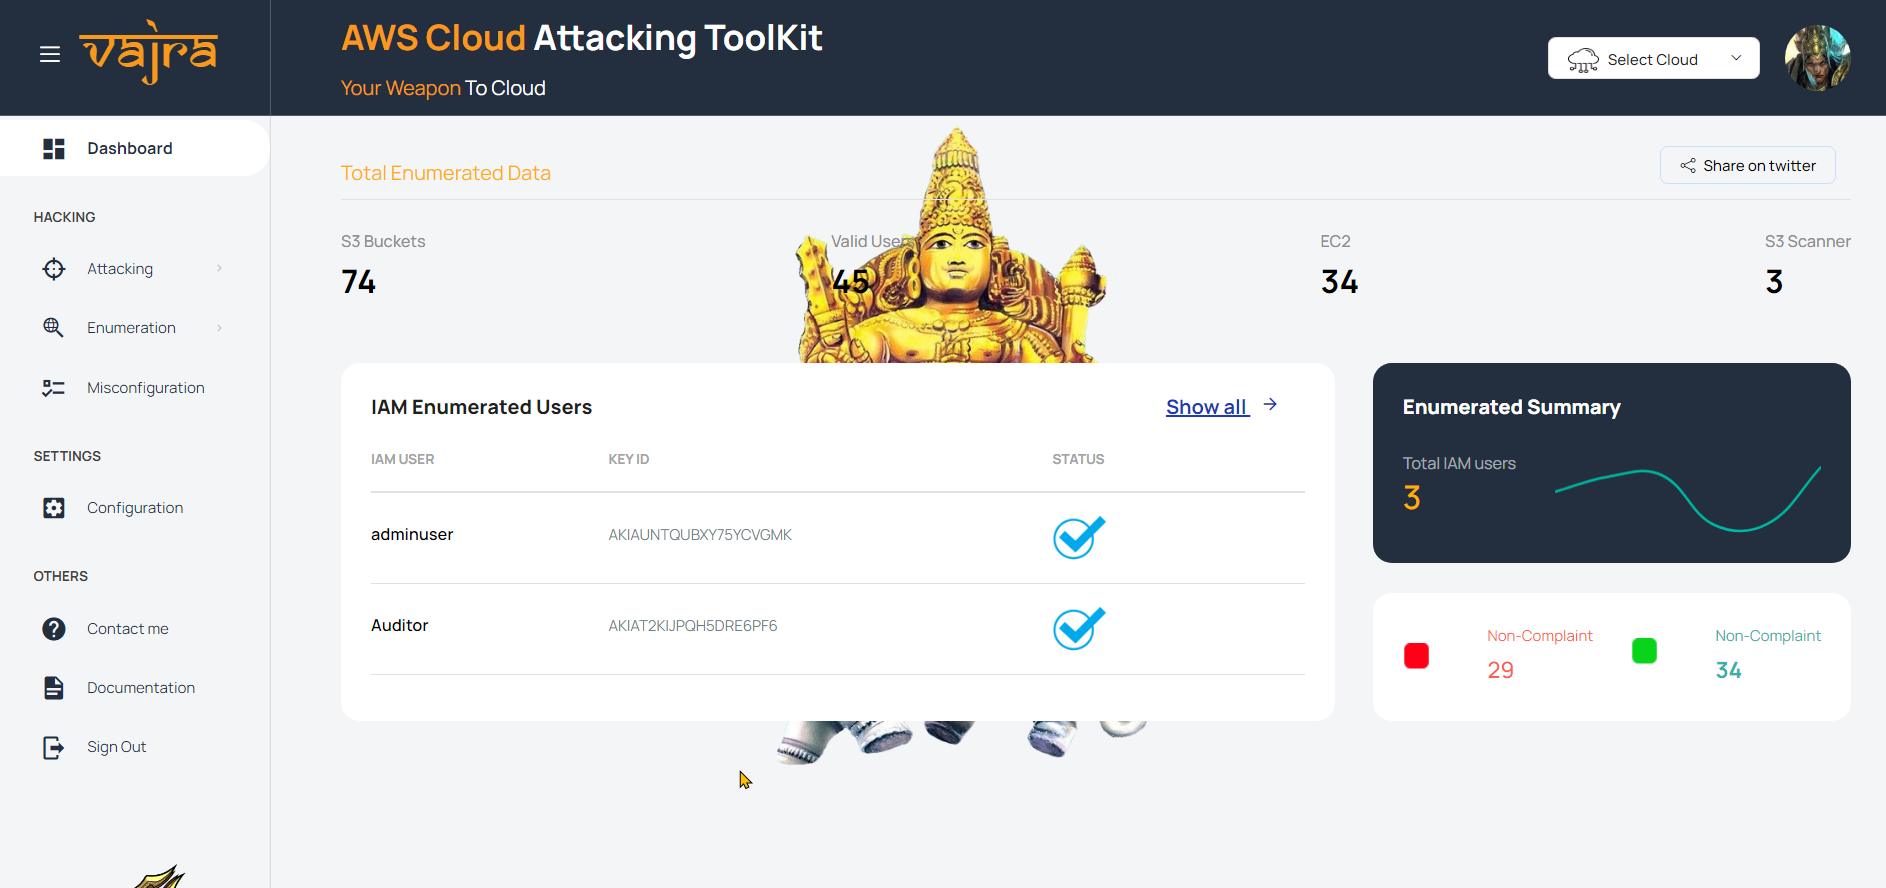
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…