
f5-waf-quick-patch-cve-2021-44228
 irgoncalves/f5-waf-quick-patch-cve-2021-44228
This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
api-securitycloud-securitydevsecops+3
3
irgoncalves/f5-waf-quick-patch-cve-2021-44228This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode
 diedromeo/cve-2026-62201-openclaw-ssrf
Deep-dive analysis of CVE-2026-62201: OpenClaw sandbox exec-server network policy bypass (SSRF). Root cause, vulnerable vs patched code,…
 gagaltotal/cve-2026-82329-poc
PoC and validation tool for CVE-2026-82329 in JFrog Artifactory. Forges JWT with empty signing key to obtain admin token, verifies access, and…
 rotemreiss/robusto
Robust Subdomain Takeover Tool
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 issaboudin/cve-2025-27136
XML External Entity PoC in an S3.
 rockmelodies/bentoml_cve-2025-54381
Ai相关
 jeromeyoung/vmware-cve-check
CVE-2021-22005
 gothburz/cve-2024-11040
vllm-project vllm version 0.5.2.2 is vulnerable to Denial of Service attacks.
 purpleteam-labs/purpleteam-tls-checker
TLS checking component of purpleteam
 knqyf263/cve-2020-10749
Proof-of-concept exploit for CVE-2020-10749 demonstrating Kubernetes MitM attacks via IPv6 rogue router advertisements between pods.
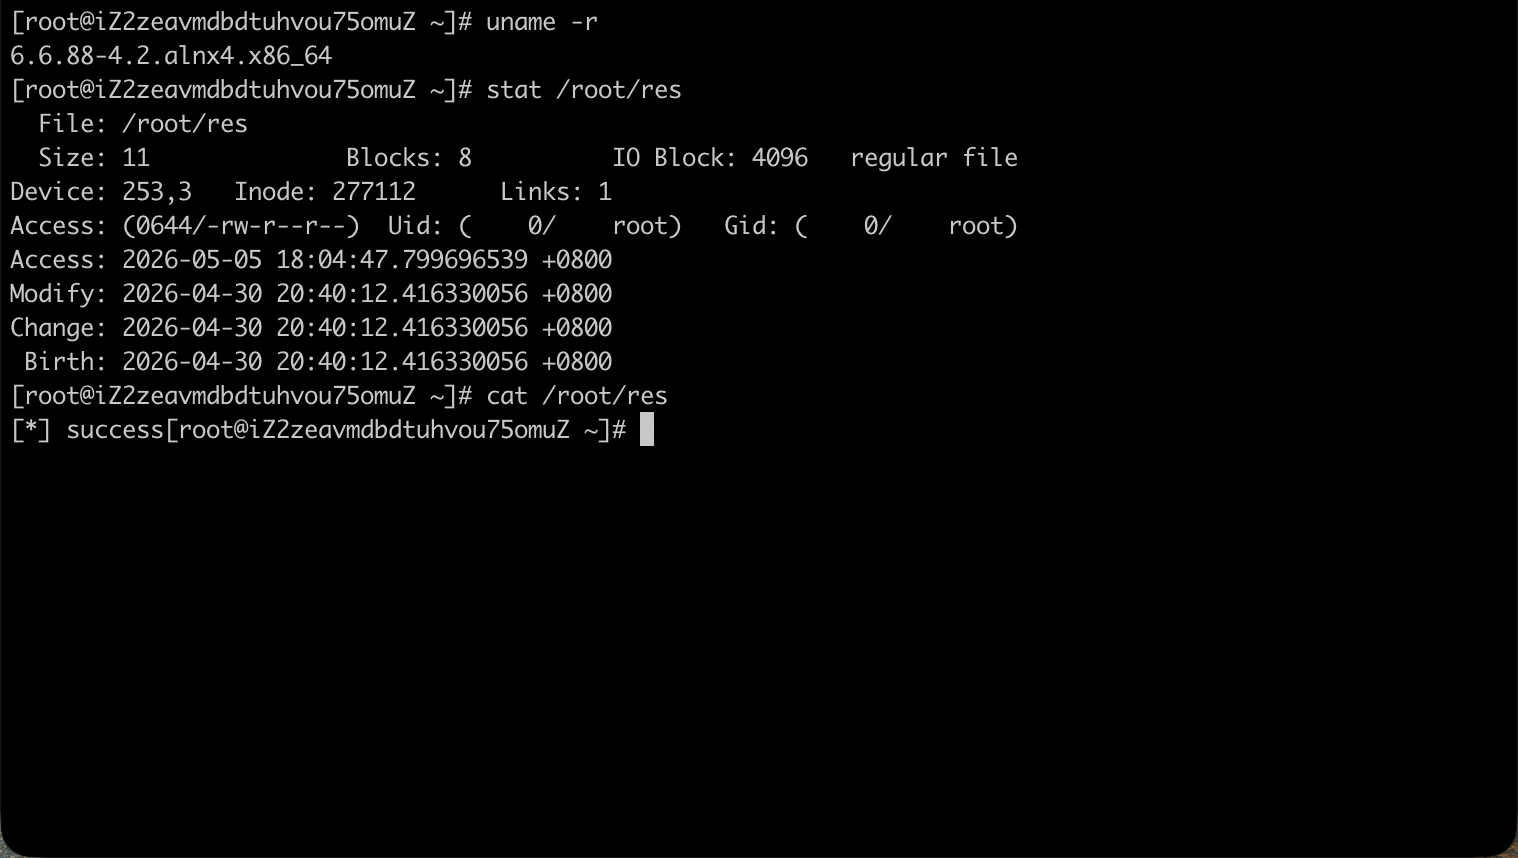 percivalll/copy-fail-cve-2026-31431-kubernetes-poc
PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 future-architect/vuls
Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
 cloudquery/cloudquery
Data pipelines for cloud config and security data. Build cloud asset inventory, CSPM, FinOps, and vulnerability management solutions. Extract from…
 elementalsouls/claude-bughunter
A Claude Code skill bundle for bug hunting and external red-team work - 82 skills, 15 slash commands, 681 disclosed-report patterns curated across 24…