
BloodBash
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
cloud-securityconfiguration-auditingidentity-access-management+6
491
squidsec/bloodbashOffline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
 secdevops-cuse/cyberrange
The Open-Source AWS Cyber Range
 rhinosecuritylabs/gcpbucketbrute
A script to enumerate Google Storage buckets, determine what access you have to them, and determine if they can be privilege escalated.
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 pumasecurity/serverless-prey
Serverless Functions for establishing Reverse Shells to Lambda, Azure Functions, and Google Cloud Functions
 brompwnie/botb
A container analysis and exploitation tool for pentesters and engineers.
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…
 qsecure-labs/overlord
Python-based CLI for automated red team infrastructure deployment on AWS and Digital Ocean, with modular support for C2, email servers, HTTP…
 voulnet/barq
barq: The AWS Cloud Post Exploitation framework!
 cyberark/shimit
A tool that implements the Golden SAML attack
 evict/poc_cve-2018-1002105
Proof-of-concept exploit for CVE-2018-1002105 targeting Kubernetes API server. Supports authenticated and unauthenticated privilege escalation to…
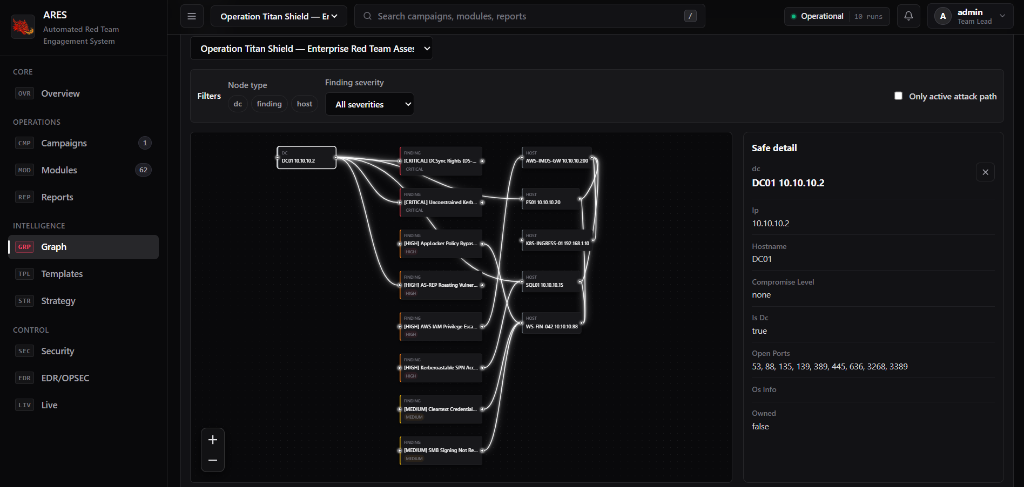 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
 professionallyevil/harpoon
A collection of scripts, and tips and tricks for hacking k8s clusters and containers.

 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus