
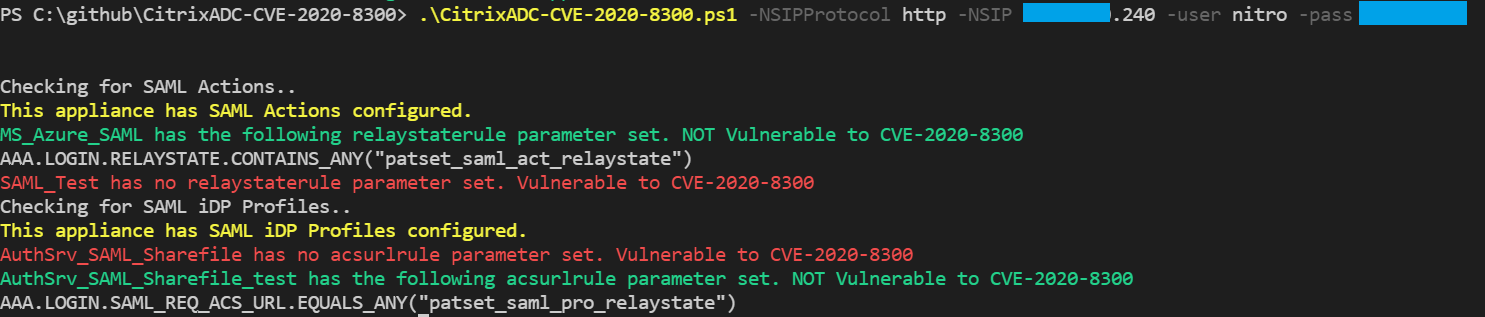
CitrixADC-CVE-2020-8300
 stuartcarroll/citrixadc-cve-2020-8300
Detect Citrix ADC SAML action or SAML iDP Profile config vulnerable to CVE-2020-8300 using Citrix ADC NITRO API
cloud-securityconfiguration-auditingnetwork-security+3
1
stuartcarroll/citrixadc-cve-2020-8300Detect Citrix ADC SAML action or SAML iDP Profile config vulnerable to CVE-2020-8300 using Citrix ADC NITRO API
 craig-m-unsw/omigod-lab
A Vagrant VM test lab to learn about CVE-2021-38647 in the Open Management Infrastructure agent (aka "omigod").
 benzamir/cve-2026-7791
Local Privilege Escalation in Amazon WorkSpaces via TOCTOU and Arbitrary File Write
 taroballzchen/cve-2023-28432-metasploit-scanner
MinIO Information Disclosure Vulnerability scanner by metasploit
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…

 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
 edtrackai/nextjs-supabase-stripe-security-checker
Local static security scanner for Next.js, Supabase and Stripe apps: 24 AST-based checks for leaked keys, missing RLS and grants, unsafe webhooks.…
 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…
 legit-labs/gh-legitify
GitHub CLI extension for running "legitify"
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 syedhafiz1234/cve-2023-34039
CVE-2023-34039
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 blackm4c/cve-2021-41805
HashiCorp Consul exploit with python. (CVE-2021-41805)
 tocong282/cve-2026-44578-poc
Proof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.