

mcp-server
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
api-security-testingcloud-securitycode-analysis+3
offensive360/mcp-serverMCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 george0papasotiriou/cve-2026-23007-serverless-cold-start-memory-remanence-data-leakage-
Simulates CVE-2026-23007 serverless cold-start memory remanence; demonstrates how persistent global state across Lambda invocations can leak secrets…
 heshamash/cve-2026-11417-aws-cdk-rce
Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.
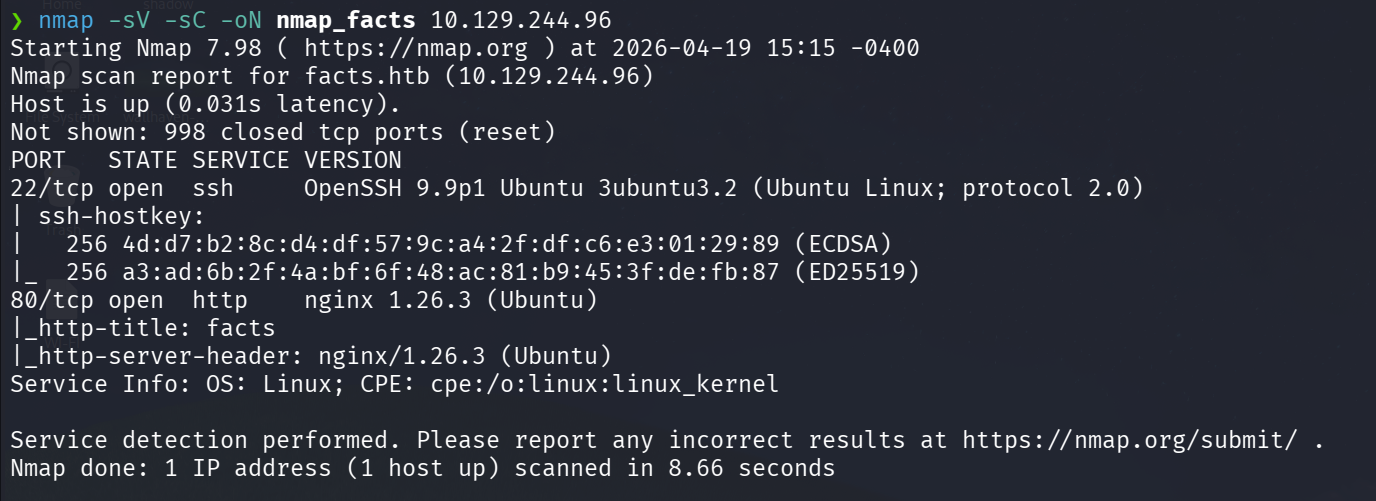 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 michaeladamgroberman/cve-2026-32662
CVE-2026-32662: Active Debug Code in Production — Gardyn Home Kit (ICSA-26-055-03)
 aaronm-sysdig/log4j-vuln-demo
Intentionally vulnerable Log4j 2.14.1 demo for Sysdig CNAPP scanning (CVE-2021-44228)
 regaan/cve-2026-33340
CVE-2026-33340: Critical SSRF in lollms-webui /api/proxy - Unauthenticated arbitrary request forgery (CVSS 9.1)
 jinlei-chen-uwo/cve-2024-34351-demo
Minimal Next.js 14.0.0 demo app for CVE-2024-34351 SSRF vulnerability. Includes exploit setup, interactsh confirmation, Burp interception, and AWS…
 mrk336/cve-2025-27480-the-silent-gateway-risk
Letting attackers run malicious code without needing a cracked password, user interaction, or even a foothold in your network. That’s CVE-2025-27480
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
 ayush-parab/sentinel-gpt
Automated threat hunting pipeline that ingests Azure logs, uses LLM reasoning to detect suspicious activity, assess risk, and generate remediation…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 fevar54/cve-2026-54420-litespeed-symlink-exploit
PoC de CVE-2026-54420: explotacion via symlink en el plugin LiteSpeed de cPanel/WHM.
 nayankadamm/cve-2023-34233_proof_of_concept
Proof-of-concept demonstrating CVE-2025-24793 SQL injection vulnerability in Snowflake Connector for Python, with auto-detection of patched/unpatched…
 astraljays/traditionaljay
Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
 mokokash/ejbca-pqc-lab
Pure PQC two-tier PKI hierarchy using ML-DSA-65 (NIST FIPS 204) on EJBCA Community Edition — Root CA + Sub CA with CRL and OCSP
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.