poc-cve-2024-0132
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
cloud-securitycontainer-escapecontainer-security+3
5
ssst0n3/poc-cve-2024-0132Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 devenes/text4shell-cve-2022-42889
Kubernetes Lab for CVE-2022-42889
 niclas-zone/ci/trivy
GitLab CI component for Trivy scanning
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 wadesweaponshed/cve-2026-50751-mitigation-scripts
Mitigation scripts for CVE-2026-50751
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
 oscerd/cve-2026-40564
CVE-2026-40564: SSRF via FlinkSessionJob jarURI in apache/flink-kubernetes-operator. Self-contained reproducer that runs on a local kind cluster with…
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 joaoreis13/flight-risk
Security toolkit for CVE-2025-55182 (React2Shell) — scan, detect, correlate, and test React Server Components RCE vulnerability
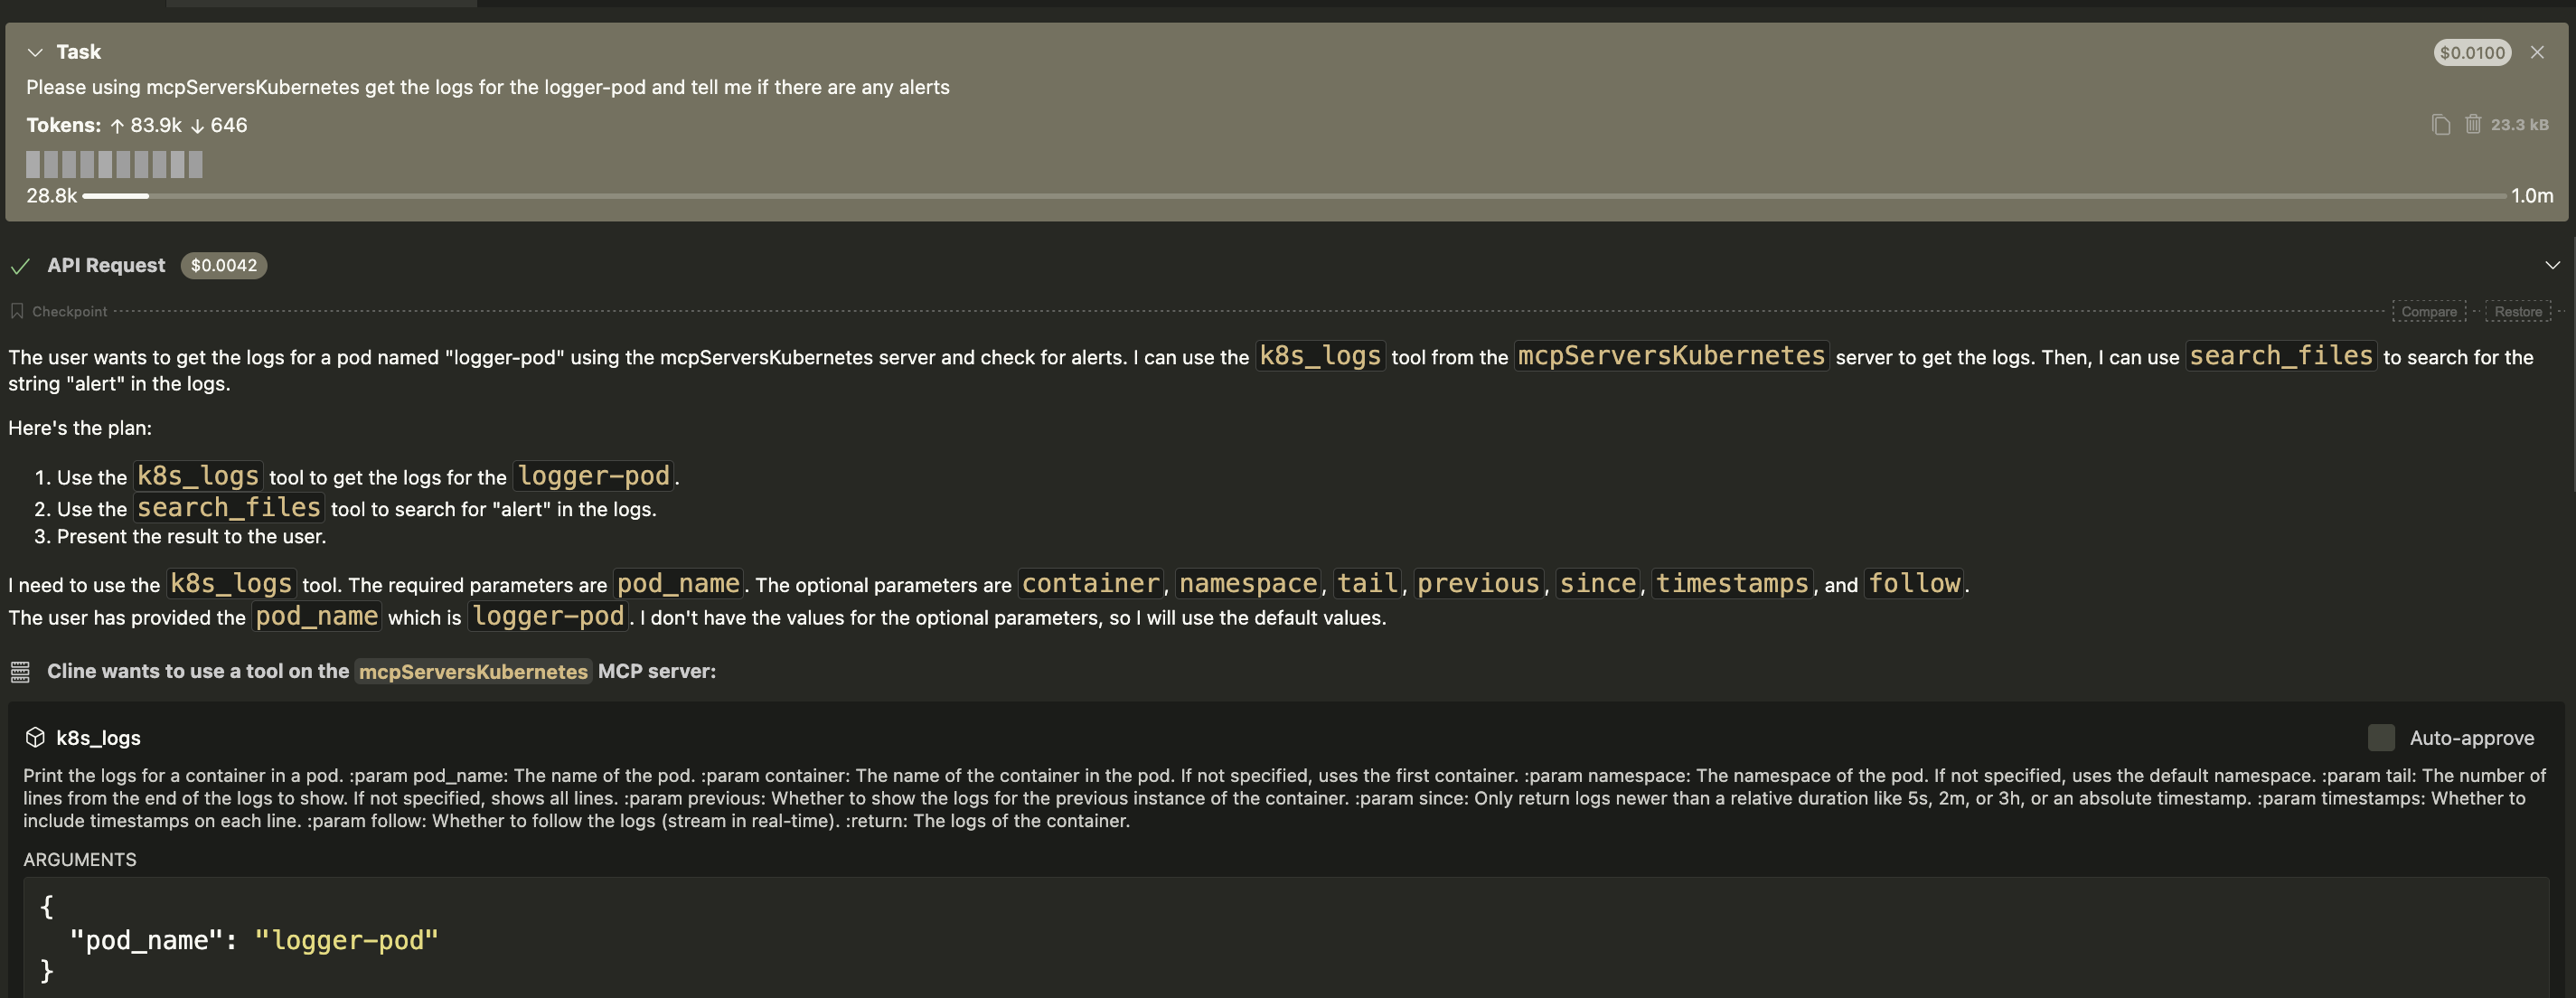 william31212/cve-requests-1896609
CVE-2025-59376, CVE-2025-59377
 salman-sec/patch-management-
Scenario-based training exercise for IT administrators: identify, approve, and deploy critical patches for financial systems under a 48-hour SLA…
 rjhaikal/poc-ingressnightmare-cve-2025-1974
POC IngressNightmare (CVE-2025-1974), modified from https://github.com/yoshino-s/CVE-2025-1974
 boianeduard/cve-2025-1974
ingress-nginx admission controller RCE escalation PoC
 shoucheng3/apache__dolphinscheduler_cve-2023-51770_3_2_1_fixed
Exploit for CVE-2023-51770 targeting Apache DolphinScheduler versions 3.2.1 and earlier, enabling remote code execution via crafted workflow…
 tuladhar/ingress-nightmare
IngressNightmare (CVE-2025-1974)
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 gravitational/cve-2018-1002105
Kubernetes cluster vulnerability scanner that detects CVE-2018-1002105 by testing for unauthenticated API access and privilege escalation via…