
AzureHunter
 darkquasar/azurehunter
A Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
cloud-securitydigital-forensicsincident-response+3
darkquasar/azurehunterA Cloud Forensics Powershell module to run threat hunting playbooks on data from Azure and O365
 greycatz/cloudunflare
Reconnaissance Real IP address for Cloudflare Bypass
 google/gcp_scanner
GCP resource scanner that evaluates access levels of compromised credentials by enumerating cloud services, projects, and IAM permissions across…
 bishopfox/smogcloud
Find cloud assets that no one wants exposed 🔎 ☁️
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
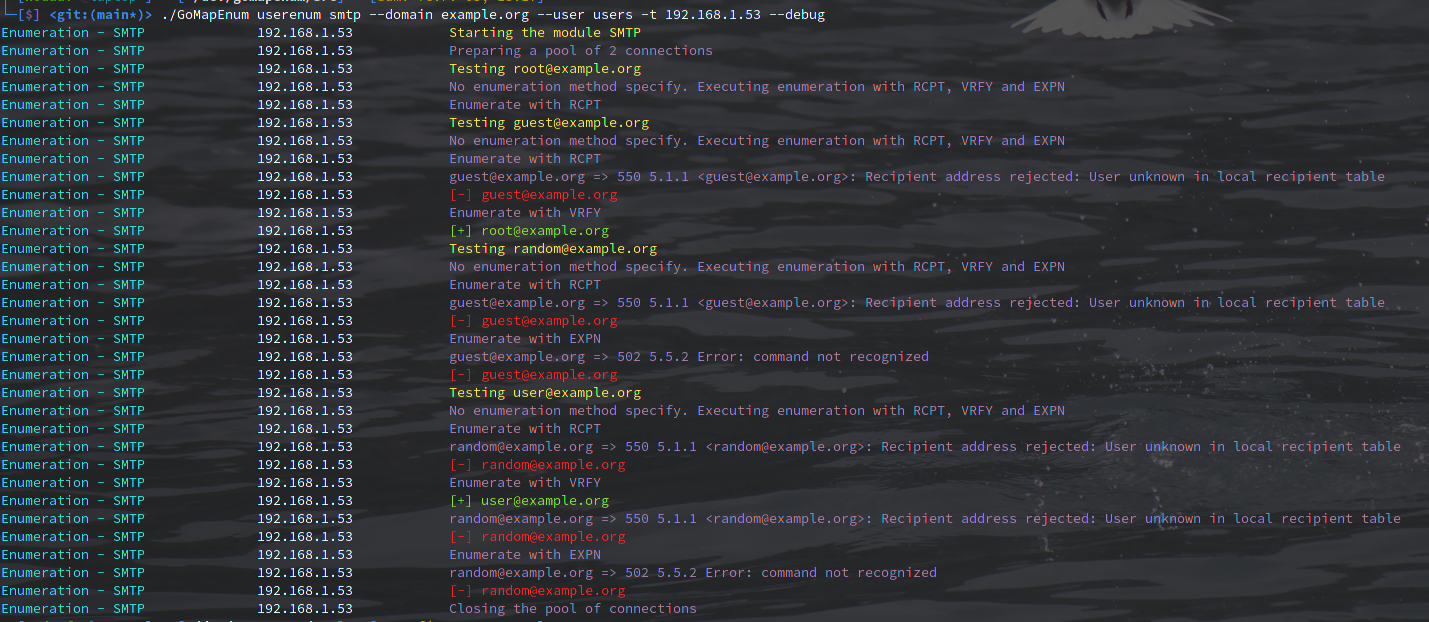 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
 g0ldencybersec/cloudrecon
Suite of tools for red teamers and bug hunters to discover ephemeral cloud assets by scanning IP ranges and inspecting SSL certificates for hidden…
 shabarkin/aws-enumerator
Read-only AWS service enumerator with 600+ API calls for cloud reconnaissance, info dumping, and result analysis during penetration testing.
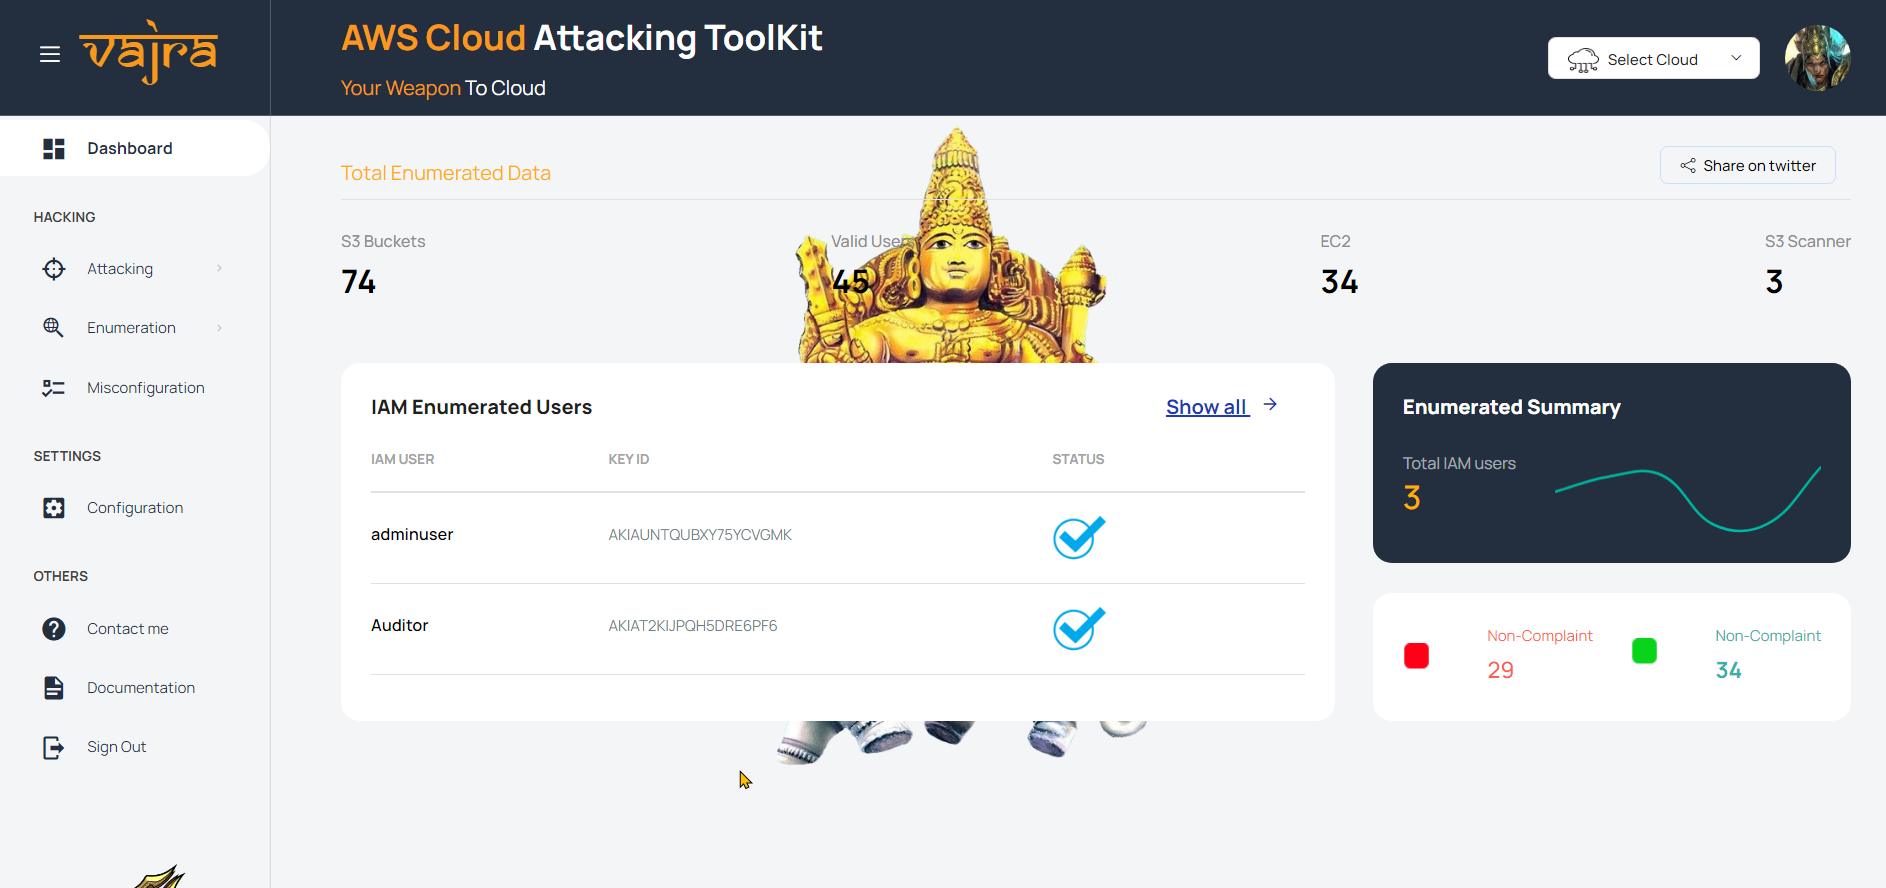 trouble-1/vajra
Vajra is a UI-based tool with multiple techniques for attacking and enumerating in the target's Azure and AWS environment. It features an intuitive…
 koenrh/s3enum
Fast and stealthy Amazon S3 bucket enumeration tool for pentesters.
 mayyhem/maestro
Abusing Azure services over C2
 mgeeky/azurert
AzureRT - A Powershell module implementing various Azure Red Team tactics
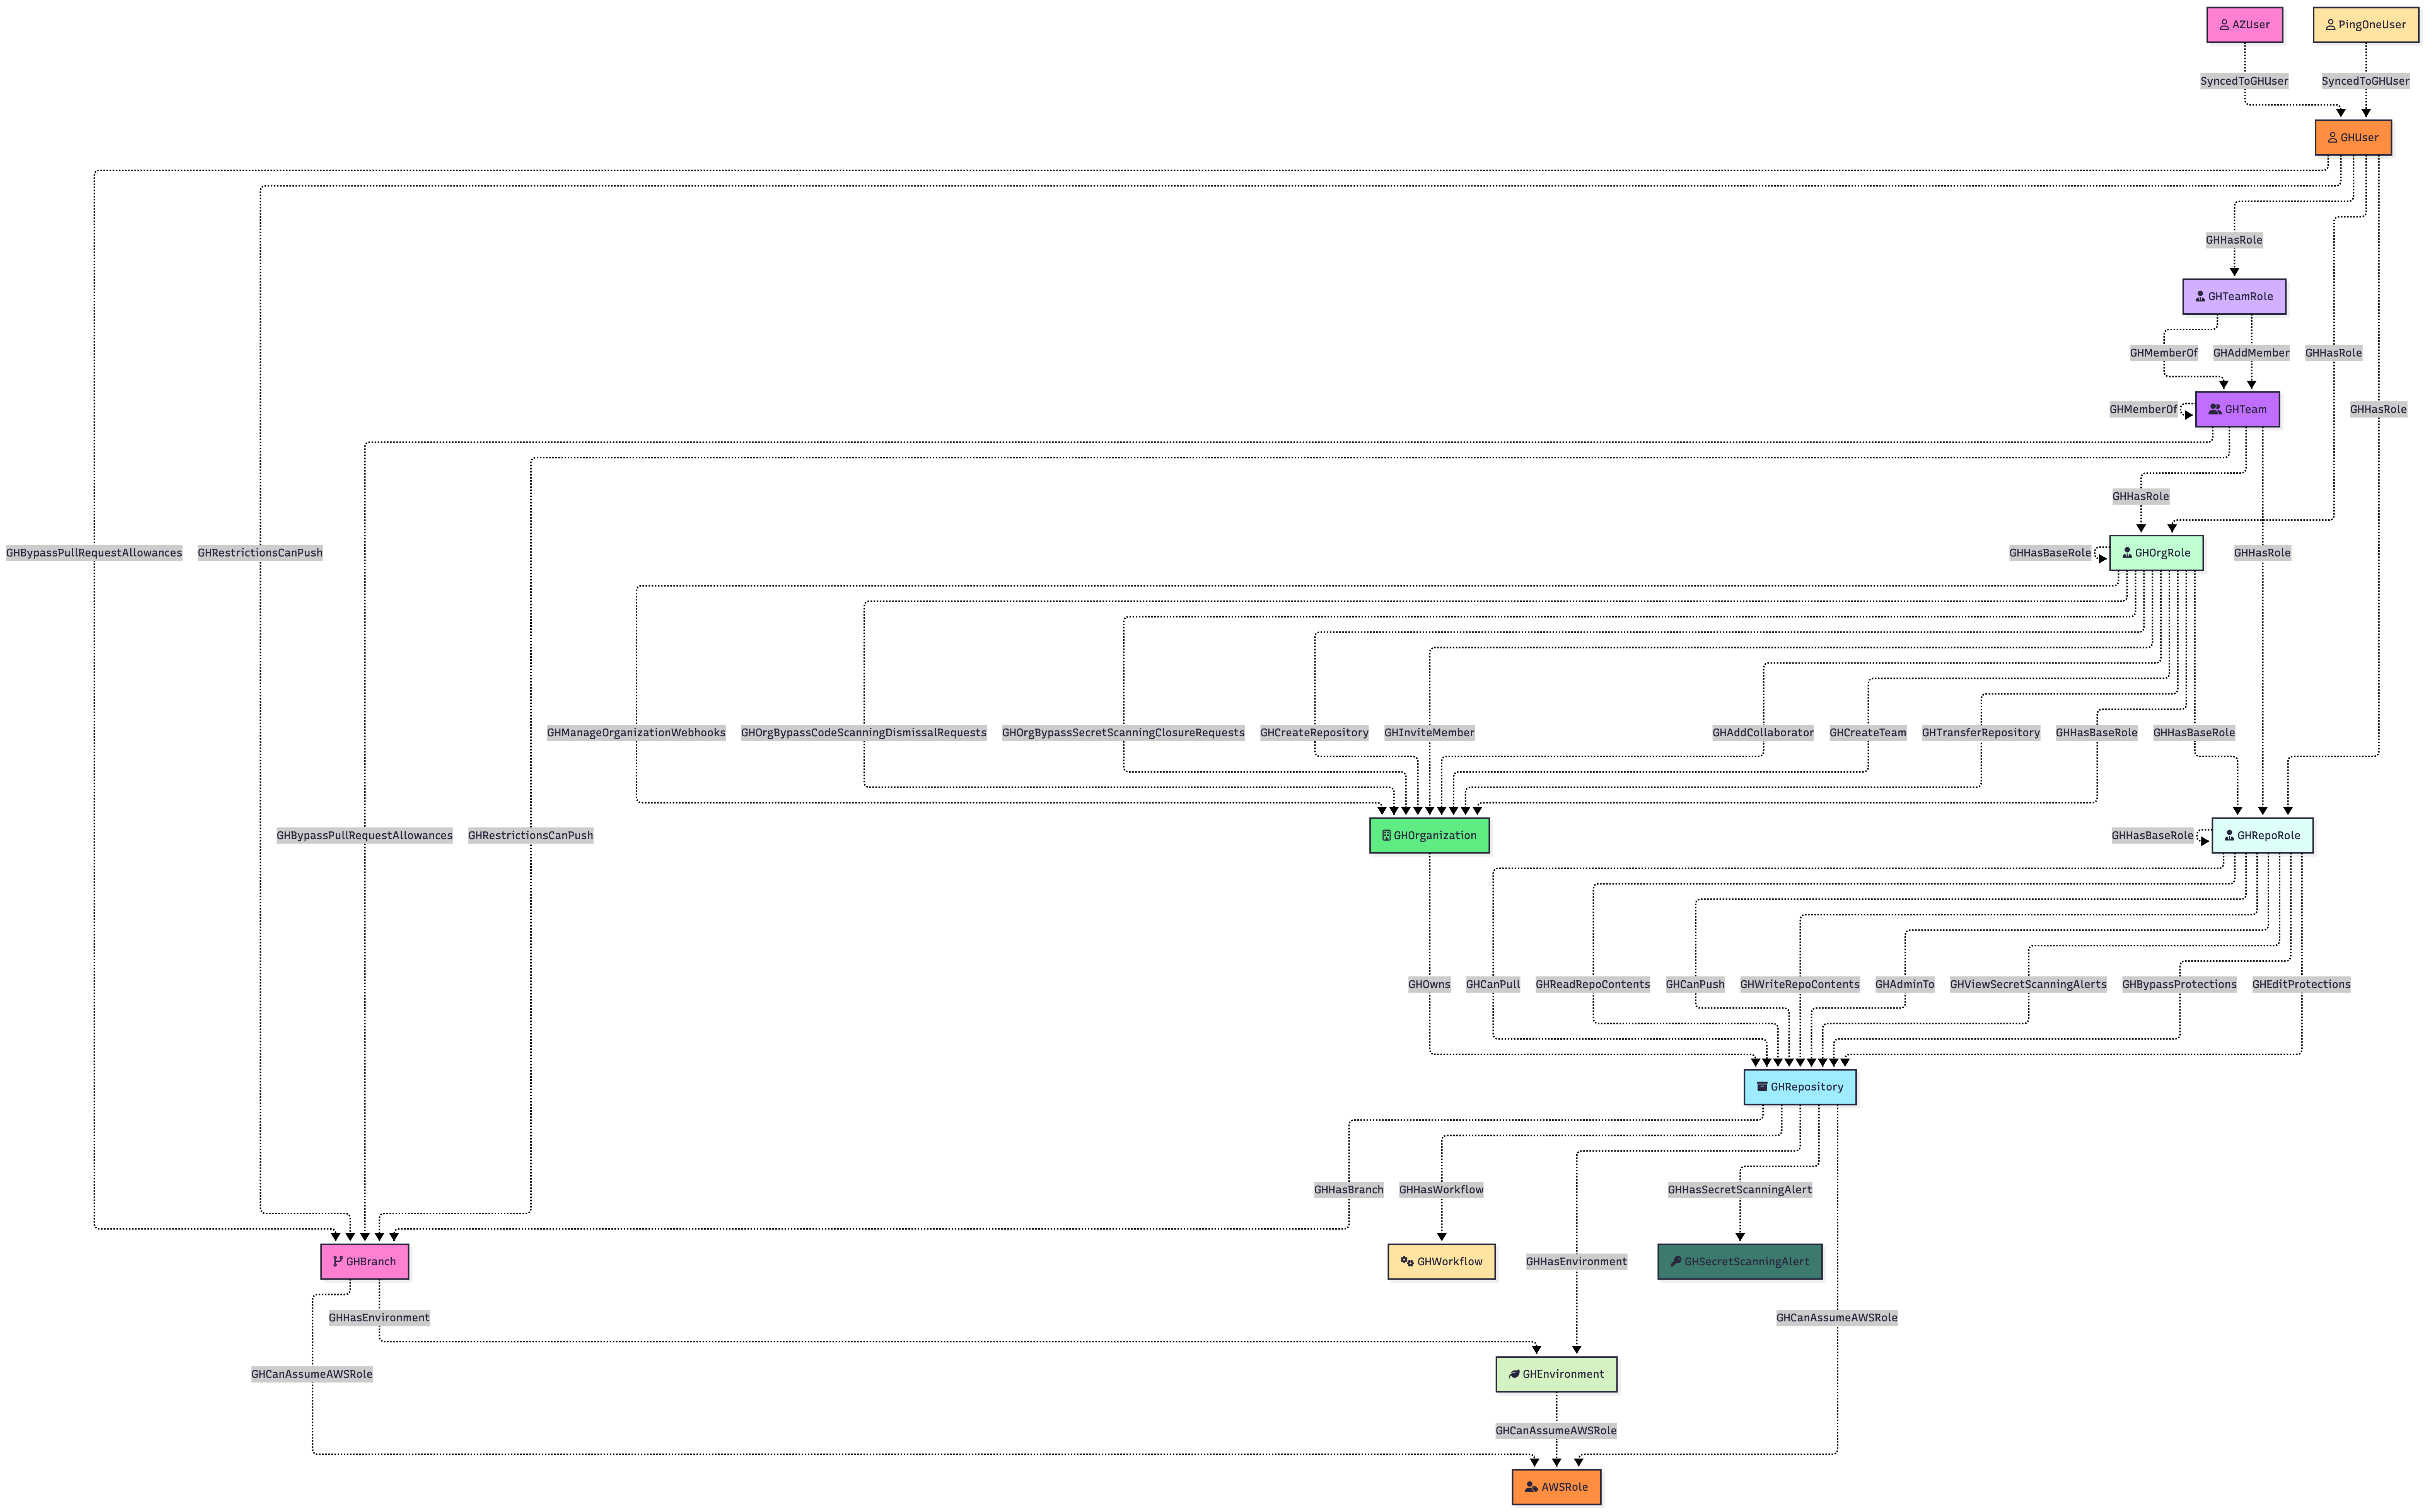 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
 redbyte1337/credspy
Entra ID user enumeration and auth method discovery via the public GetCredentialType API
 yuyudhn/azsubenum
DNS-based subdomain enumeration tool for Azure services, probing App Services, Storage Accounts, Databases, Key Vaults, and CDN endpoints via…
 blacklanternsecurity/offensive-azure
Collection of offensive tools targeting Microsoft Azure
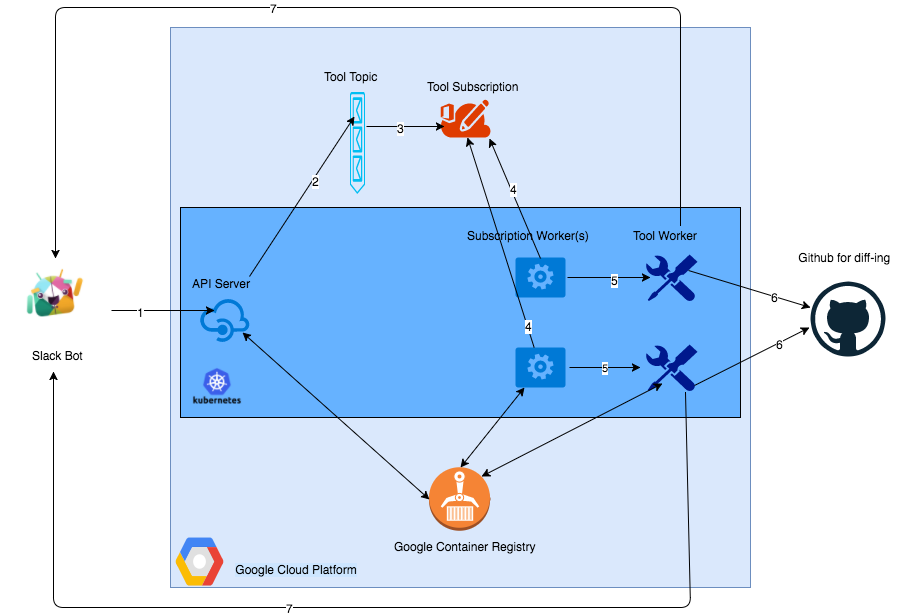 anshumanbh/kubebot
A security testing Slackbot built with a Kubernetes backend on the Google Cloud Platform