
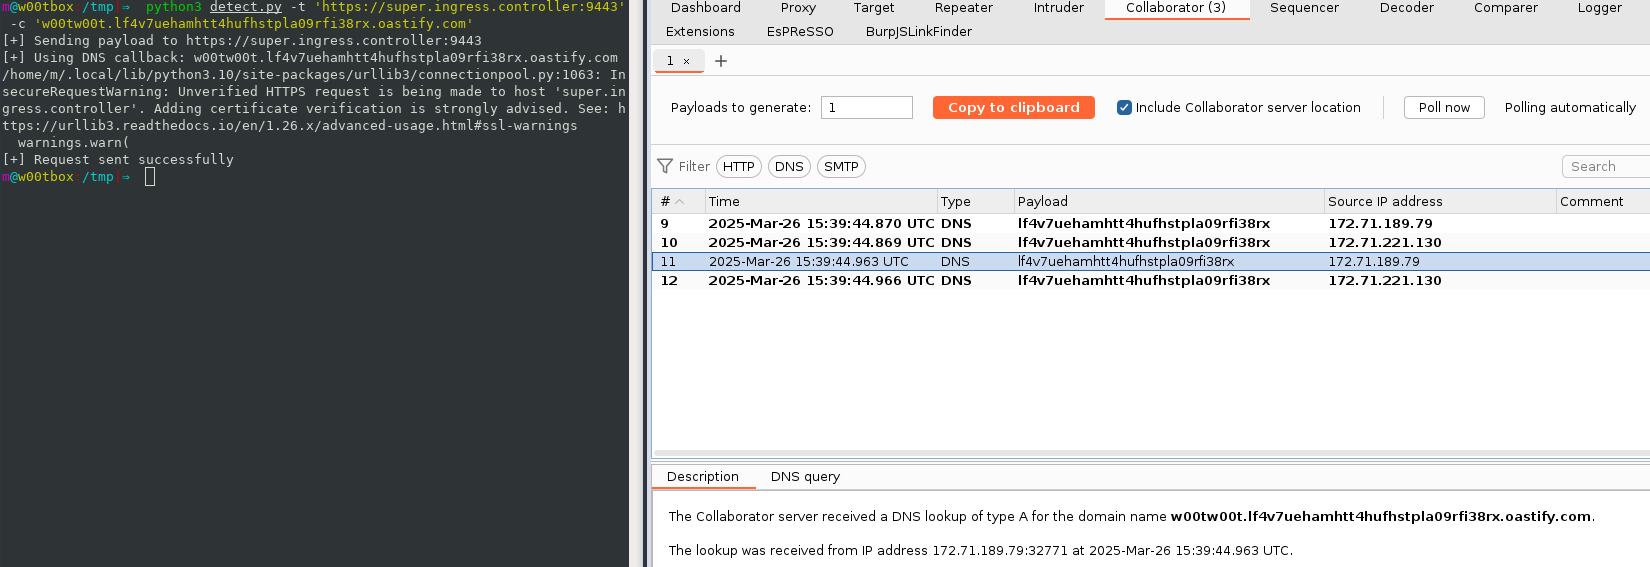
ingressnightmare-detection-poc
 m-q-t/ingressnightmare-detection-poc
Proof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
cloud-securityexploitationmisconfiguration+3
m-q-t/ingressnightmare-detection-pocProof-of-Concept Tool to detect IngressNightmare (CVE-2025-1974) via (non-intrusive) active means.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
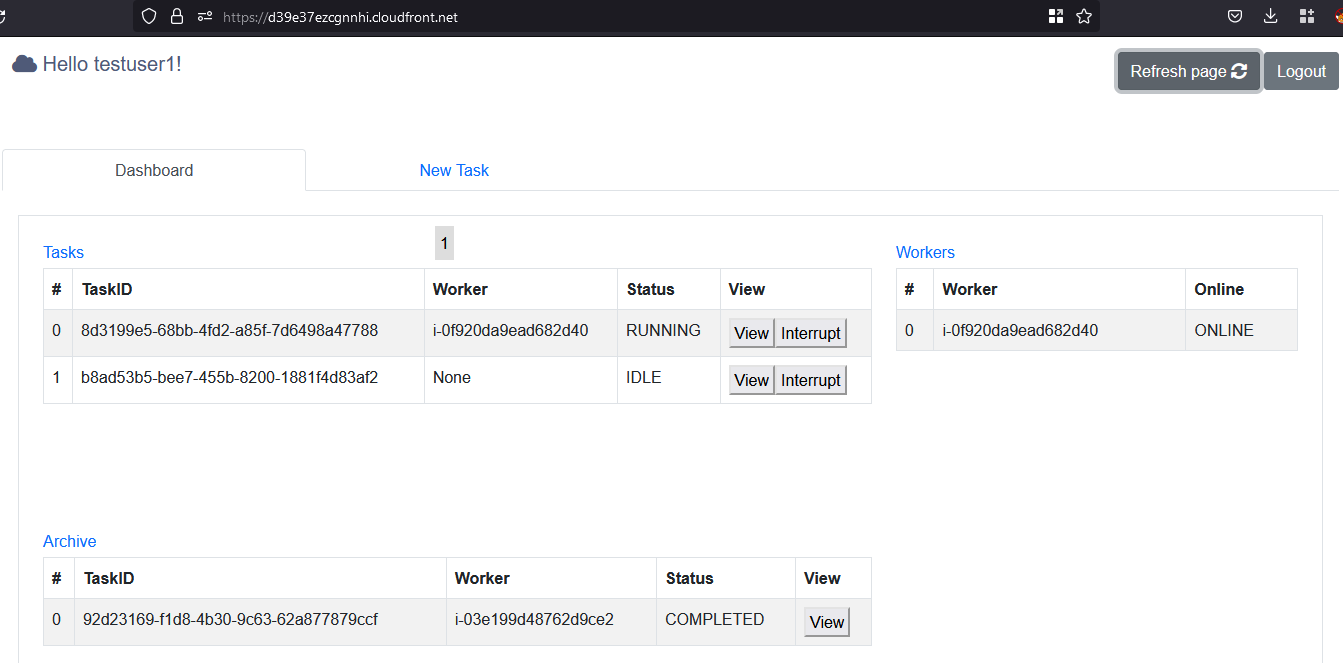 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 shaheryar773/mitigate-cve-2026-23869-react-server-component-loops
Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.
 cdxiaodong/cve-2021-25741
Proof-of-concept exploit for CVE-2021-25741 enabling Kubernetes container escape via subpath volume mount manipulation, designed for security testing…
 china-china/minio_cve-2023-28432_exp
Exploit for MinIO information disclosure vulnerability CVE-2023-28432, allowing unauthorized access to sensitive environment variables.
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 gduma-phdata/patch-cve-2026-07219
Deploys a critical patch for F5 BIG-IP iControl REST vulnerability CVE-2026-07219, with validation and deployment tracking for production…
 b0b0haha/cve-2026-29955
Proof-of-concept for CVE-2026-29955, a command injection vulnerability in KubePlus kubeconfiggenerator allowing remote code execution and…
 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 gobysec/cve-2023-28432
Exploit for CVE-2023-28432, a sensitive information disclosure vulnerability in MinIO's verify interface, allowing attackers to read system…
 v0wkeep3r/cve-2024-21626-runcpoc
Proof-of-concept for CVE-2024-21626, a runc container escape vulnerability. Includes verification scripts, two exploitation methods (cron reverse…
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 tcollins-hashicorp/vault-cve-2026-5006-audit
Audit and educational toolkit for CVE-2026-5006, a Vault templated-policy slash-injection vulnerability. Includes a read-only audit script generating…
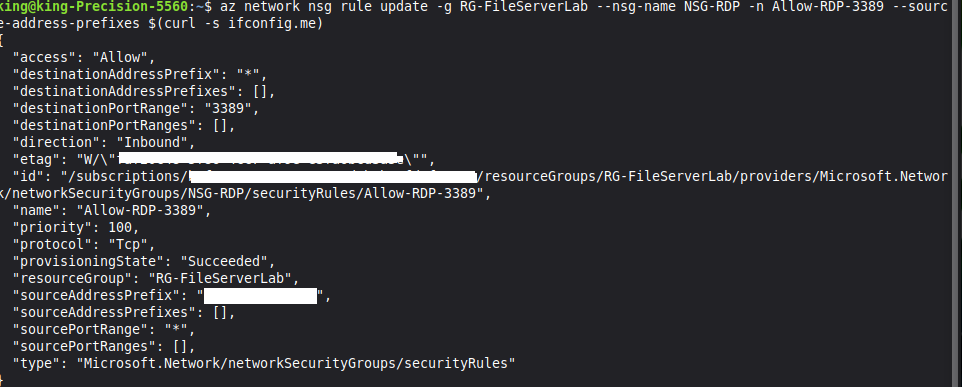 kingsrule50/nessus-vulnerability-scanning-lab
Enterprise vulnerability management on Azure — Terraform-deployed Nessus scanner, credentialed scanning, CVE-2013-3900 remediation with verified…
 sk3pper/cve-2024-21626
Proof-of-concept exploits for CVE-2024-21626, a Docker/runc container escape vulnerability, demonstrating multiple attack vectors to access and…