Check-Point-Trusted-Access-Review

Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…

Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…

Kubernetes cluster vulnerability scanner that detects CVE-2018-1002105 by testing for unauthenticated API access and privilege escalation via…

Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…

OpenSSL Heartbleed (CVE-2014-0160) vulnerability scanner.

GitLab CI component for Trivy scanning

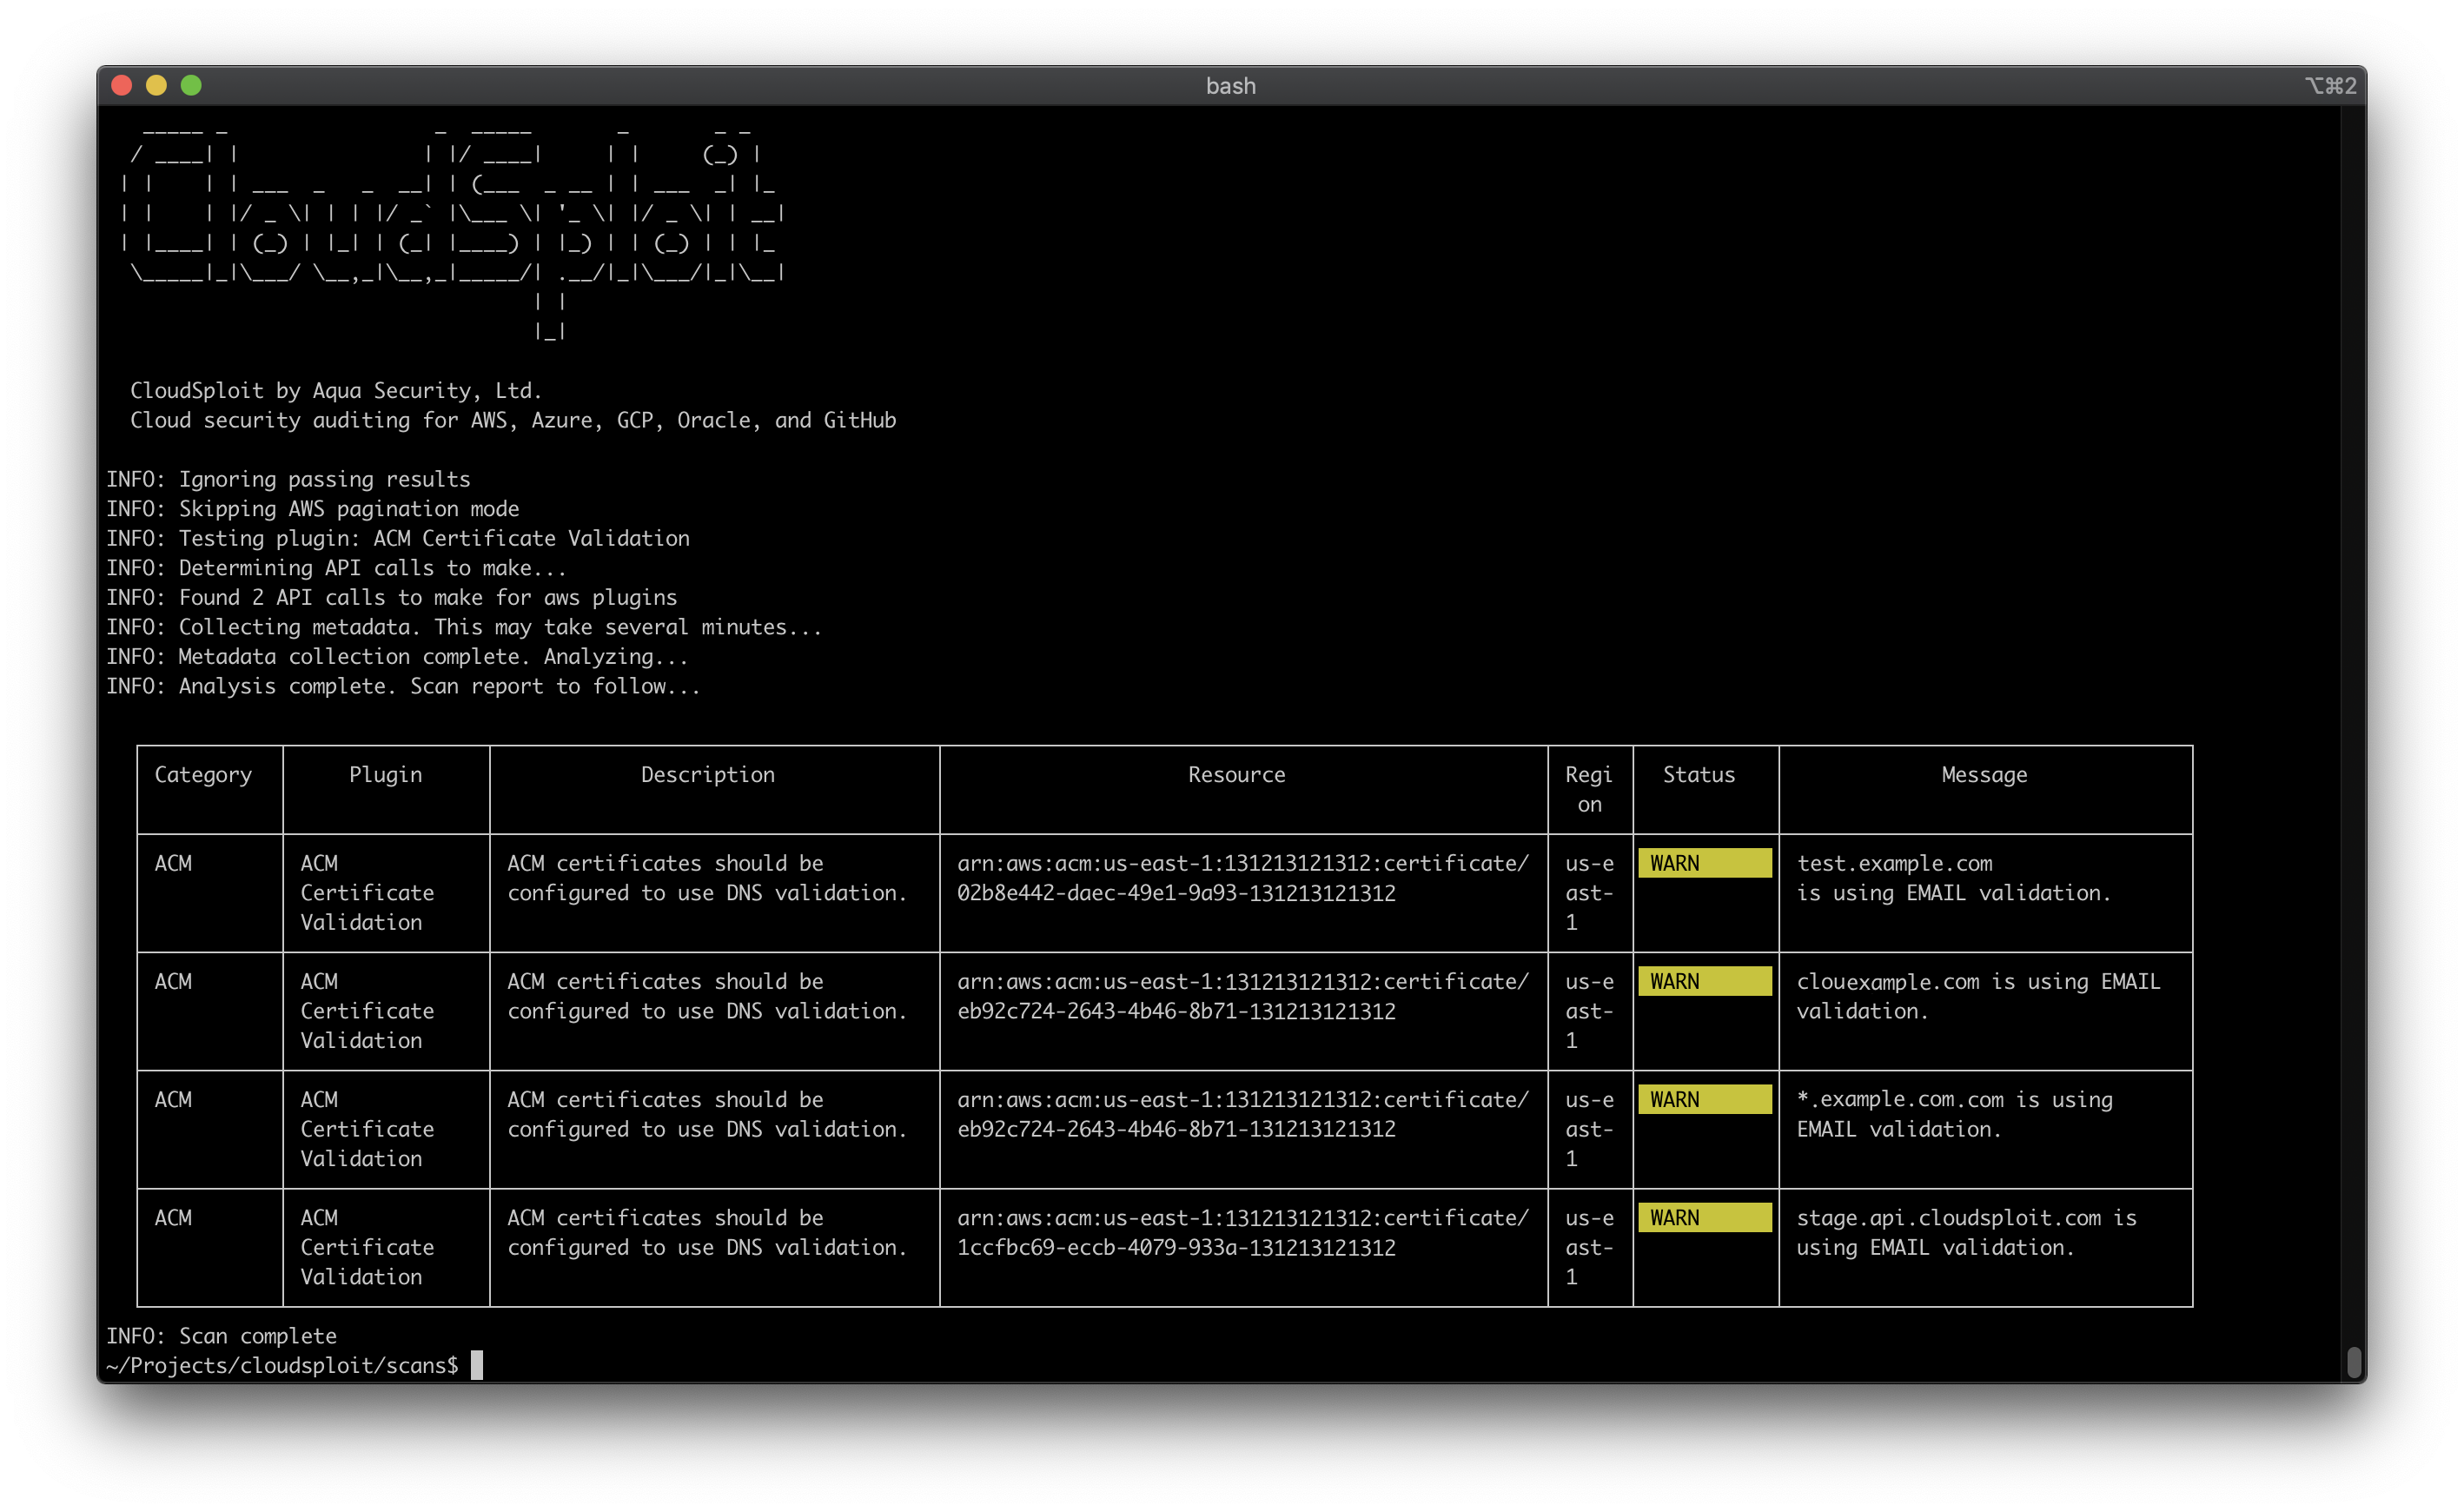
Multi-cloud security posture scanner that audits AWS, Azure, GCP, and OCI for misconfigurations, compliance violations (HIPAA, PCI, CIS), and…

Deliberately vulnerable Terraform infrastructure for learning cloud security misconfigurations and validating IaC scanner detection across AWS and…

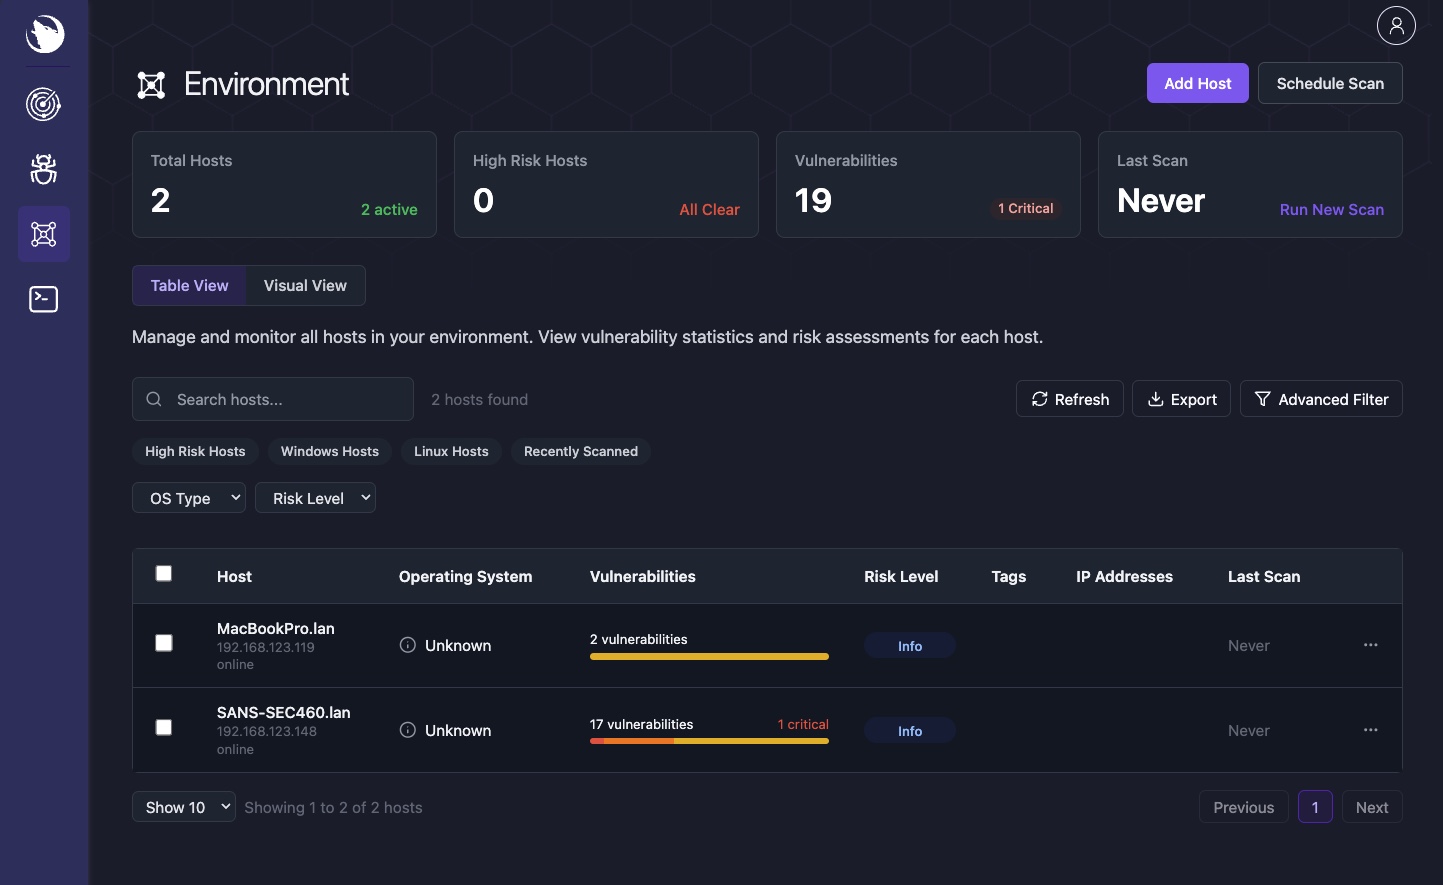
Open-source vulnerability scanner with automated network discovery, CVE-based detection, CVSS scoring, risk dashboards, remote agents via gRPC, and a…

AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…

Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…

Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…

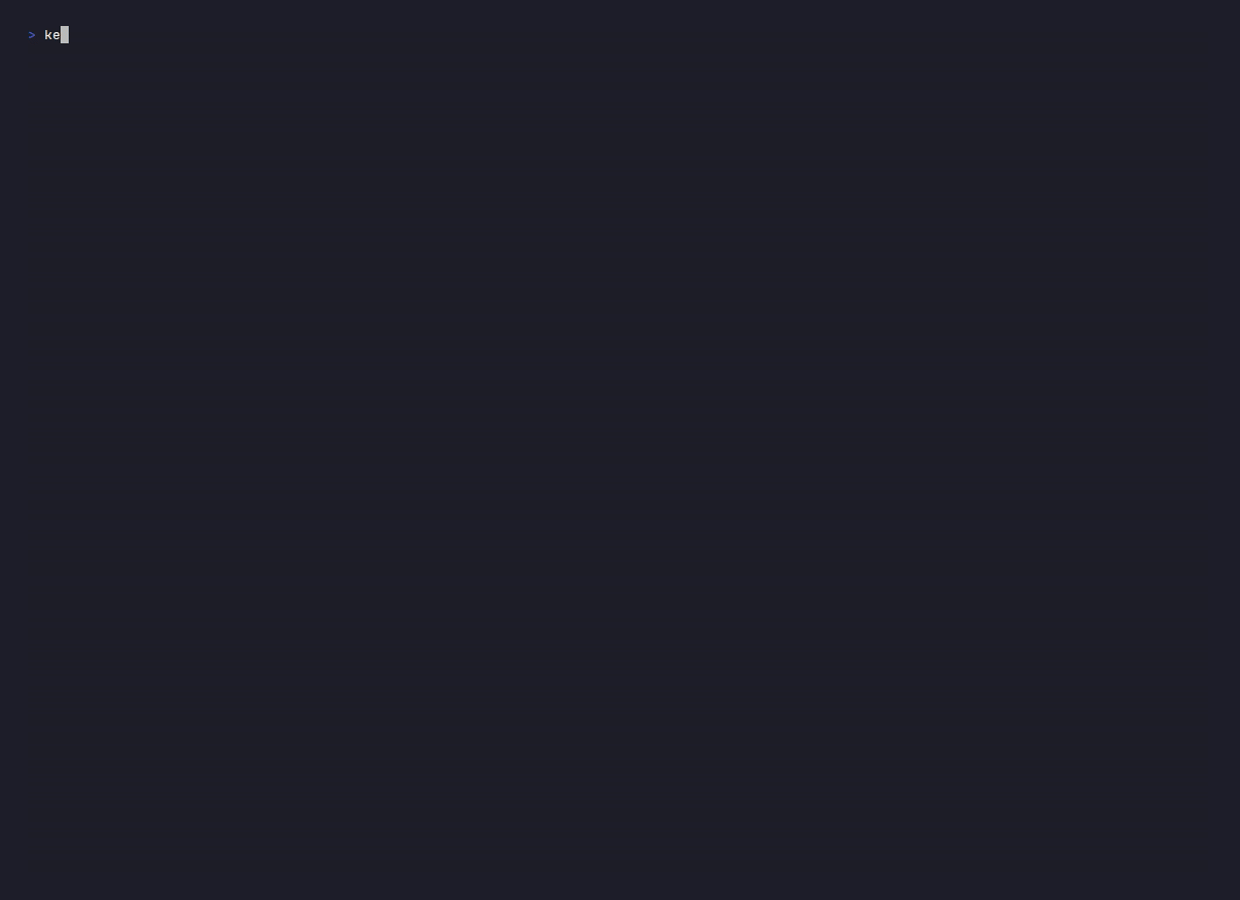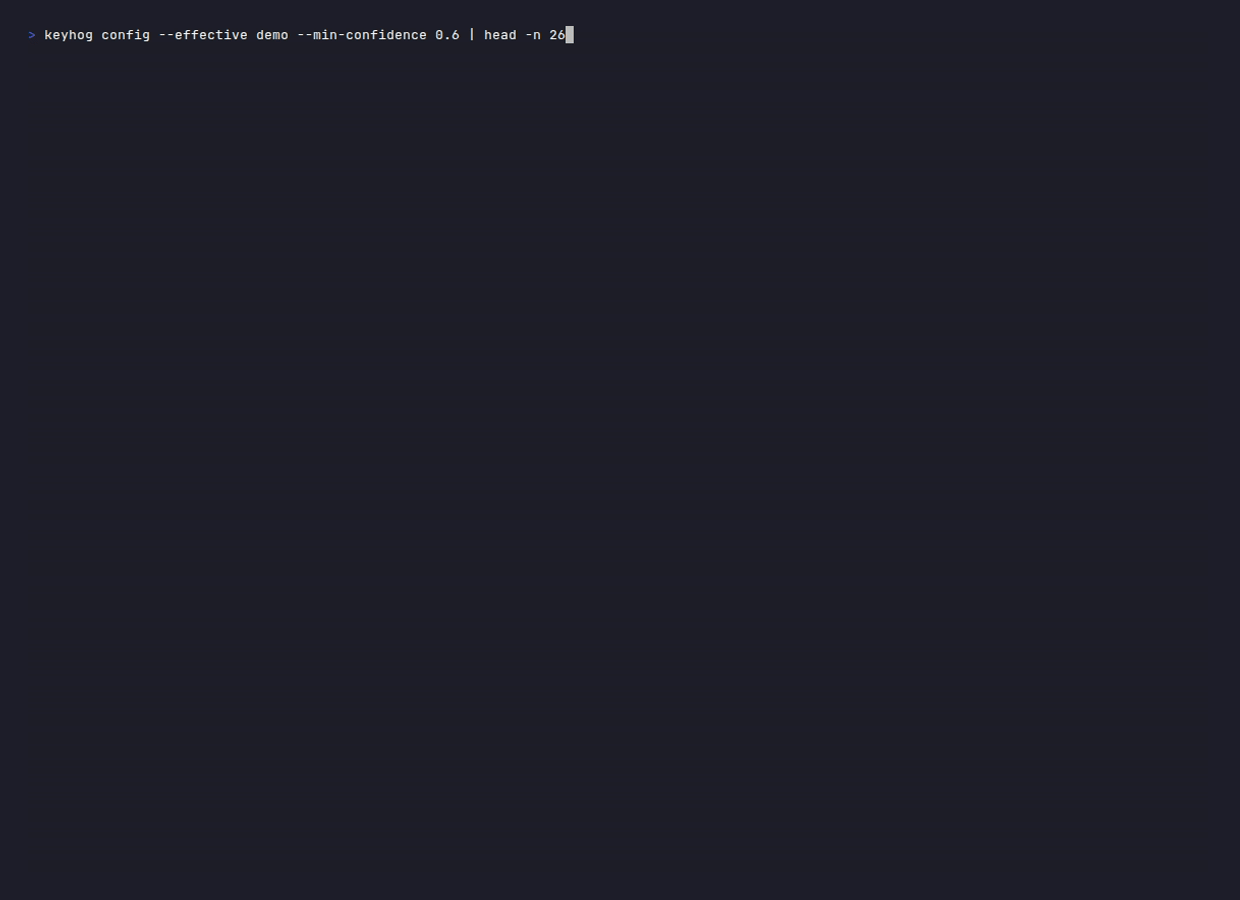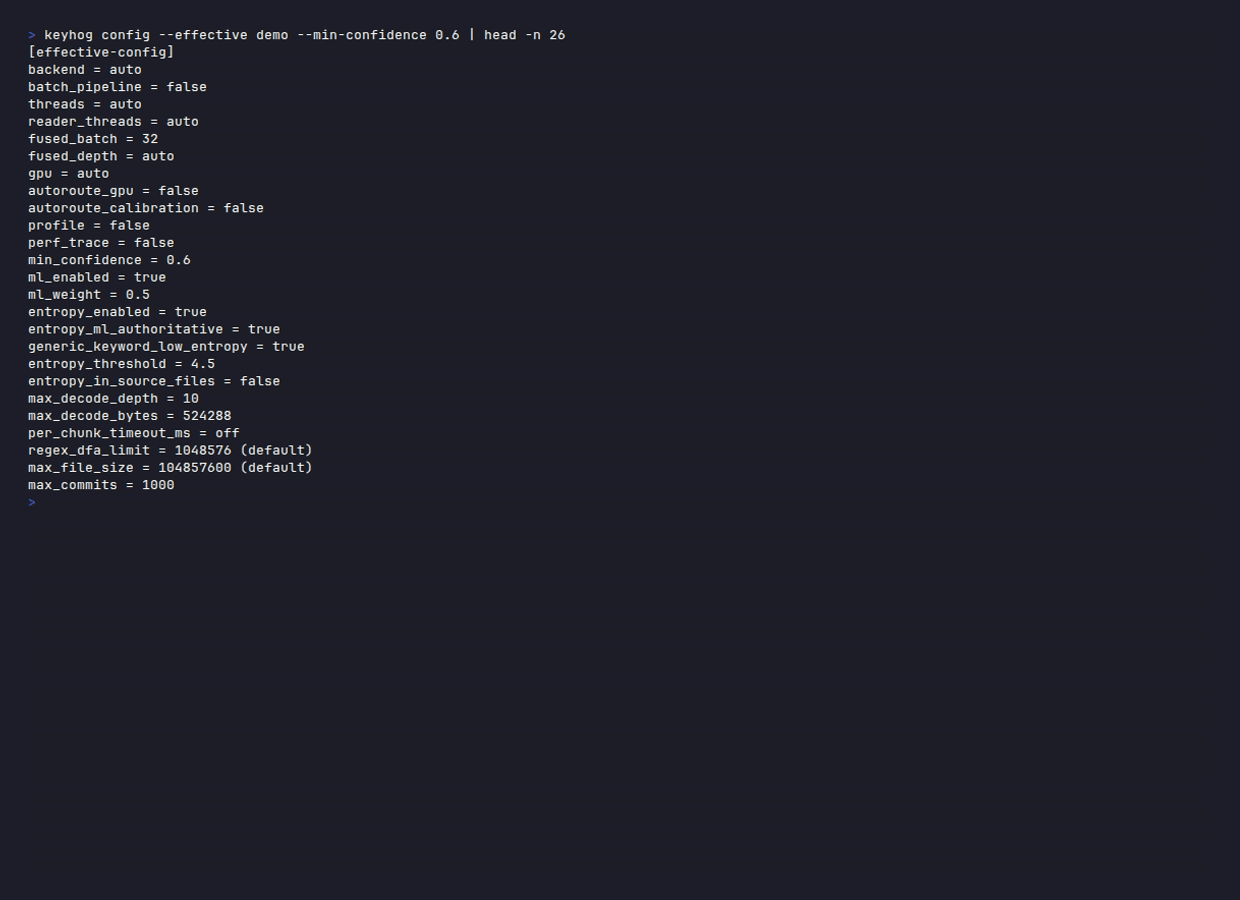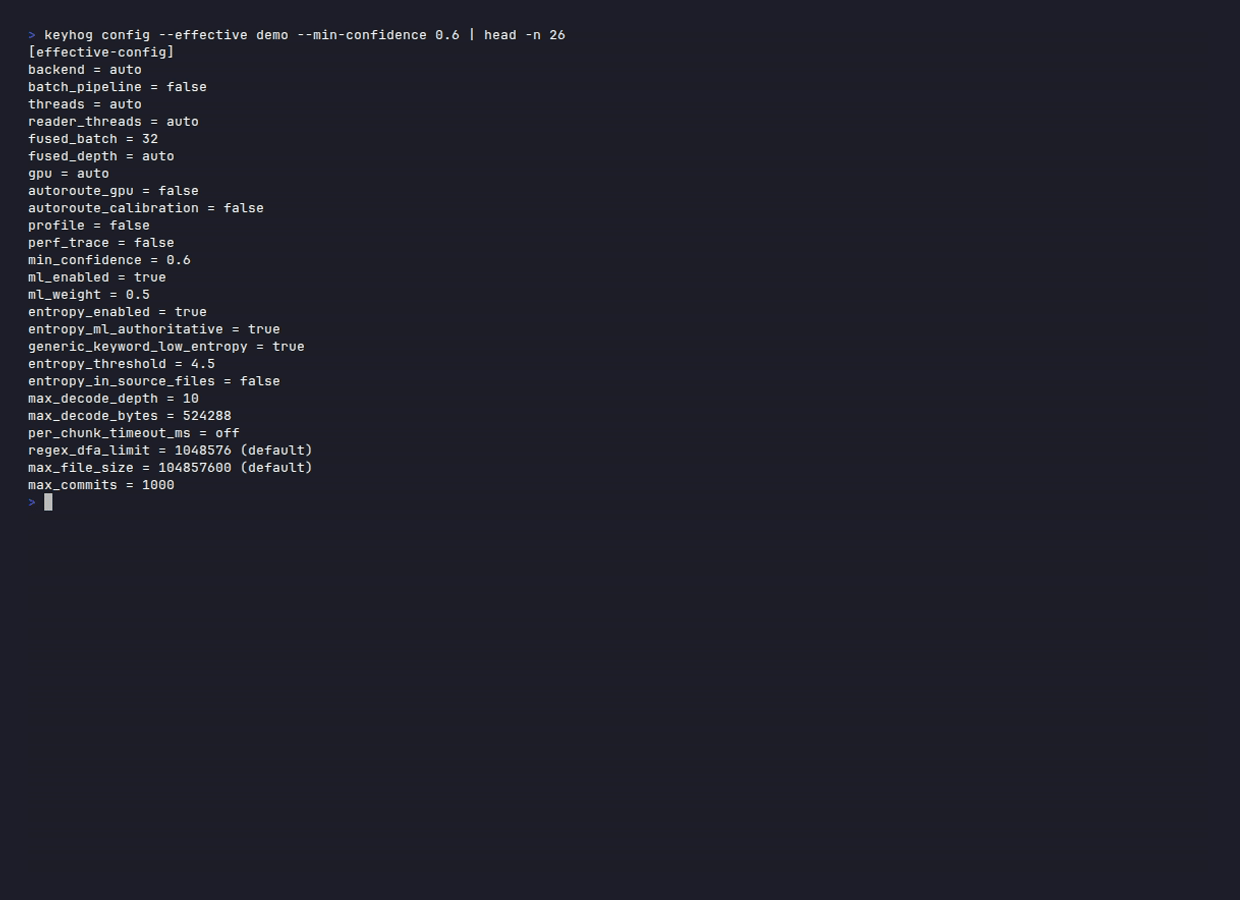
Open-source secret scanner in Rust

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

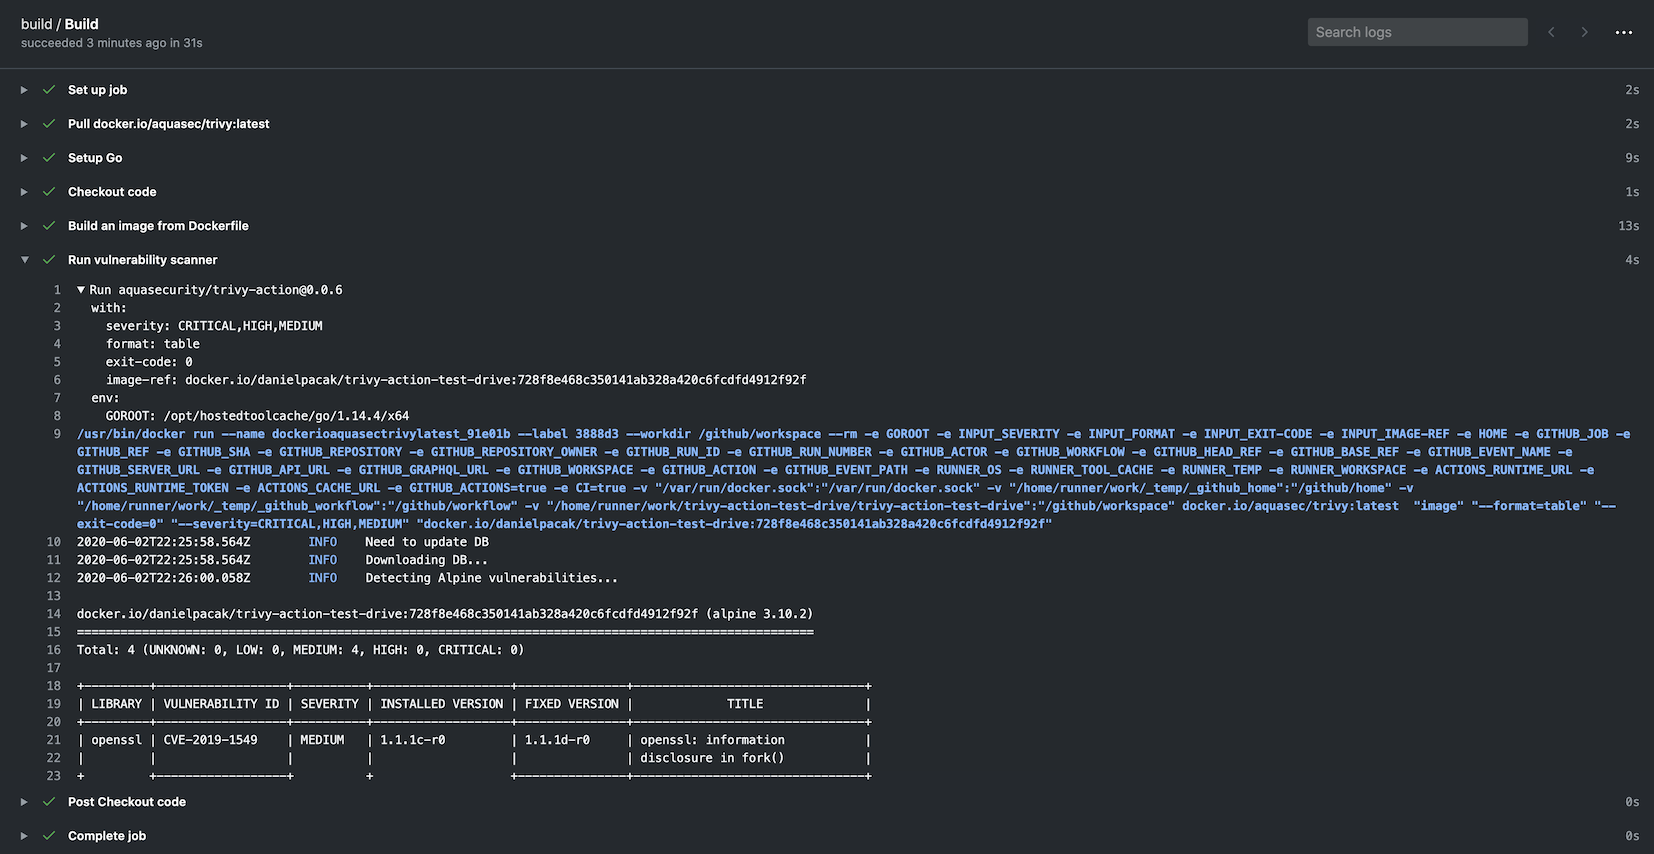
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities

Linux, macOS and Windows Install scripts for cnquery & cnspec

A fast enumeration tool for publicly exposed Azure Storage blobs.

Automated security checker for Kubernetes clusters with Istio service mesh, enforcing best practices via OPA policies and generating remediation…

KubeClarity is a tool for detection and management of Software Bill Of Materials (SBOM) and vulnerabilities of container images and filesystems