
agent
 bomfather/agent
eBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
cloud-securityconfiguration-auditingcontainer-security+2
32
bomfather/agenteBPF-based Linux agent that enforces executable-level access policies in kernel space, sandboxing processes and restricting file, network, and GPU…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 lucab85/log4j-cve-2021-44228
Ansible playbook automating Red Hat's Log4j detector script to scan Linux hosts for CVE-2021-44228 (Log4Shell) vulnerability with GPG verification.
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
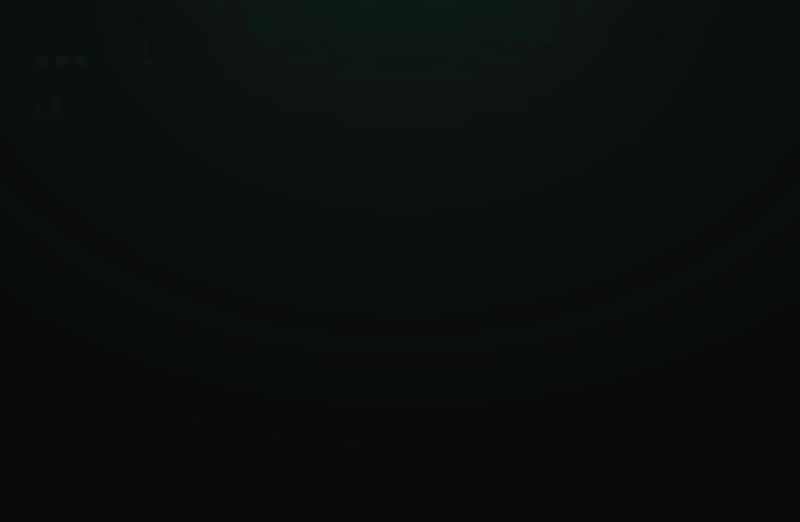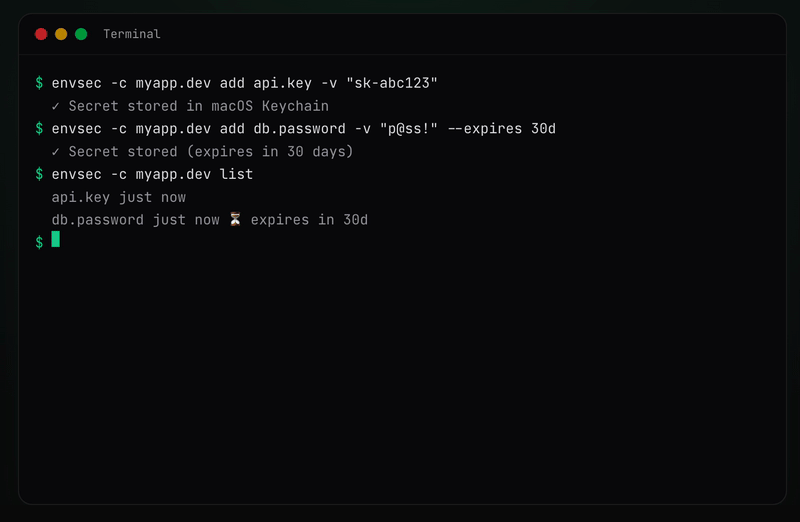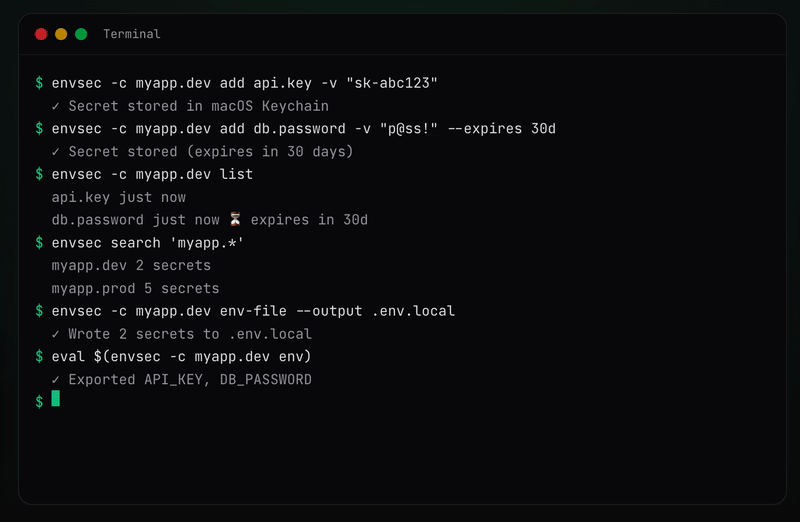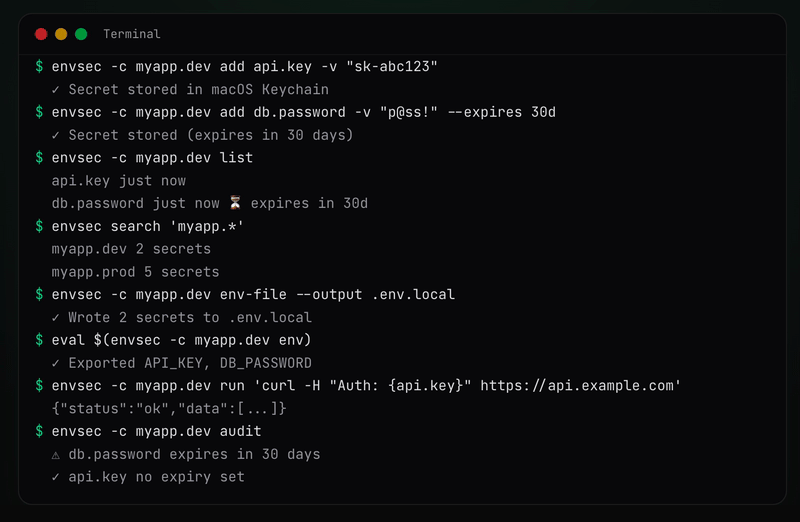 davidnussio/envsec
Secure CLI tool for managing environment secrets using native OS credential stores (macOS Keychain, Linux Secret Service, Windows Credential Manager)
 marcosimioni/omigood
OMIGOD! OM I GOOD? A free scanner to detect VMs vulnerable to one of the "OMIGOD" vulnerabilities discovered by Wiz's threat research team,…
 morpheuslord/startup-sbom
A tool to reverse engineer and inspect the RPM and APT databases to list all the packages along with executables, service, versions and CVE.
 cgwalters/container-cve-2021-22555
Containerized reproducer for CVE-2021-22555 Linux privilege escalation, with seccomp mitigation profiles and deployment guidance for Kubernetes and…
 discordianfish/cve-2022-0185-crash-poc
Docker container that runs a crash proof-of-concept for CVE-2022-0185, a Linux kernel vulnerability. Designed for unprivileged execution to test…
 lucab85/ansible-role-log4shell
Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).
 rio128128/copy-fail-cve-2026-31431
Copy Fail: 732 Bytes to Root on Every Major Linux Distribution.
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
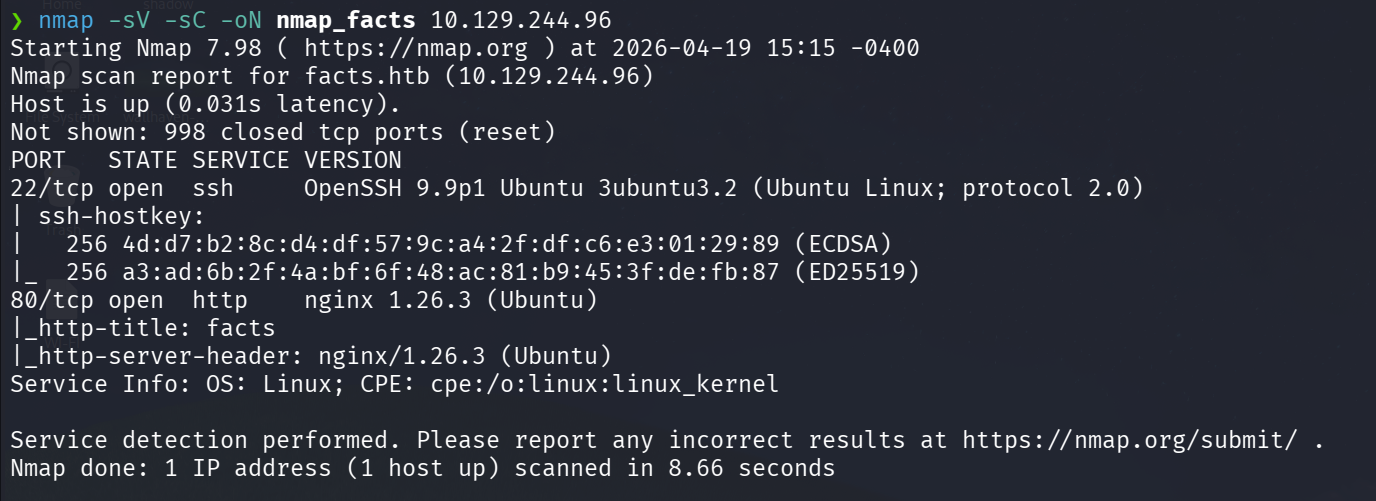 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 cj667113/oci-ansible-fix-cve-2026-31431
Ansible playbook that automates remediation of CVE-2026-31431 (Copy Fail) on OCI Linux instances by installing updated kernel packages, rebooting,…
 w4r10ck423/envvisualizer
Parse and visualize /proc/self/environ on compromised Linux boxes — categorizes env vars by tech stack (AWS, Django, Rails, NodeJS, MySQL, K8s,…