

CVE-2022-3294
 arbaaz29/cve-2022-3294
Privilege Escalation using nodes/proxy (create action allowed) and nodes/status (update/patch actions allowed)
cloud-securitycontainer-securityexploitation+3
arbaaz29/cve-2022-3294Privilege Escalation using nodes/proxy (create action allowed) and nodes/status (update/patch actions allowed)
 mrk336/cluster-chaos-exploiting-cve-2025-59359-for-kubernetes-takeover
A hands-on forensic walkthrough of CVE-2025-59359, a critical OS command injection flaw in Chaos-Mesh. Learn how attackers hijack Kubernetes clusters…
 fevar54/cve-2026-54420-litespeed-symlink-exploit
PoC de CVE-2026-54420: explotacion via symlink en el plugin LiteSpeed de cPanel/WHM.
 mrk336/azure-networking-privilege-escalation-exploit-cve-2025-54914
CVE-2025-54914 exposes a critical flaw in Azure Networking that allows attackers to escalate privileges and control routing across subnets. The…
 beelzebruh/cve-2019-5737
Exploit for CVE-2019-5737, a Docker runc container escape vulnerability, with build and run instructions for Linux and Windows.
 xrayzen/cve-2025-9074-poc
2025年8月20日に公開されたDockerDesktopの脆弱性(対策済み)を実証する
 vincentdthe/cve-2025-53786
Proof-of-concept exploit for CVE-2025-53786, demonstrating privilege escalation in hybrid Microsoft Exchange environments via misconfigured trust…
 a1ex-var1amov/ctf-cve-2019-11043
Intentionally vulnerable PHP app with Nginx/PHP-FPM setup for reproducing CVE-2019-11043, including Docker and Kubernetes deployment,…
 rockmelodies/blackash-cve-2025-41115
CVE-2025-41115
 thelsa/harbor-give-me-admin
harbor(<1.7.6/1.8.3) privilege escalation (CVE-2019-16097)
 ugorange/cve-2022-3172
Proof-of-concept exploit for CVE-2022-3172 in Kubernetes, demonstrating unauthorized access to metrics API via a crafted token.
 khuntor/cve-2021-43858-minio
Go-based exploit for CVE-2021-43858 targeting MinIO privilege escalation vulnerability. Executes against a specified IP and port to demonstrate the…
 acfirthh/cve-2021-41805
A proof-of-concept for CVE-2021-41805 which is a vulnerability in HashiCorp Consul Enterprise allowing for Remote Code Execution (RCE) with escalated…
 charondefalt/cve-2023-34039
VMware exploit
 certologists/modified-cve-2024-37081-poc
Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.
 abdurahmon3236/cve-2024-36539
PoC exploit for insecure permissions in Contour v1.28.3 that retrieves a Kubernetes service account token and accesses the cluster API, demonstrating…
 abian2/cve-2024-21626
Proof-of-concept for CVE-2024-21626, a container escape vulnerability in runc, demonstrating exploitation techniques.
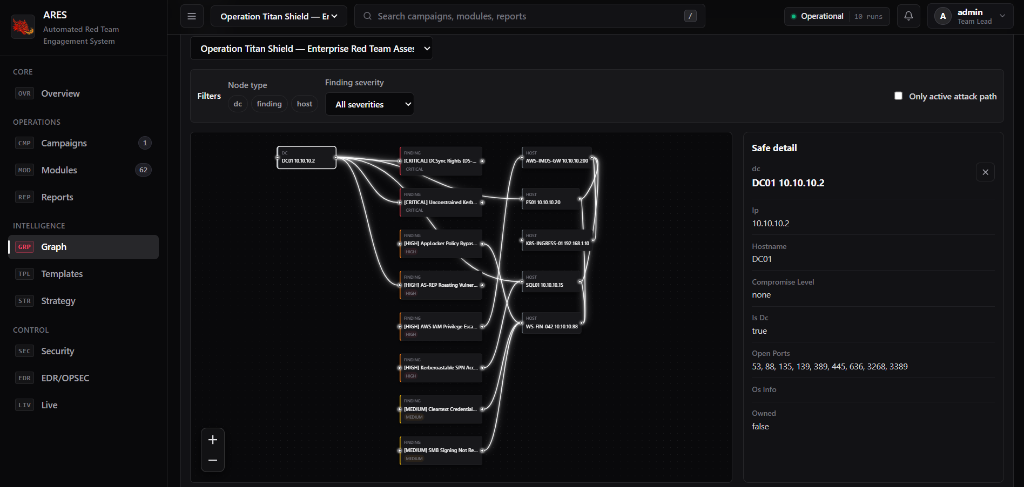 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…