
CVE-2026-43813
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
authentication-authorizationbinary-analysiscloud-security+5
9
eastarctica/cve-2026-43813CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 ash1996x/cve-2025-54914-poc
Exploit for CVE-2025-54914 in Azure Networking, creating malicious routes with evasion, persistence, multi-target scanning, and reporting for…
 netwrix/pingcastlecloud
Audit program for AzureAD
 trailofbits/algo
Set up a personal VPN in the cloud
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 awarexone/agentic-bug-hunter
AI-powered bug bounty hunting toolkit that works with or without subscription.
 elastic/agent-skills
Official Elastic Skills
 logisek/huntcyberark
CyberArk Security Audit
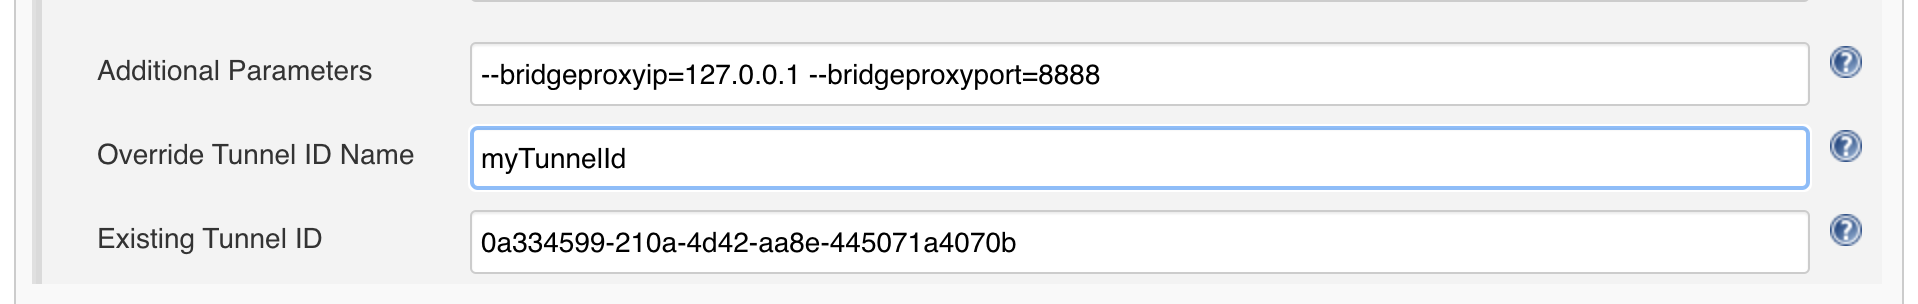 shoucheng3/jenkinsci__perfecto-plugin_cve-2020-2261_1-17
Jenkins plugin for automated mobile app testing via Perfecto cloud, managing secure tunnel connections and app uploads within CI/CD pipelines.
 cyberark/shimit
A tool that implements the Golden SAML attack
 mr-un1k0d3r/azureredops
Azure RedOps is a offensive security toolkit for assessing the security posture of Microsoft Entra ID
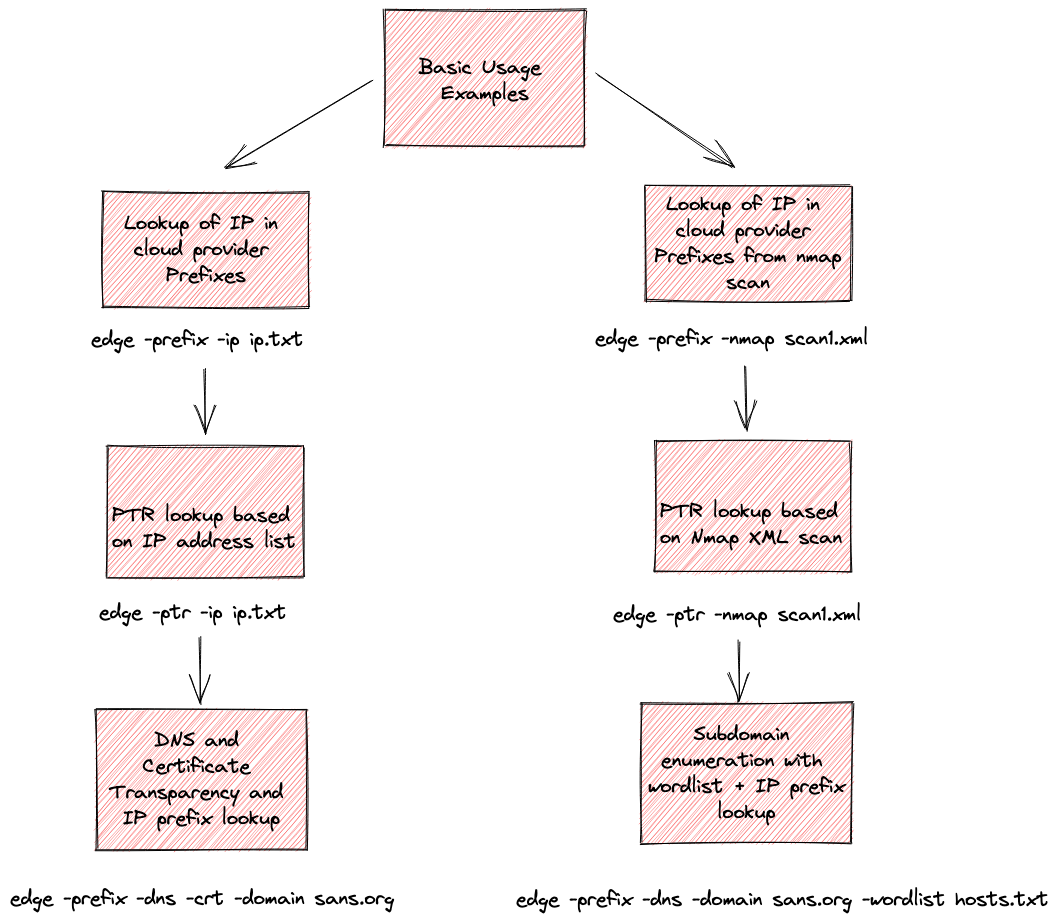 iknowjason/edge
Whois for the Cloud: Recon tool for cloud provider attribution. Supports AWS, Azure, Google, Cloudflare, and Digital Ocean.
 irsl/google-osconfig-privesc
Proof of concept about the privilege escalation flaw identified in Google's Osconfig
 ank1036official/cloudcheck
Checks using a test string if a Cloudflare DNS bypass is possible using CloudFail.
 oscerd/cve-2026-46456
Reproducer for CVE-2026-46456 — Apache Camel camel-aws2-sqs inbound message-attribute header injection (Camel control-header injection via…
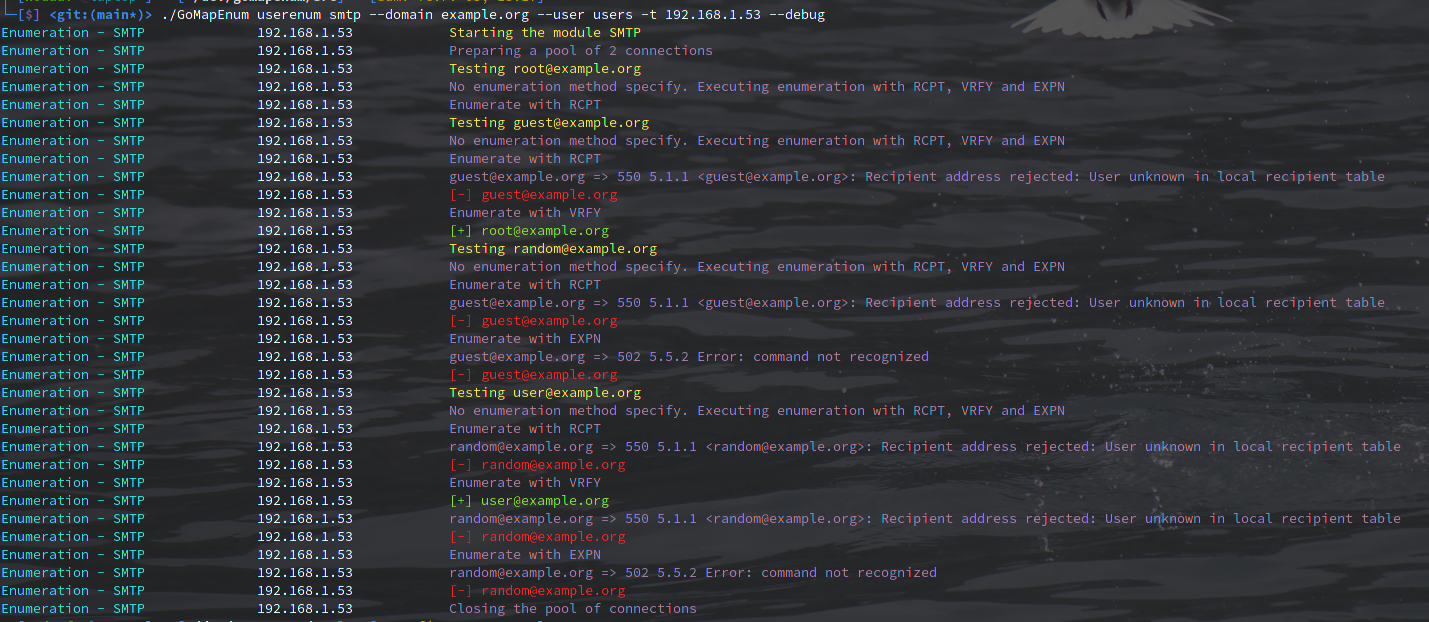 nodauf/gomapenum
User enumeration and password bruteforce on Azure, ADFS, OWA, O365, Teams and gather emails on Linkedin
 cnotin/m365_groups_enum
Enumerate Microsoft 365 Groups in a tenant with their metadata