CVE-2022-0492-Checker
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
cloud-securitycontainer-escapecontainer-security+3
13
sofianehamlaoui/cve-2022-0492-checkerA script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
 penteraio/cve-2022-22948
Scanner for CVE-2022-22948 an Information Disclosure in VMWare vCenter
 penteraio/vscalation-cve-2021-22015
Scanner for vScalation (CVE-2021-22015) a Local Privilege Escalation in VMWare vCenter
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 brompwnie/cve-2019-1002101-helpers
PoC helper scripts and Dockerfile for CVE-2019-1002101
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
 masahiro331/kube-trivy
Trivy for Kubernetes
 snailsploit/cve-2026-3288
Walkthrough: ingress-nginx Configuration Injection via rewrite-target Annotation
 heroku/heroku-cve-2013-0156
Inspect all of your heroku apps to see if they are running a vulnerable version of Rails
 mrunalp/block-copyfail
BPF LSM blocker for CVE-2026-31431 (Copy Fail) - zero-reboot remediation for OpenShift 4
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554
 deckhouse/d8-copy-fail-mitigation
Kubernetes-native CVE-2026-31431 mitigation with automated kernel module blocking, runtime Falco detection rules, and bashible-based node…
 grabesec/xcp_ng_cve-2026-43284_tester
Tester for CVE-2026-43284
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
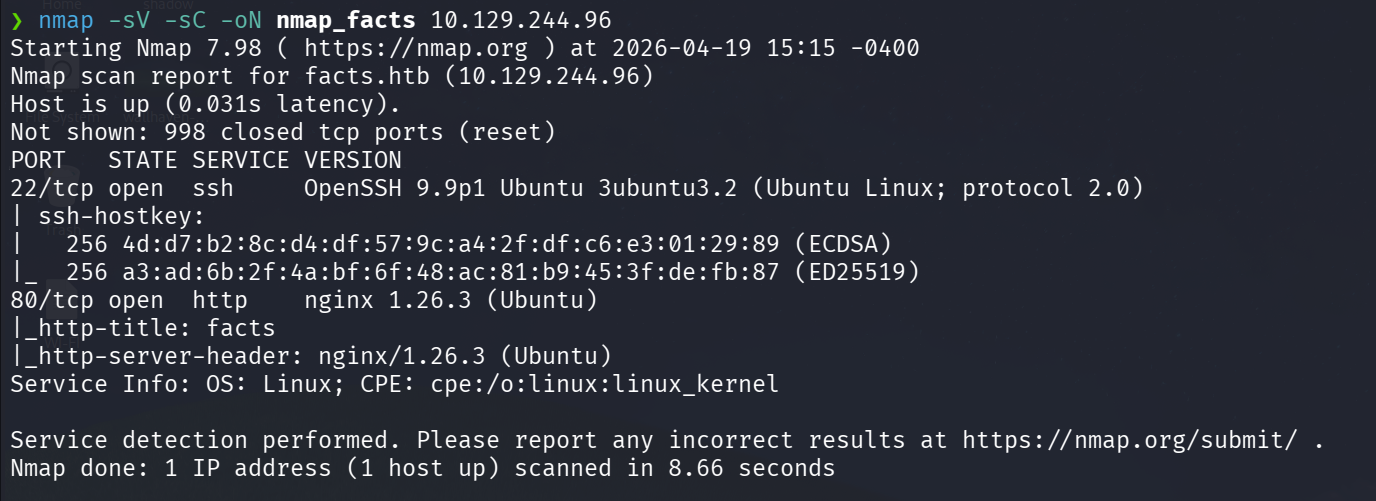 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
 bbo513/cve-2023-7231
PoC and Disclosure for CVE-2023-7231 – Memcached Gopher RCE chain