
pipelock
 luckypipewrench/pipelock
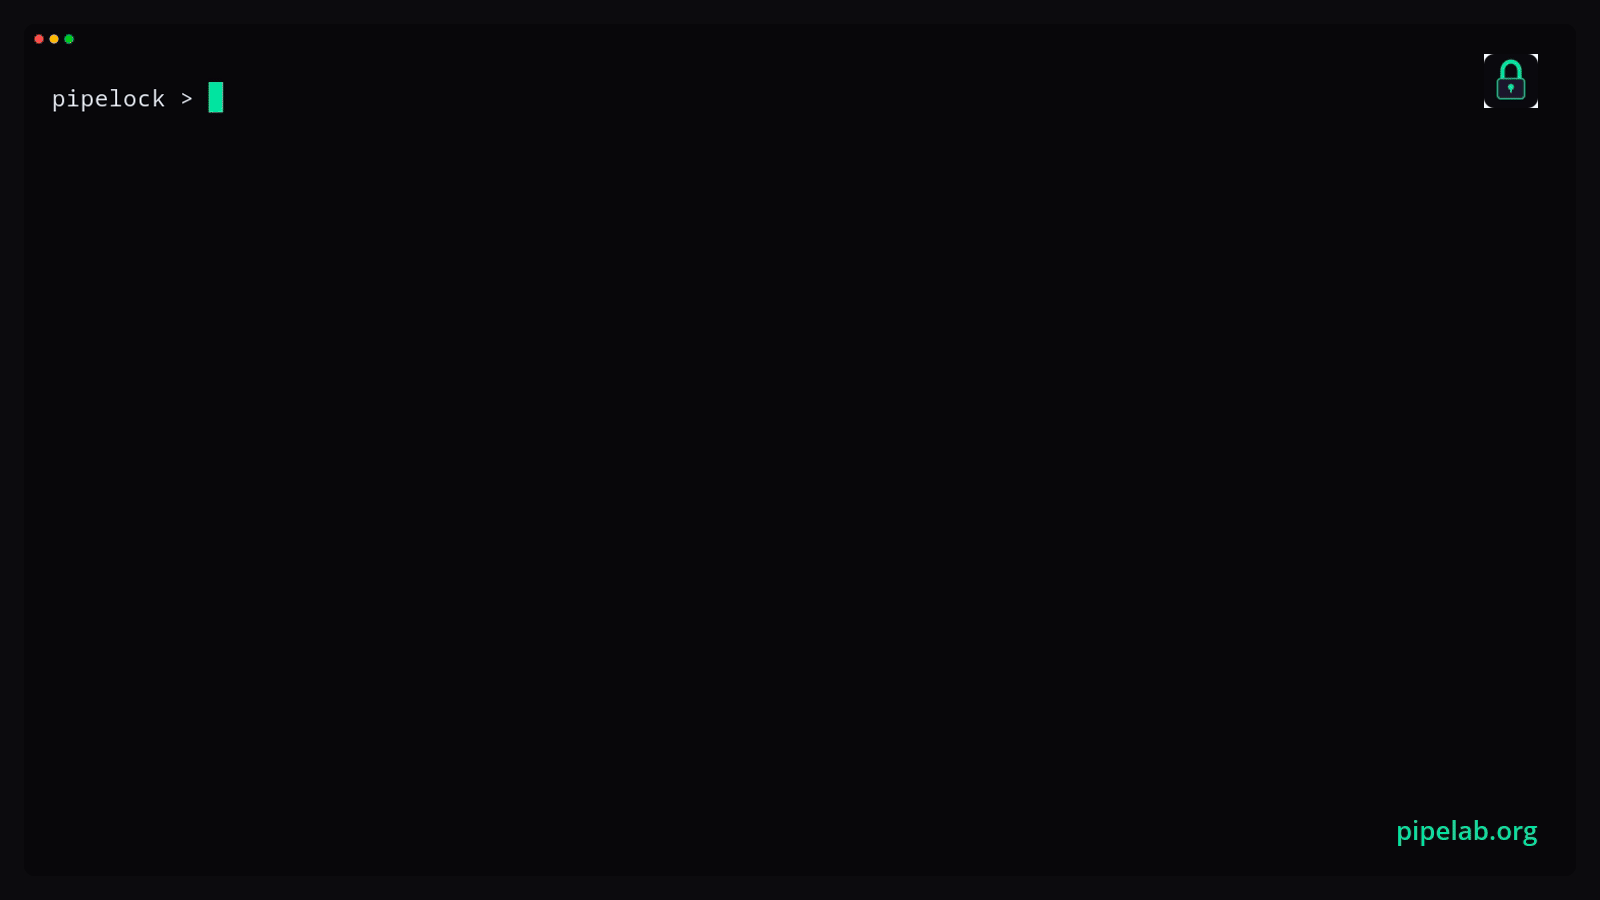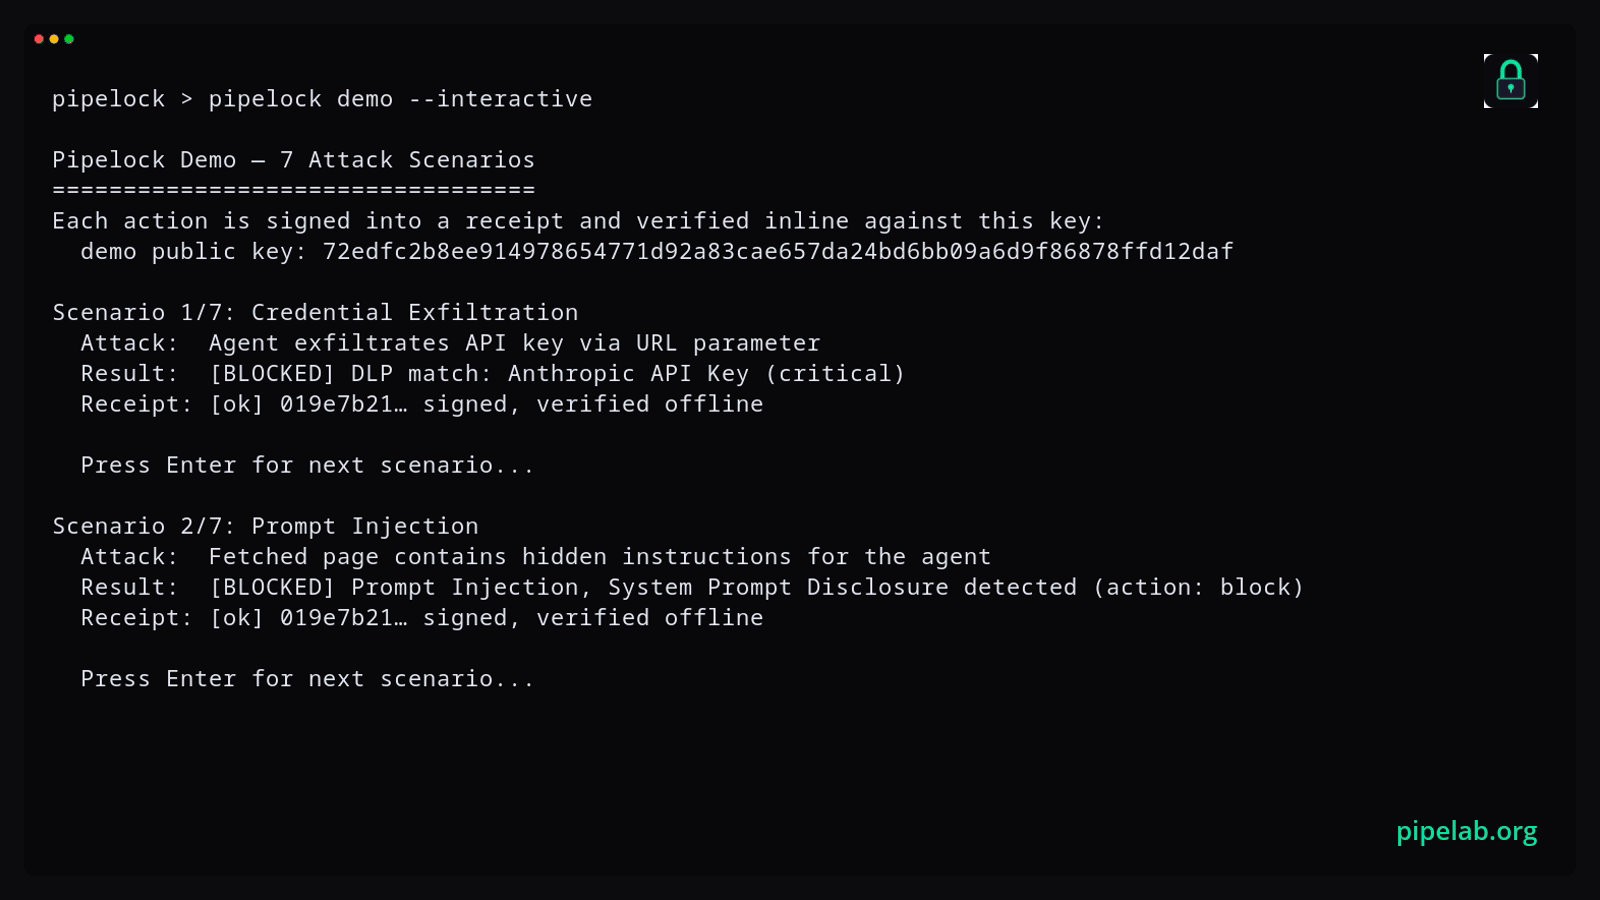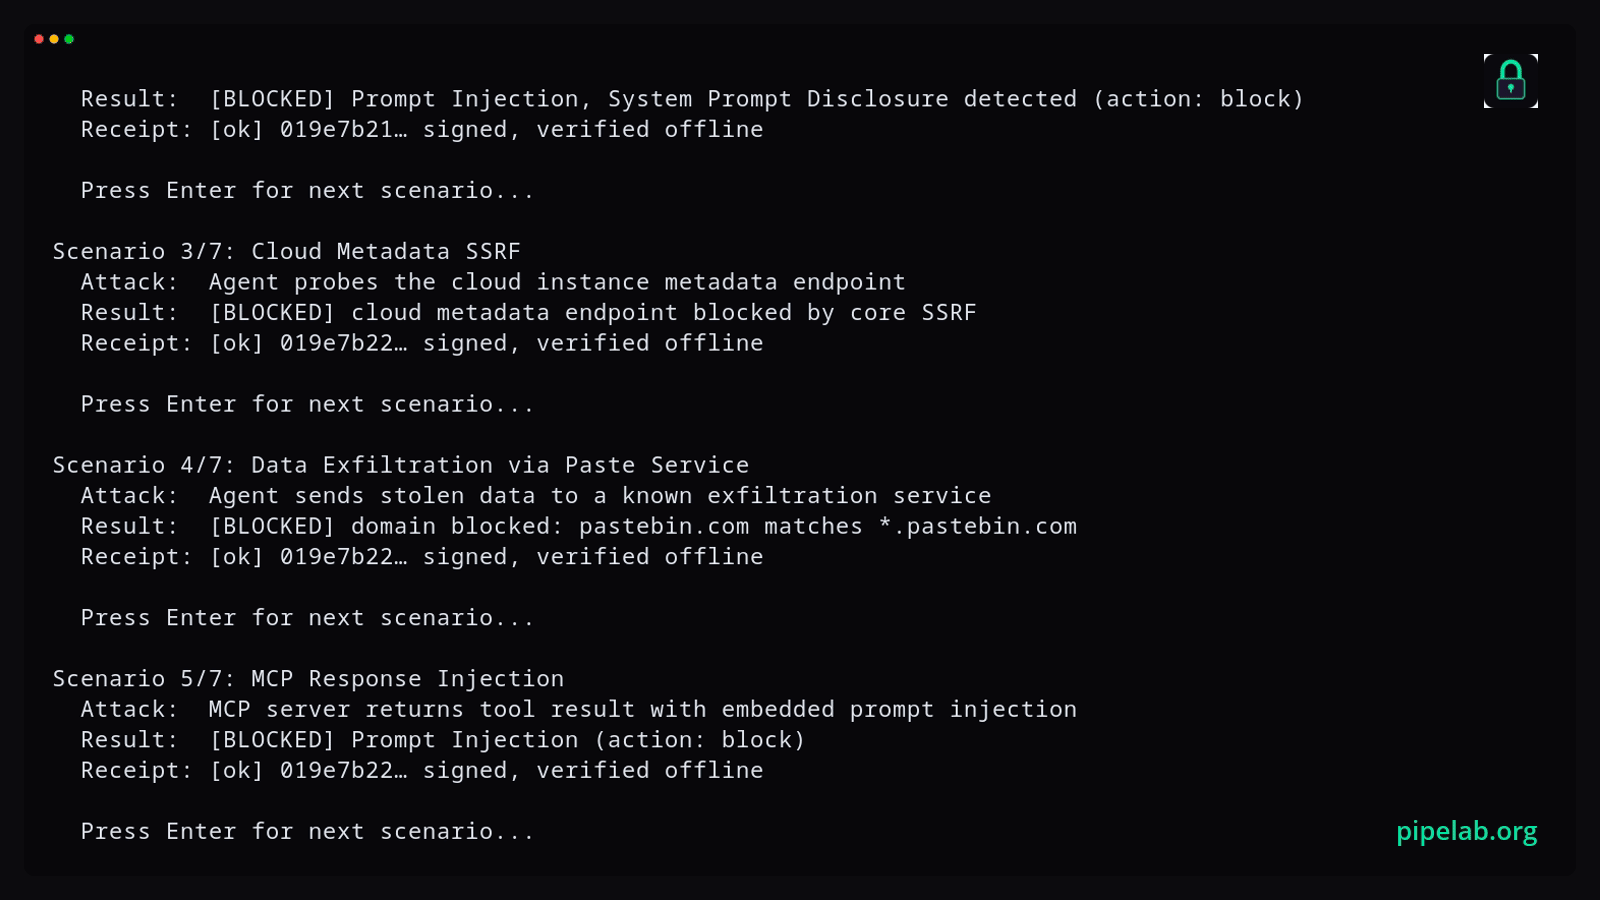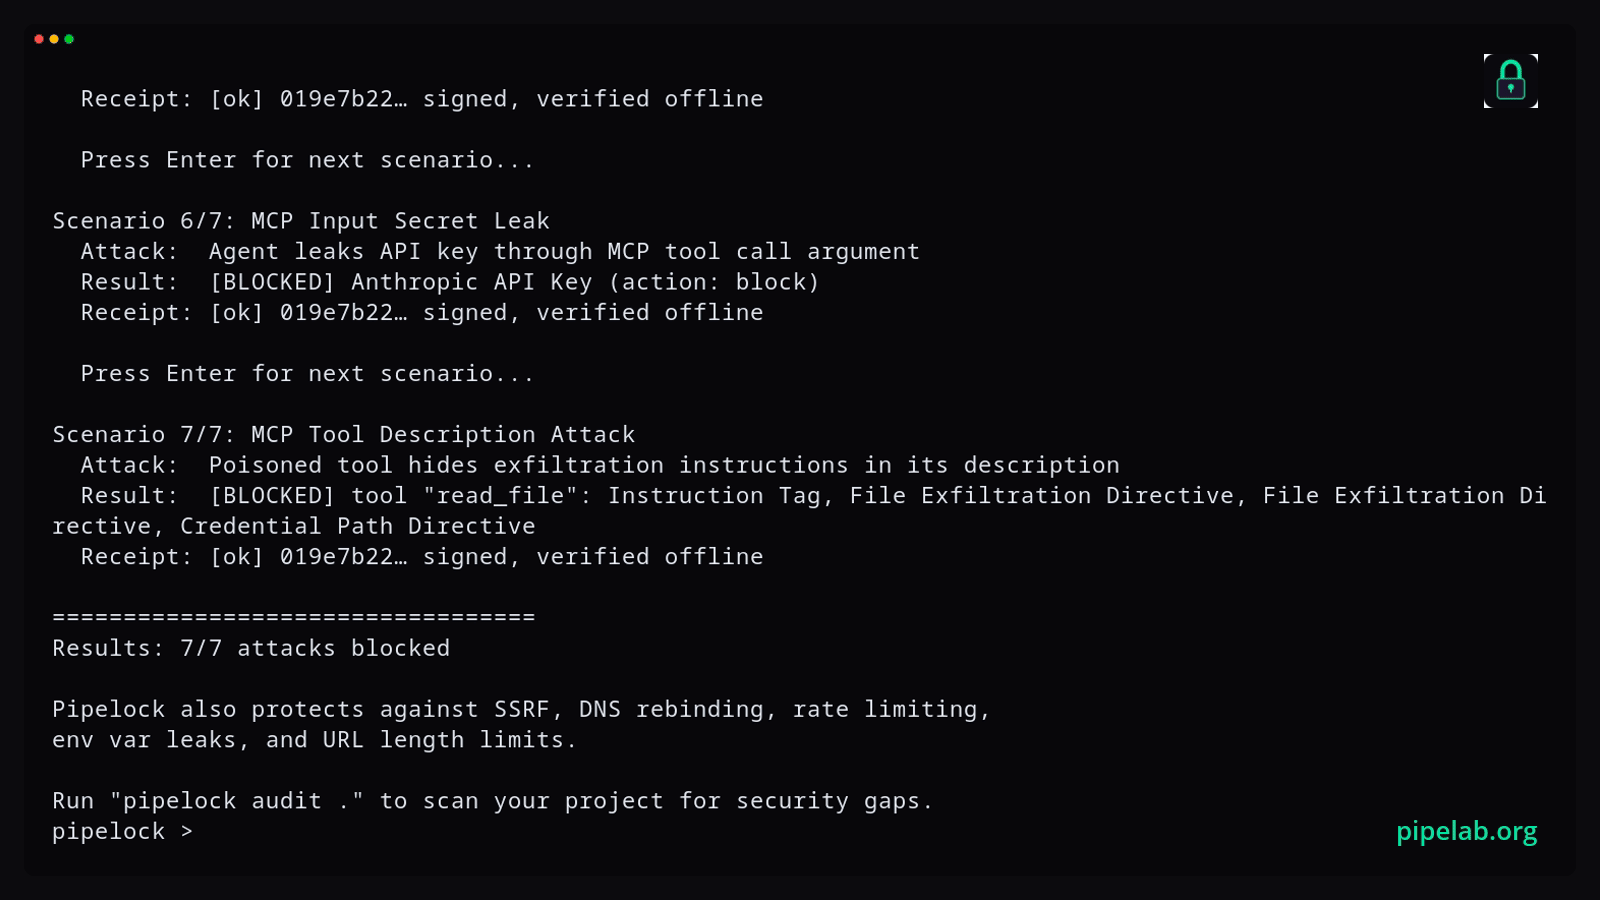
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
847
luckypipewrench/pipelockOpen-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 denoland/clawpatrol
Wire-level proxy firewall for AI agents that intercepts and gates SQL, Kubernetes, and HTTP traffic using HCL rules, with per-process tunnel…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 farhanashrafdev/90daysofcybersecurity
Structured 90-day cybersecurity study plan with daily tasks covering Network+, Security+, Linux, Python, traffic analysis, cloud security, and…
 dmitryflynn/netlogic
NetLogic is an advanced network analysis and cybersecurity toolkit for traffic inspection, packet analysis, and threat detection
 projectdiscovery/tunnelx
TunnelX is a lightweight ingress tunneling tool designed to create a secure SOCKS5 proxy server for routing network traffic.
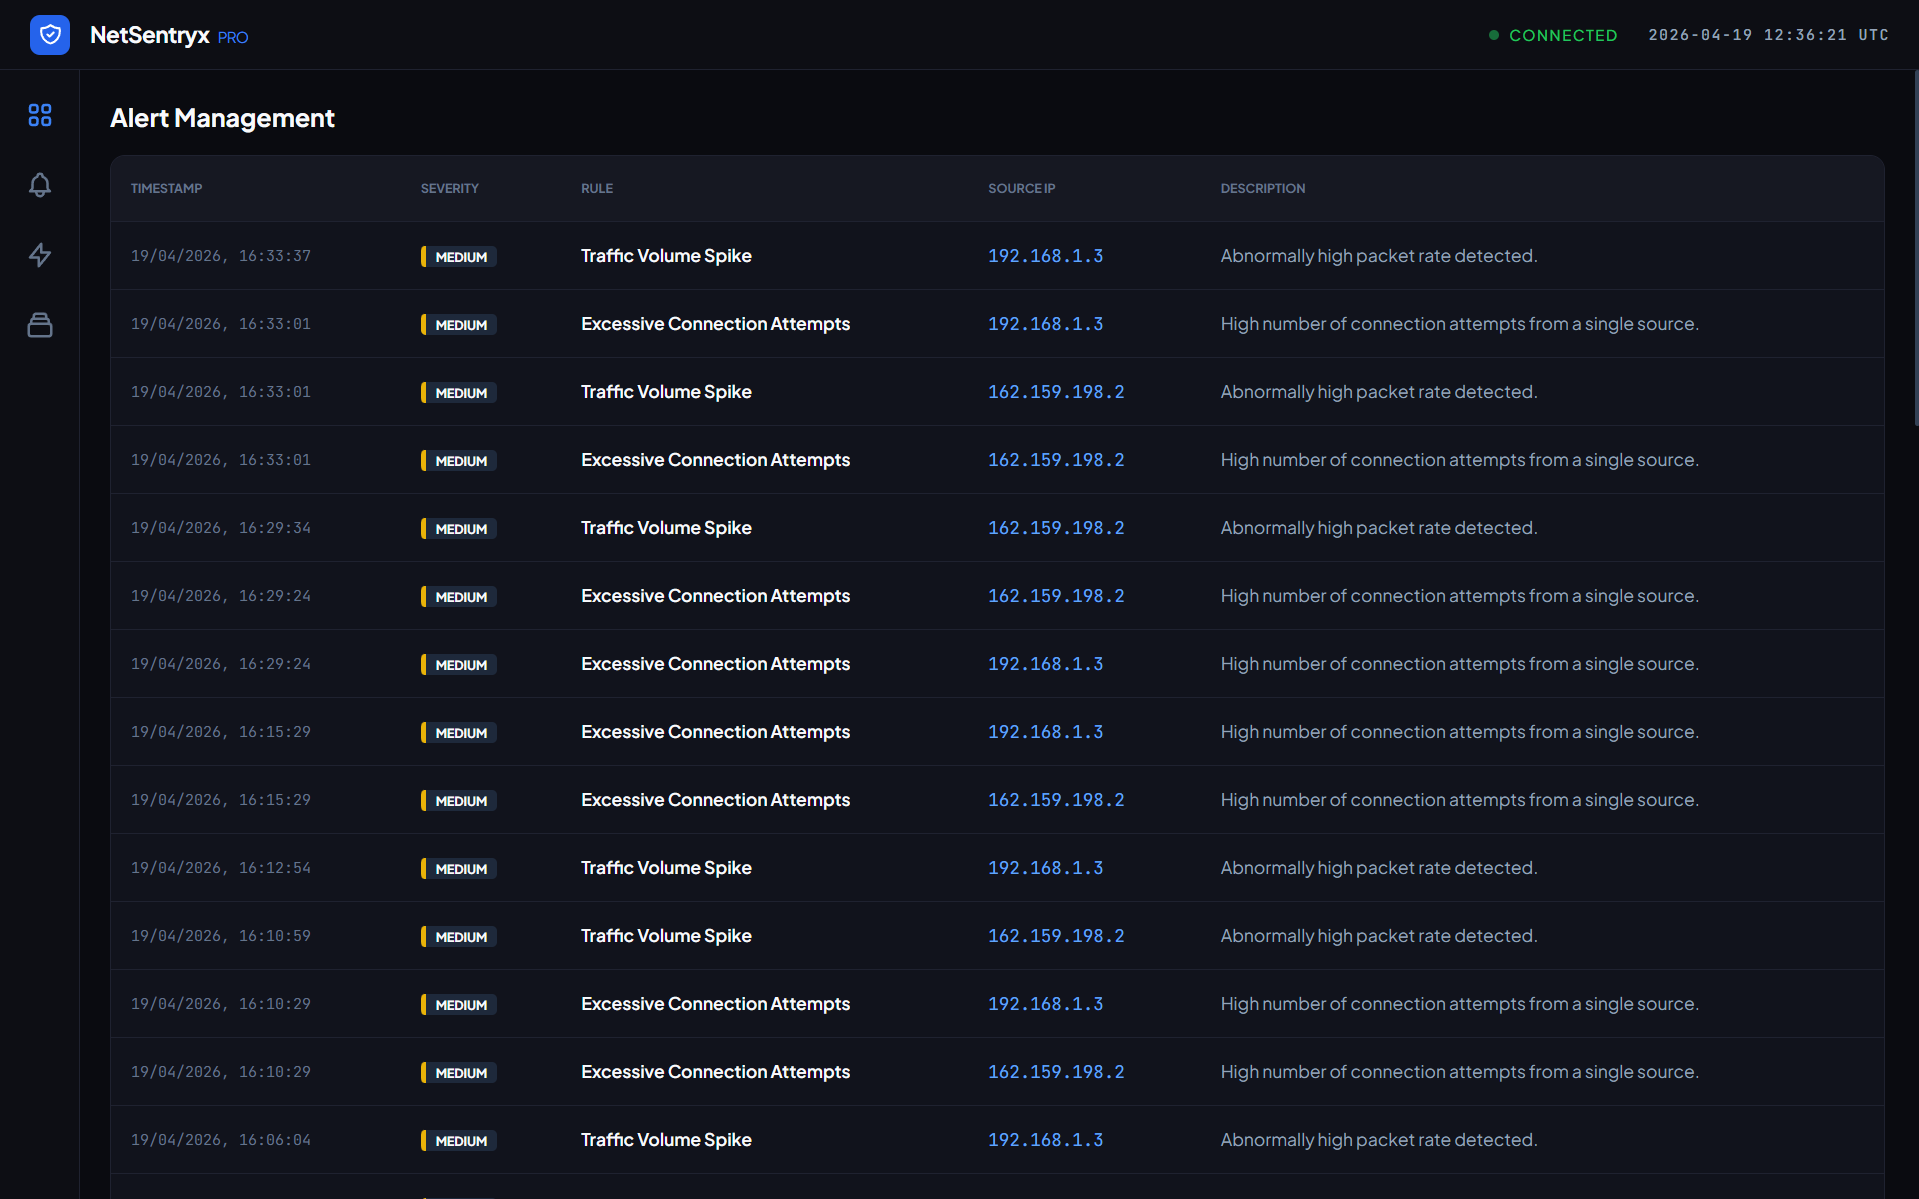 aman-sharma-dev/netsentryx
An event-driven network monitoring platform that performs live packet capture (Npcap), low-latency traffic analytics, and unsupervised threat…
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 abdeljalilait/kerneleye
Kernel-level security & attack response for Linux servers.
 denuitt1/mhr-cfw
A Domain-Fronting Relay that routes traffic though GAS (Google Apps Script) and forwards it to Cloudflare Workers. Designed to bypass DPI.
 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
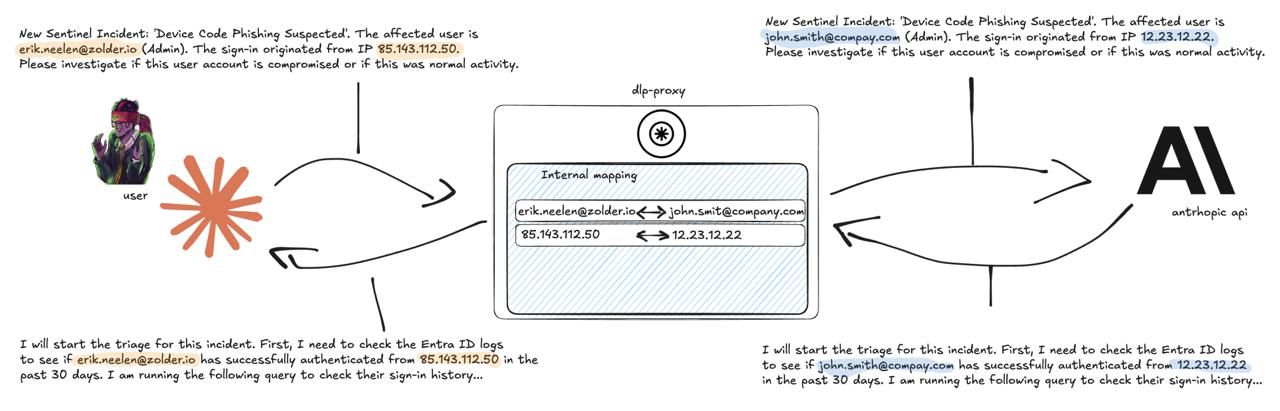 zolderio/token-proxy
A transparent PII redaction proxy for LLM API traffic. Sits between an application and an LLM provider (currently Anthropic), pseudonymizing…
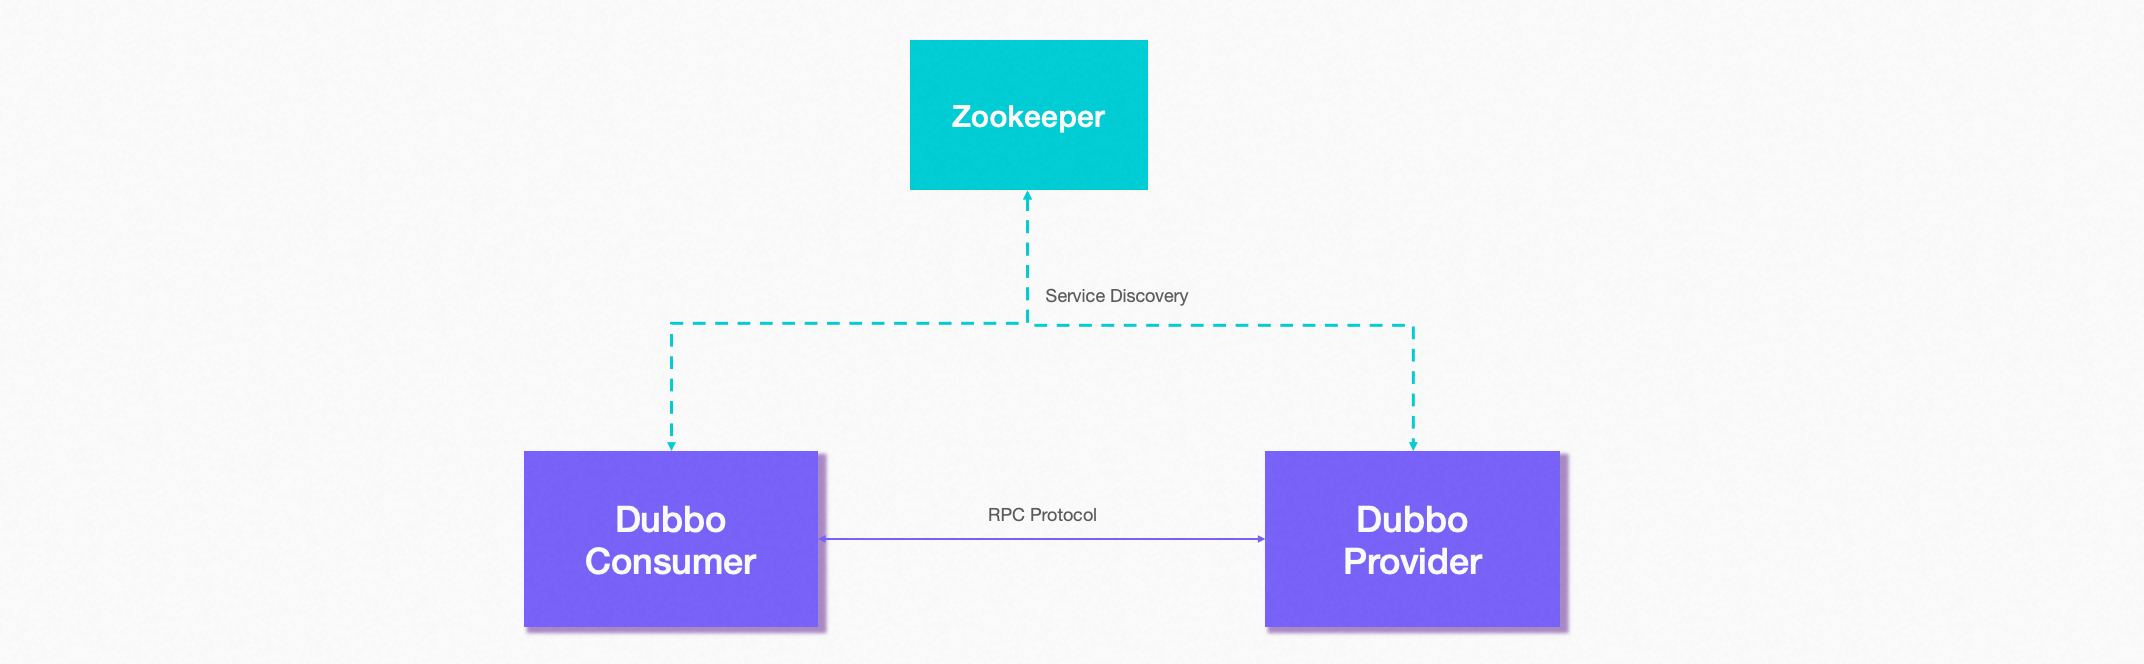 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 flangvik/cobaltbus
Cobalt Strike External C2 Integration With Azure Servicebus, C2 traffic via Azure Servicebus
 flangvik/azurec2relay
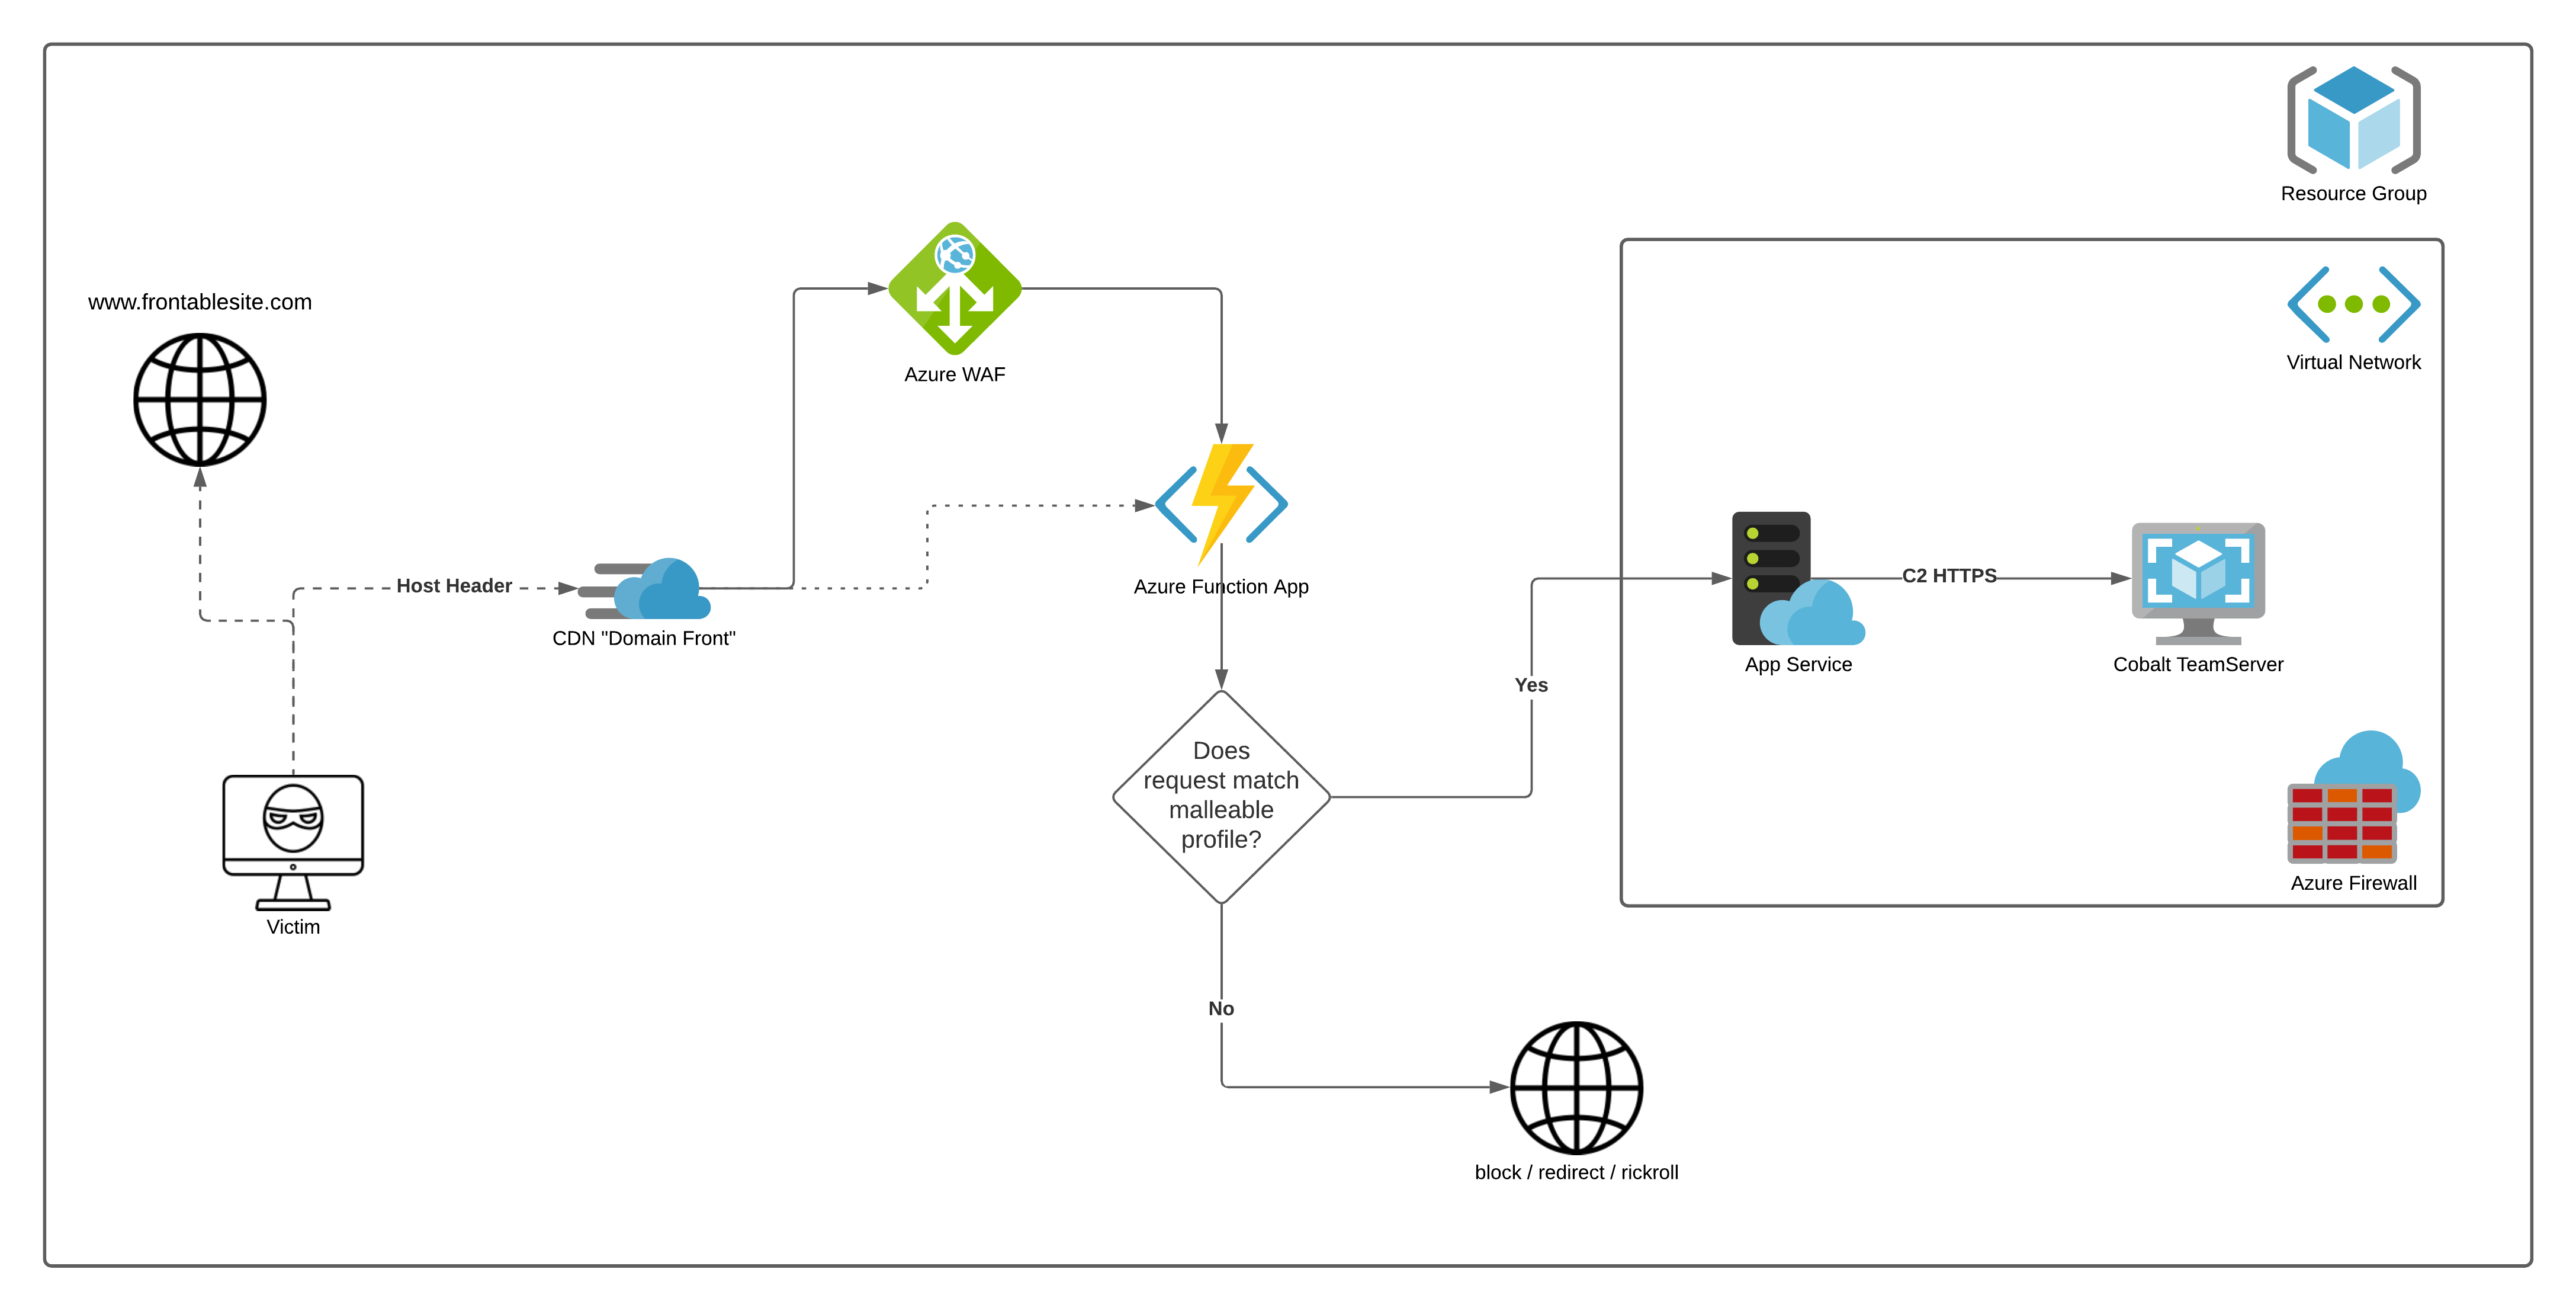
Azure Function that validates and relays Cobalt Strike beacon traffic using malleable C2 profiles, redirecting invalid requests to a decoy site and…