
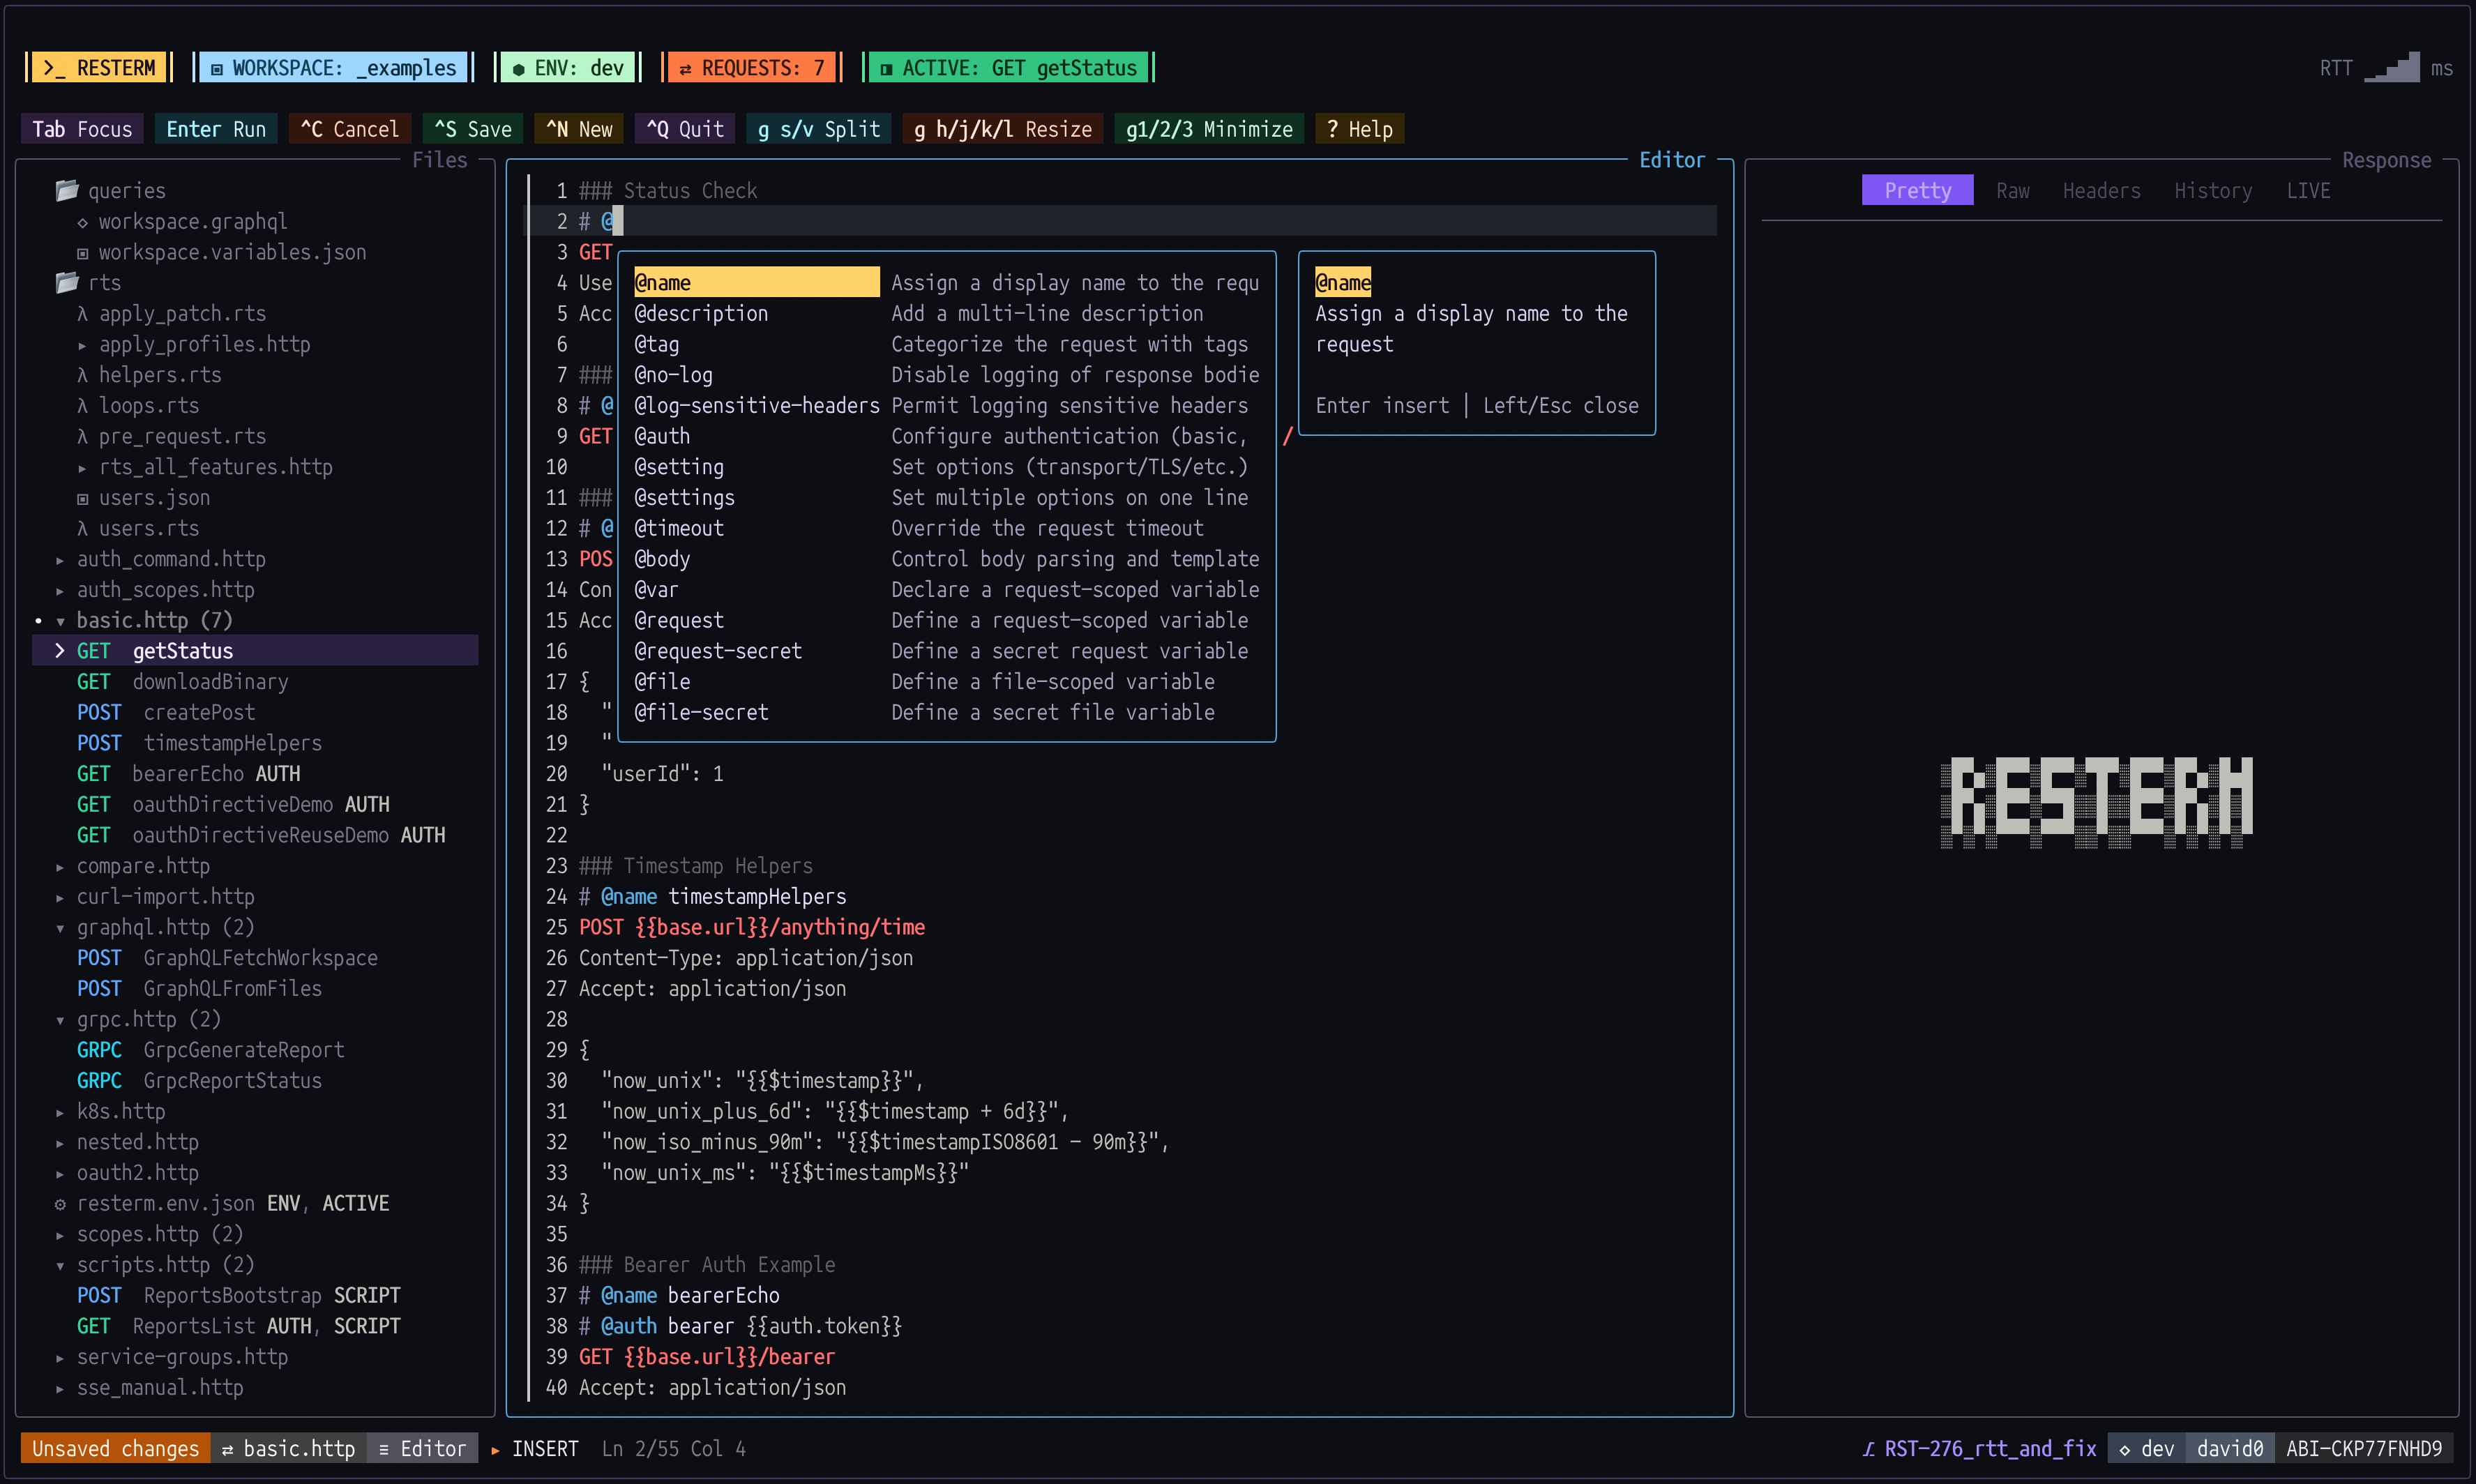
resterm
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
api-security-testingcloud-securitydevsecops+3
unkn0wn-root/restermTerminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 foxboron/ssh-tpm-agent
SSH agent that creates and manages TPM-sealed keys for hardware-bound authentication, supporting key generation, import, wrapping, PIN protection,…
 gravitational/teleport
The easiest, and most secure way to access and protect all of your infrastructure.
 pirafrank/vault-conductor
An SSH Agent that provides SSH keys stored in Bitwarden Secrets Manager
 0xdak/cve-2026-44881_exploit
Single-script exploit for CVE-2026-44881 that chains .git credential leakage, Portainer Git-symlink injection, arbitrary host file read, and SSH…
 suriyaboon/hackthebox-facts
HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
 tstephens1080/palo-alto-cve-2026-0265-checker
Python script to sweep a fleet of Palo Alto firewalls and Panoramas via SSH, check PAN-OS version against CVE-2026-0265 (Authentication Bypass via…
 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 blacknon/lssh
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
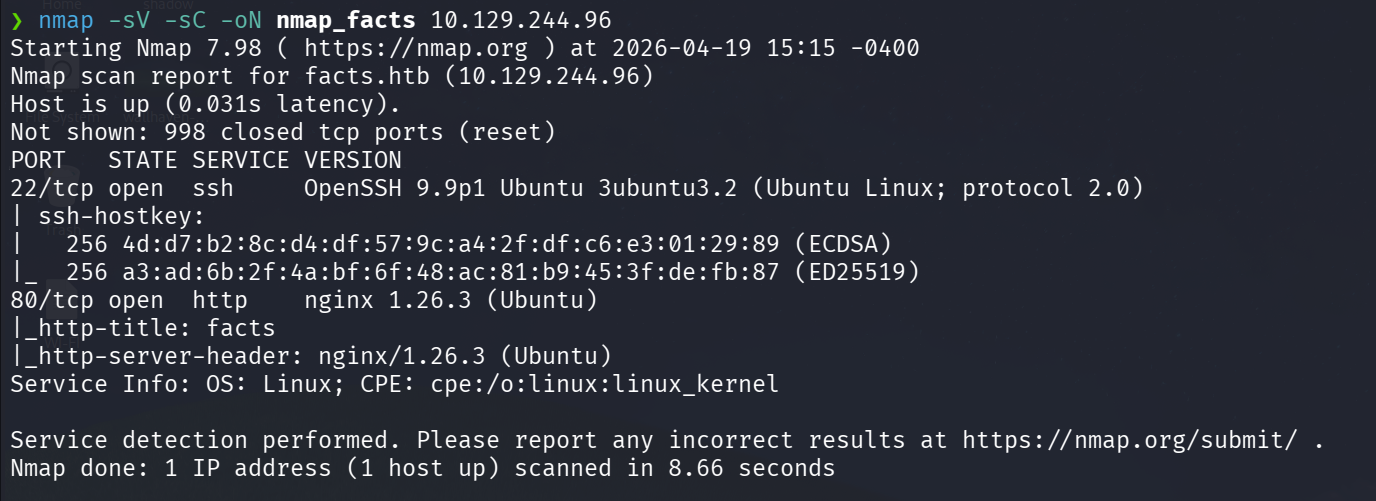 mattiapertusati/htb-facts
HackTheBox — Facts (Easy/Linux) | CVE-2025-2304 + AWS S3 + SSH Key + Facter PrivEsc
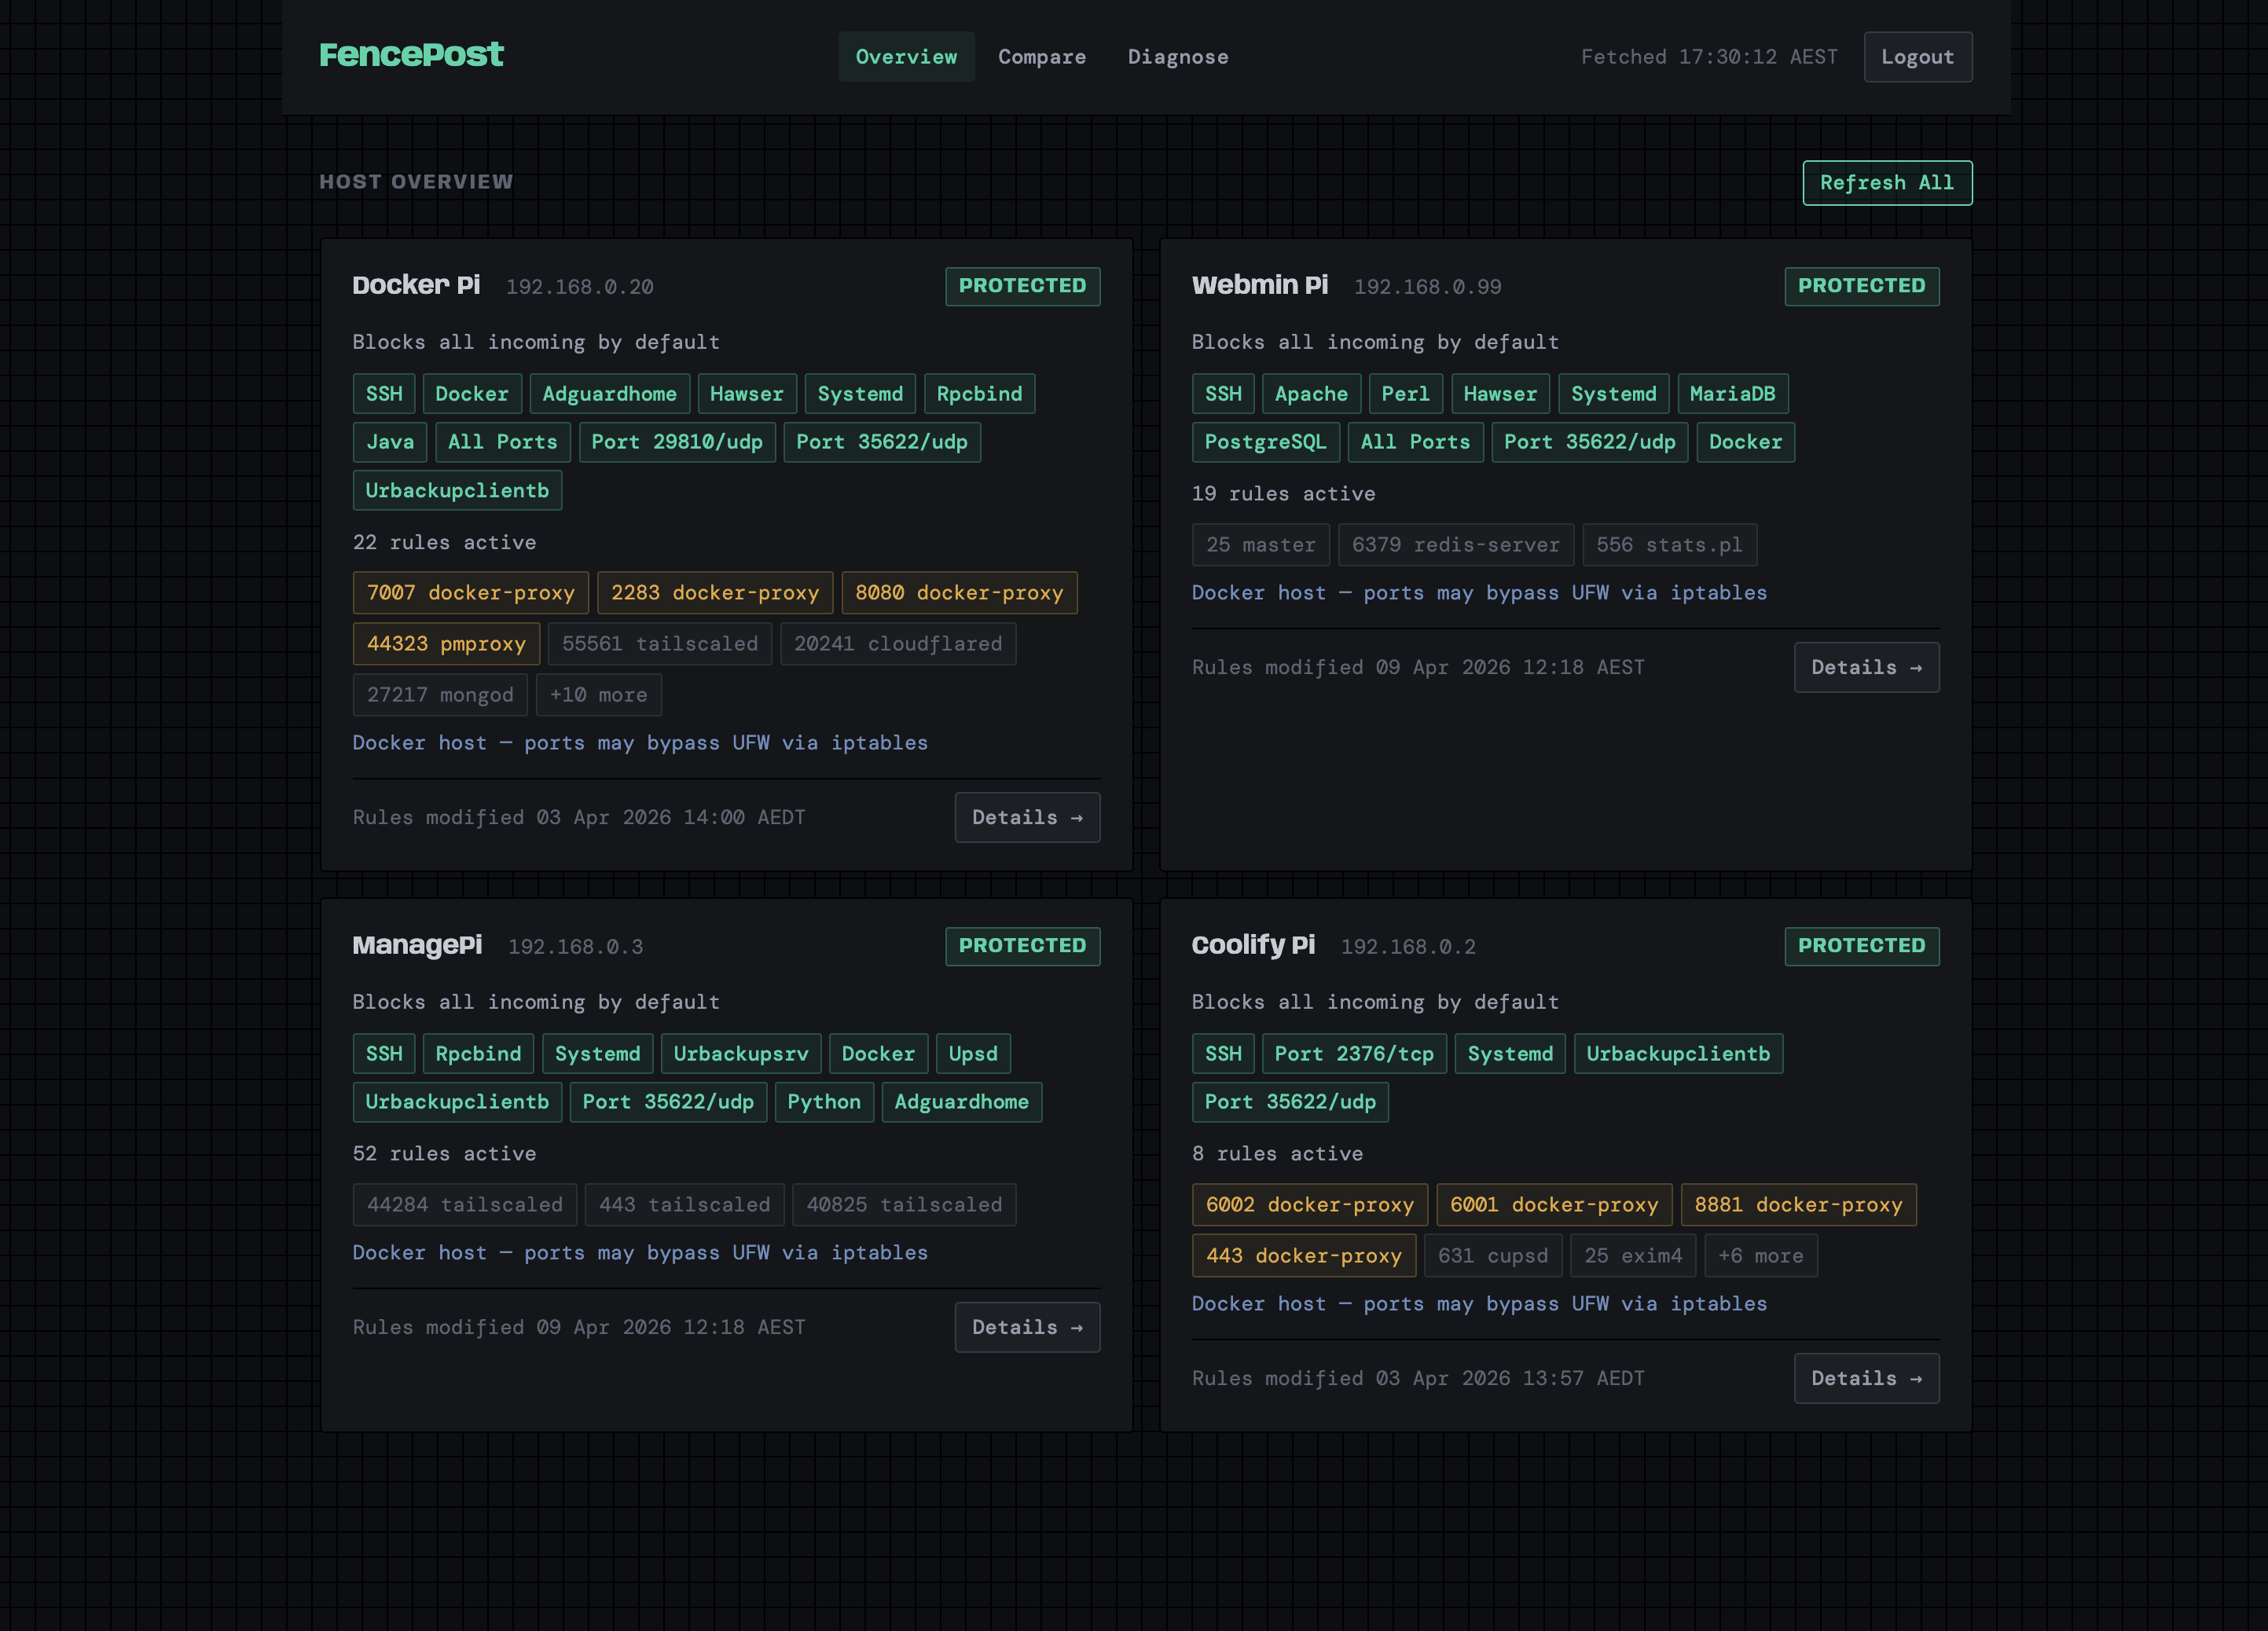 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 elkirrs/dumper
CLI utility for creating encrypted database backups (PostgreSQL, MySQL, MongoDB) with support for multiple storage backends (SFTP, S3, Azure), SSH…
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…