

BloodBash
 squidsec/bloodbash
Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
cloud-securityconfiguration-auditingidentity-access-management+6
499
squidsec/bloodbashOffline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…
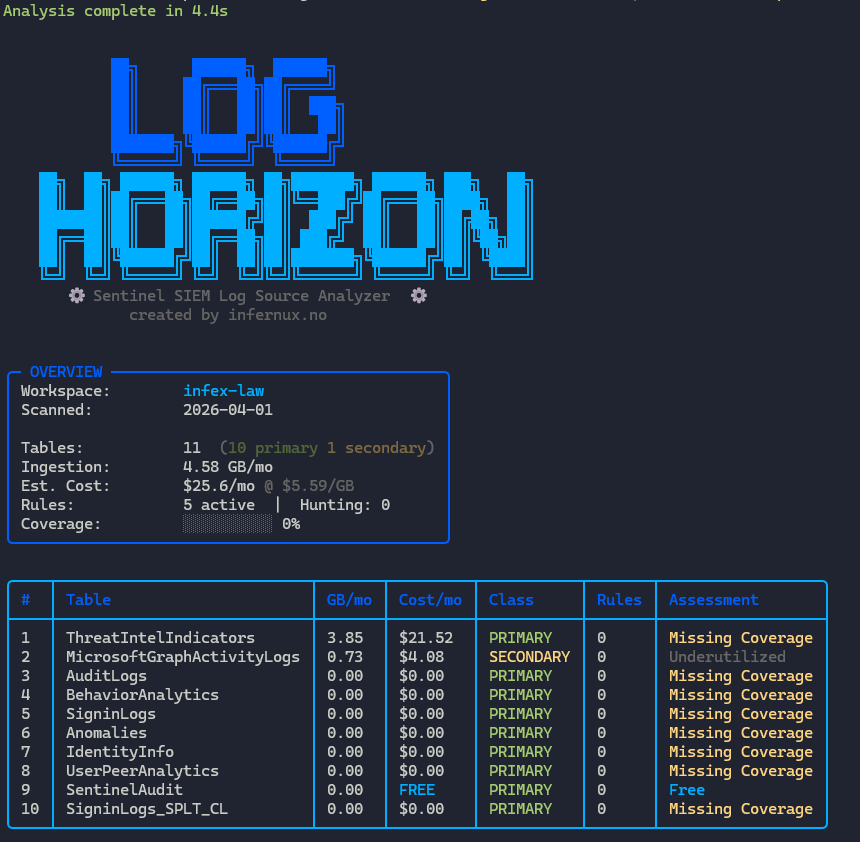 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 szzxli/soc-home-lab
Hands-on SOC lab: AWS mini-SOC with CloudTrail/GuardDuty, a Python CloudTrail IOC analyzer, phishing header forensics, ELF binary triage, and agent…
 skyscanner/cfripper
Library and CLI tool for analysing CloudFormation templates and check them for security compliance.
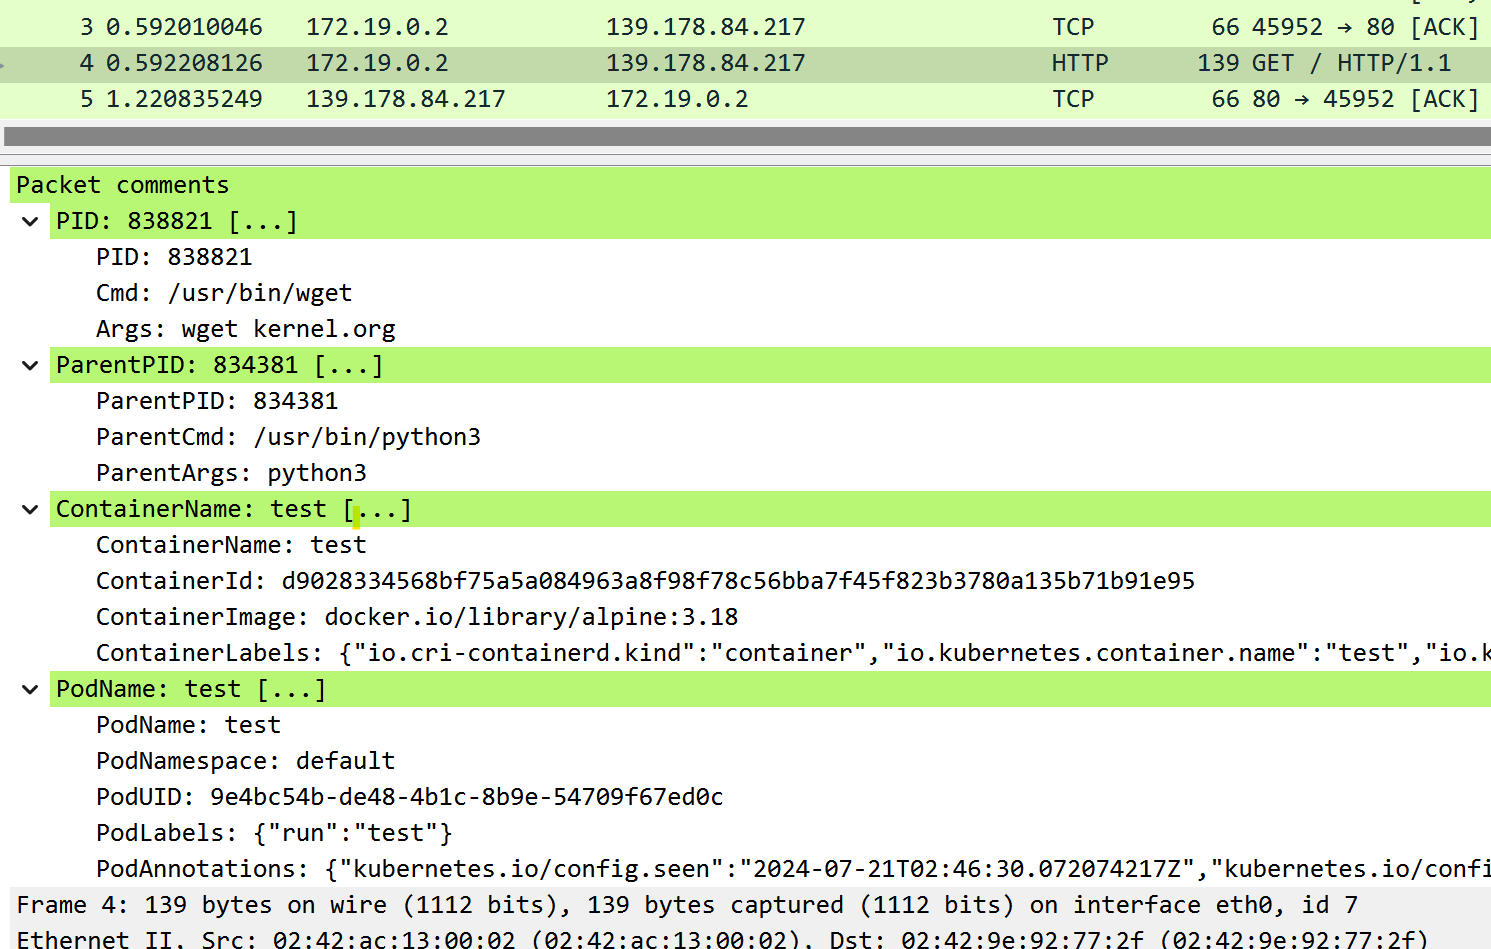 mozillazg/ptcpdump
eBPF-based packet analyzer that captures network traffic with automatic process, container, and Kubernetes pod metadata annotation, supporting…
 davidhavoc/ayaflow
A high-performance, eBPF-based network traffic analyzer written in Rust.
 mhaggis/package-inferno
A Public Package Scanner for The Community
 tenable/terrascan
Detect compliance and security violations across Infrastructure as Code to mitigate risk before provisioning cloud native infrastructure.
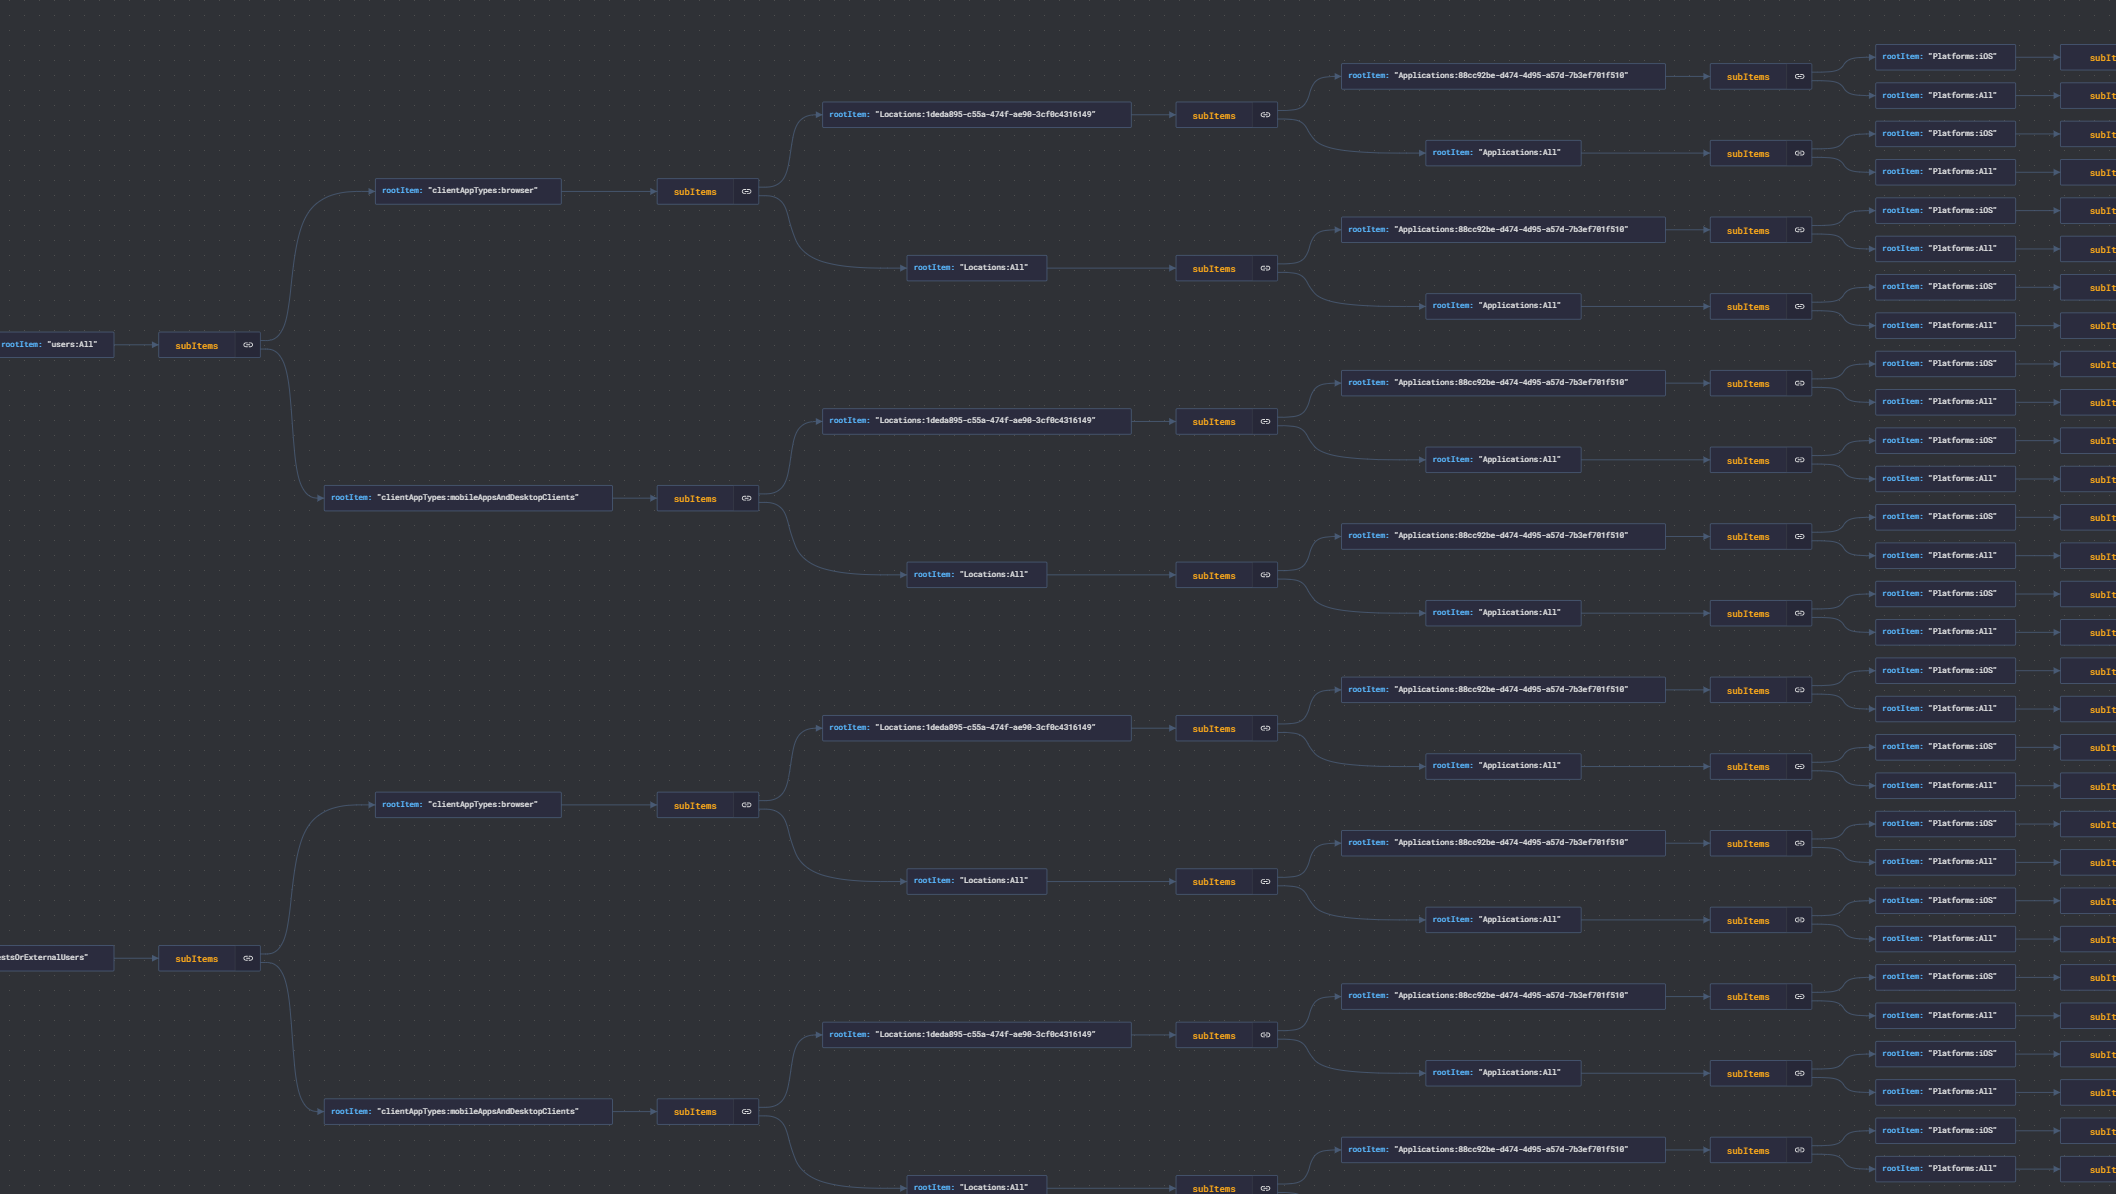 jsa2/caoptics
CA Optics - Azure AD Conditional Access Gap Analyzer
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638