My-Exploits
 m4xsec/my-exploits
Metasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
cloud-securitycontainer-securityeducation+7
1
m4xsec/my-exploitsMetasploit modules, Python PoCs and throwaway Docker labs for four platform CVEs: Keycloak (CVE-2026-18963), Apache NiFi (CVE-2026-39816), HashiCorp…
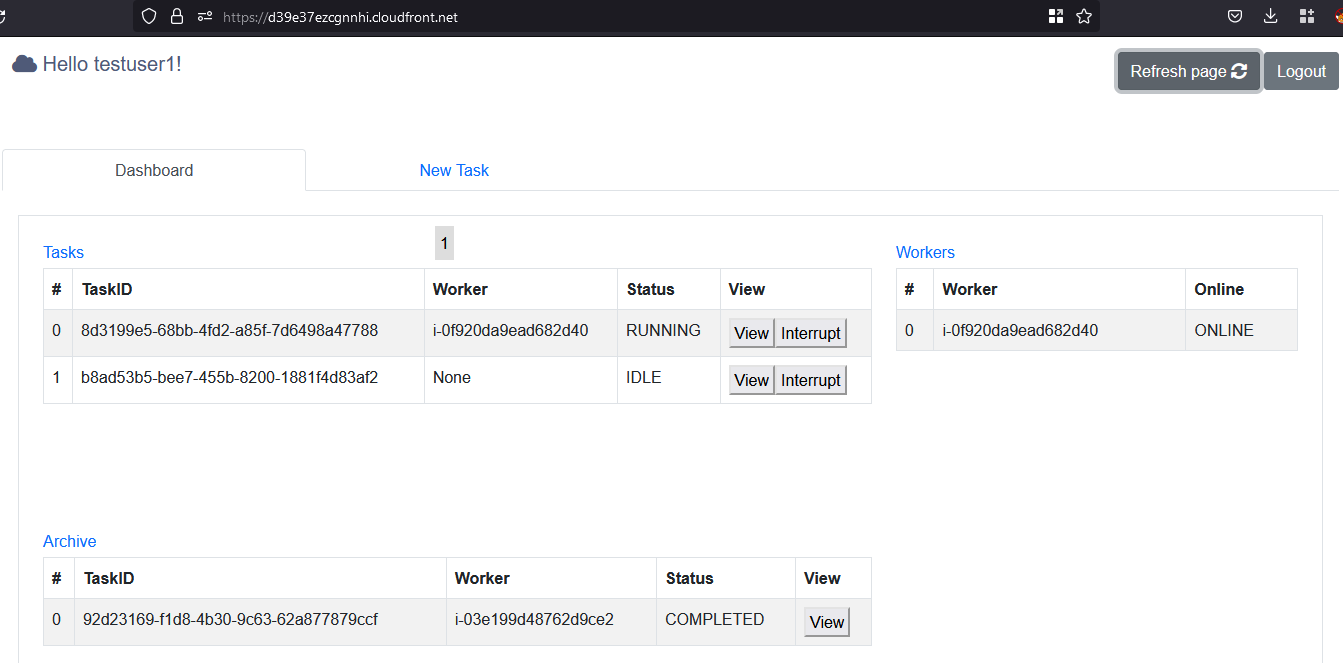 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 cgwalters/cve-2020-14386
Reproducer for Linux kernel memory corruption vulnerability CVE-2020-14386, deployed as a Kubernetes pod to test node vulnerability by triggering a…
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
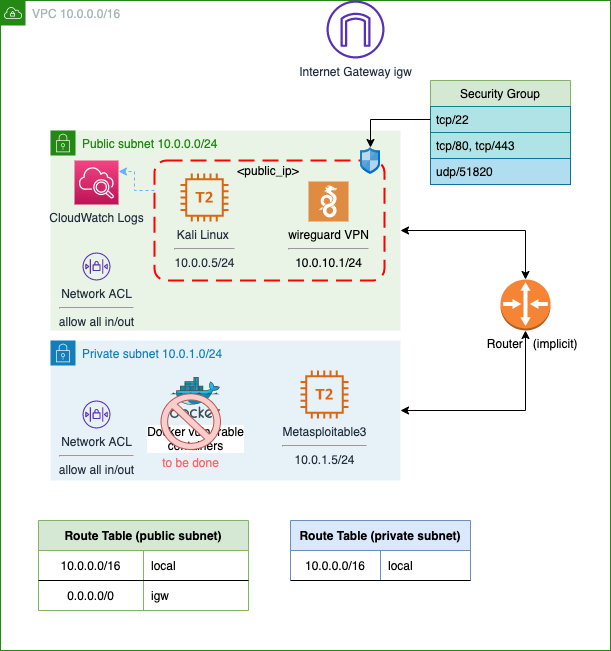 juanjosanz/aws-pentesting-lab
Pentesting lab with a Kali Linux instance accessible via ssh & wireguard VPN and with vulnerable instances in a private subnet
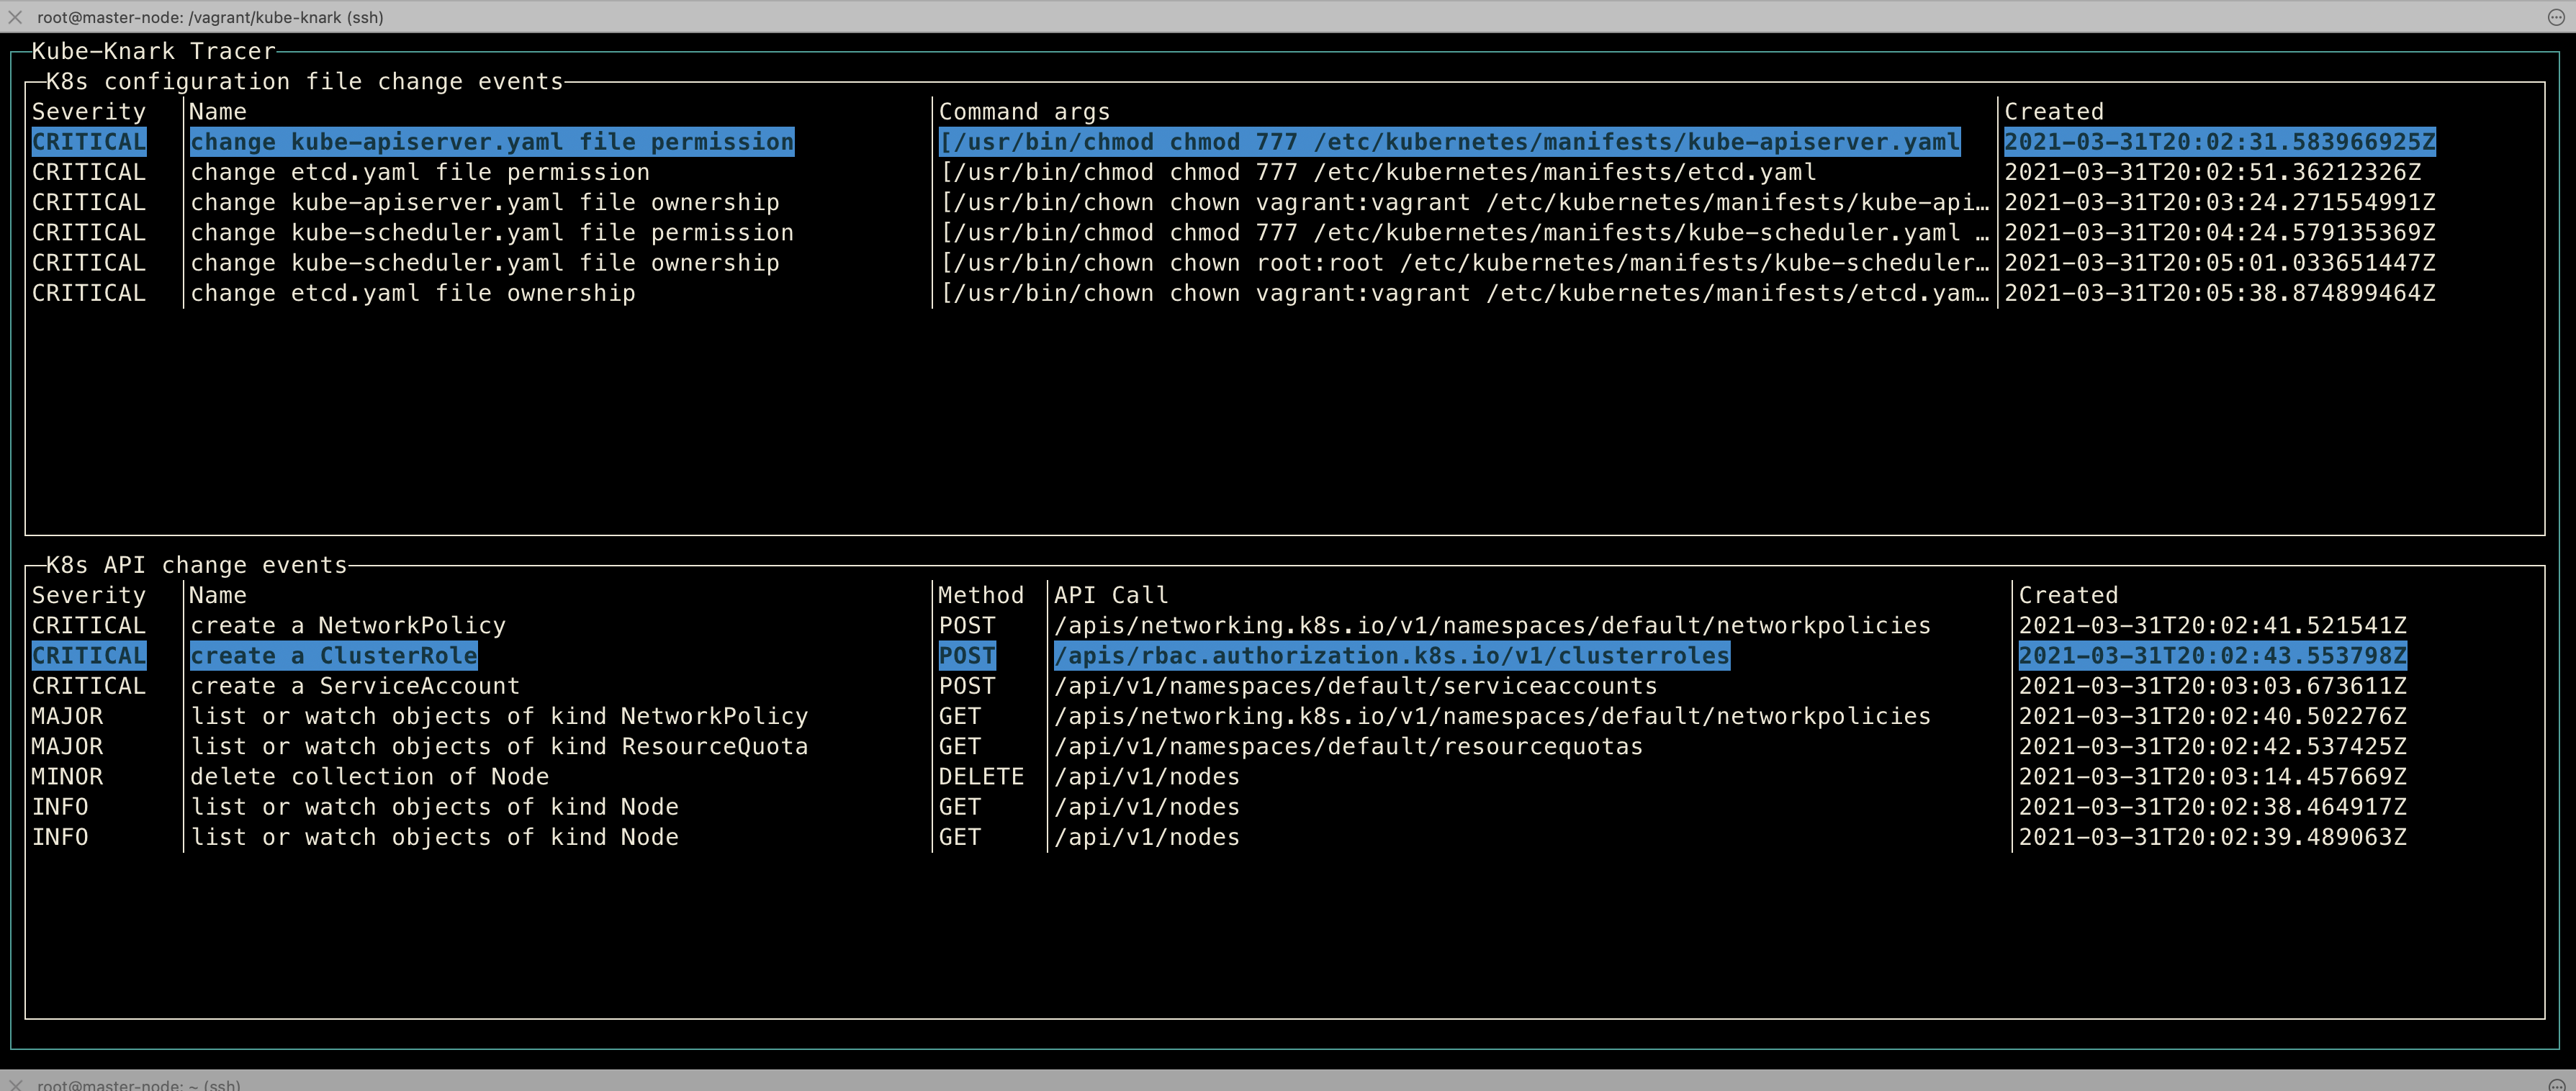 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 chen-keinan/kube-beacon
Open Source runtime scanner for k8s cluster and perform security audit checks based on CIS Kubernetes Benchmark specification
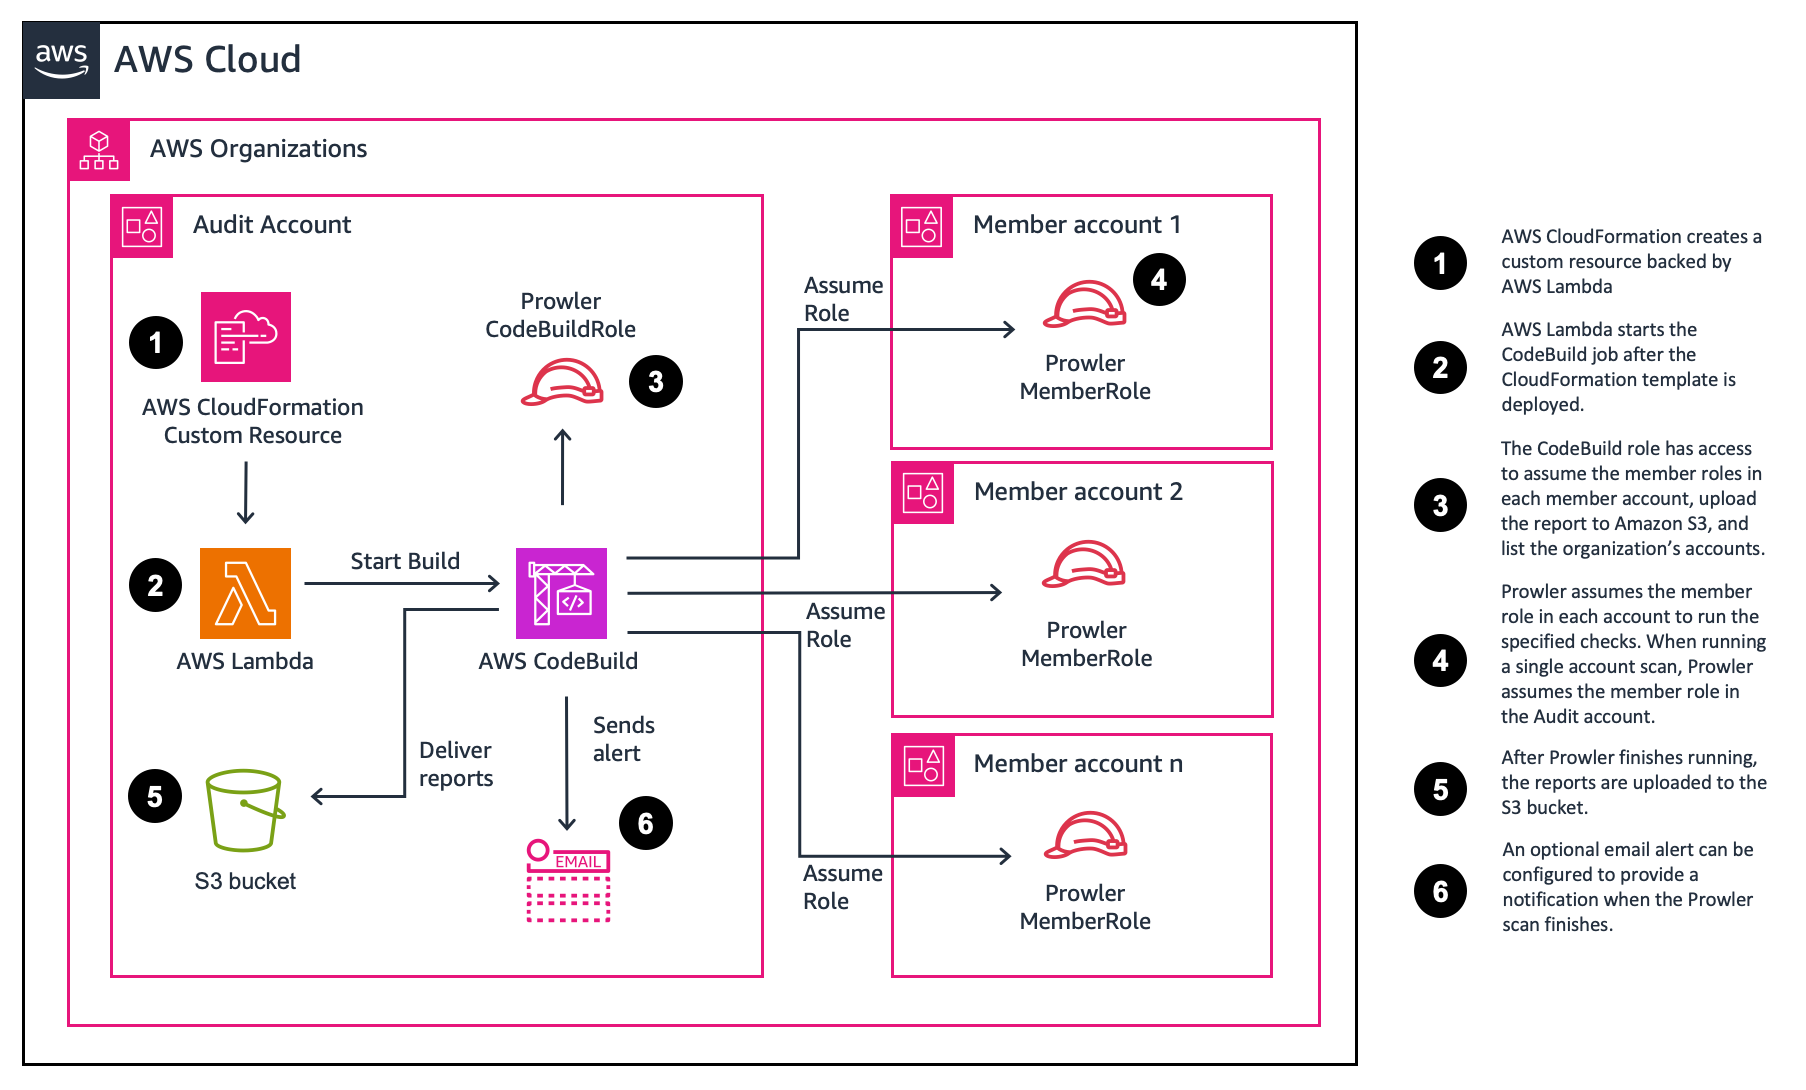 awslabs/aws-security-assessment-solution
An AWS tool to help you create a point in time assessment of your AWS account using Prowler.