TriSuElla-AIDLCA-Framework

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.

KQL injection in adx-mcp-server via table_name — CVE-2026-33980 / CVSS 8.3

Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

AI-first security scanner. NEW in v2026.7: Claude Code compromise detection — vet .claude/ hooks, permissions & skills before you clone — plus an…

[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github

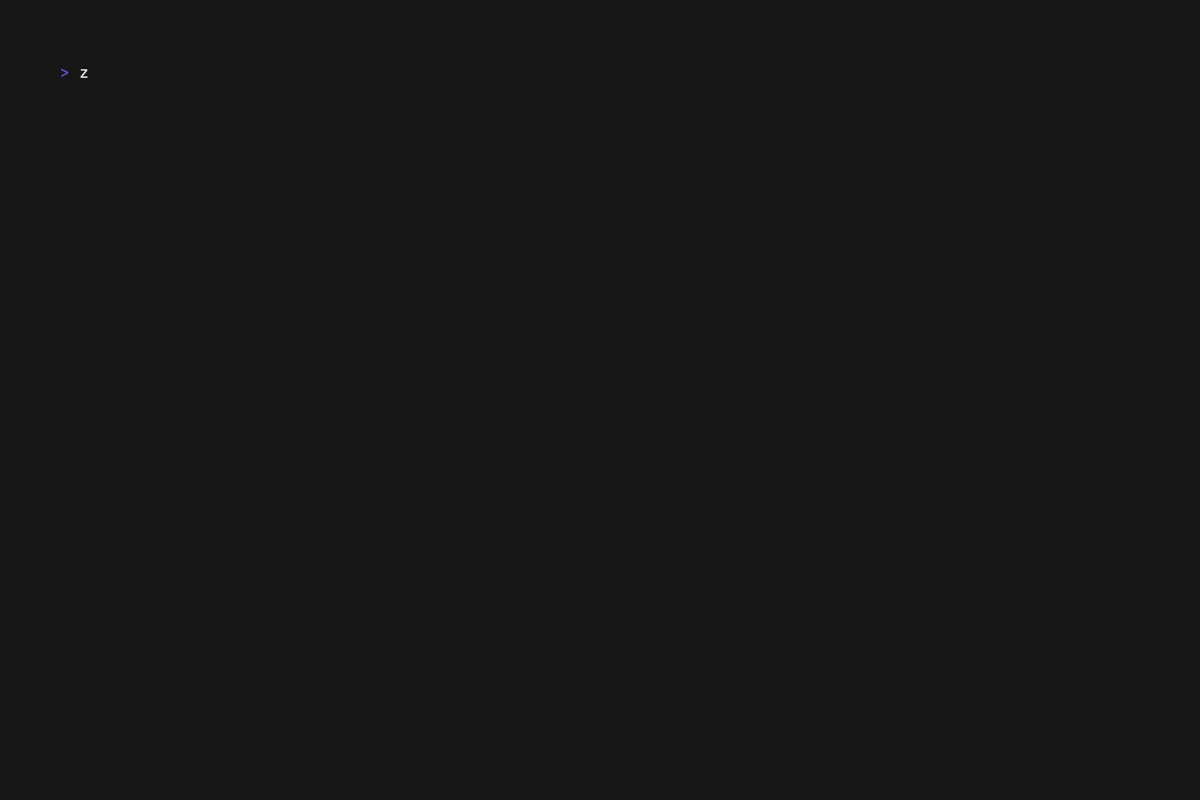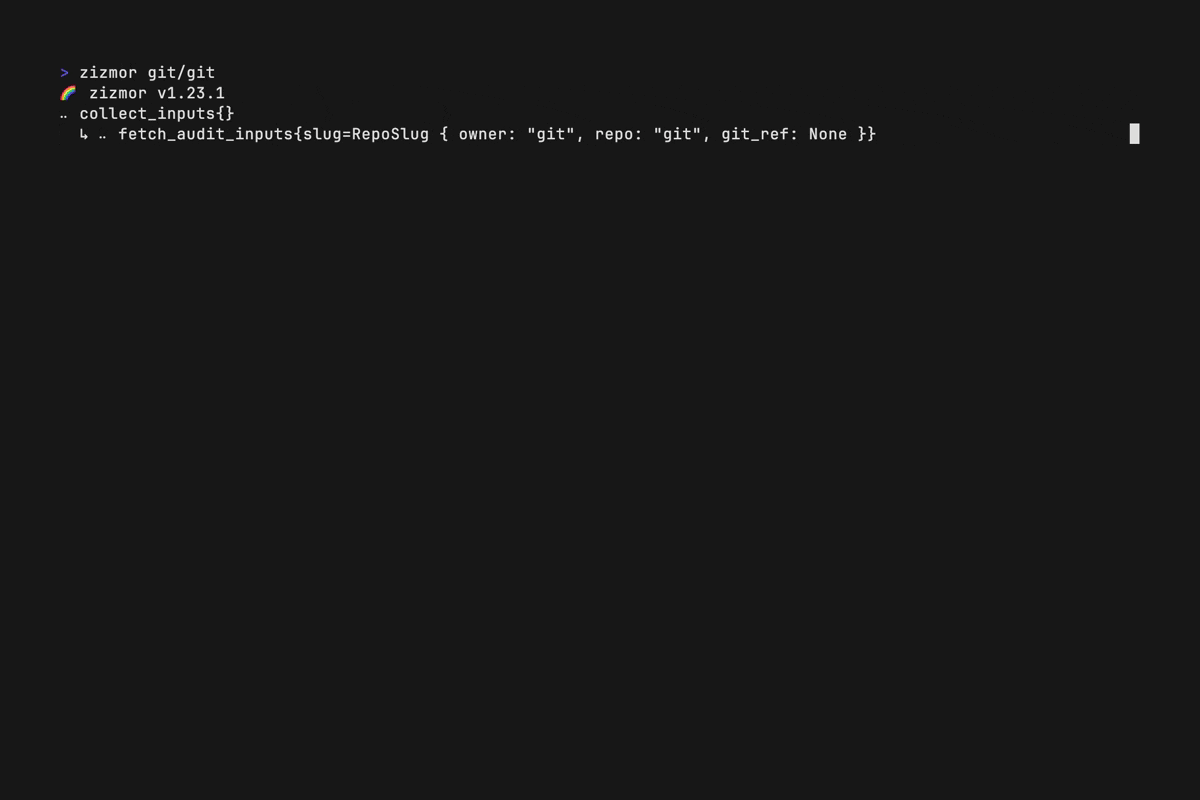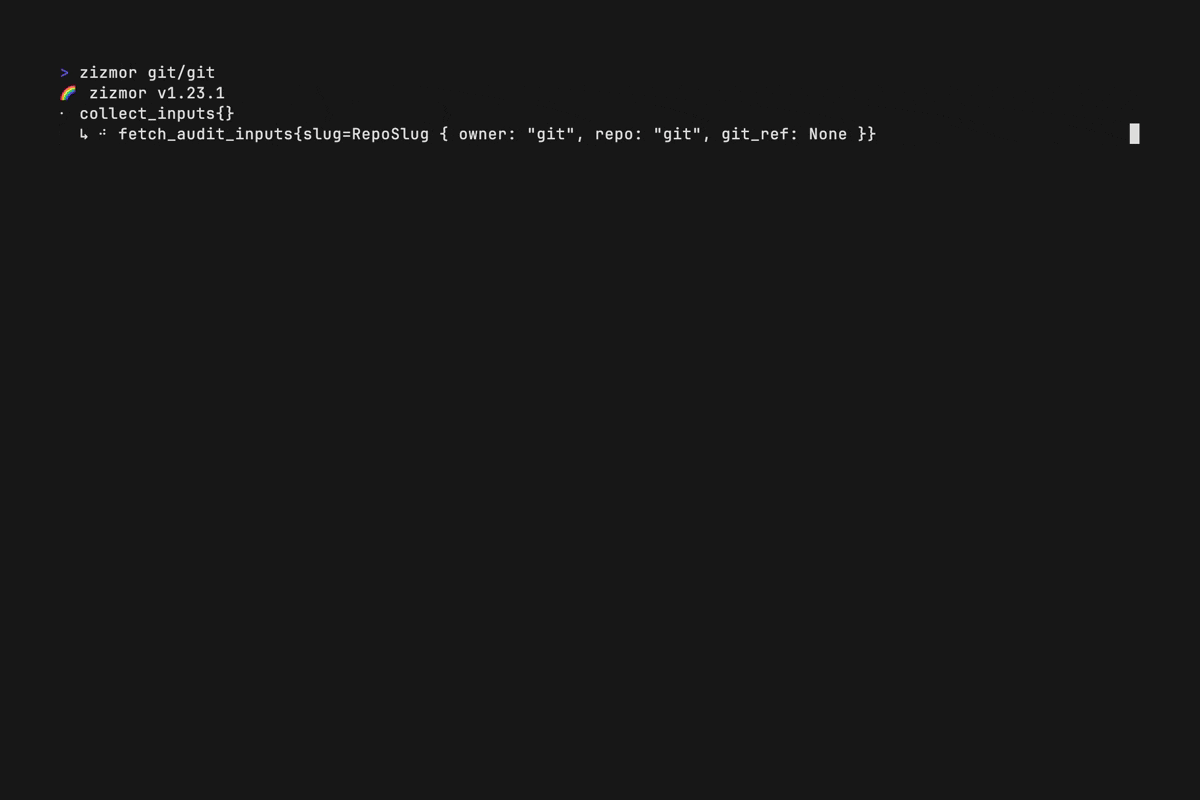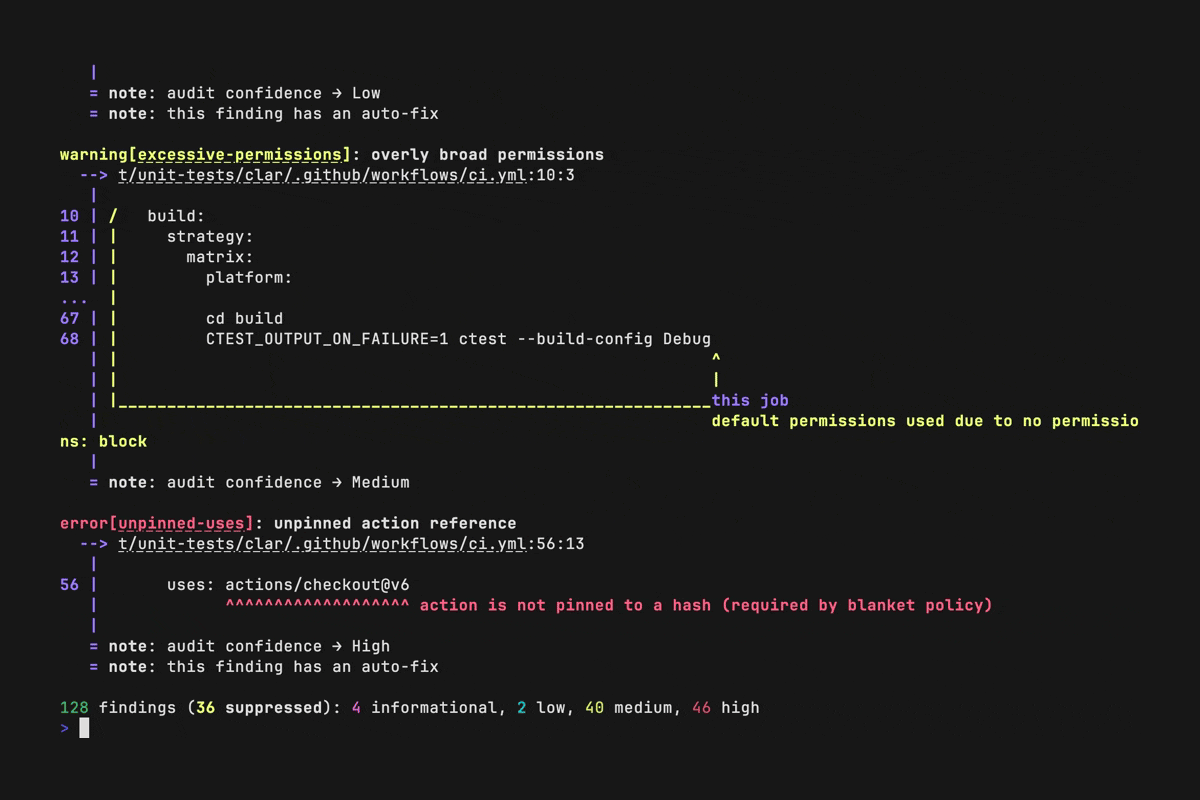
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…

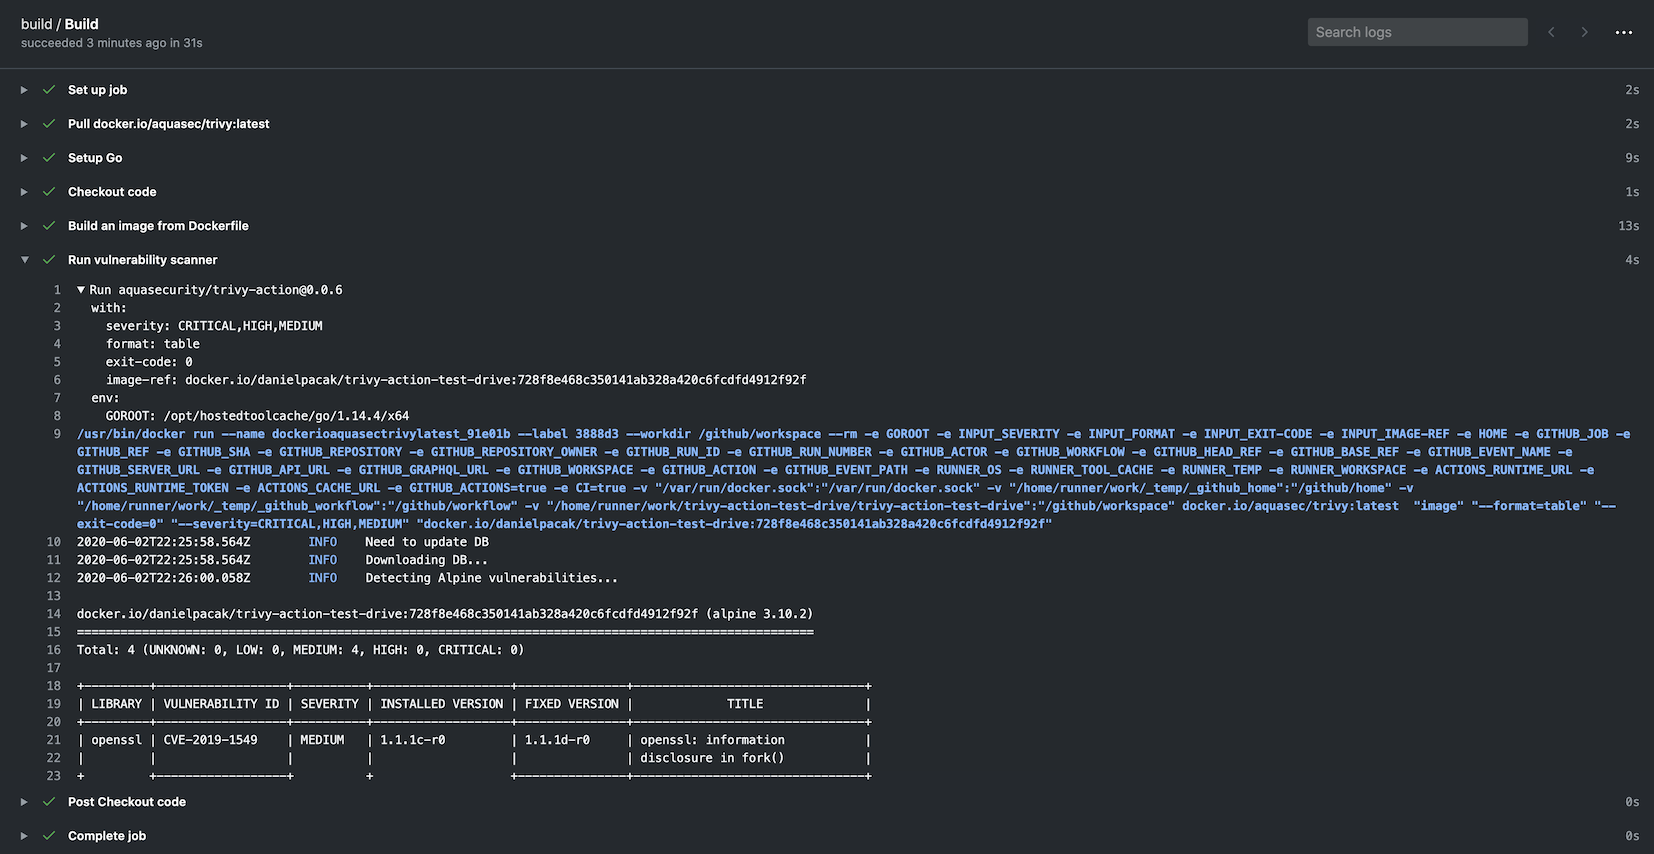
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities

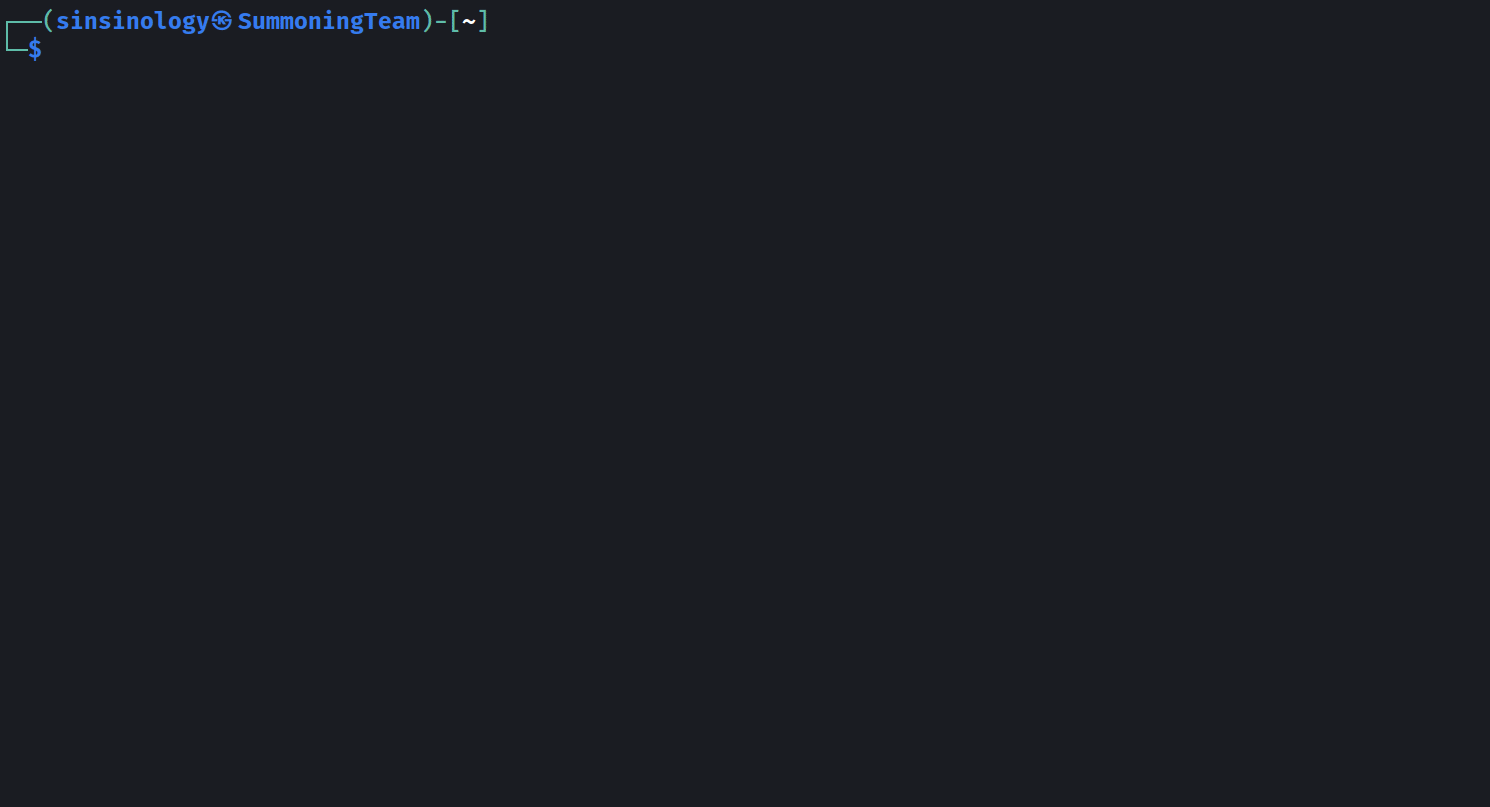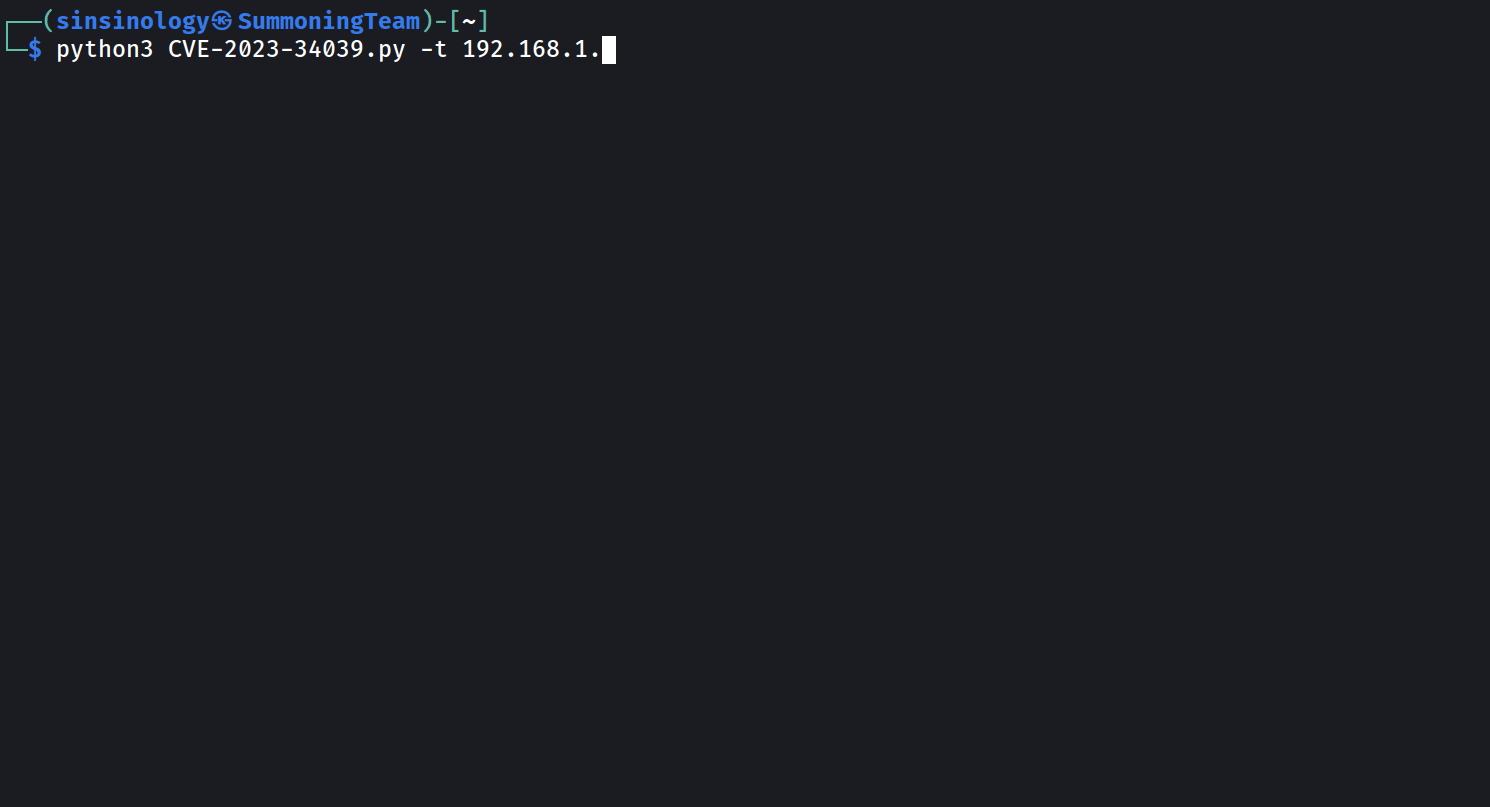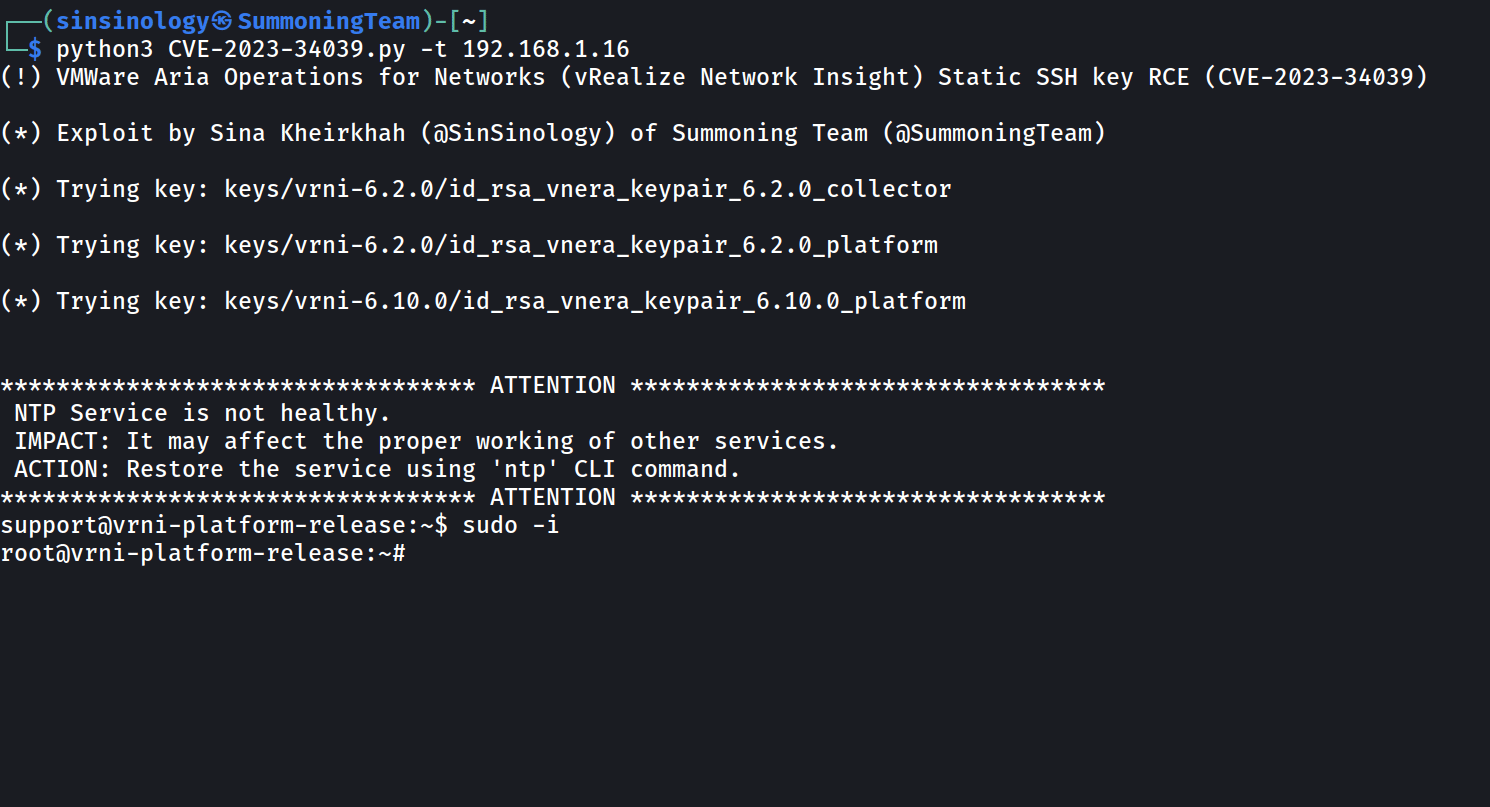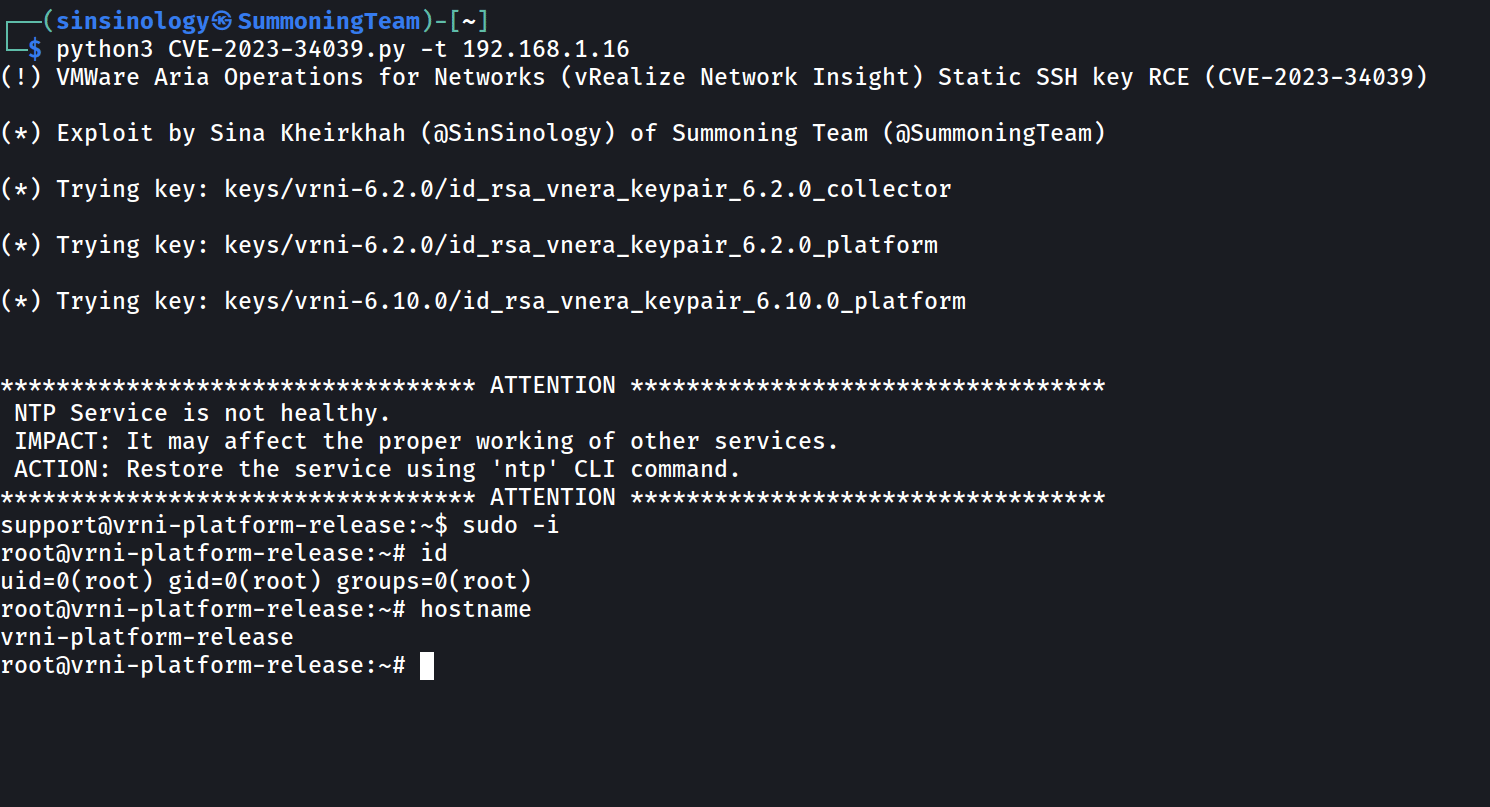
VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)

CVE-2023-34039

Reproducer for CVE-2026-43867 — Apache Camel camel-pqc AwsSecretsManagerKeyLifecycleManager unsafe key-metadata deserialization (RCE)

Technical writeup and Proof of Concept (PoC) for CVE-2026-11417: OS Command Injection / Remote Code Execution (RCE) in AWS CDK's NodejsFunction.

OWASP Secure Agent Playbook Project

Open-source secret scanner in Rust

Maven-based demonstration of CVE-2023-33246 mitigation for Apache RocketMQ, featuring attack testing and enhanced parameter validation to prevent…

Professional Service scripts to aid in the identification of affected Java applications in TeamServer