
CVE-2025-62506
 yoshino-s/cve-2025-62506
Verification script for CVE-2025-62506, a privilege escalation vulnerability in MinIO service accounts, testing if restricted accounts can bypass…
cloud-securityexploitationpenetration-testing+2
yoshino-s/cve-2025-62506Verification script for CVE-2025-62506, a privilege escalation vulnerability in MinIO service accounts, testing if restricted accounts can bypass…
 tellerops/teller
Cloud native secrets management for developers - never leave your command line for secrets.
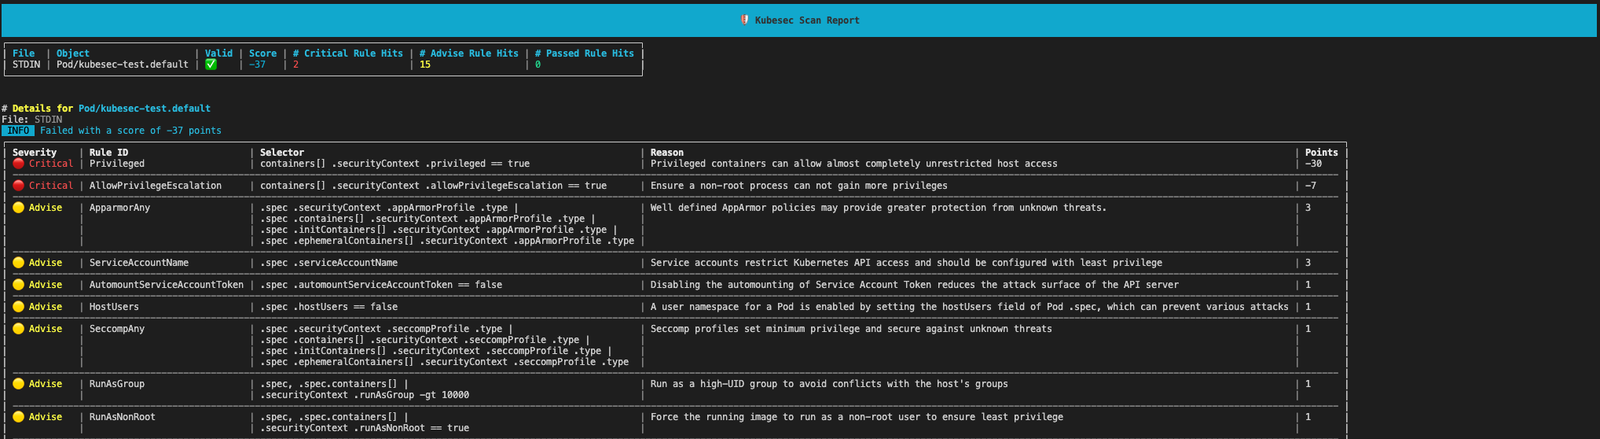 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 agentrust-io/cmcp
cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 synacktiv/gh-hijack-runner
A python script to create a fake GitHub runner and hijack pipeline jobs to leak CI/CD secrets.
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
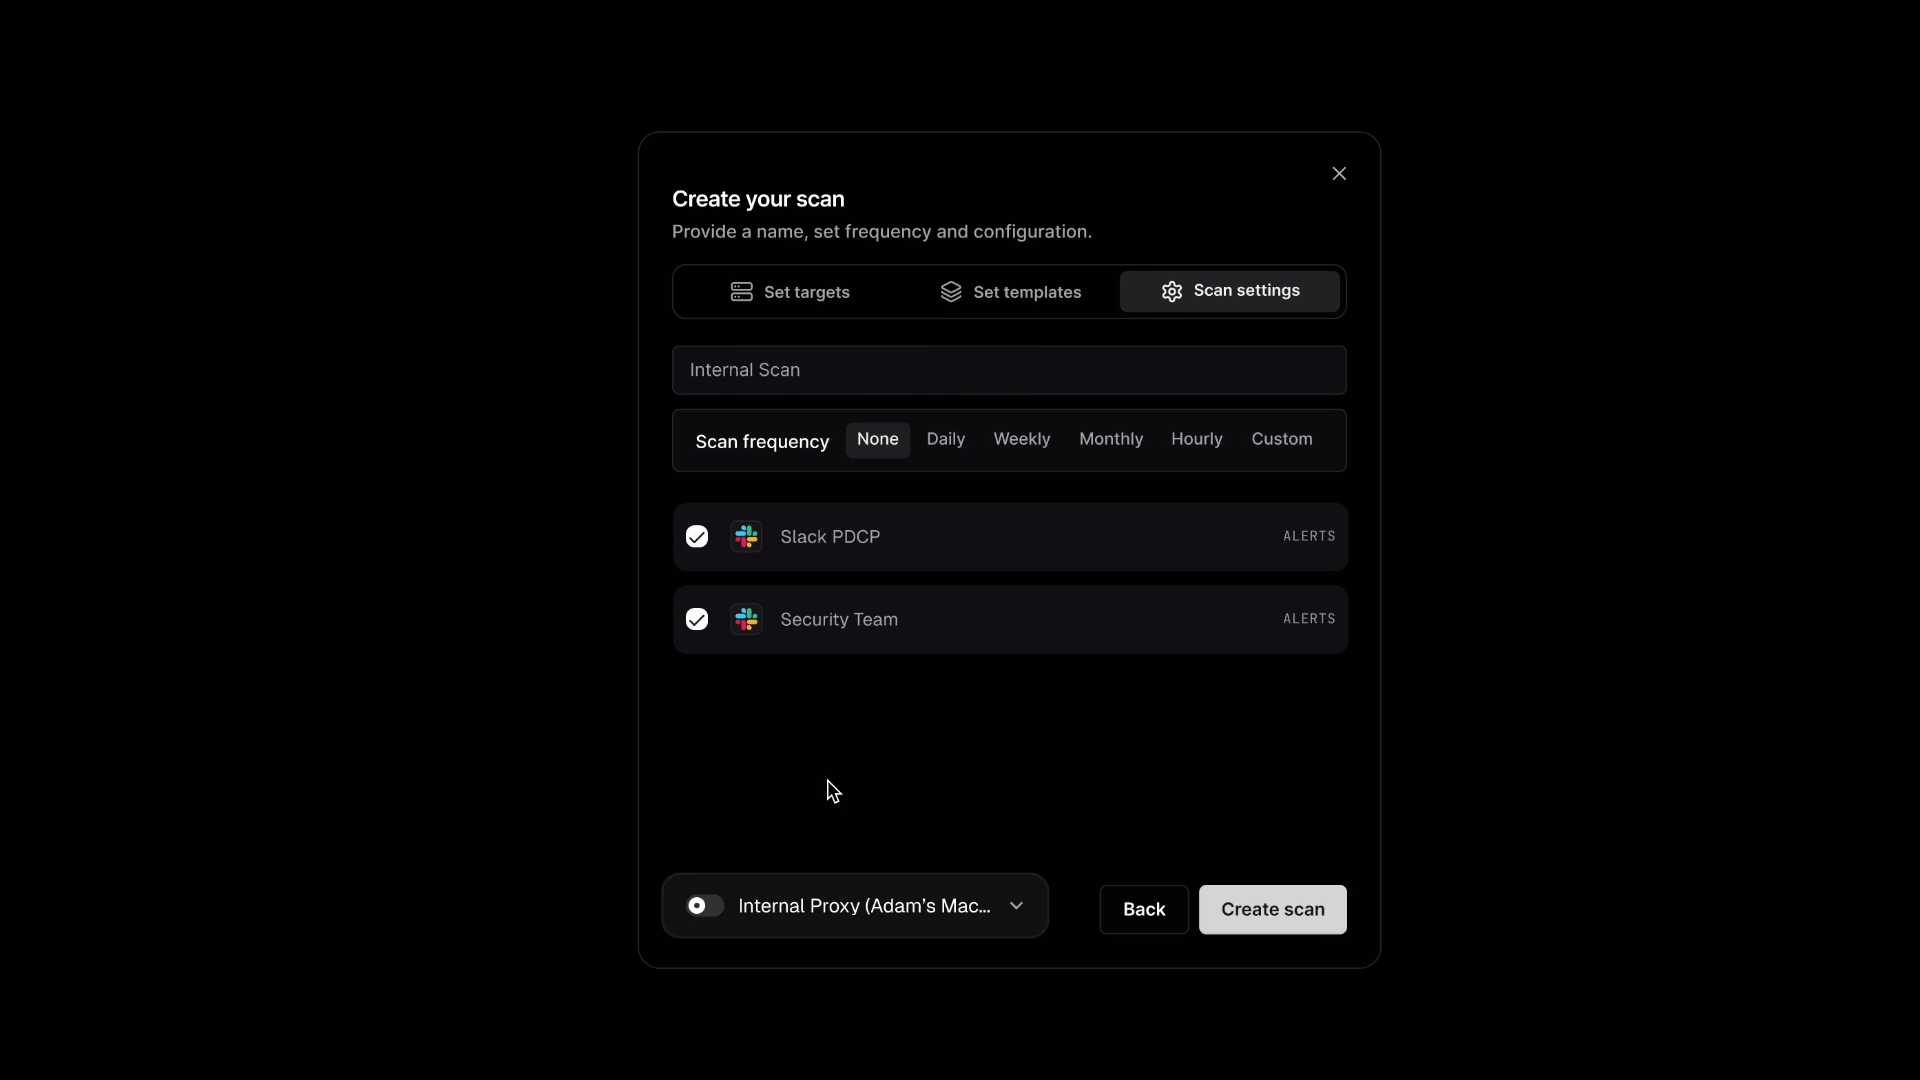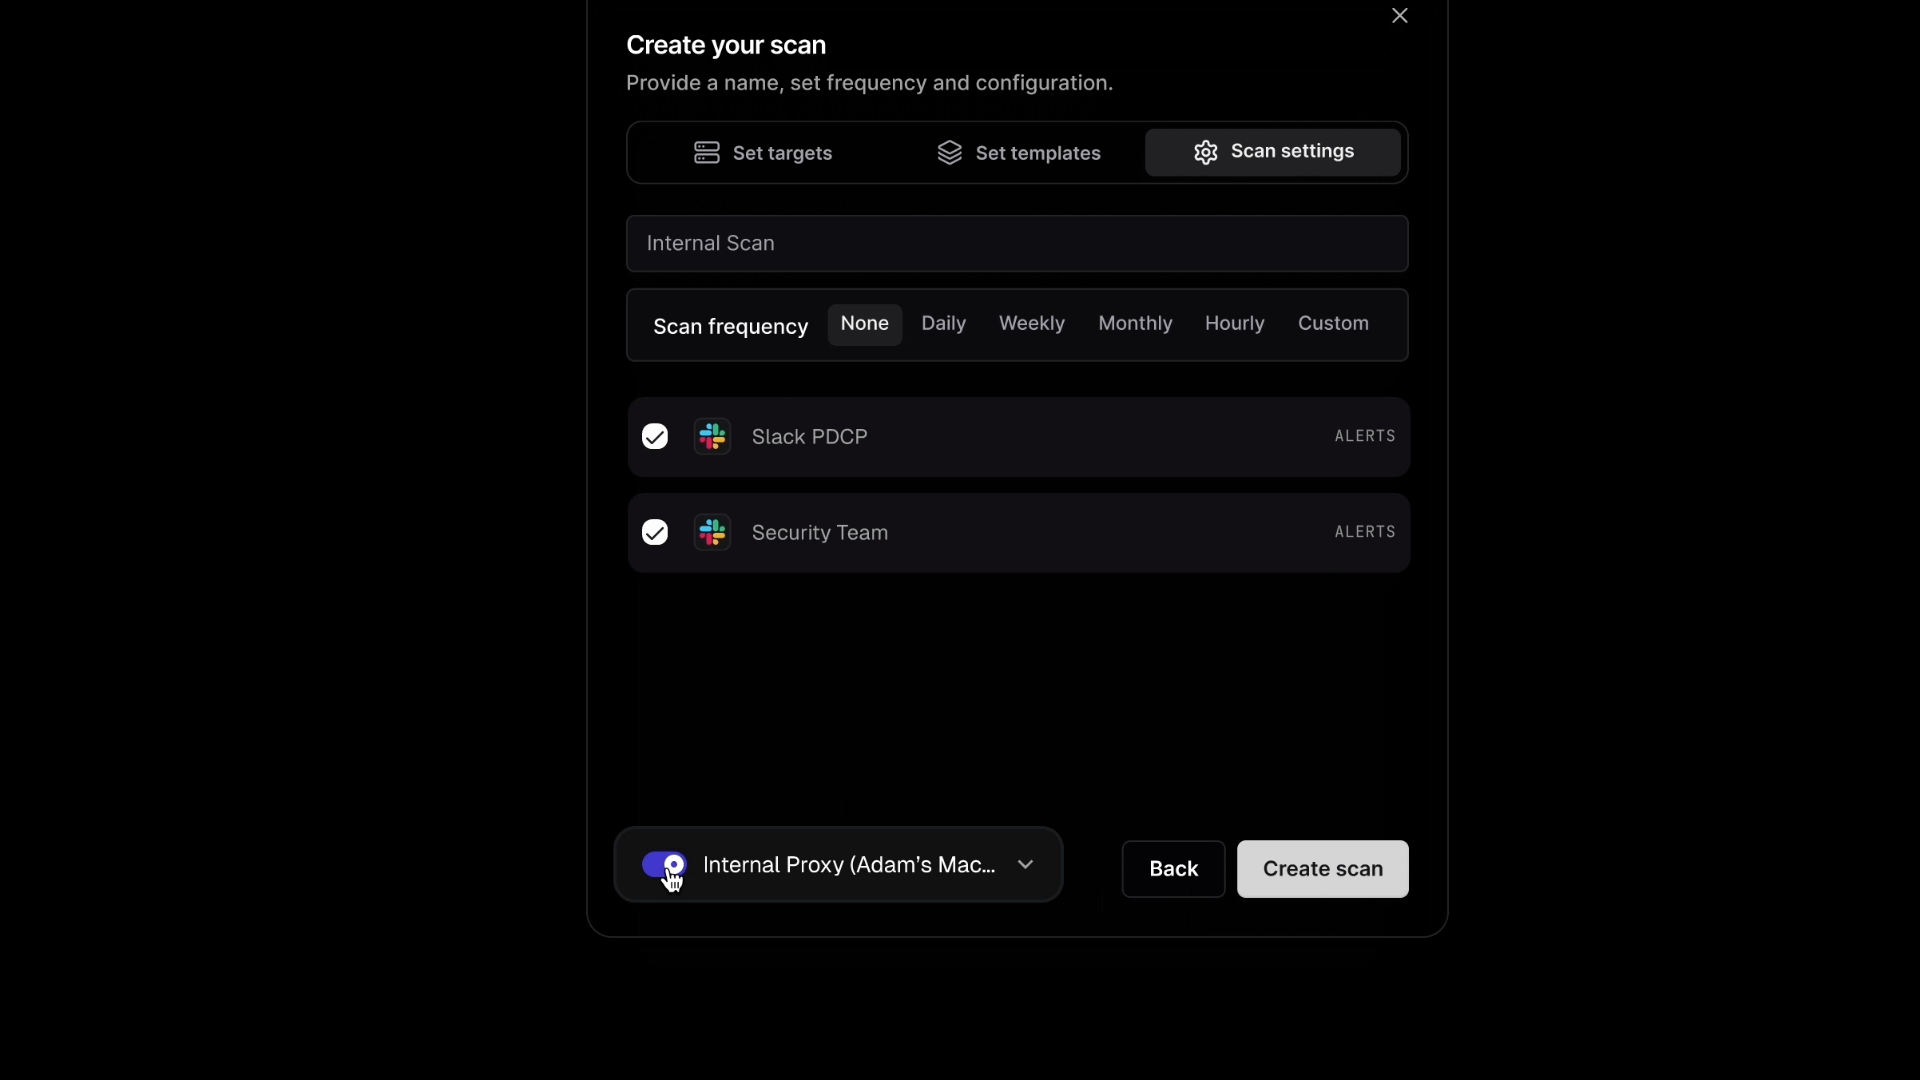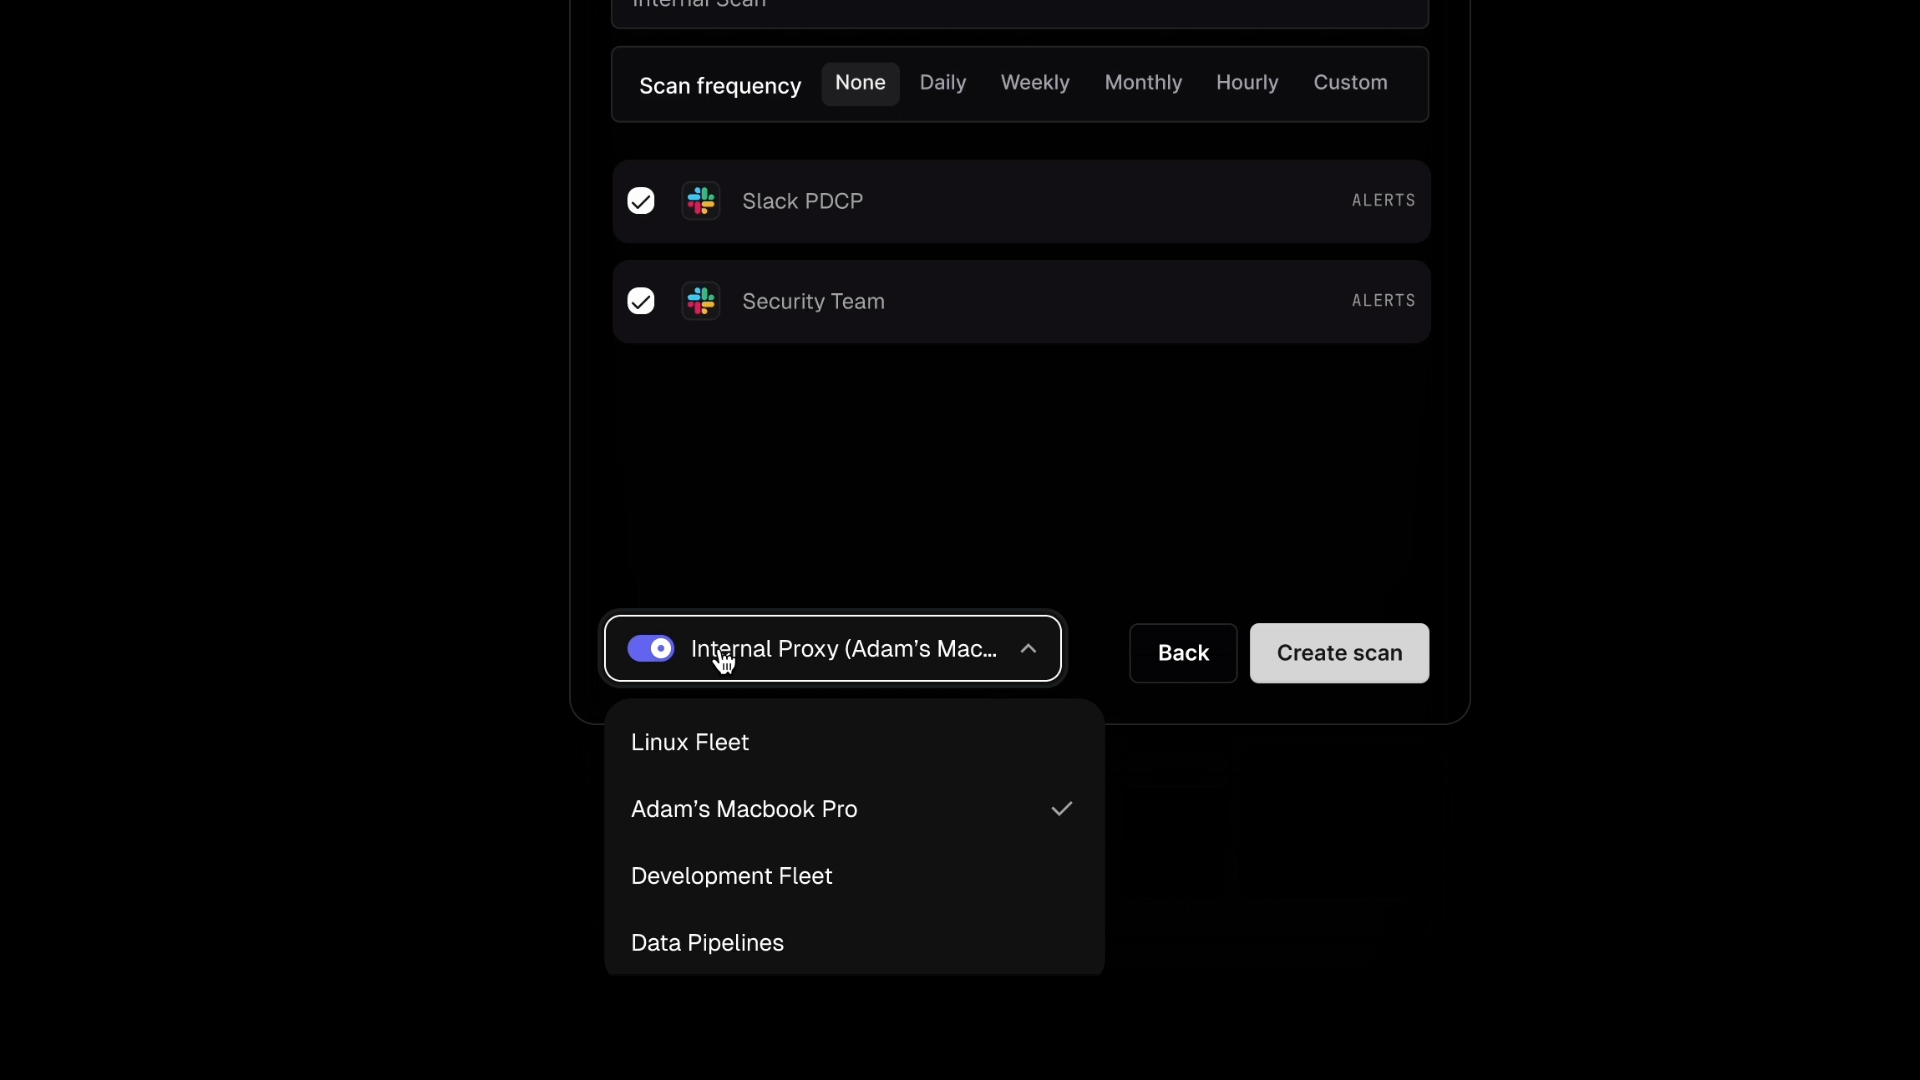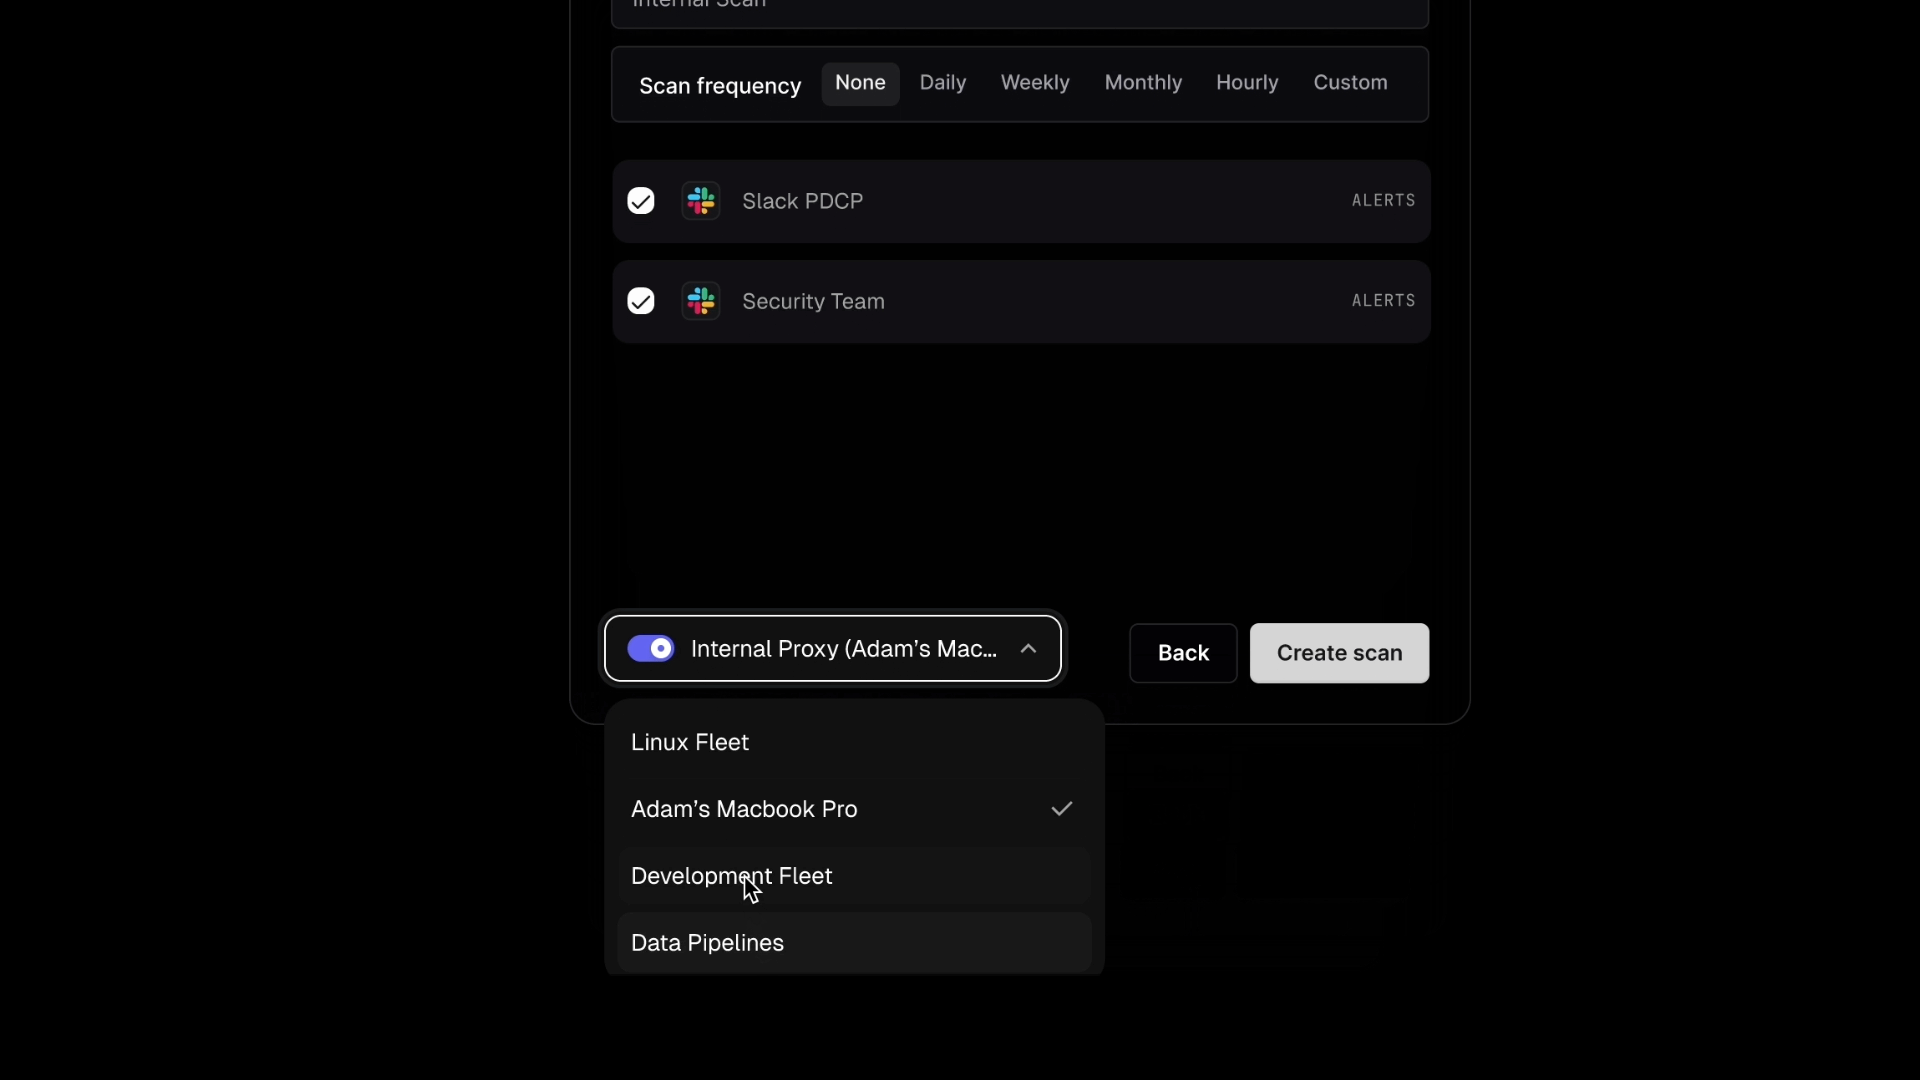 projectdiscovery/tunnelx
TunnelX is a lightweight ingress tunneling tool designed to create a secure SOCKS5 proxy server for routing network traffic.
 ianxtianxt/cve-2019-16097
Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
 dolby360/cve-2022-27518_poc
Proof-of-concept exploit for CVE-2022-27518 targeting Citrix ADC and Citrix CPX containers, demonstrating remote code execution via crafted HTTP…
 arbaaz29/cve-2022-3294
Privilege Escalation using nodes/proxy (create action allowed) and nodes/status (update/patch actions allowed)
 ariesq/gh-safe-repo
Python CLI that creates GitHub repos with safe defaults — branch protection, Dependabot, secret scanning, and pre-flight security scanning — applied…
 kontext-security/kontext-cli
Secure agents in seconds with permissions enforced at runtime.
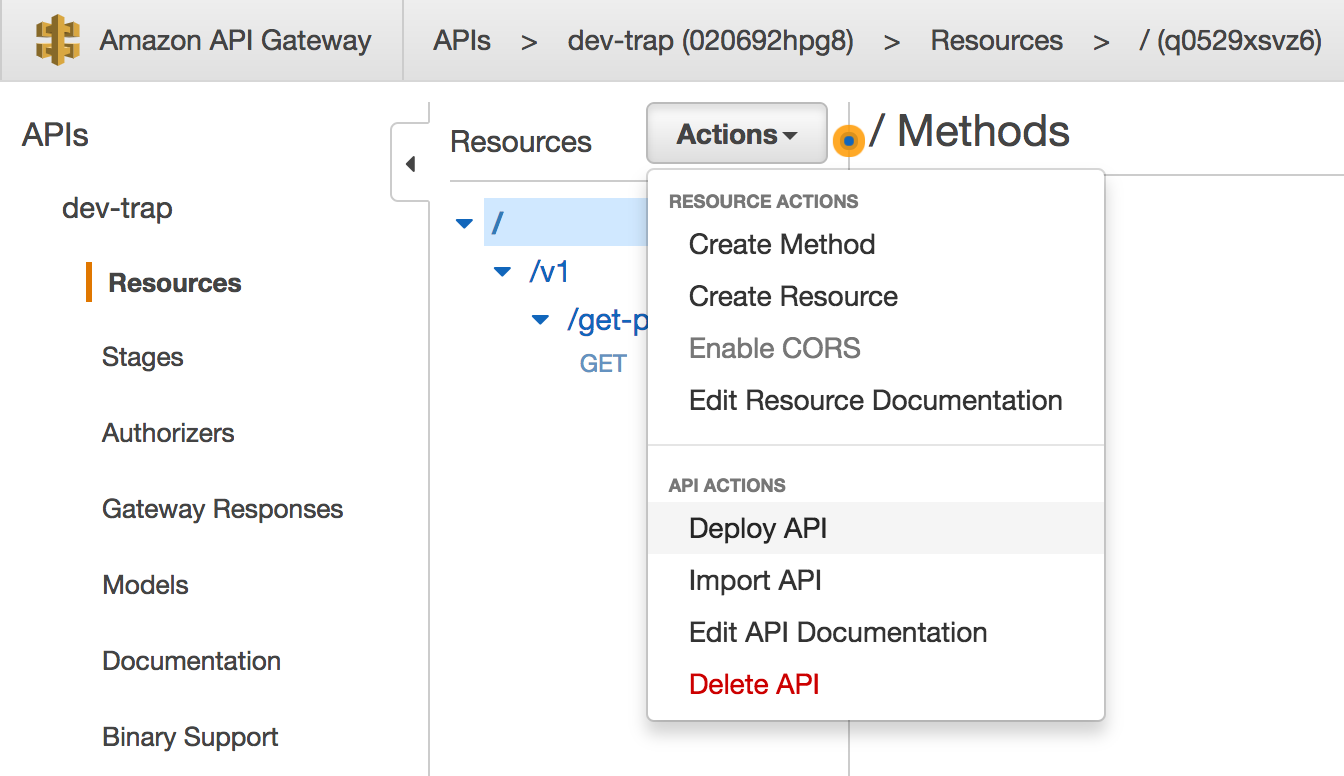 0x4d31/honeylambda
honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
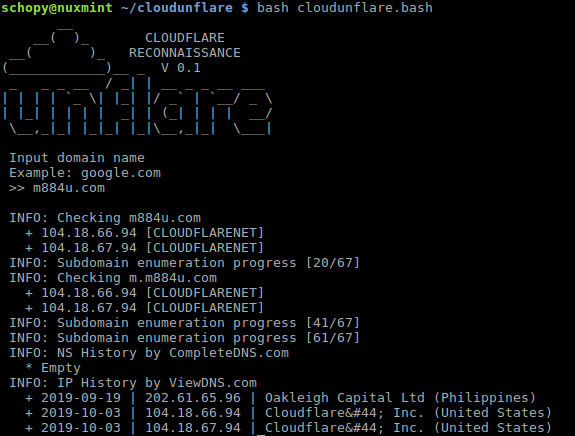 greycatz/cloudunflare
Reconnaissance Real IP address for Cloudflare Bypass
 splunk/attack_range
A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
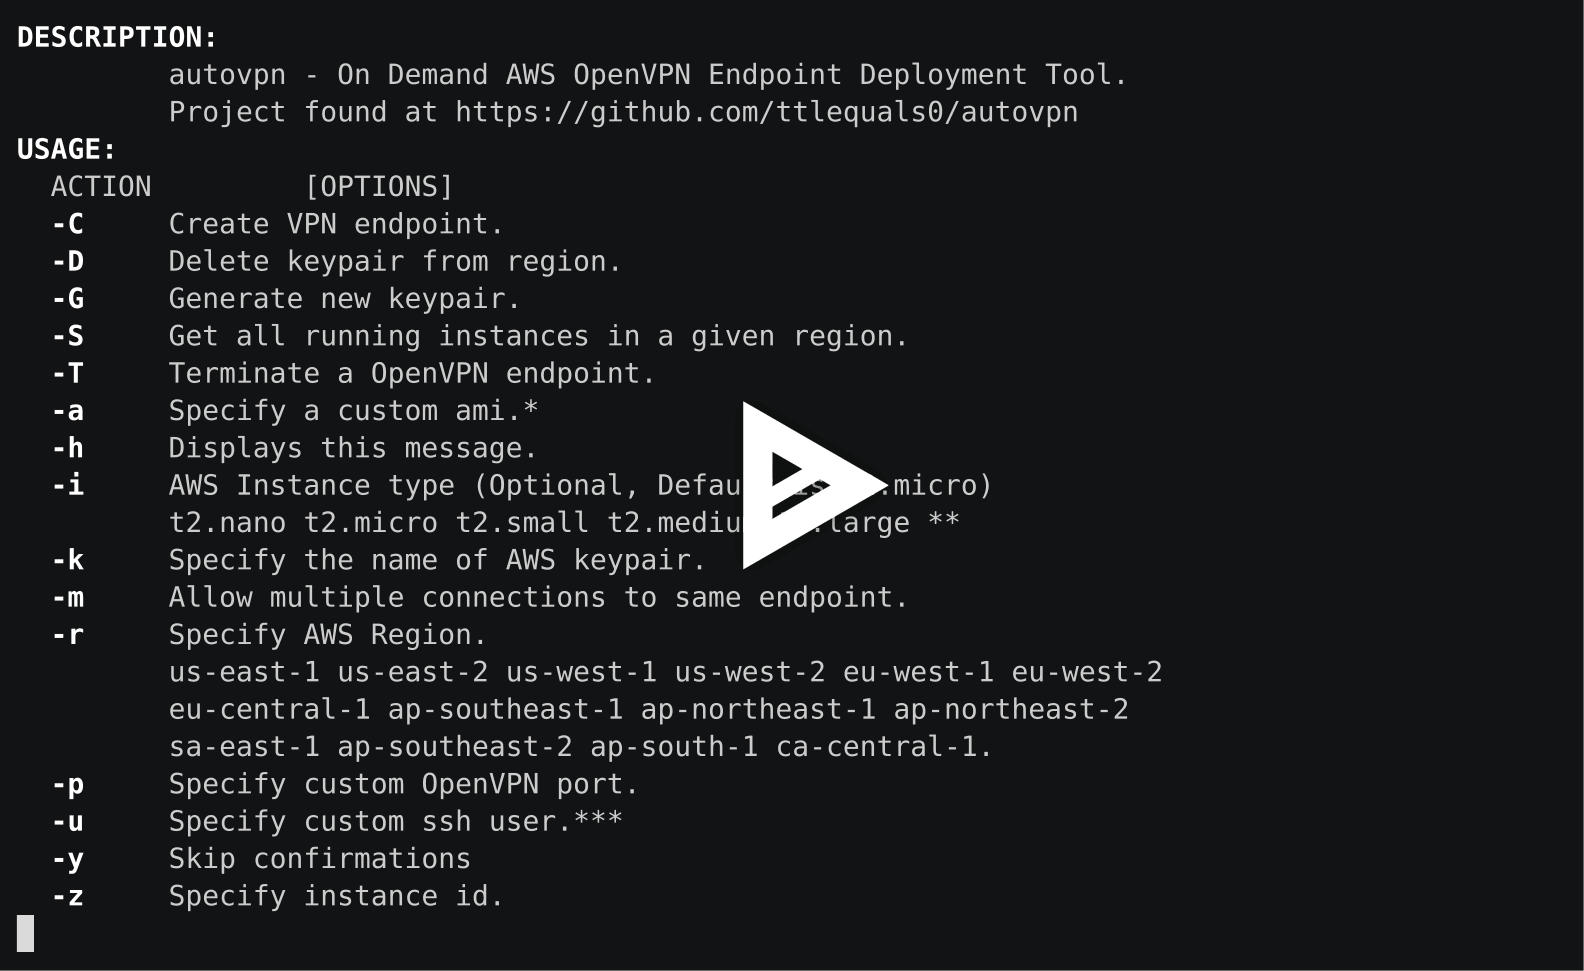 ttlequals0/autovpn
Create On Demand Disposable OpenVPN Endpoints on AWS.