

ARES
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
cloud-securitycommand-and-controldefensive-tools+5
633
mafifrizi/aresAutonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 masahiro331/kube-trivy
Trivy for Kubernetes
 ascit31/dark-moon
Autonomous AI pentesting engine, continuous offensive security across web, cloud, AD & Kubernetes. Agentic reasoning + real exploit execution deliver…
 pensarai/apex
AI-powered offensive security testing using autonomous agents, directly in your terminal.
 owasp/owasp-cstg
Vendor-neutral cloud security testing guide with structured phases for enumeration, privilege escalation, lateral movement, and post-exploitation…
 paolokappa/sharepointsecuritymonitor
A comprehensive PowerShell-based SharePoint security monitoring solution with CVE-2025-53770 protection, advanced DLL analysis, threat detection, and…
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 taroballzchen/cve-2023-28432-metasploit-scanner
MinIO Information Disclosure Vulnerability scanner by metasploit
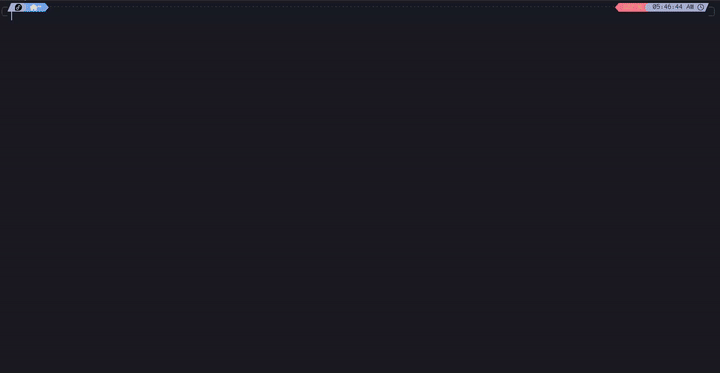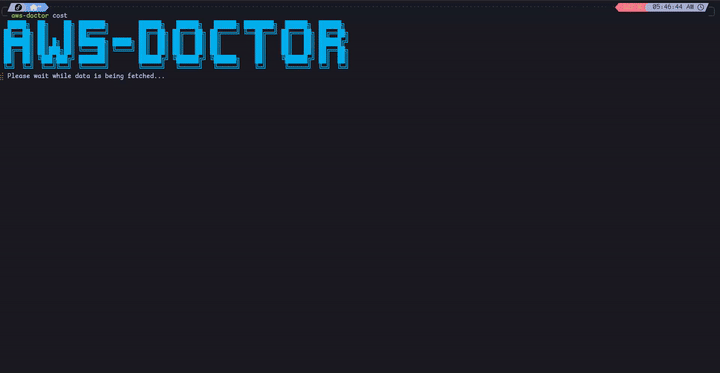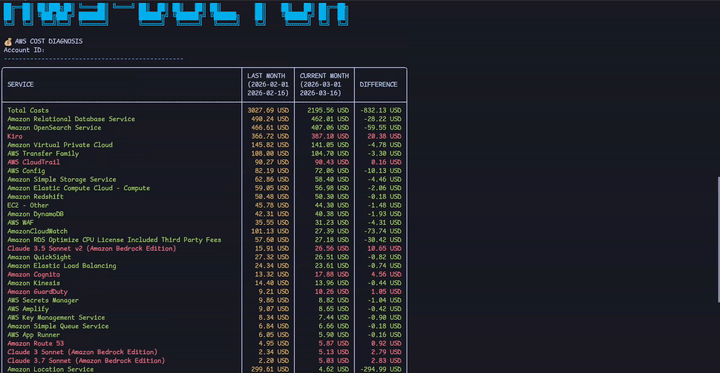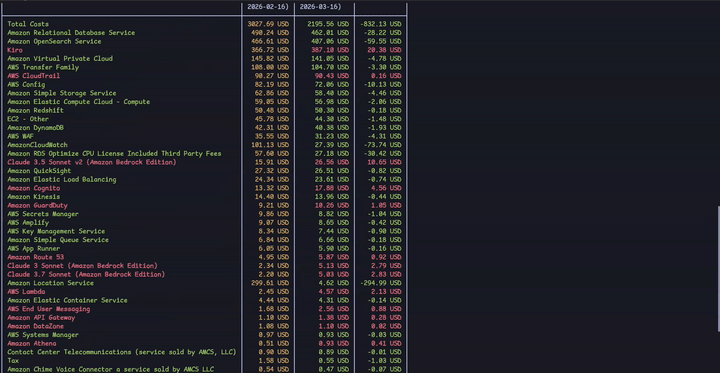 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 logisek/huntcyberark
CyberArk Security Audit
 awslabs/threat-modeling-mcp-server
MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…
 certologists/modified-cve-2024-37081-poc
Proof of concept for VMware vCenter CVE-2024-37081, modified to enhance usability for security testing and validation of the vulnerability.
 selinuxproject/selinux-notebook
Comprehensive open-source book on SELinux covering kernel components, userspace libraries, policy toolchain, and policy language. Includes build…
 resiprocate/resiprocate
C++ implementation of SIP, ICE, TURN and related protocols.
 cr0hn/dockerscan
The Most Comprehensive Docker Security Scanner
 redsiege/graphstrike
Cobalt Strike HTTPS beaconing over Microsoft Graph API
 gl4ssesbo1/nebula
Nebula is a cloud C2 Framework, which at the moment offers reconnaissance, enumeration, exploitation, post exploitation on AWS, but still working to…