
CVE-2026-21994
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
authenticationcloud-securityexploitation+3
g0w6y/cve-2026-21994Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…

 zpxlz/cve-2024-21626-poc
Proof-of-concept exploit for CVE-2024-21626, a container escape vulnerability in runc/Docker using file descriptor manipulation. For educational and…
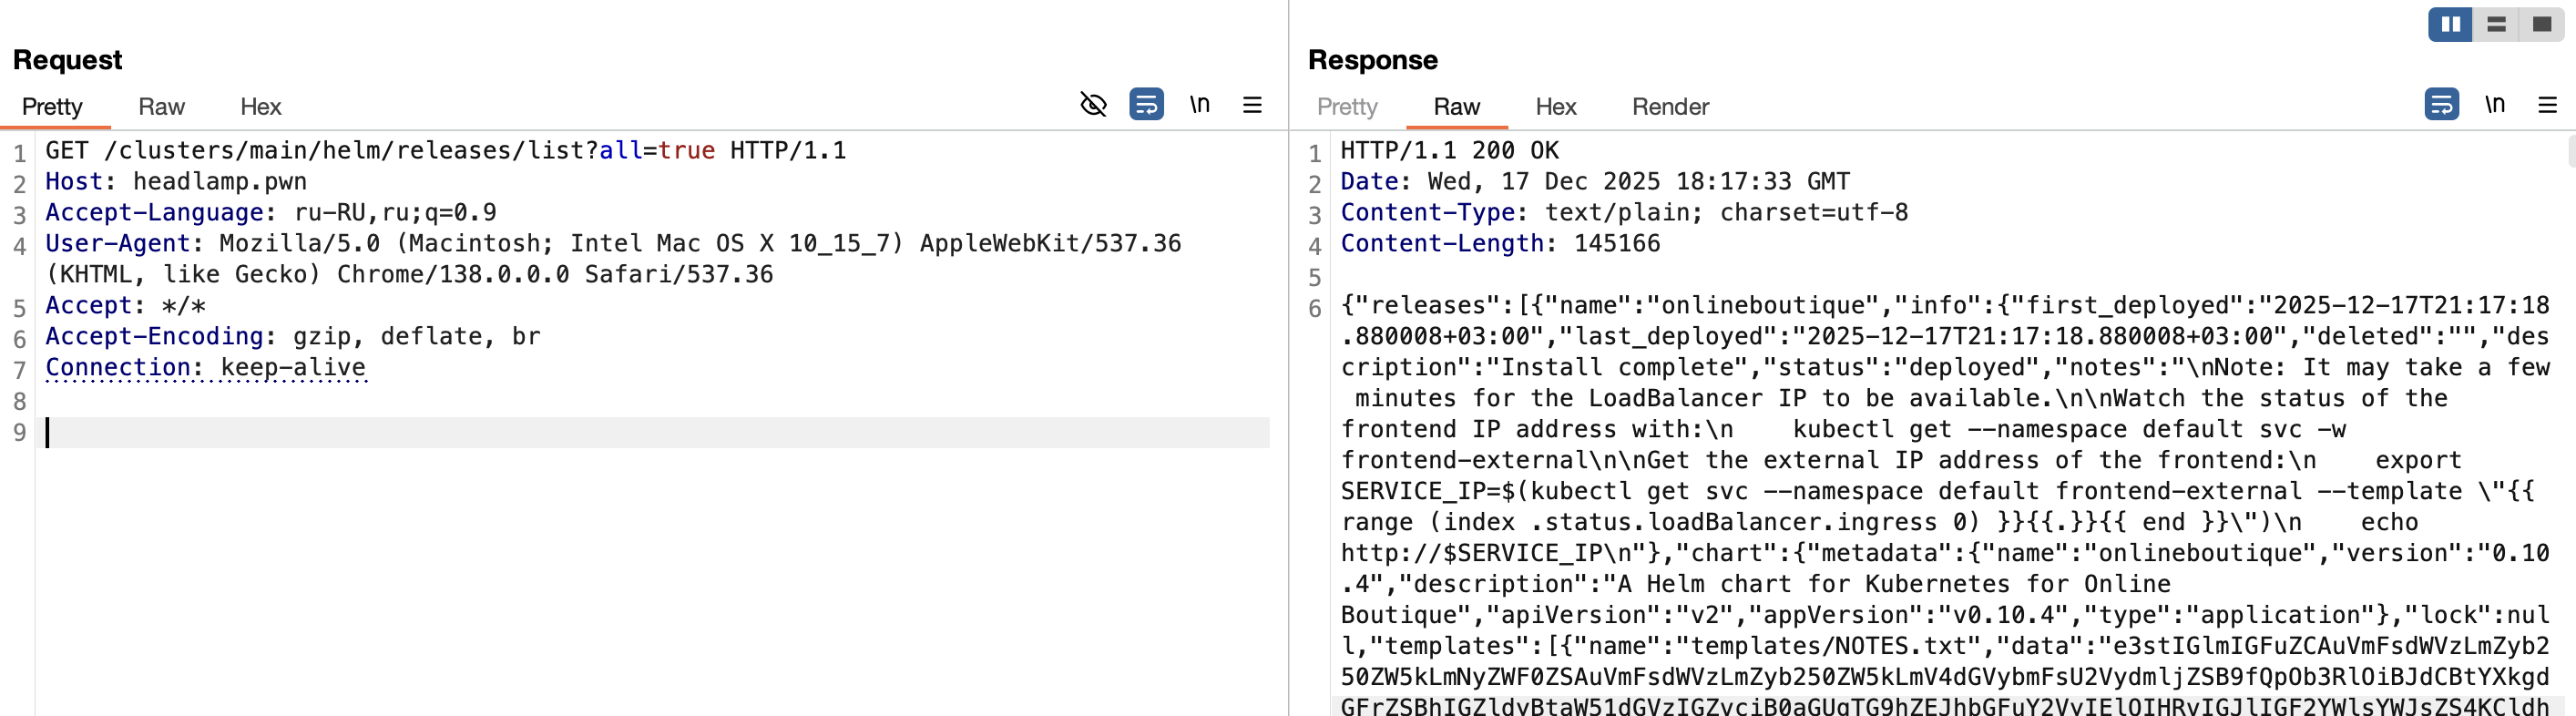 r0binak/cve-2025-14269
CVE-2025-14269 PoC exploit
 mightysai1997/cve-2024-3094
Shell scripts to detect CVE-2024-3094 backdoor in liblzma5 across Kubernetes pods and Docker containers, with SBOM generation via Trivy for…
 teyhouse/cve-2024-3094
K8S and Docker Vulnerability Check for CVE-2024-3094
 maxwitat/check-aad-connect-for-cve-2021-36949-vulnerability
check if Azure AD Connect is affected by the vulnerability described in CVE-2021-36949
 brinhosa/cve-2024-3094-one-liner
One-liner scripts to check server and Docker image vulnerability to CVE-2024-3094, including version detection and repository scanning for xz…
 almogopp/openssh-cve-2024-6387-fix
A Bash script to mitigate the CVE-2024-6387 vulnerability in OpenSSH by providing an option to upgrade to a secure version or apply a temporary…
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 heroku/heroku-cve-2013-0156
Inspect all of your heroku apps to see if they are running a vulnerable version of Rails