

checkov
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
cloud-infrastructure-securitycloud-securitycode-analysis+12
9.1k
bridgecrewio/checkovStatic analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
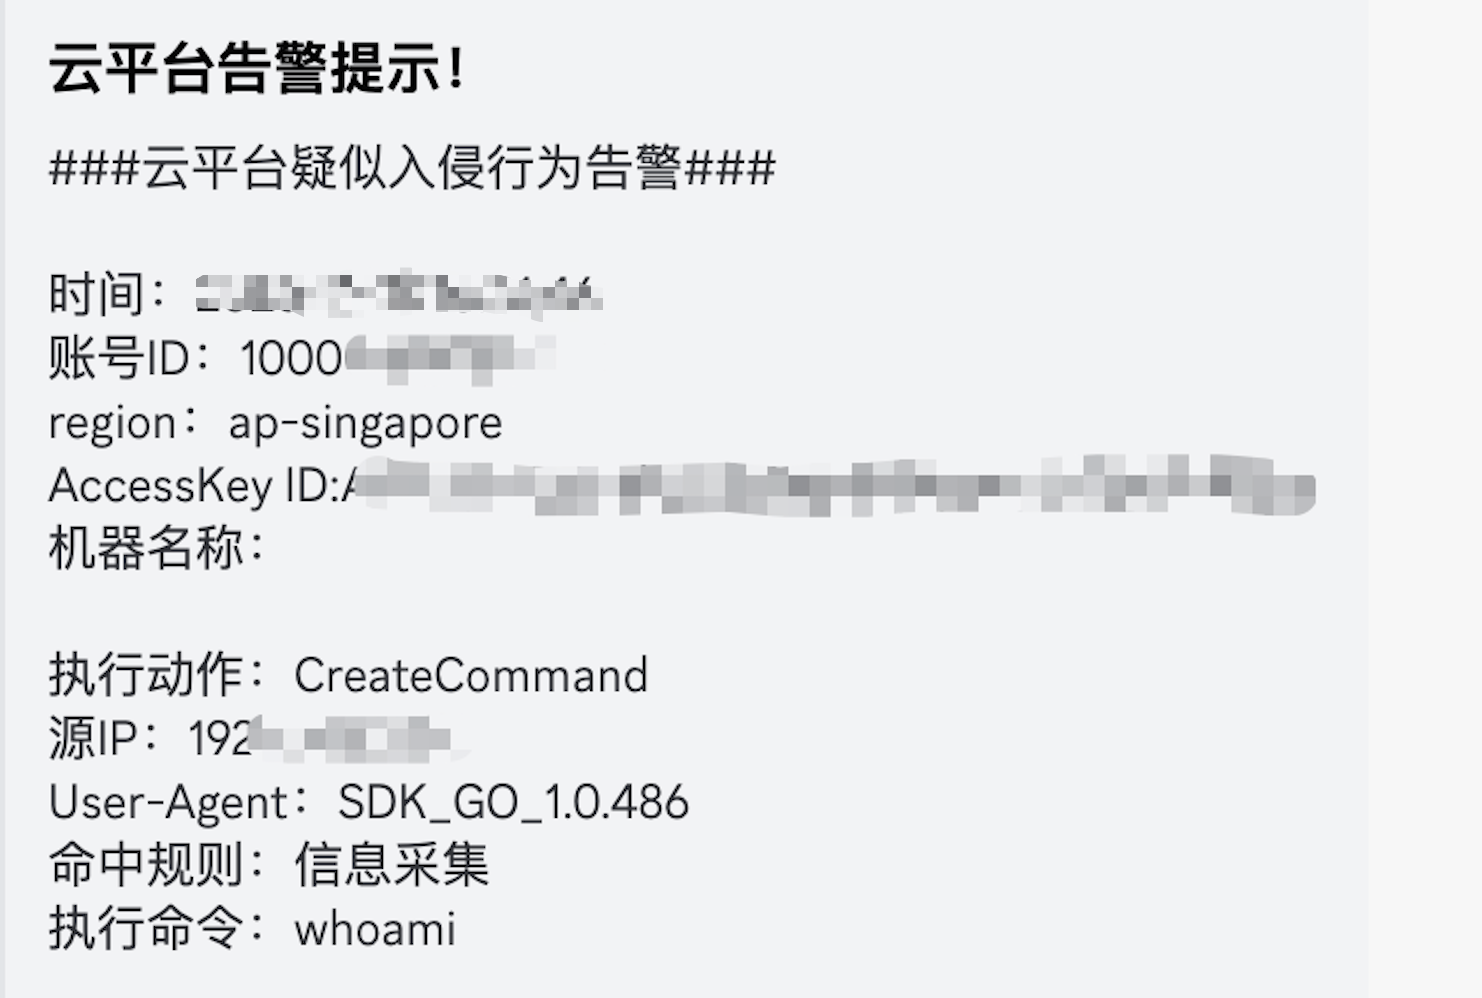 al0ne/cloud-audit
Automated cloud security auditing tool that detects AK/SK credential misuse by periodically auditing cloud platform logs using anomaly detection,…
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 pii-shield/pii-shield
Zero-code K8s sidecar for log sanitization. Detects secrets via Entropy Analysis, preserves JSON integrity, and redacts PII deterministically. 🛡️
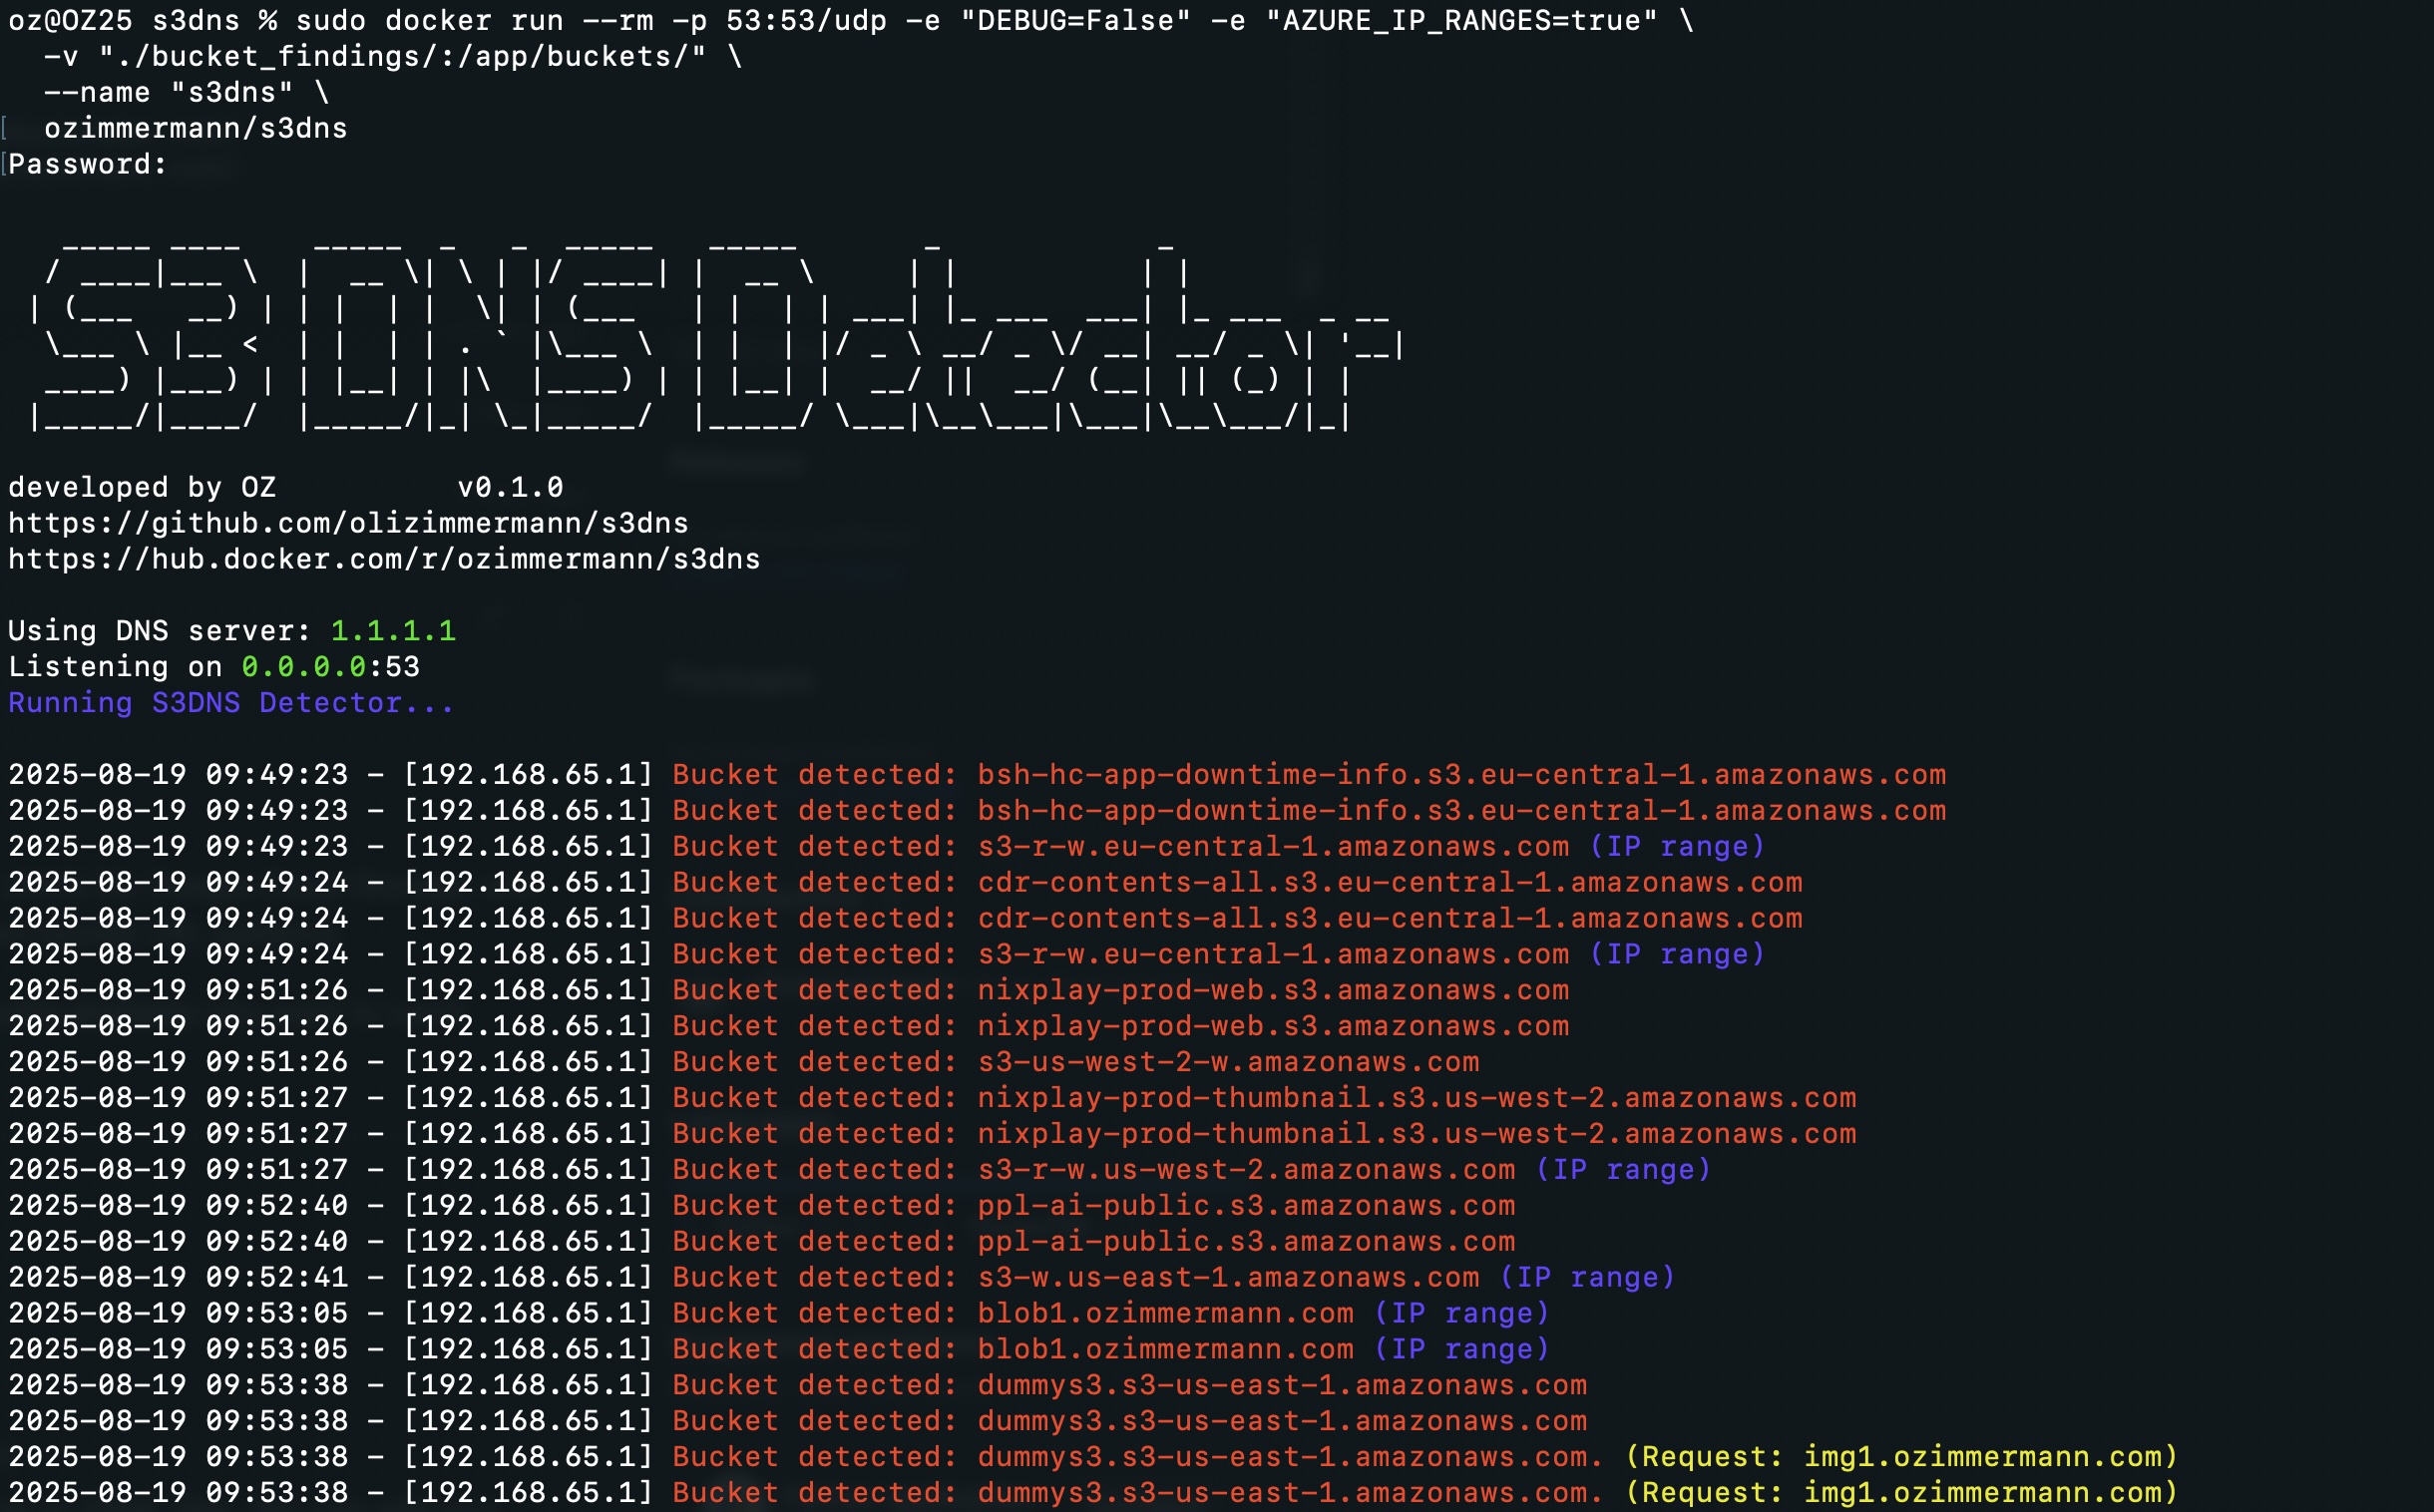 olizimmermann/s3dns
Passive DNS server that detects exposed cloud storage buckets (AWS S3, GCP, Azure) by resolving DNS requests, tracing CNAME chains, and flagging…
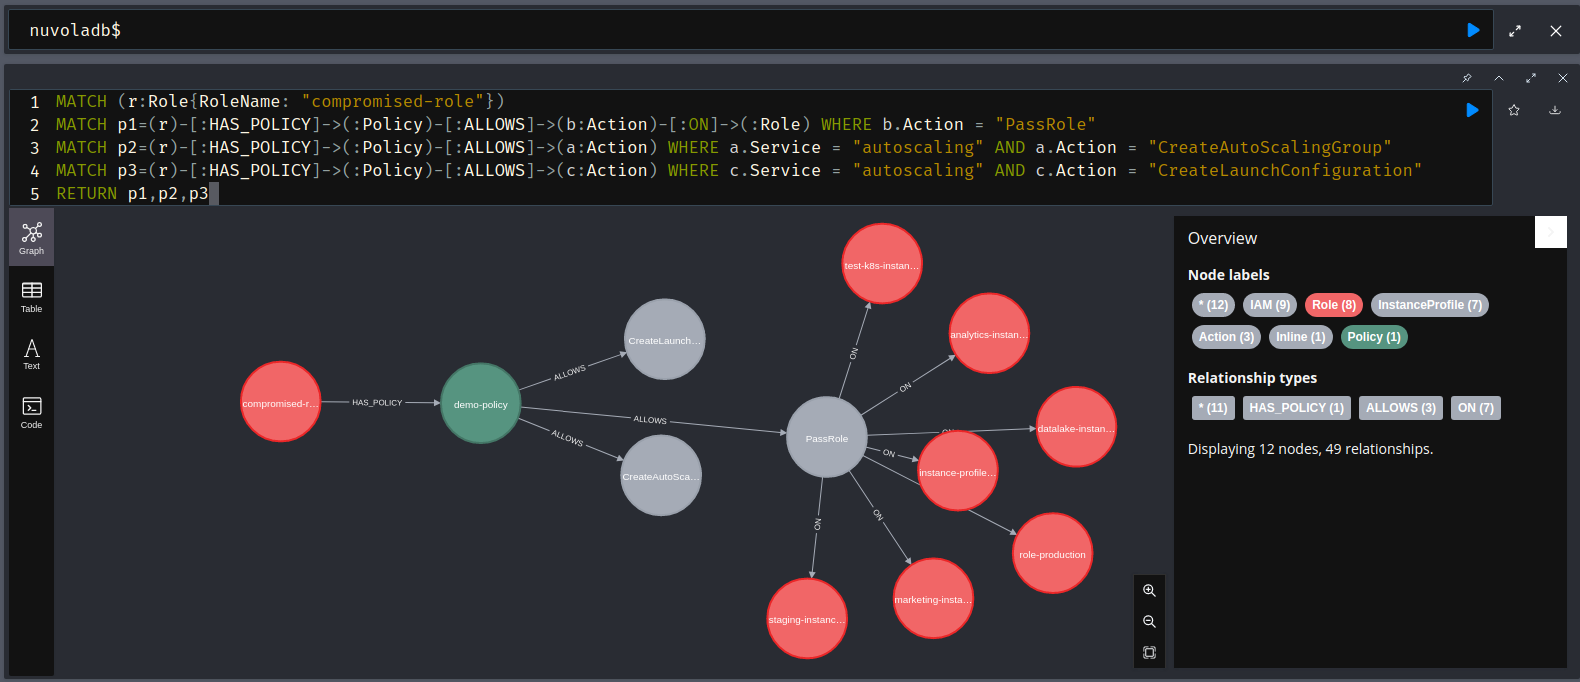 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 kube-tarian/tarian
eBPF-based runtime security agent for Kubernetes that detects unknown processes and file changes, enforces pre-registered constraints, and automates…
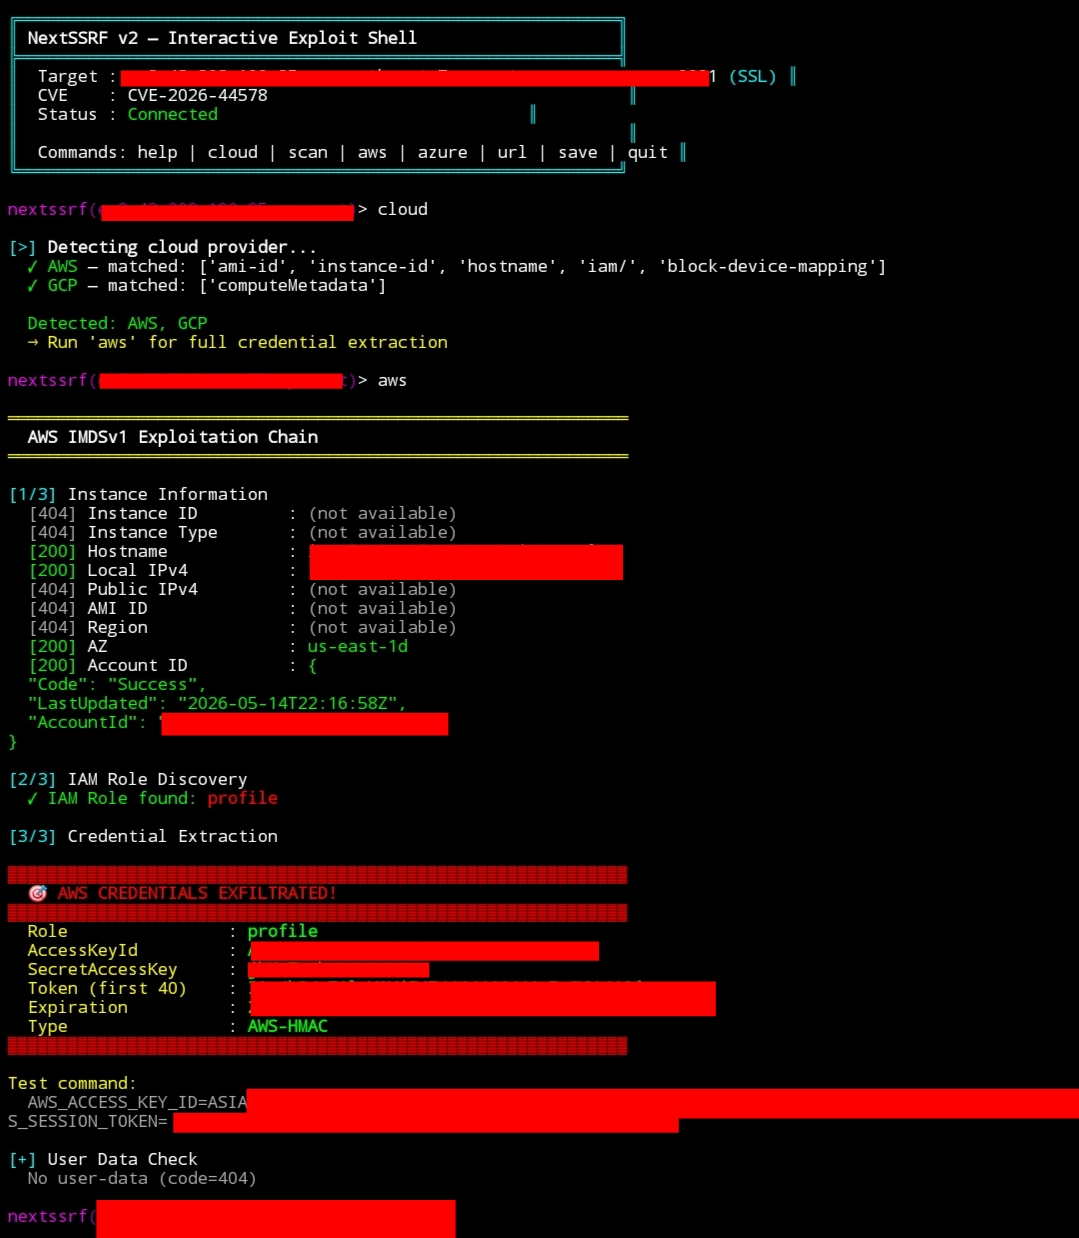 ynsmroztas/nextssrf
CVE-2026-44578 scanner and exploit tool for SSRF in Next.js WebSocket upgrade handler. Detects vulnerable versions, extracts cloud metadata, and…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 onapsis/onapsis-mandiant-cve-2025-31324-vuln-compromise-assessment
CVE-2025-31324 & CVE-2025-42999 vulnerability and compromise assessment tool
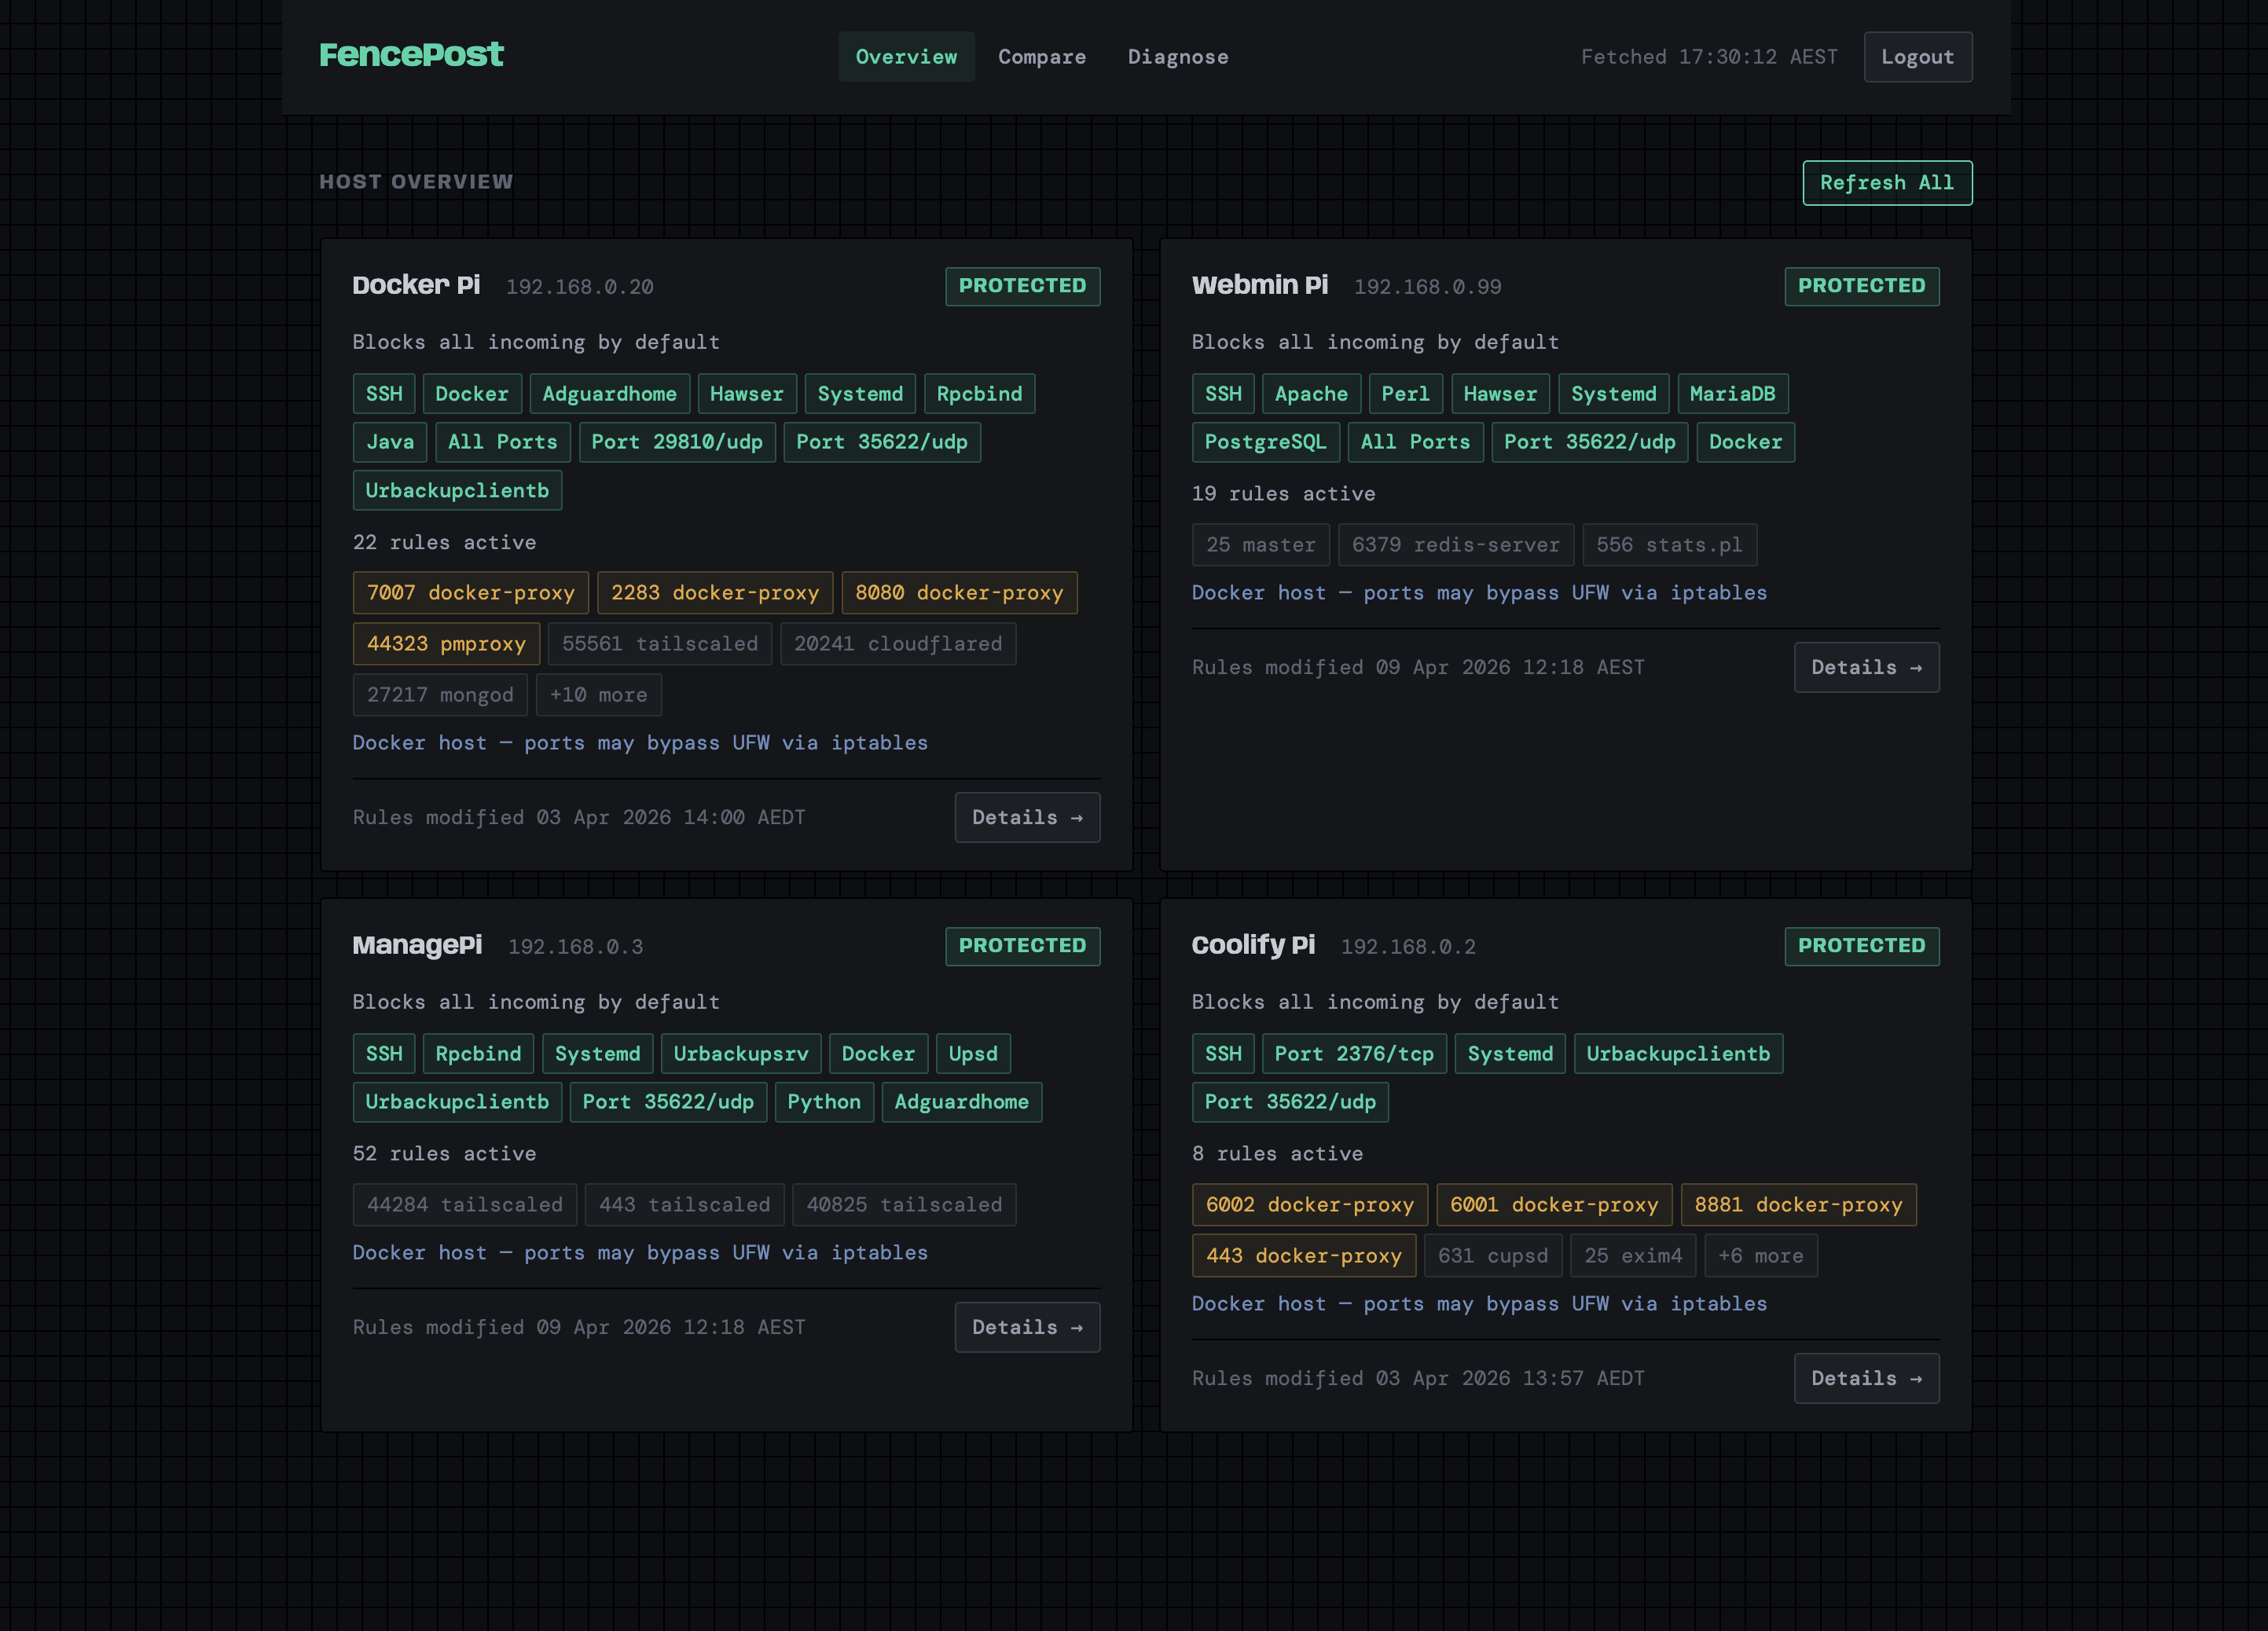 seriocomic/fencepost
Multi-host UFW firewall dashboard — explains rules in plain English, detects security gaps, and provides connection diagnostics
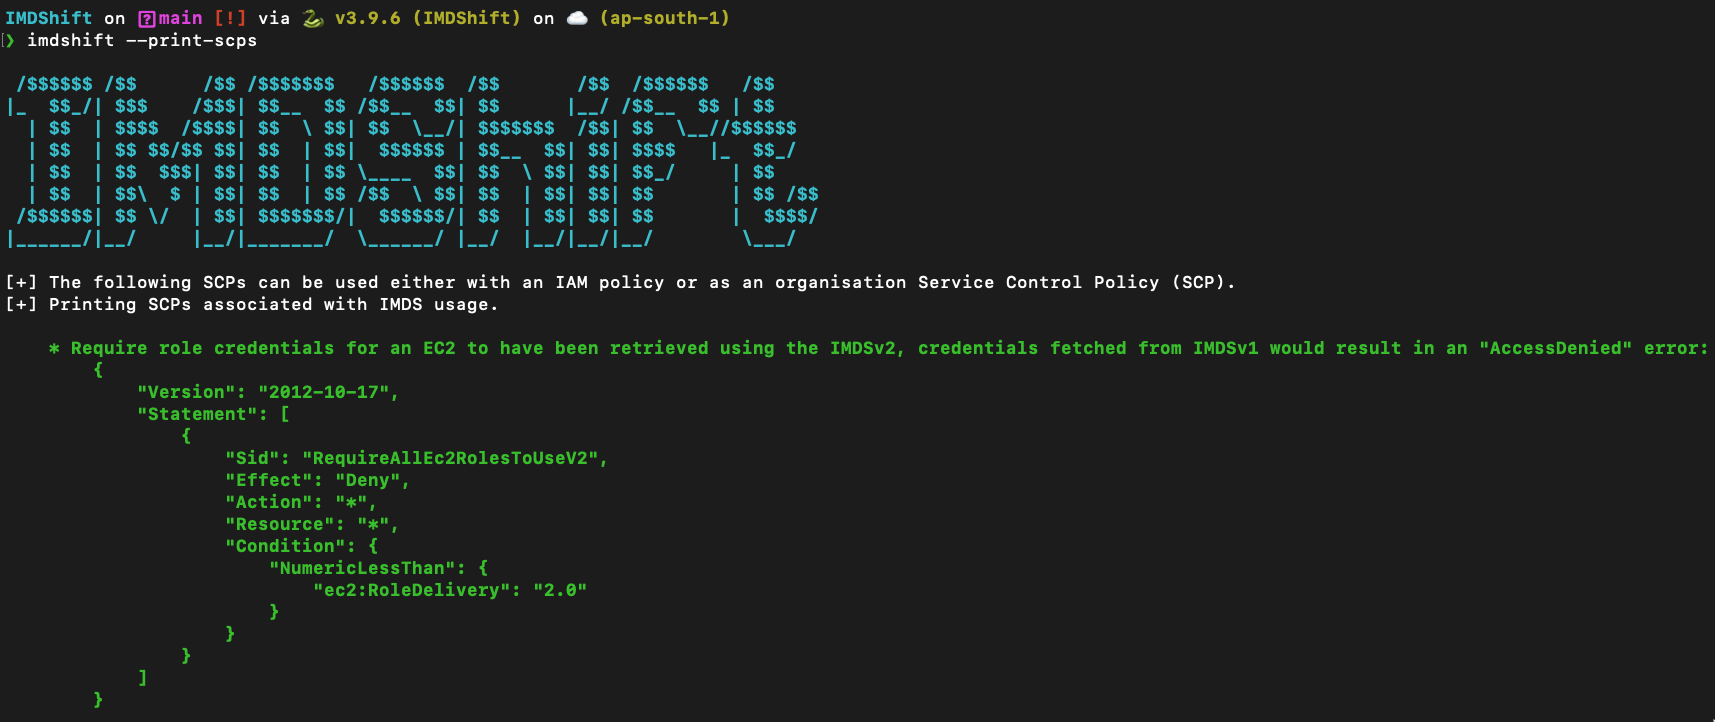 ayushpriya10/imdshift
Automates migration of AWS workloads from IMDSv1 to IMDSv2 to mitigate SSRF attacks. Detects IMDSv1 usage across EC2, ECS, EKS, Lightsail, and more,…
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 kubesphere/kubeeye
Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…
 cicd-sensor/cicd-sensor
eBPF-powered runtime security sensor for CI/CD pipelines. Detects supply-chain attacks, logs process ancestry and file access, and provides forensic…
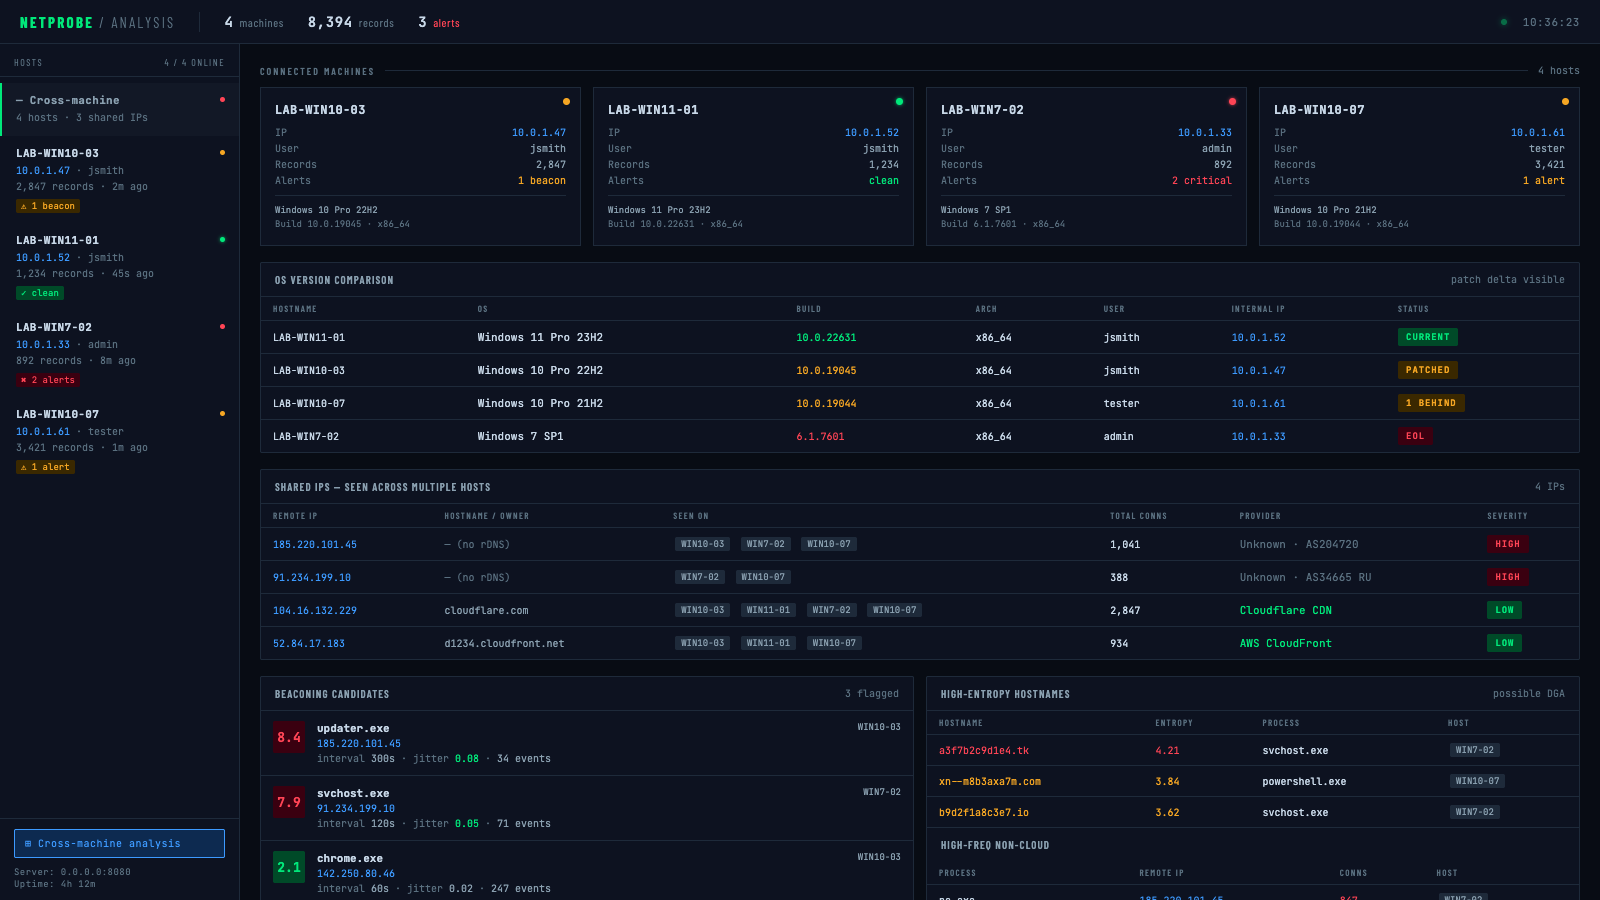 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity