
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
25 results
iam-vulnerable preview

iam-vulnerable

GitHubbishopfox/iam-vulnerable

Use Terraform to create your own vulnerable by design AWS IAM privilege escalation playground.
cloud-securityeducationidentity-access-management+4
590
1 year ago
autovpn preview

autovpn

GitHubttlequals0/autovpn

Create On Demand Disposable OpenVPN Endpoints on AWS.
cloud-securitygeneral-purpose-utilitiesprivacy
2.0k6 months ago
kontext-cli preview

kontext-cli

GitHubkontext-security/kontext-cli

Secure agents in seconds with permissions enforced at runtime.
ai-securityauthentication-authorizationcloud-security+3
2214 days ago
365-Stealer preview

365-Stealer

GitHubalteredsecurity/365-stealer

Automates Illicit Consent Grant attacks against Azure/O365 tenants to steal refresh tokens, exfiltrate emails/OneDrive data, and create malicious…
cloud-securitypenetration-testingphishing+1
5876 months ago
cloudfoxable preview

cloudfoxable

GitHubbishopfox/cloudfoxable

Create your own vulnerable by design AWS penetration testing playground

cloud-infrastructure-securitycloud-securityctf+3
4754 months ago
CVE-2019-16097 preview

CVE-2019-16097

GitHubianxtianxt/cve-2019-16097

Batch exploit script for CVE-2019-16097, targeting Harbor container registry to create unauthorized admin accounts via crafted API requests.
cloud-securitycontainer-securityexploitation+3
7 years ago
teller preview

teller

GitHubtellerops/teller

Cloud native secrets management for developers - never leave your command line for secrets.
cloud-infrastructure-securitycloud-securitycode-analysis+2
3.2k8 months ago
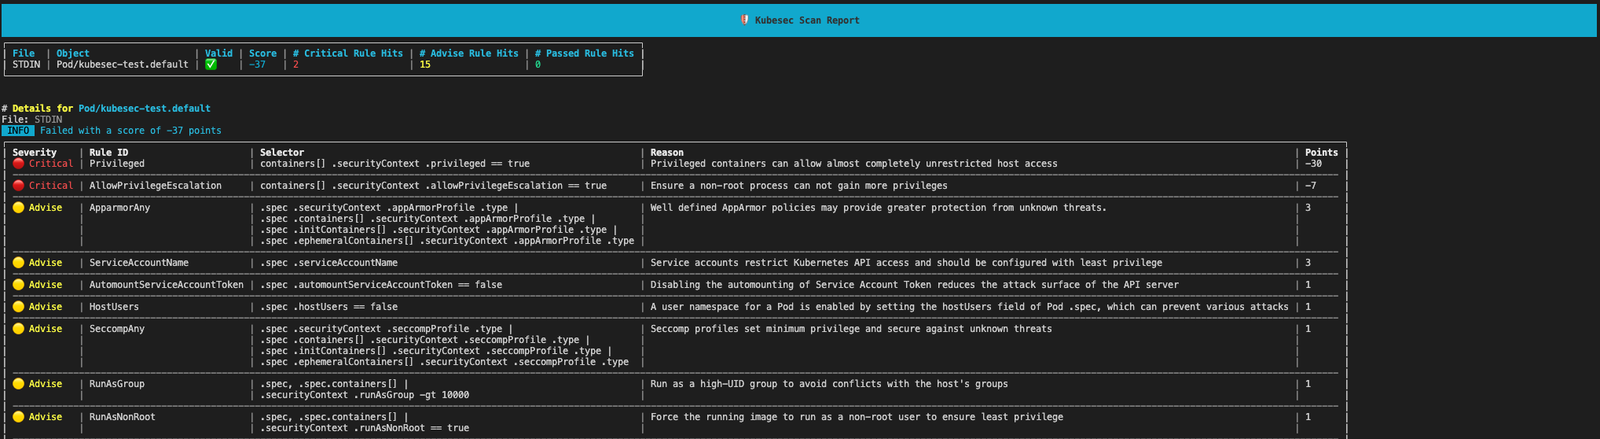
kubesec preview

kubesec

GitHubcontrolplaneio/kubesec

Security risk analysis for Kubernetes resources
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
1.5k3 months ago
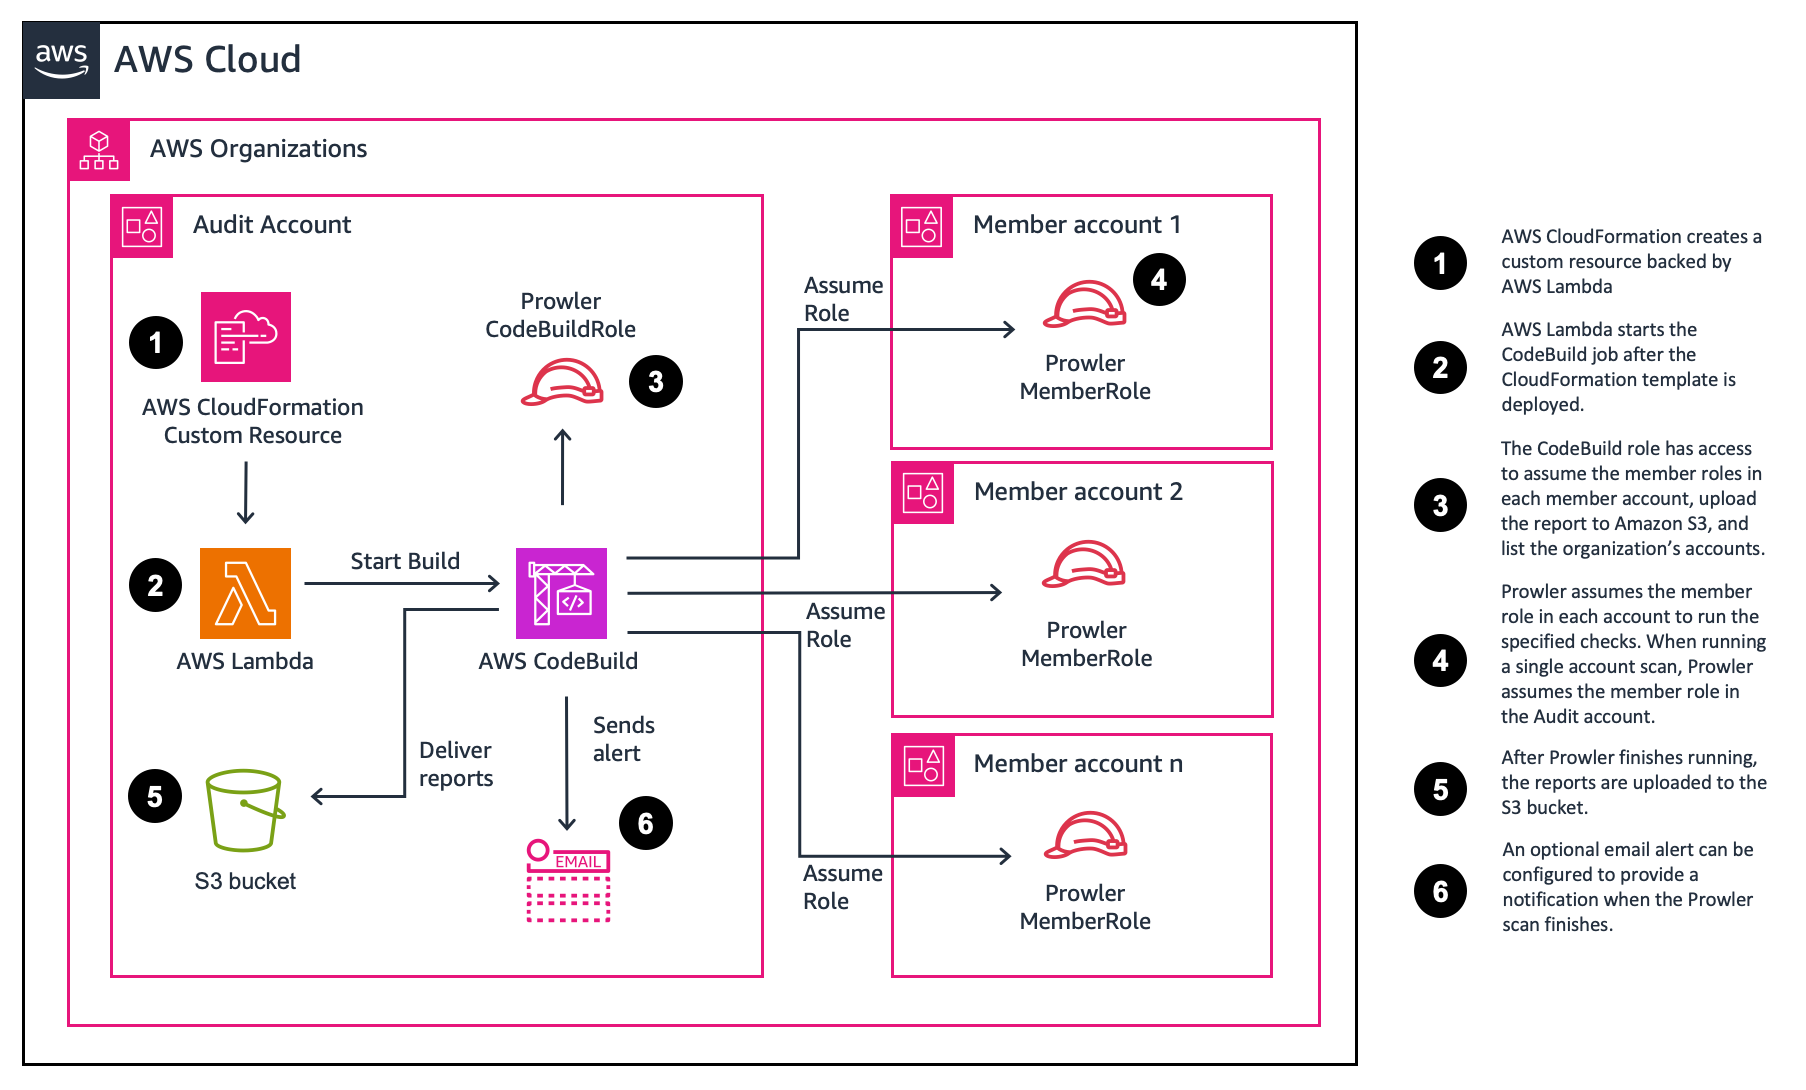
aws-security-assessment-solution preview

aws-security-assessment-solution

GitHubawslabs/aws-security-assessment-solution

An AWS tool to help you create a point in time assessment of your AWS account using Prowler.
cloud-infrastructure-securitycloud-securityconfiguration-auditing+2
6281 day ago
cmcp preview

cmcp

GitHubagentrust-io/cmcp

cMCP: Confidential MCP Gateway. Hardware-attested policy enforcement for MCP tool calls.
ai-securityapi-securityauthentication-authorization+4
3116h 47m ago
badPods preview

badPods

GitHubbishopfox/badpods

A collection of manifests that will create pods with elevated privileges.
cloud-securitycontainer-escapecontainer-security+4
7119 months ago
cve-2021-44228-workaround-buildpack preview
Archived

cve-2021-44228-workaround-buildpack

GitHubalexandreroman/cve-2021-44228-workaround-buildpack

Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
cloud-securitydevsecopseducation+3
34 years ago
attack_range preview

attack_range

GitHubsplunk/attack_range

A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
cloud-securityeducationlabs-practice+1
2.6k1 month ago
honeyLambda preview

honeyLambda

GitHub0x4d31/honeylambda

honeyλ - a simple, serverless application designed to create and monitor fake HTTP endpoints (i.e. URL honeytokens) automatically, on top of AWS…
cloud-securitydefensive-toolsincident-response+2
5257 years ago
yatas preview

yatas

GitHubpadok-team/yatas

:owl::mag_right: A simple tool to audit your AWS/GCP infrastructure for misconfiguration or potential security issues with plugins integration
cloud-infrastructure-securitycloud-securityconfiguration-auditing+3
3434 months ago
BlueTeam.Lab preview

BlueTeam.Lab

GitHubop7ic/blueteam.lab

Blue Team detection lab created with Terraform and Ansible in Azure.
cloud-securityconfiguration-auditingdefensive-tools+7
1911 year ago
gh-hijack-runner preview

gh-hijack-runner

GitHubsynacktiv/gh-hijack-runner

A python script to create a fake GitHub runner and hijack pipeline jobs to leak CI/CD secrets.
cloud-securitydata-exfiltrationexploitation+3
331 year ago
tunnelx preview

tunnelx

GitHubprojectdiscovery/tunnelx

TunnelX is a lightweight ingress tunneling tool designed to create a secure SOCKS5 proxy server for routing network traffic.

authenticationcloud-securitynetwork-security+3
31 month ago
Previous12Next