

trivy
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
cloud-infrastructure-securitycloud-securitycode-analysis+14
38.1k
aquasecurity/trivyFind vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 tenable/kaimonkey
Deliberately vulnerable Terraform infrastructure for learning cloud security misconfigurations and validating IaC scanner detection across AWS and…
 contrastsecurity/contrast
SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 xlab-si/iac-scan-runner
Service that scans your Infrastructure as Code for common vulnerabilities
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…
 dnscontrol/dnscontrol
Infrastructure as code for DNS!
 getanteon/anteon
eBPF-powered Kubernetes monitoring and performance testing platform that automatically generates service maps, tracks real-time metrics, and runs…
 microsoft/whatthehack
A collection of challenge based hack-a-thons including student guide, coach guide, lecture presentations, sample/instructional code and templates. …
 tmobile/pacbot
PacBot (Policy as Code Bot)
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
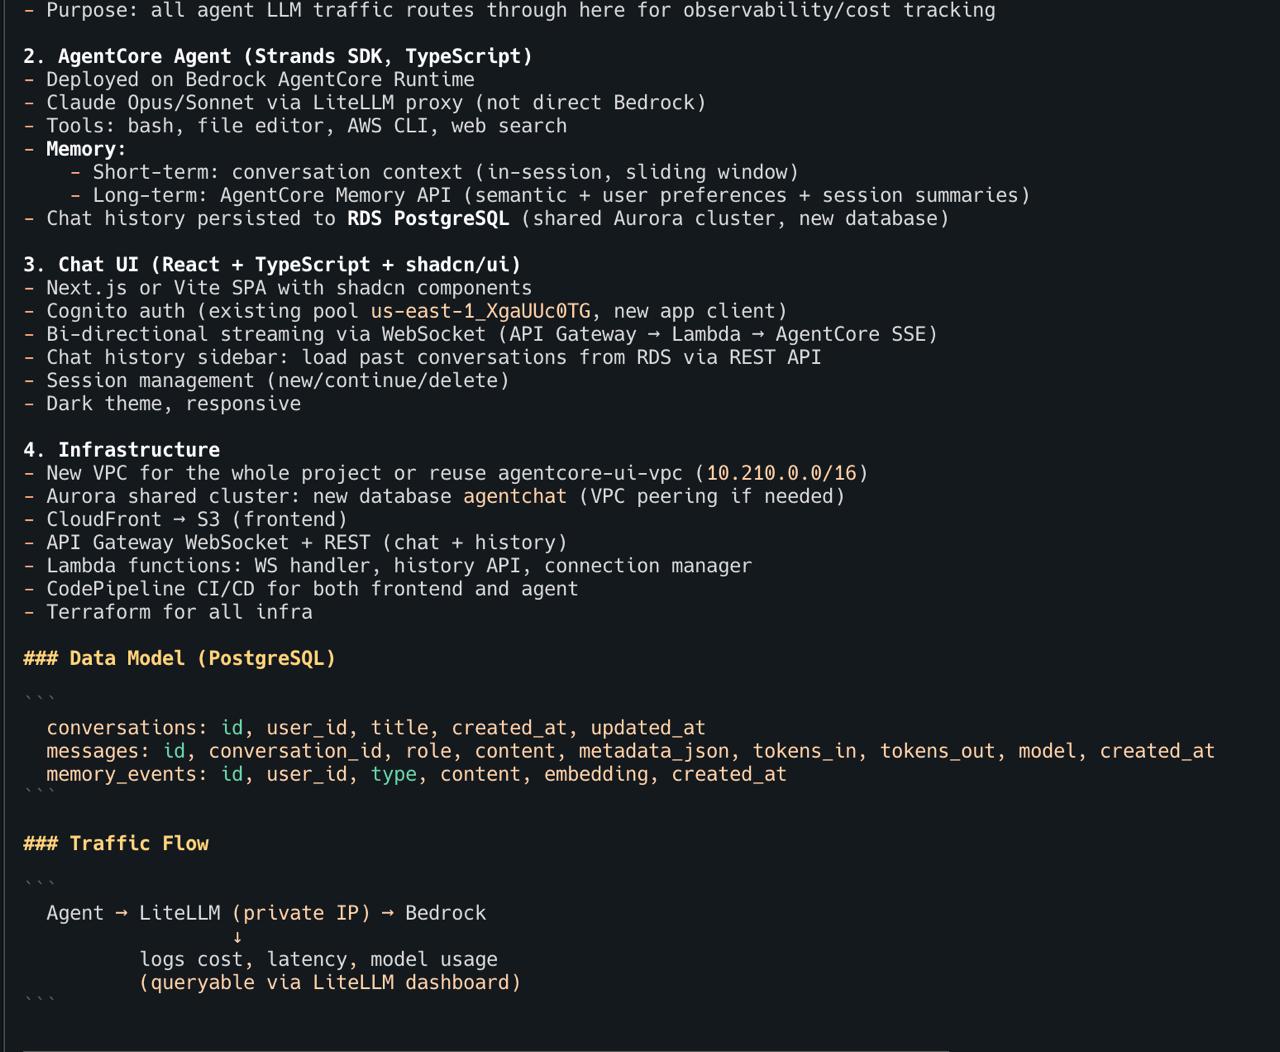 inceptionstack/lowkey
Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
 akhld/spark-exploit
Arbitary Code Execution in Unsecured Apache Spark Cluster
 george0papasotiriou/cve-2026-22008-aws-lambda-layer-injection-via-shared-layer-arn
Proof-of-concept for CVE-2026-22008 demonstrating AWS Lambda layer injection via untrusted ARNs, enabling arbitrary code execution and credential…
 radzarr/wsusresponder
Module PowerShell de réponse à l'incident CVE-2025-59287 — WSUS Remote Code Execution (RCE)
 mrk336/cve-2024-10220-kubernetes-gitrepo-volume-vulnerability
CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…