

pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.4k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 owasp/dvsa
a Damn Vulnerable Serverless Application
 dz-y/azure-apim-dev-portal-signup-bypass
Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…
 armourbird/csf
ArmourBird CSF - Container Security Framework
 shoucheng3/aws__aws-sdk-java_cve-2022-31159_1-12-2600
Java SDK for integrating with Amazon Web Services, providing secure API access to S3, DynamoDB, EC2, and more, with built-in authentication,…
 cloudgraphdev/cli
The universal GraphQL API and CSPM tool for AWS, Azure, GCP, K8s, and tencent.
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 openbmc/bmcweb
A do everything Redfish, KVM, GUI, and DBus webserver for OpenBMC
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 placeos/auth
PlaceOS authentication service and API gatekeeper.
 shoucheng3/fabric8io__kubernetes-client_cve-2021-4178_5-0-2
Java client providing fluent DSL access to Kubernetes and OpenShift REST APIs for managing cloud-native infrastructure, pods, services, and…
 shoucheng3/jenkinsci__docker-commons-plugin_cve-2022-20617_1-17
Jenkins plugin providing shared API for Docker credential management, registry authentication, daemon configuration, and image fingerprinting across…
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 shoucheng3/kubernetes-client__java_cve-2020-8570_client-java-parent-9_0_2_fixed
Java client library for the Kubernetes API, enabling programmatic management of clusters, pods, deployments, and other resources with support for…
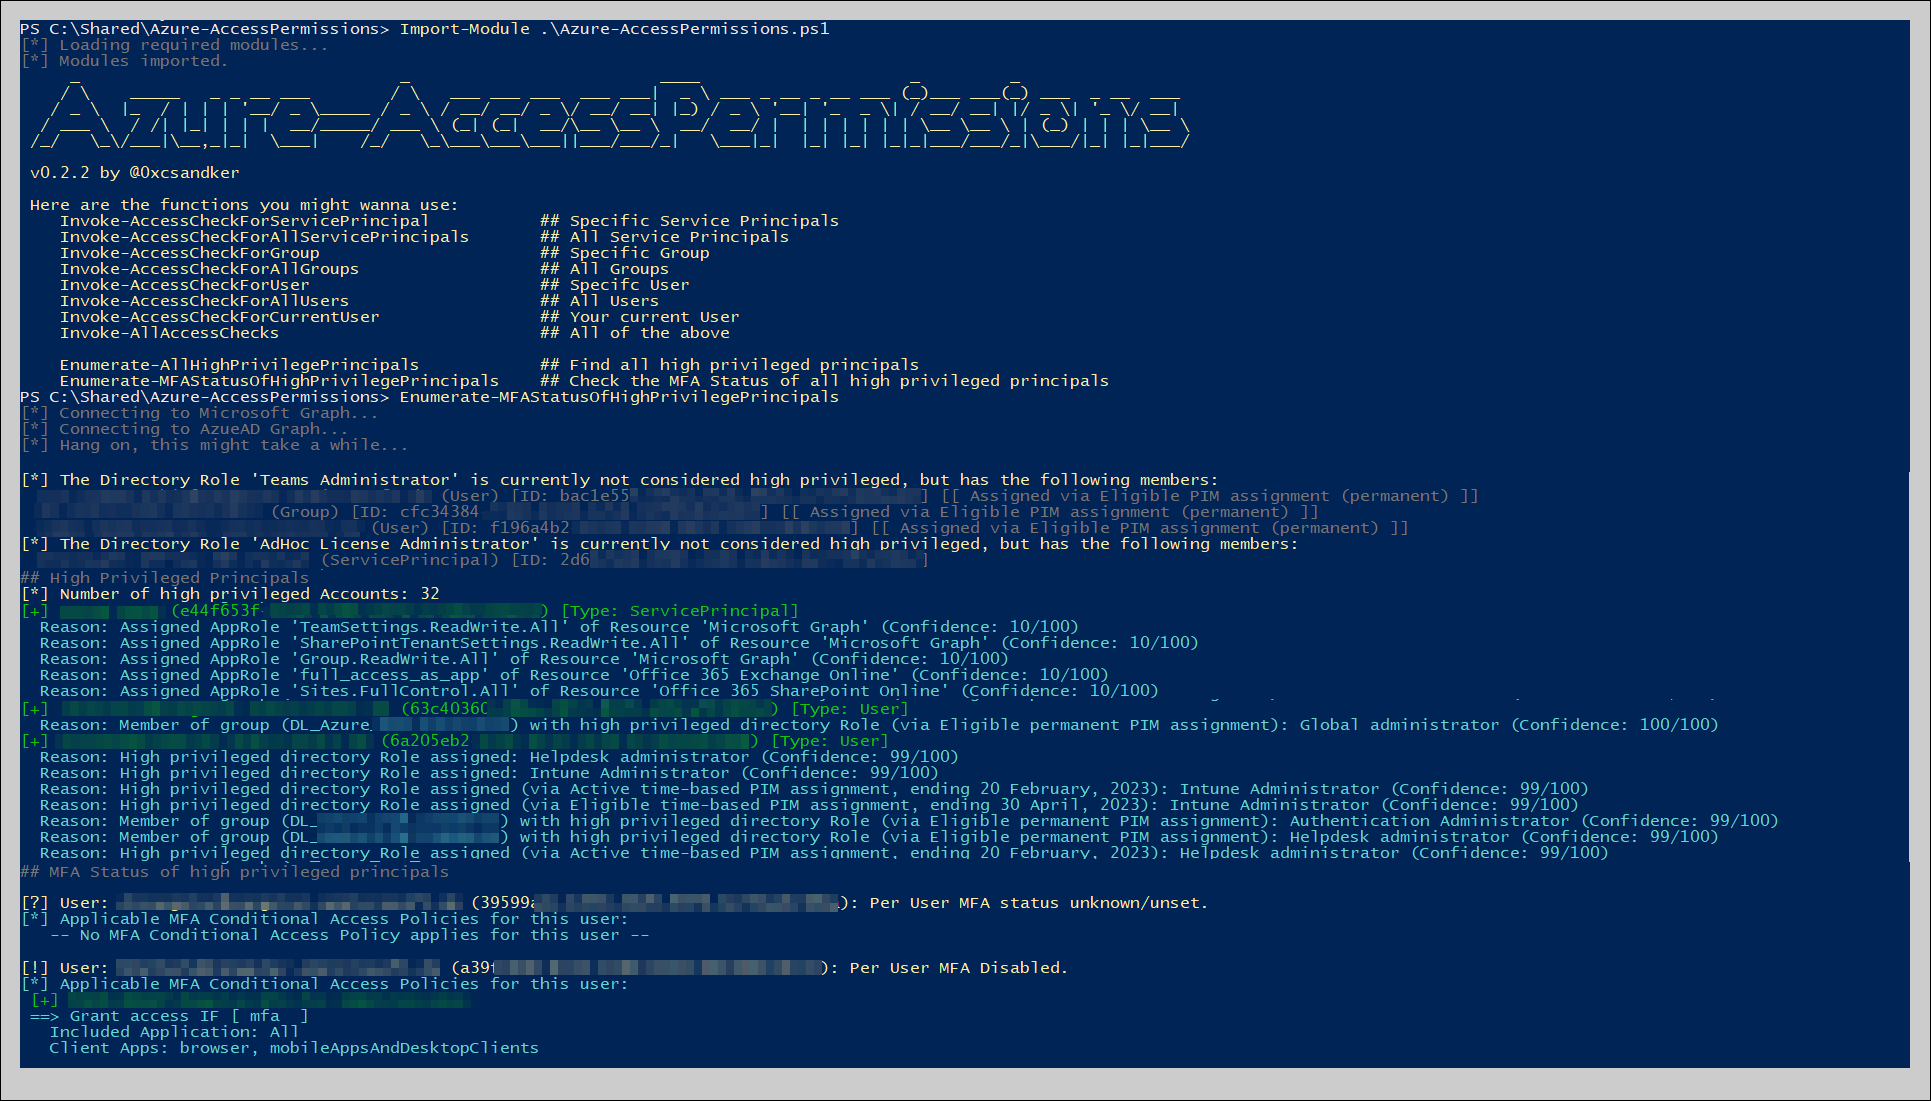 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
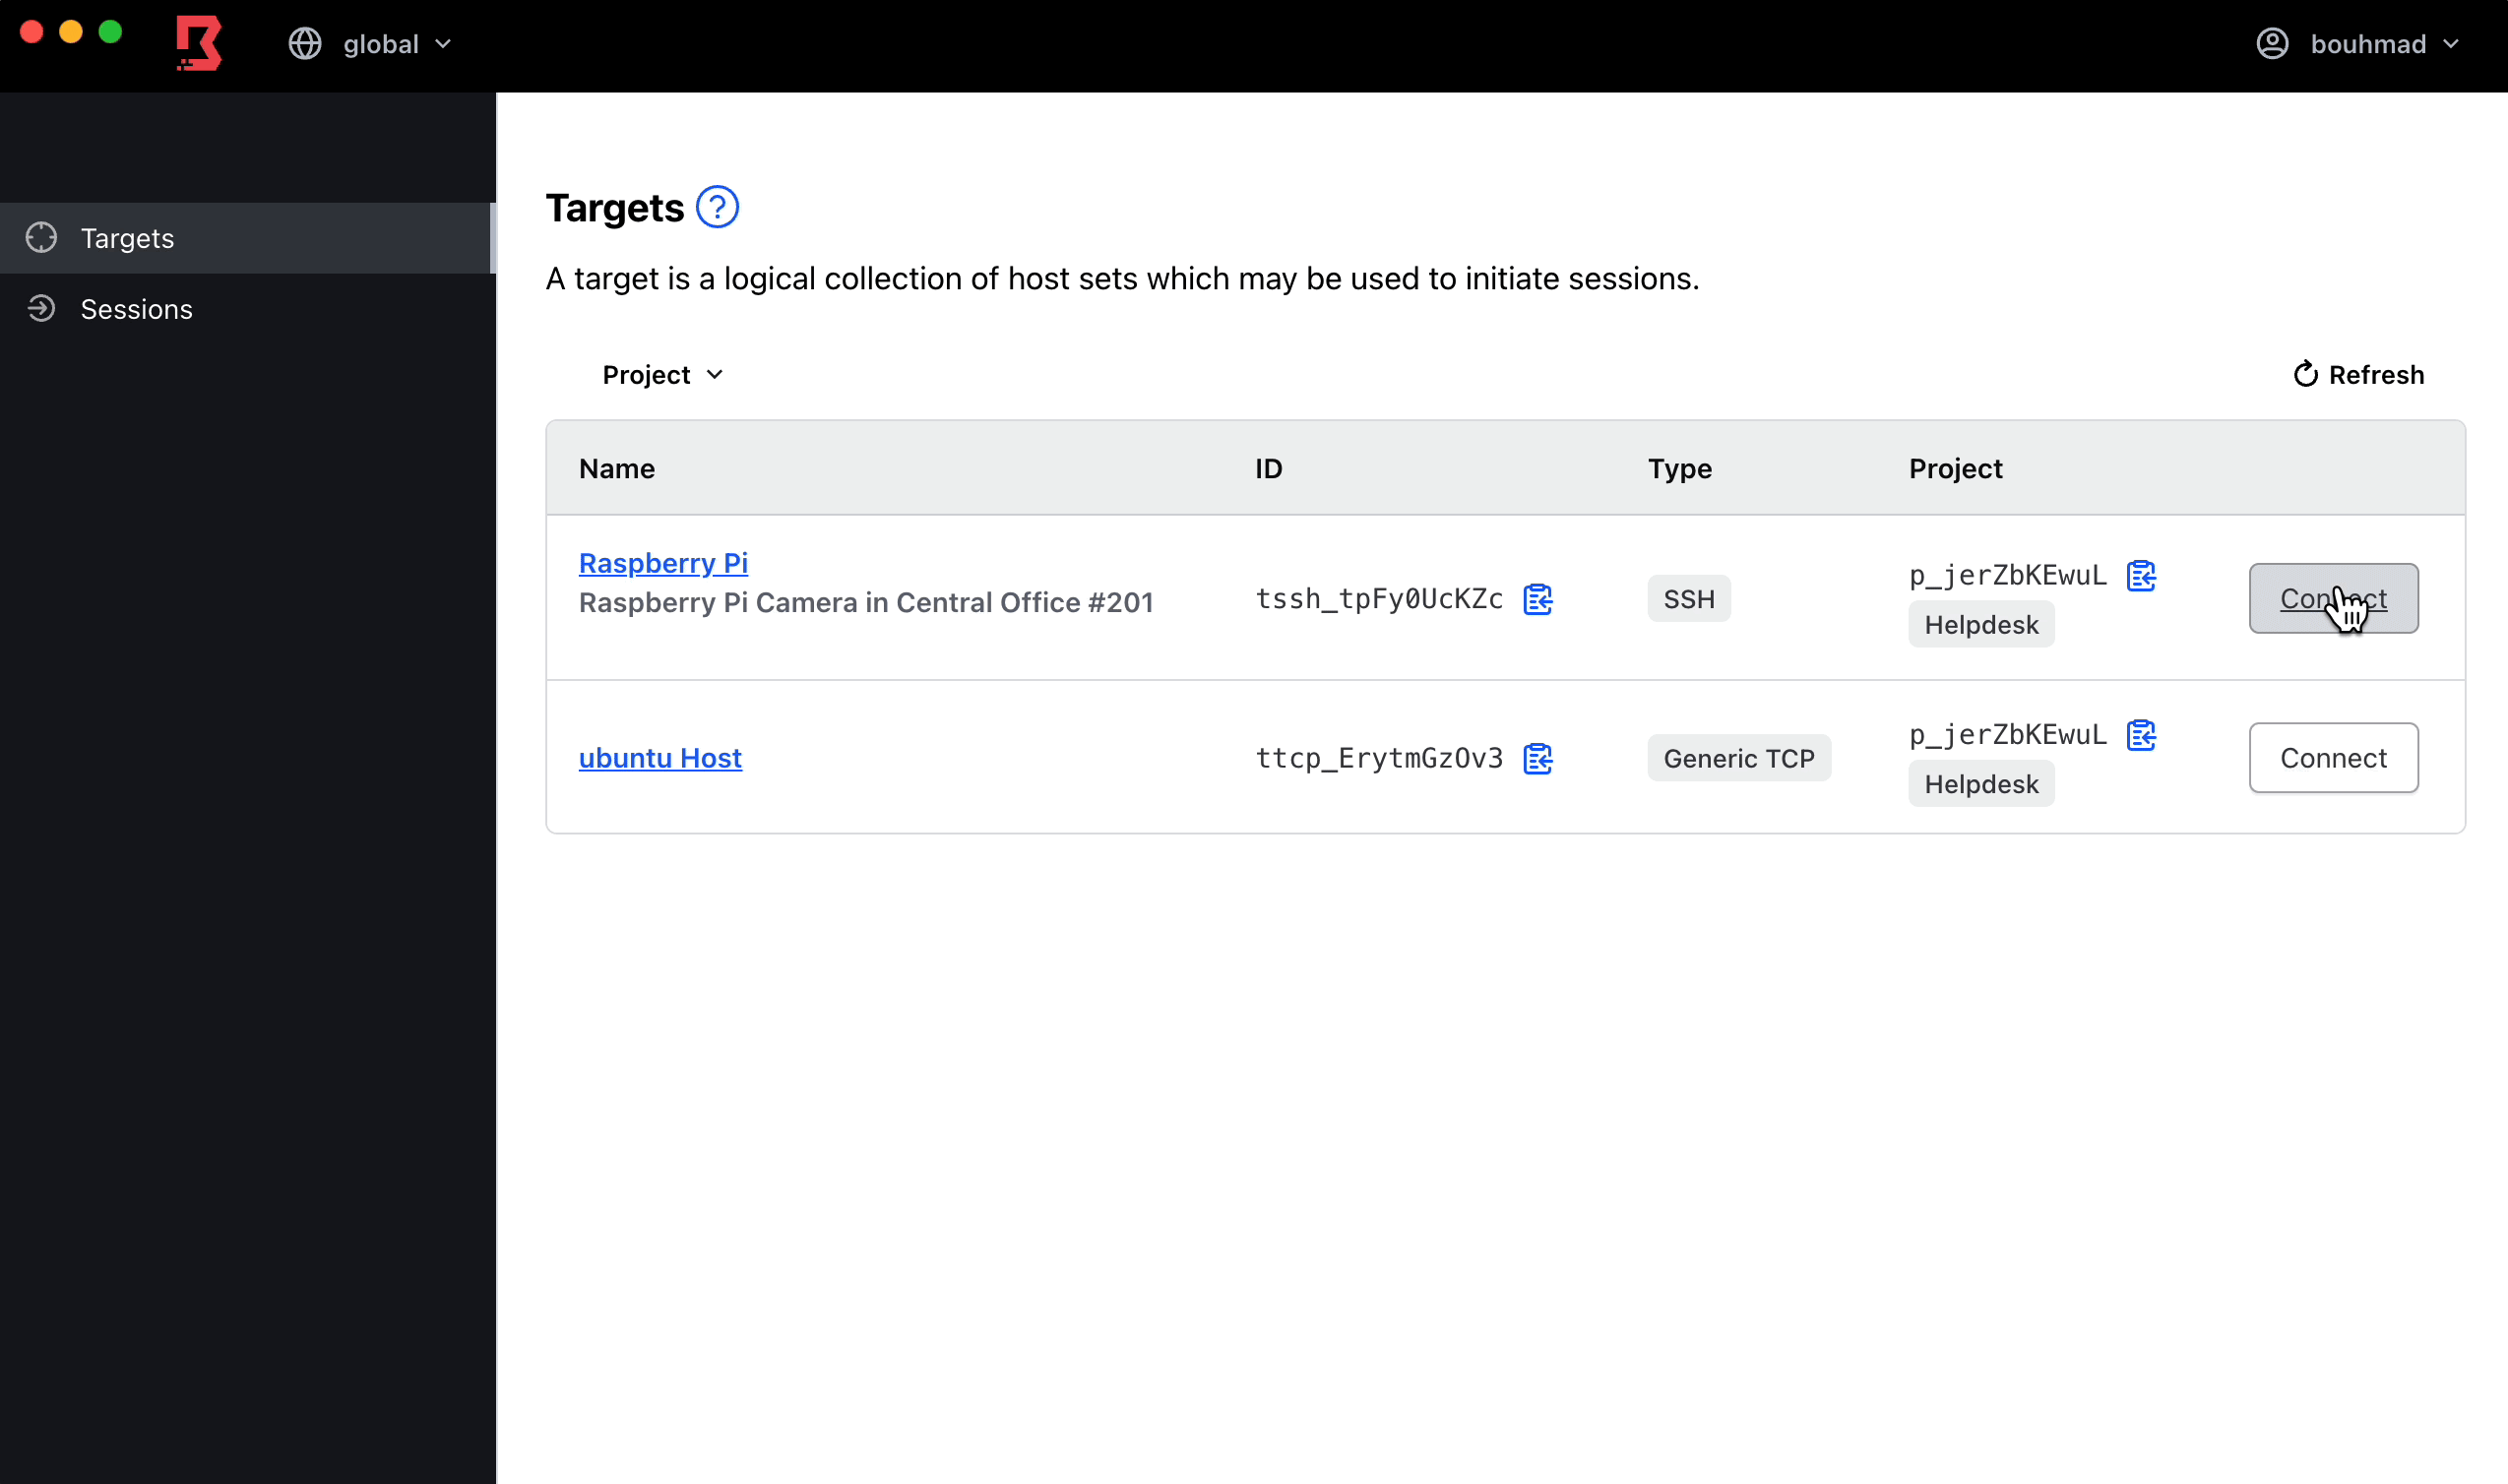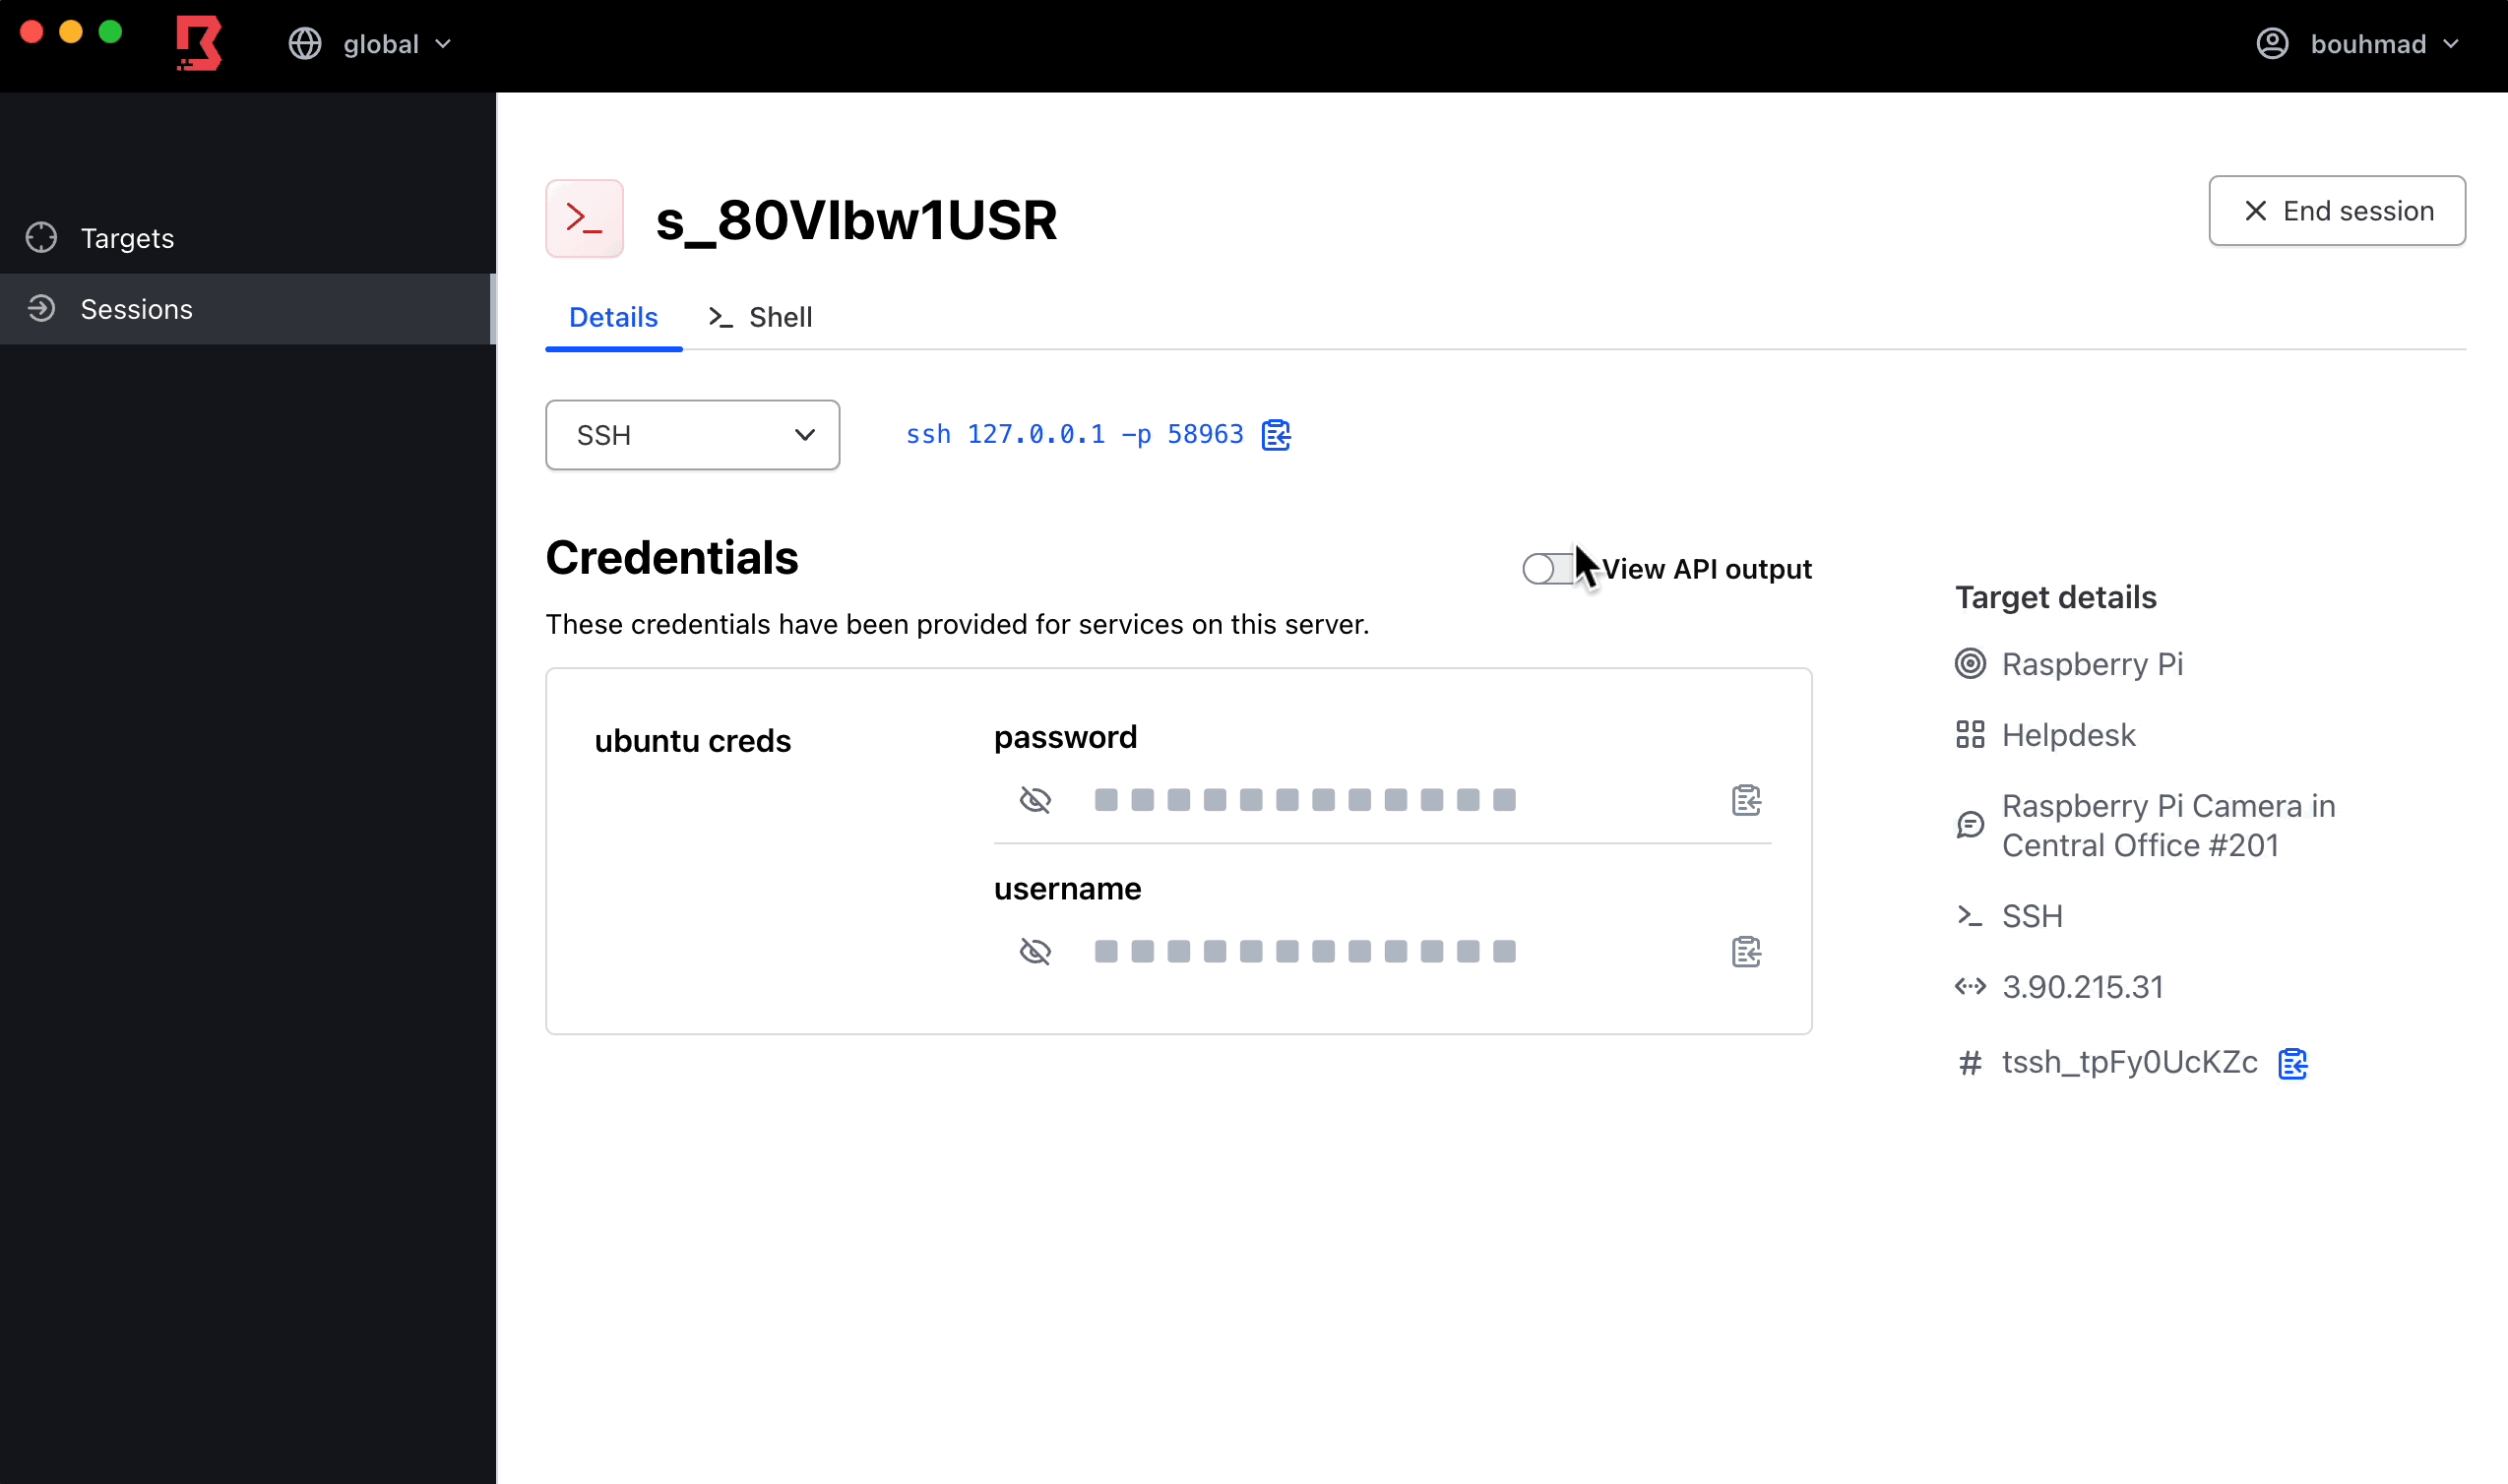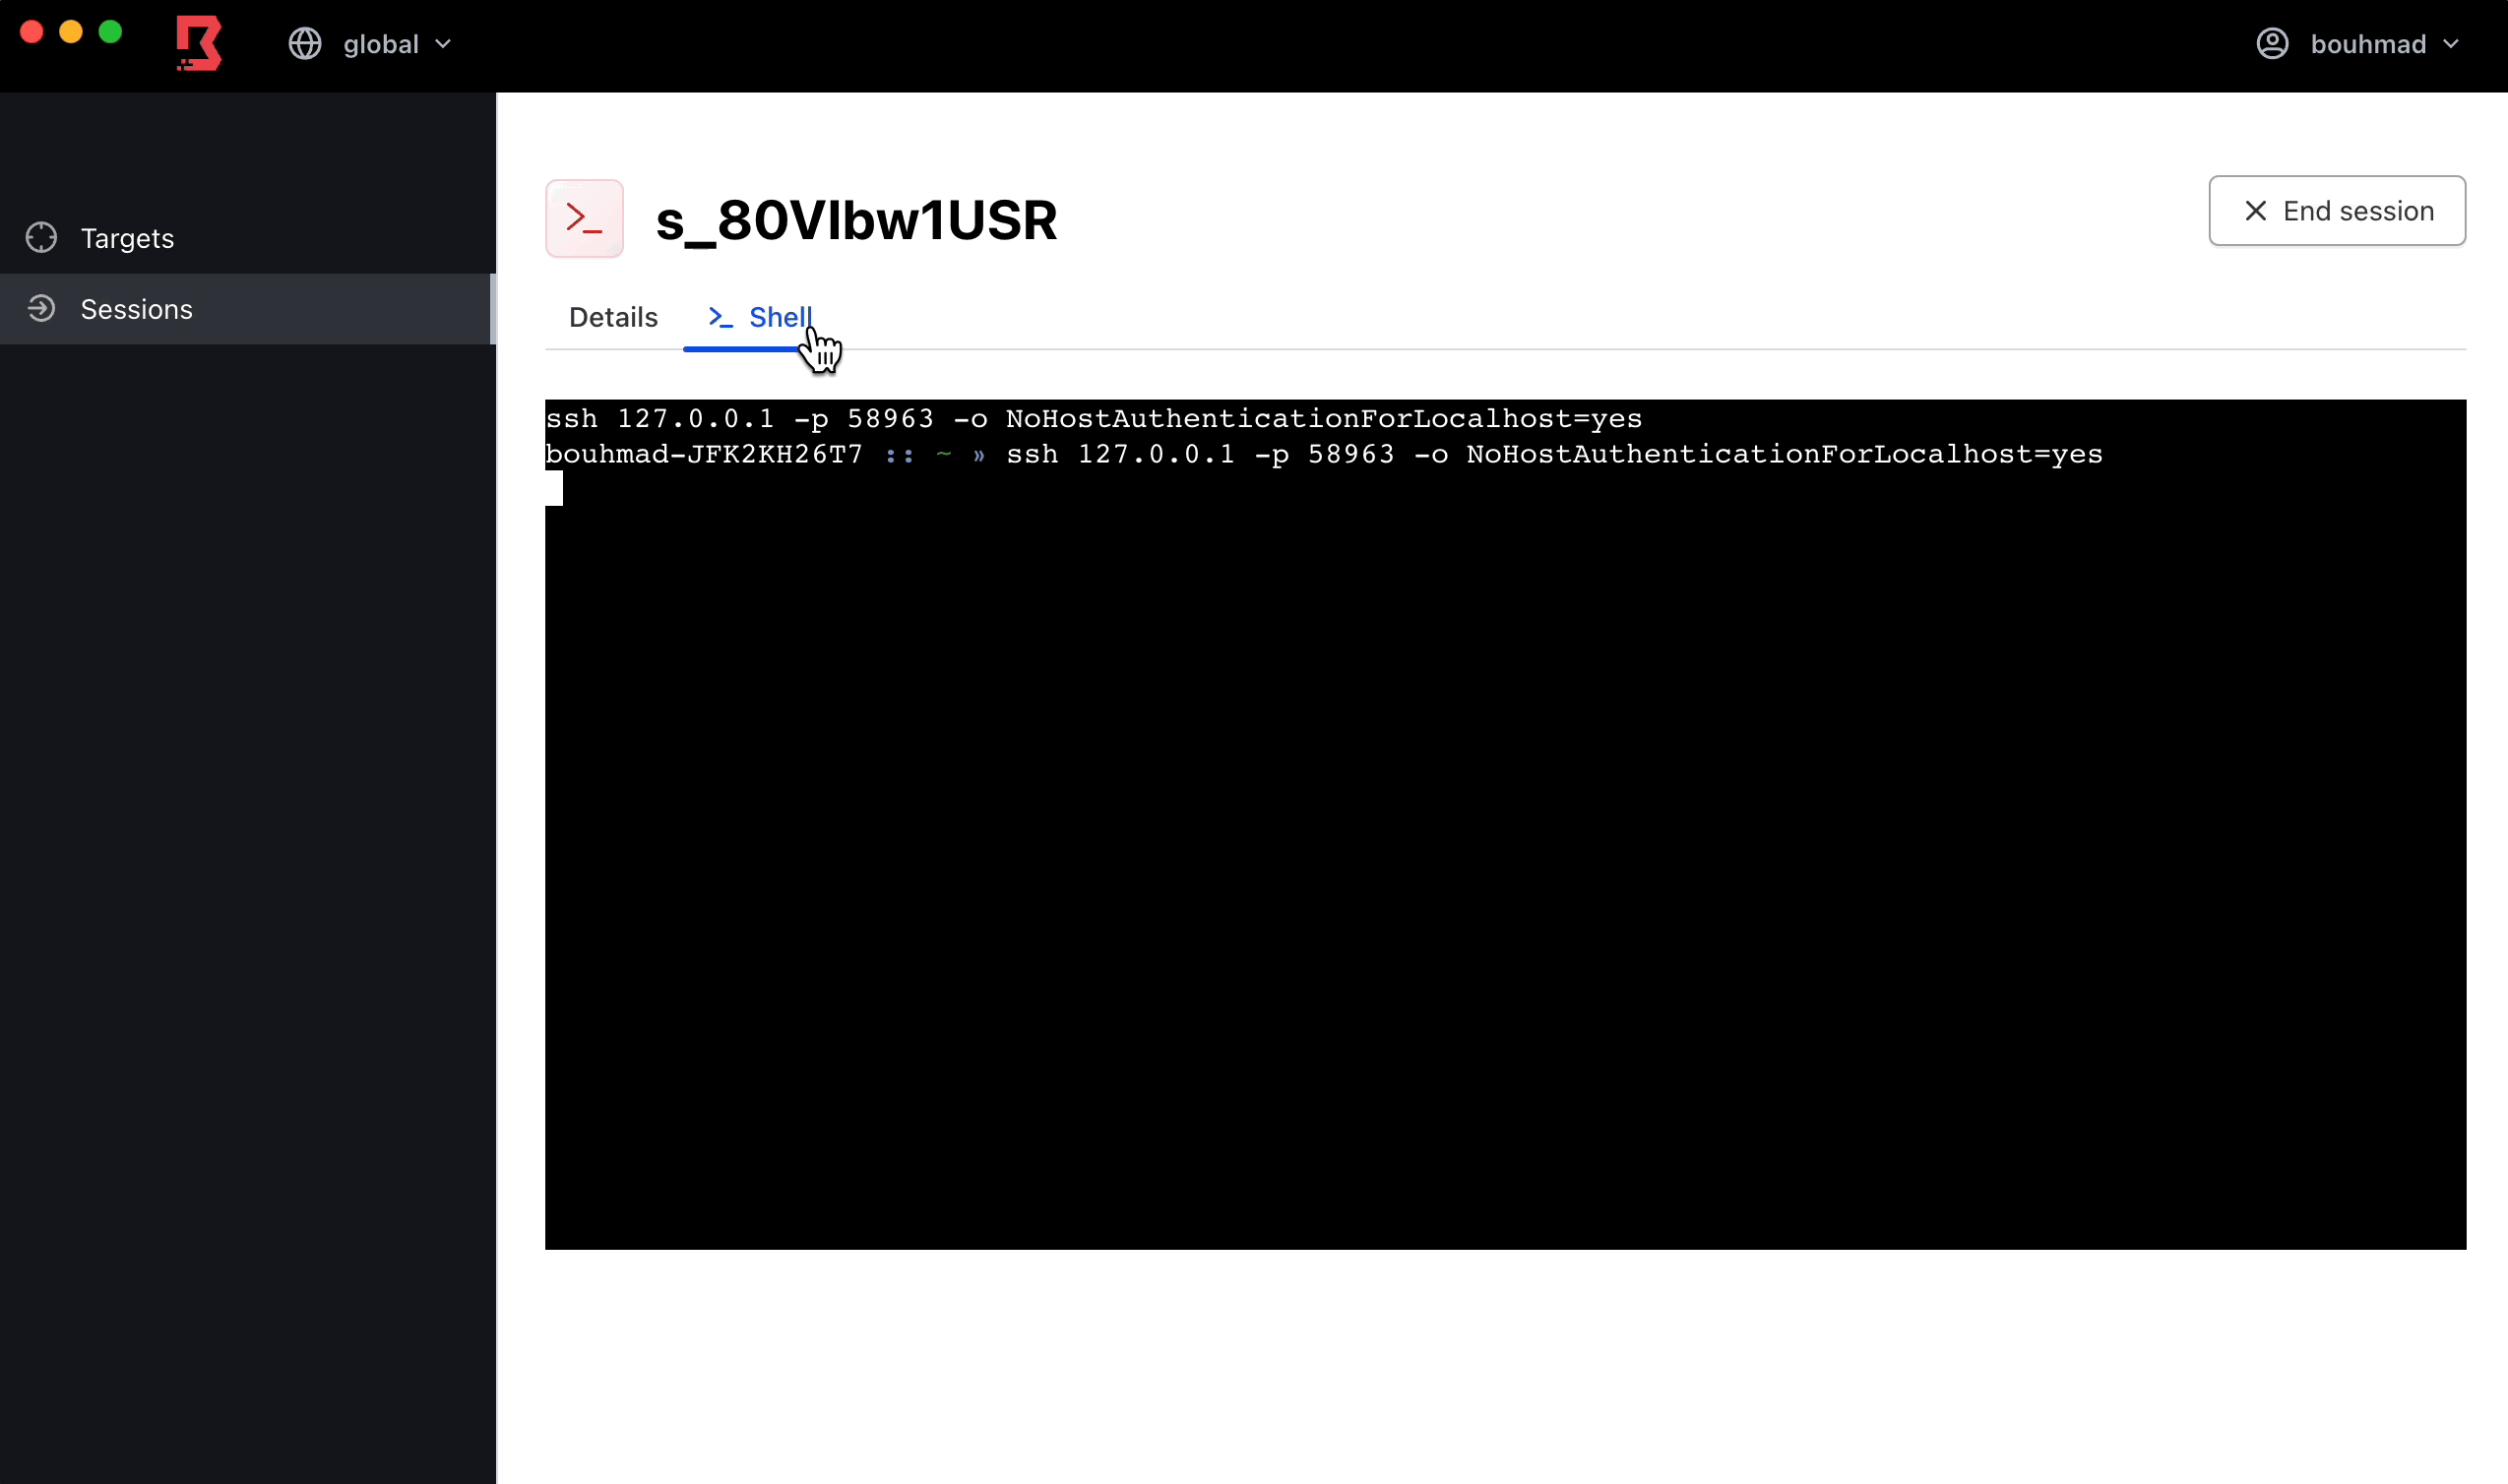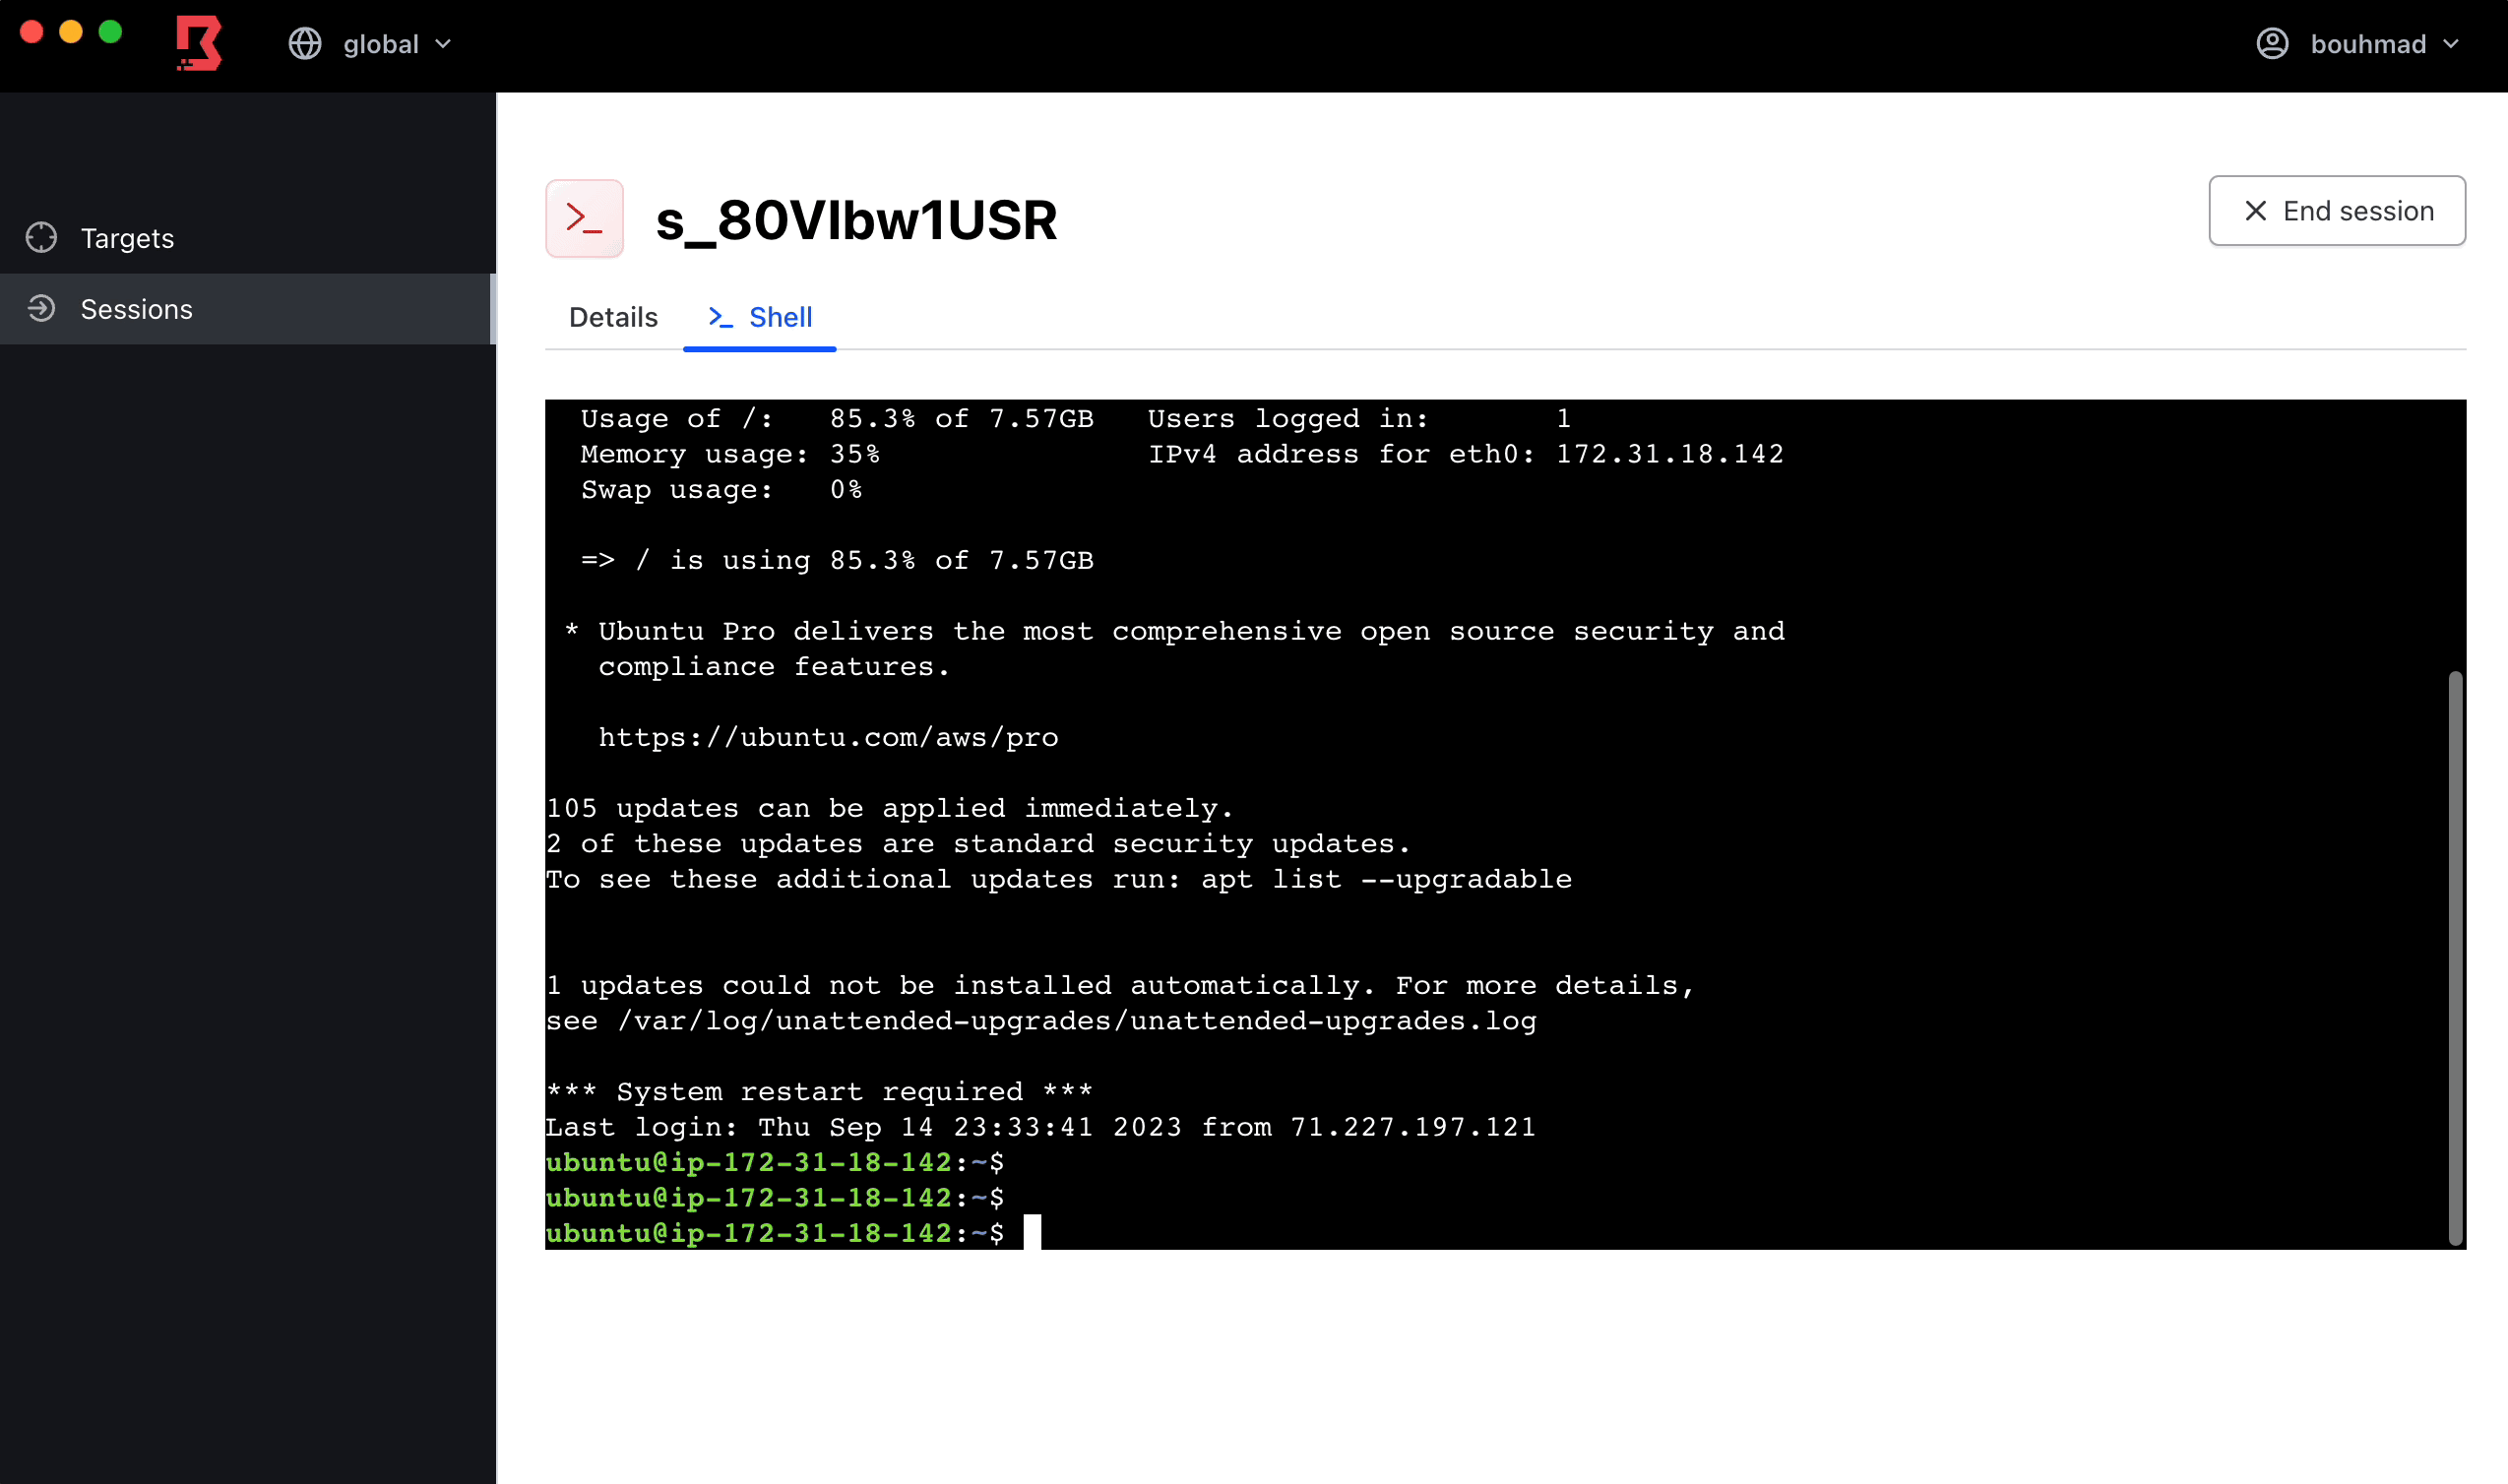 hashicorp/boundary
Boundary enables identity-based access management for dynamic infrastructure.
 aker-gateway/aker
SSH bastion/jump host/jumpserver