kubeshark
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
kubeshark/kubesharkeBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 skydive-project/skydive
An open source real-time network topology and protocols analyzer
 batfish/pybatfish
Python client for Batfish, a network configuration analysis tool that validates security, reliability, and compliance by modeling network behavior…
 cyberark/blobhunter
Find exposed data in Azure with this public blob scanner
 capture0x/aws-pentest
Automated AWS security assessment CLI with 30 modules covering IAM privilege escalation, S3 exposure, compute, network, logging and misconfiguration…
 thirukguru/aws-perimeter
A terminal-based AWS Security Scanner with 102+ security checks across VPC, IAM, S3, CloudTrail, containers (ECS/EKS), and AI attack detection.…
 abrahamsurf/sdwan-scanner-cve-2026-20127
Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026
 aquasecurity/trivy
Find vulnerabilities, misconfigurations, secrets, SBOM in containers, Kubernetes, code repositories, clouds and more
 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 usmannasir/cyberpanel
Cyber Panel - The hosting control panel for OpenLiteSpeed
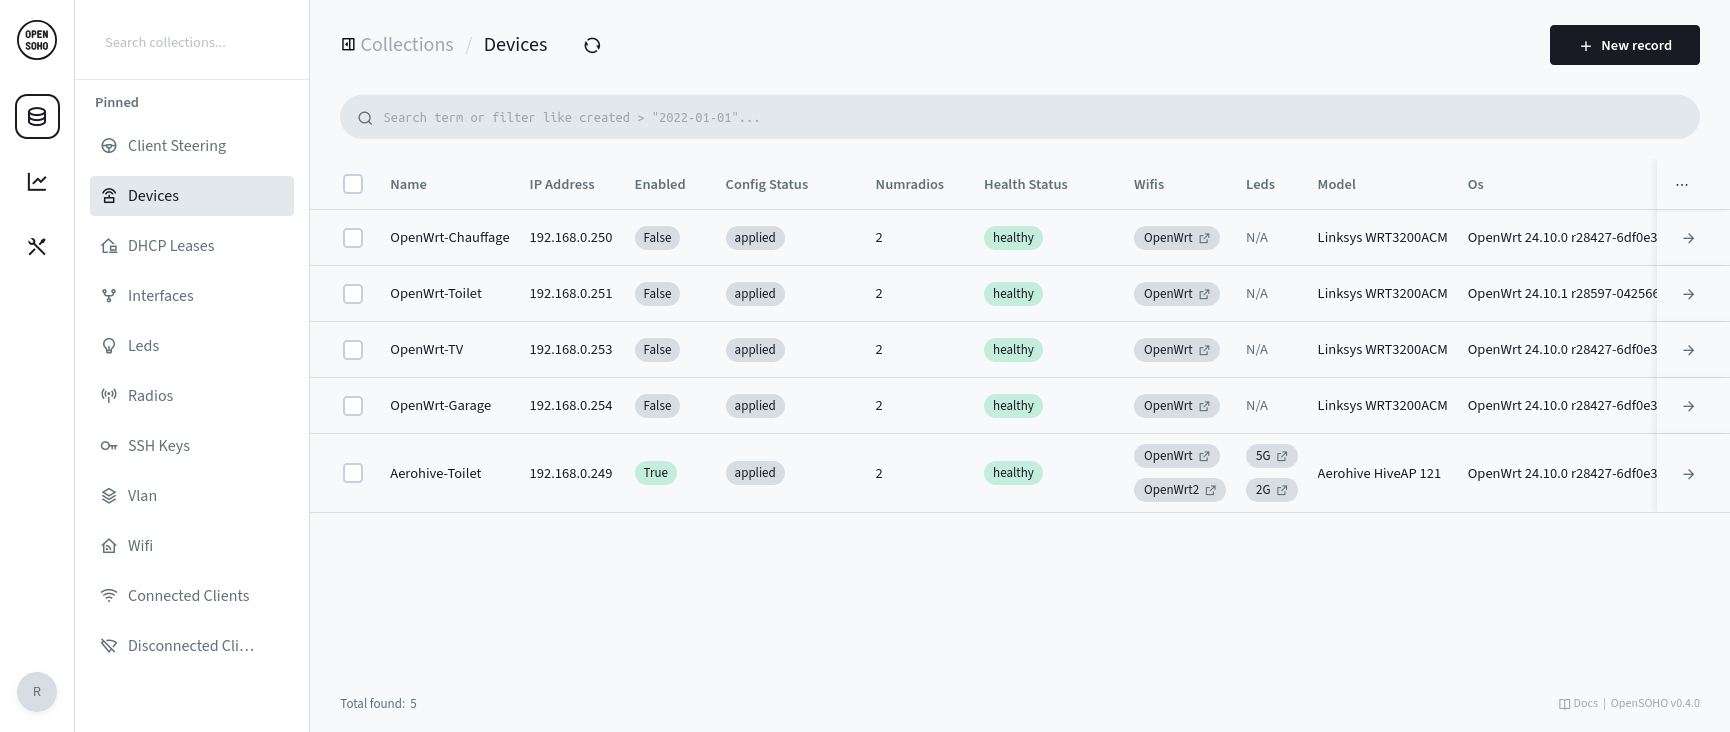 rubenbe/opensoho
Lightweight OpenWRT device management platform for small networks. Centralized configuration, monitoring, and WiFi management for 2–20 devices with…
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 owasp/awscanner
Finds internet-exposed resources in an AWS account
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)
 leitwacht/leitwacht
Leitwacht control plane — runtime security for GitLab Runner CI/CD: policy authoring, multi-tenancy, audit, GitLab integration
 fer1035_terraform/modules/terraform-aws-security-group
Terraform module to manage AWS Security Groups. Currently, the ingress and egress rules support IPv4, IPv6, and Security Group ID inputs.