
stratus-red-team
 datadog/stratus-red-team
:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
adversarial-attackcloud-infrastructure-securitycloud-security+5
2.4k
datadog/stratus-red-team:cloud: :zap: Granular, Actionable Adversary Emulation for the Cloud
 kozmer/aad-bofs
Cobalt Strike BOF collection for attacking Azure AD during red team operations, covering authentication, enumeration, and post-exploitation vectors.
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 netspi/microburst
A collection of scripts for assessing Microsoft Azure security
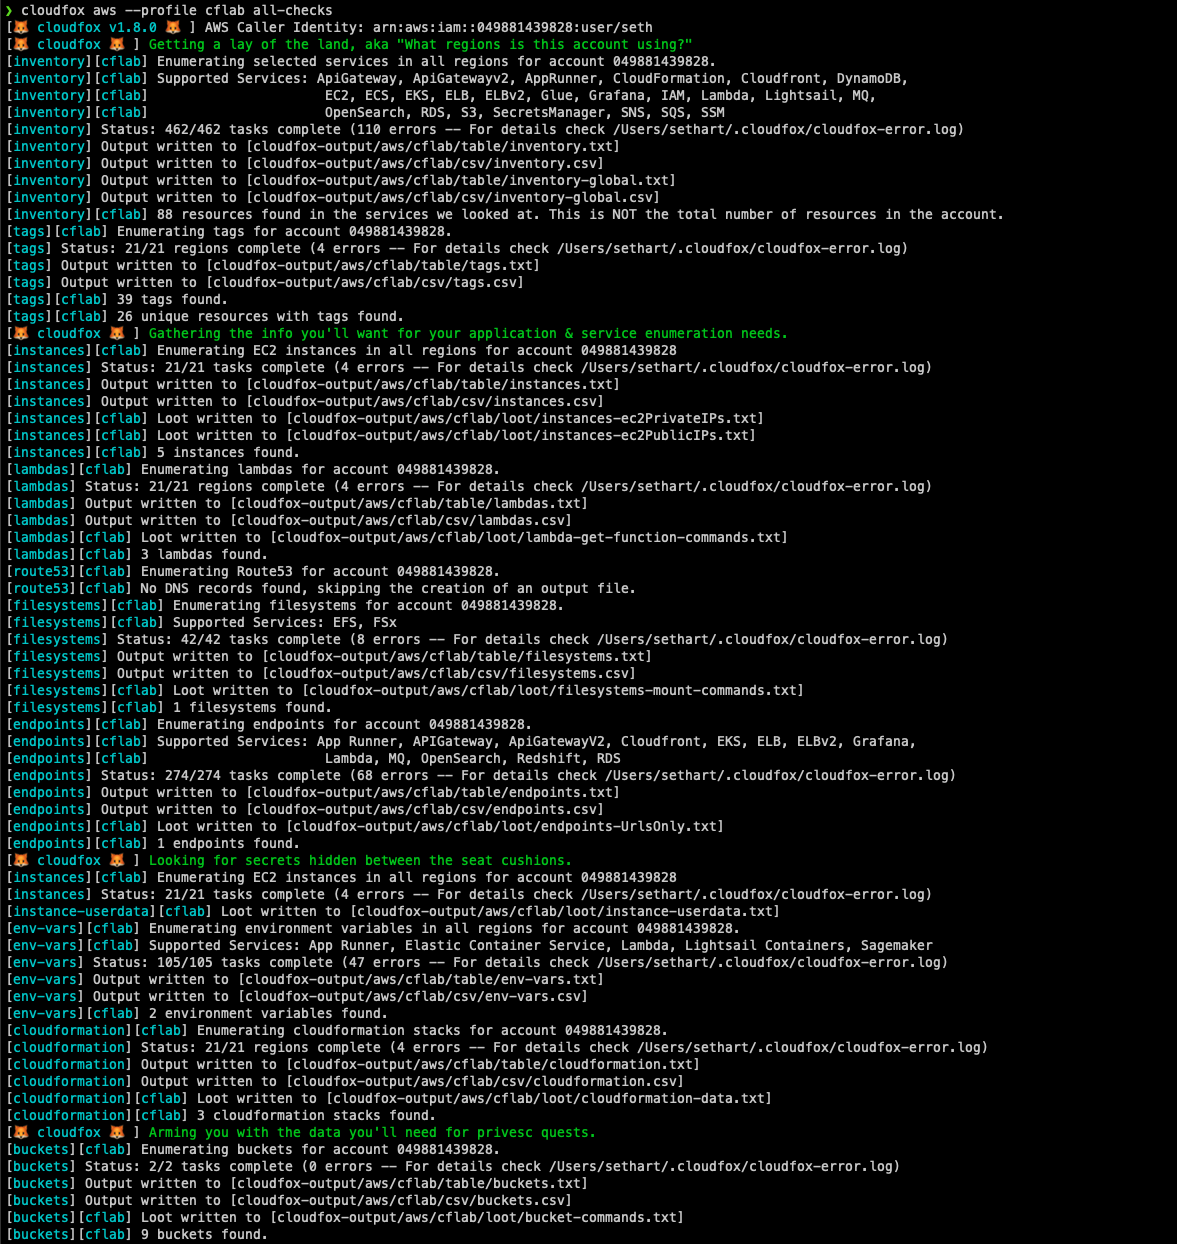 bishopfox/cloudfox
Automating situational awareness for cloud penetration tests.
 dagrz/aws_pwn
A collection of AWS penetration testing junk
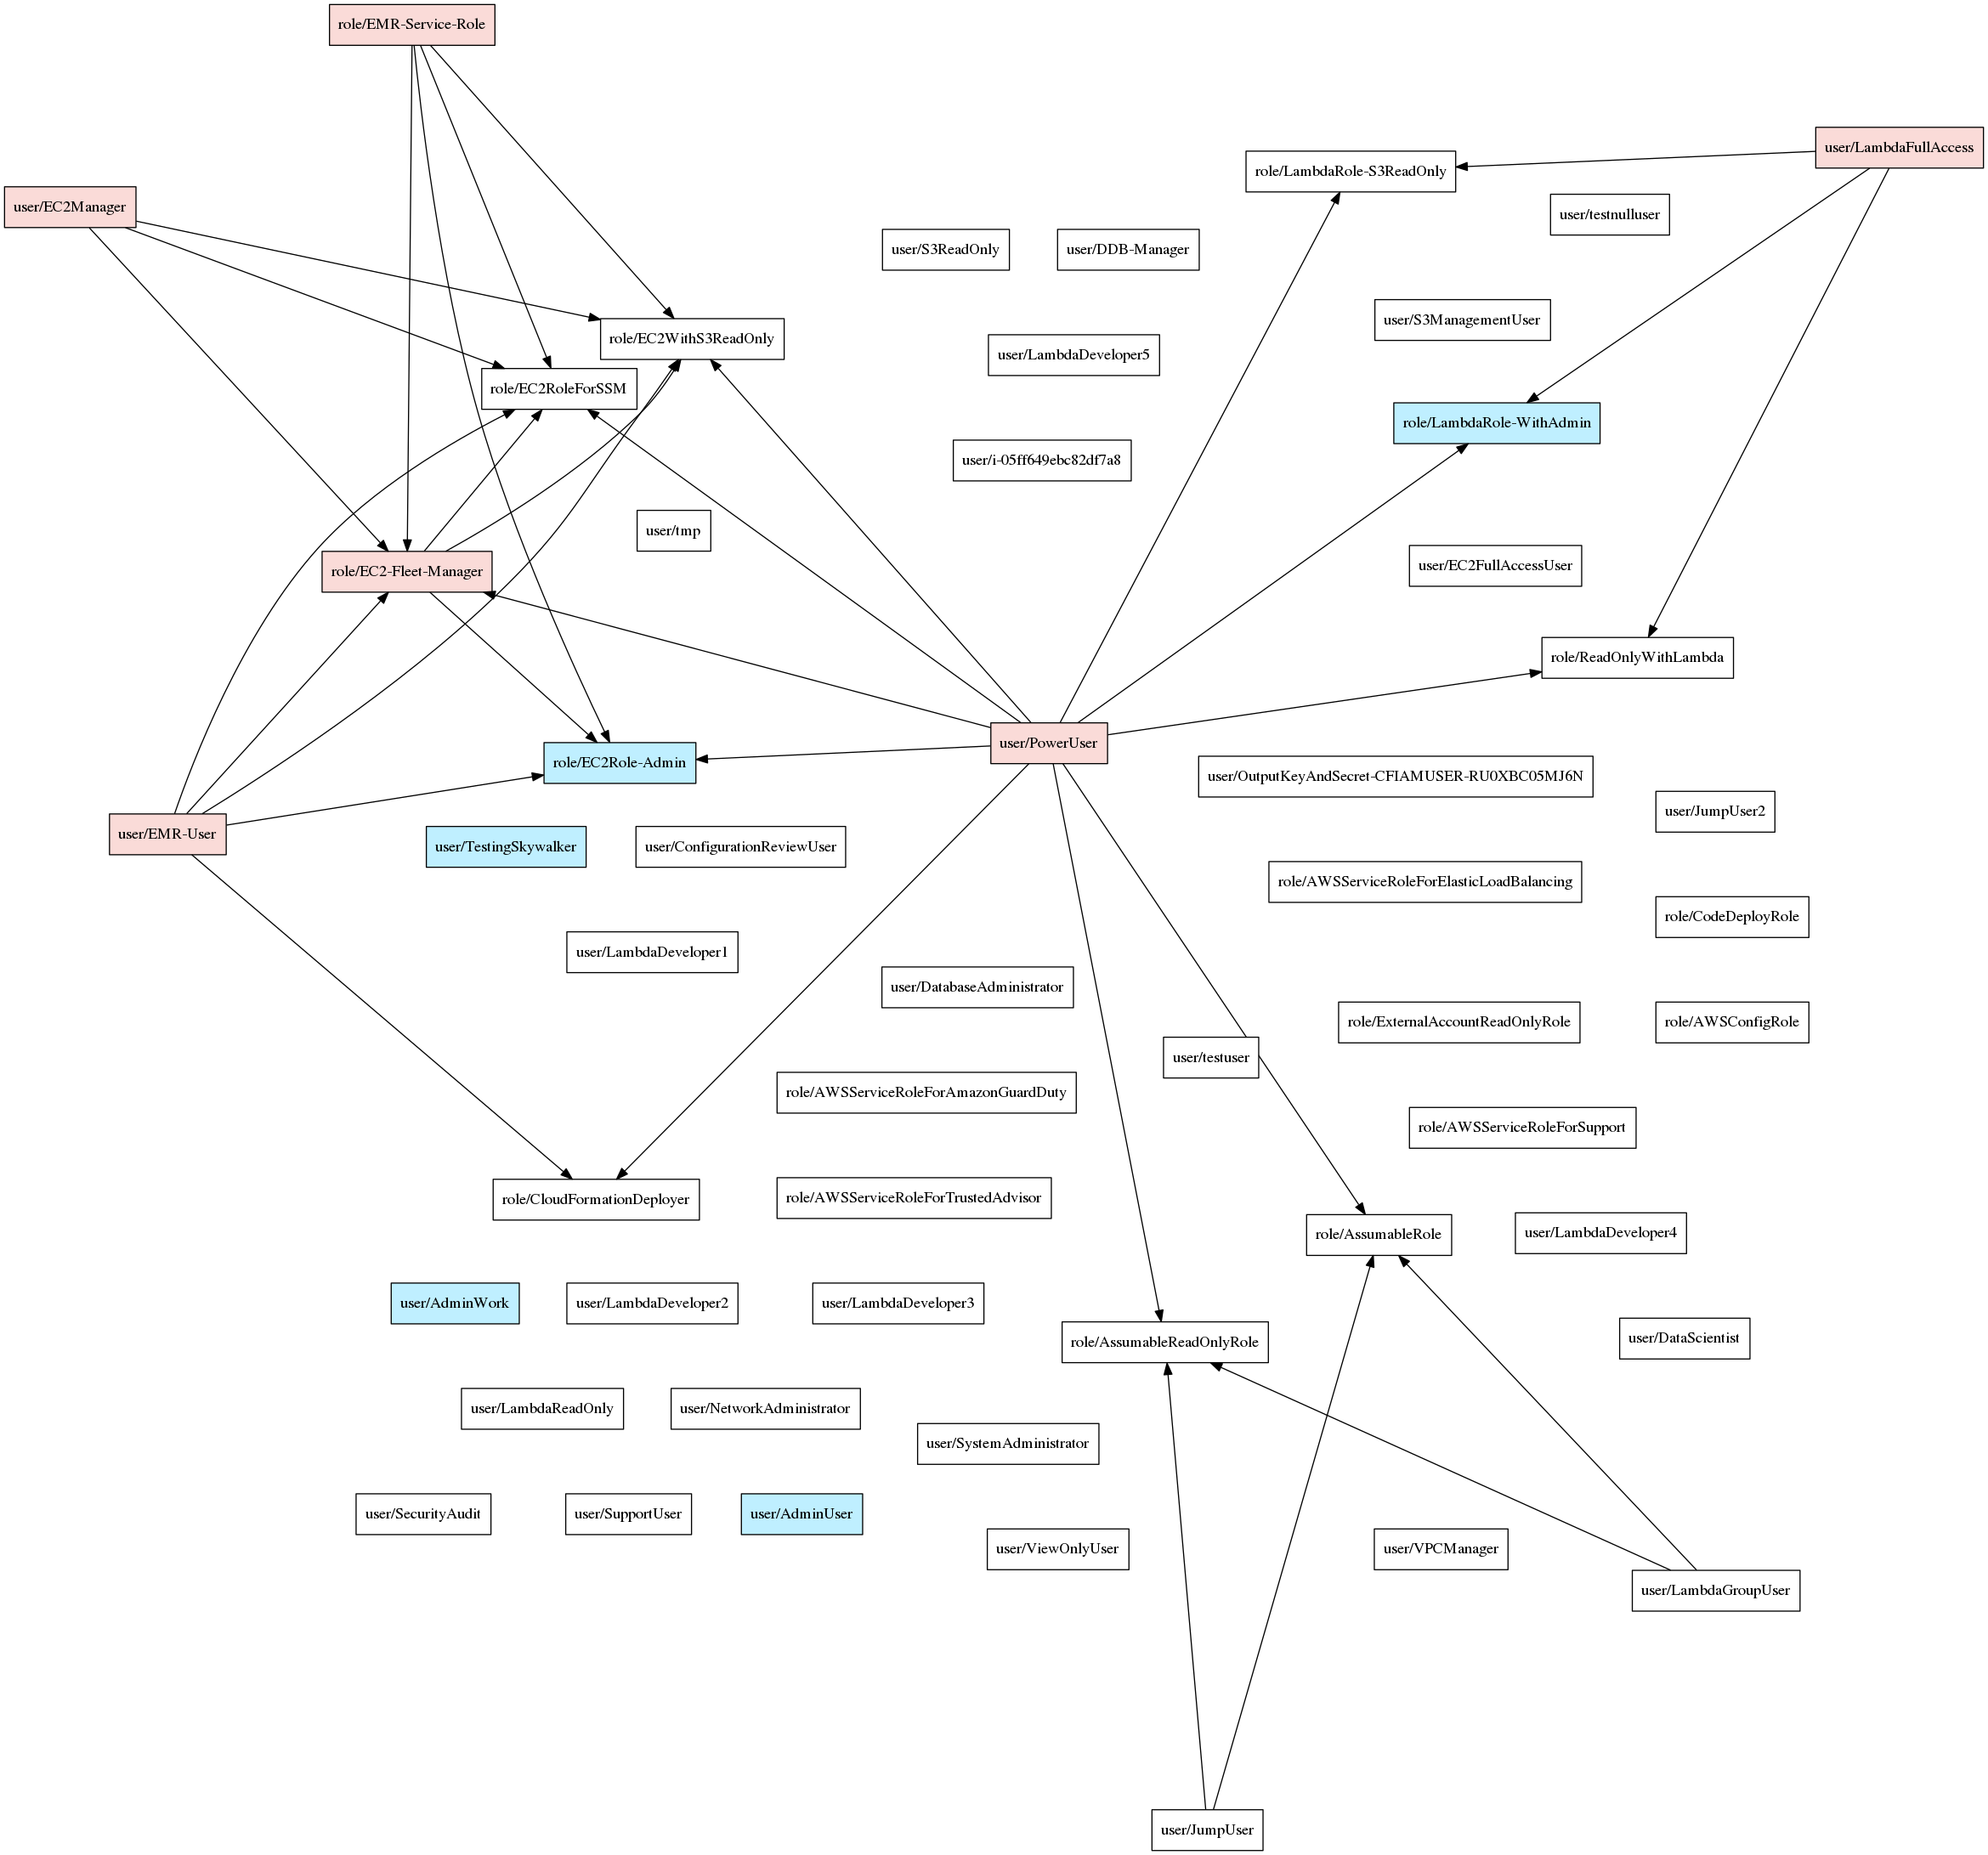 nccgroup/pmapper
A tool for quickly evaluating IAM permissions in AWS.
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 rams3sh/aaia
AWS Identity and Access Management Visualizer and Anomaly Finder
 rhinosecuritylabs/iamactionhunter
An AWS IAM policy statement parser and query tool.
 gen0cide/laforge
Competition Infrastructure Management
 tenable/escalategpt
An AI-powered tool for discovering privilege escalation opportunities in AWS IAM configurations.
 tayontech/scope
AI agent set for cloud security purple teaming, runs inside Claude Code, Gemini CLI, and Codex.
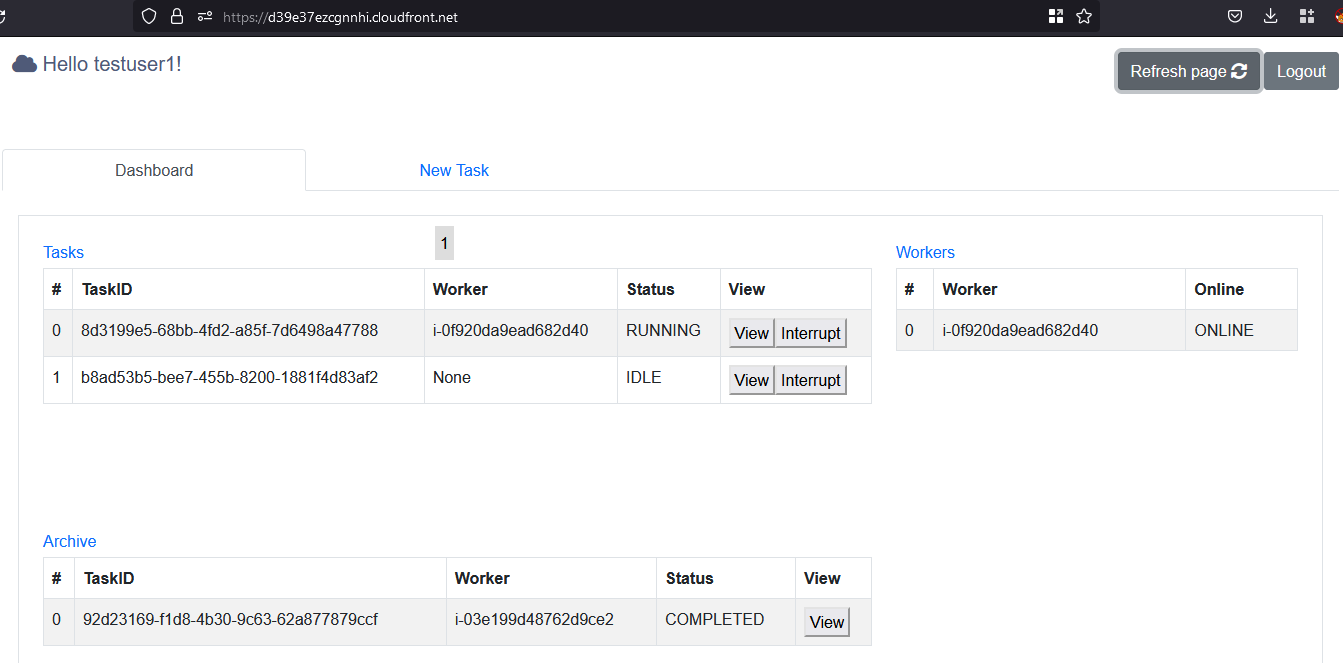 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
 pyperanger/dockerevil
WorldFirst (Public) Docker API Exploit - My security researches involving Docker and Openshift
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 seanrickerd/cve-2026-31431
Exploit for Linux kernel CVE-2026-31431 causing page cache corruption via authencesn AEAD manipulation, targeting privilege escalation in containers…
 mandiant/vcsa-hardening-tool
Automated Zero Trust hardening and forensic auditing for VMware vCenter Server Appliance (VCSA)